
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
O365-Doppelganger — A quick handy script to harvest credentials off of a user during a Red Team and get execution of a file from the user | Kitploit
Tools/GitHubGitHub/paranoidninja/o365-doppelganger
PhishingSocial EngineeringRed Teaming
GitHubparanoidninja/o365-doppelganger

O365-Doppelganger

A quick handy script to harvest credentials off of a user during a Red Team and get execution of a file from the user

View Repository
Share
25436424 years agoReviewed by Kitploit

O365-Doppelganger

O365-Doppelganger is NOT a replacement for hardcore phishing activities. There are several other tools which perform OAuth and OTA capture which is not the aim of O365-Doppelganger.

O365-Doppelganger is a quick handy script to harvest credentials of a user during Red Teams. This repository is a quick hack of one of my old red team engagement scripts which I've used several times to capture credentials and use them for making windows access tokens for lateral movement. This code repository basically performs the below tasks:

  • The GO code:
    • hosts the O365 portal (can be replaced with anything in the index.html). It is recommended to use a valid cert and key file (LetsEncrypt?) instead of the one provided in the directory
    • logs all user activity on the web portal in a seperate log file on the server
    • logs the credentials captured in a seperate log file on the server
    • can also be used to return a valid file to the user post capturing the credentials. This can be done by replacing the file named MacroFile.doc in the current directory and replacing it with HTA/ISO/MSI or anything else that the phisher wants. Theres also a small code in the GO code which would need to be modified to specify the user's file name which needs to be returned: content, err := ioutil.ReadFile("MacroFile.doc")
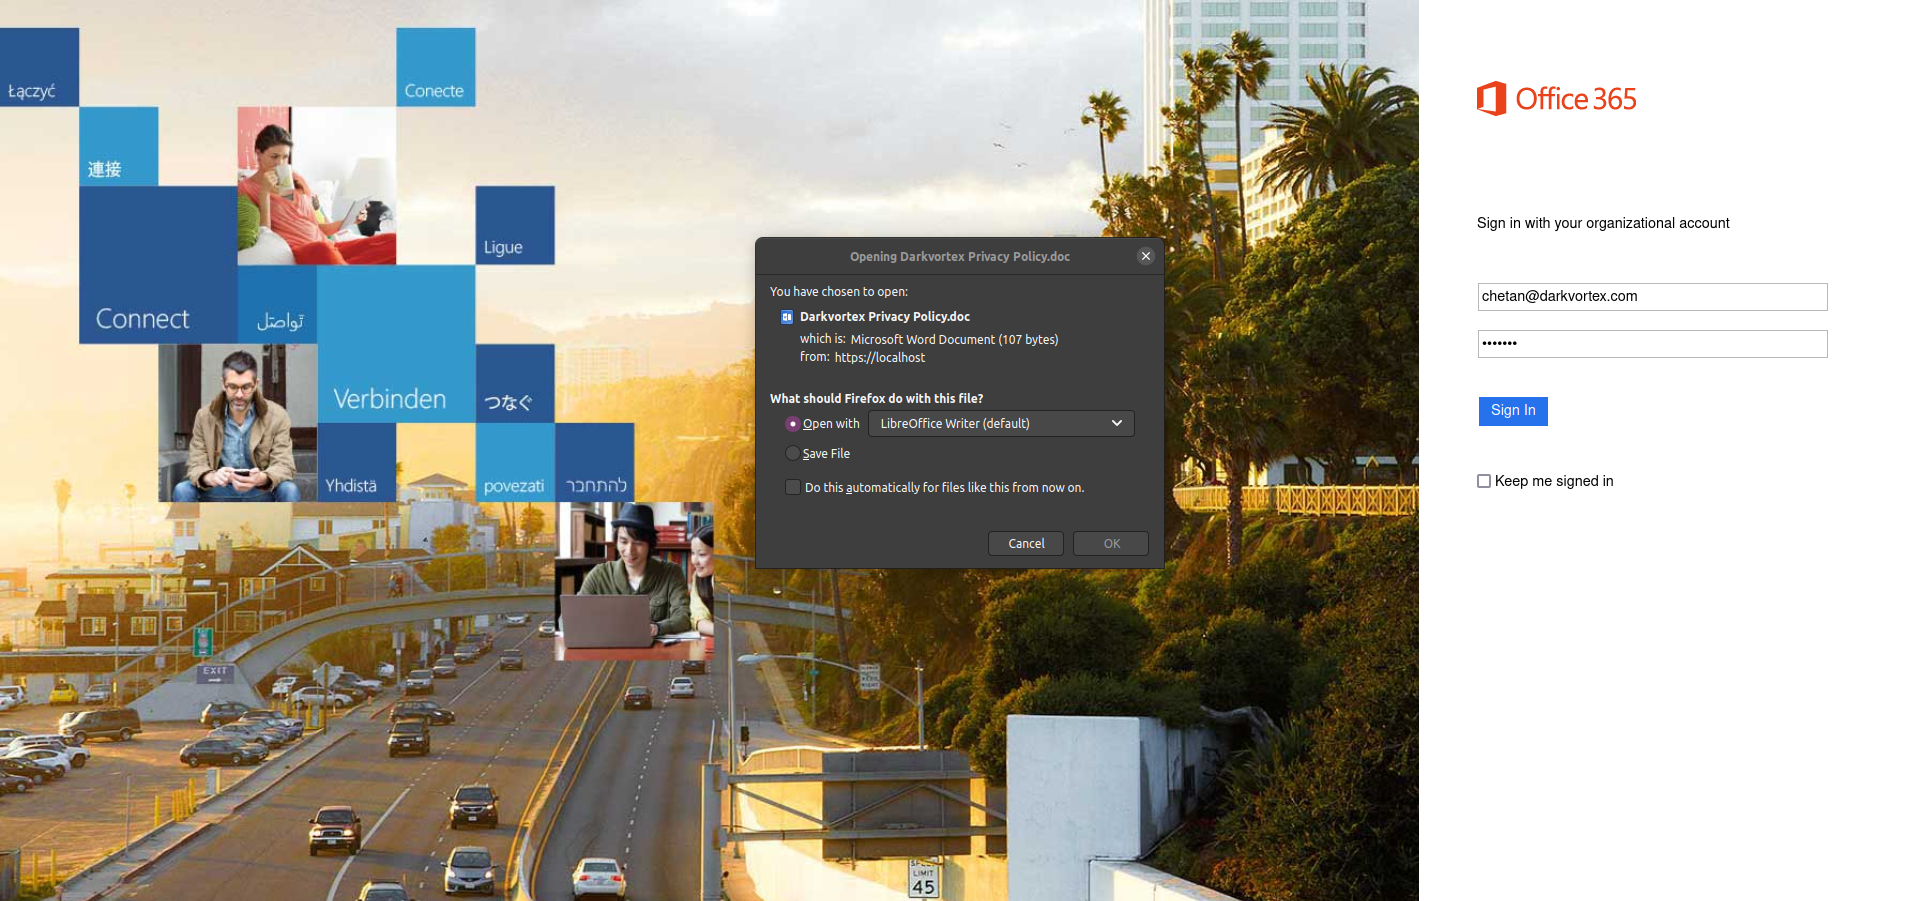
    • Once modified, the target user when enters a valid email ID and password will be asked to save the above file. This file name can be changed using the below code in the GO file: response.Header().Set("Content-Disposition", "attachment; filename=Darkvortex Privacy Policy.doc")
  • The index.html code:
    • renders an O365 portal alongside a small regex which checks for a given user's domain name to make it look a bit more legit. The regex code looks like this: pattern="^([a-zA-Z0-9_\-\.]+)@darkvortex\.([a-zA-Z]{2,5})$" title=" Valid darkvortex email ID"

    • The above regex checks if the given username contains a full valid email address else it will prompt the user to enter a correct username as follows:

  • This same check is also performed in the GO code so that user's do not use something like burp to bypass the check: if strings.Contains(value[i], "@darkvortex") {

  • It's recommended to change the name darkvortex in the index.html file to your own target company name.

  • Once the correct email ID and the password is entered, the user will be asked to save the provided file as follows:

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    936
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    555
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    353
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    348
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    336
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    288

Explore all tools

Browse our collection of tools

View all tools →





