

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2026-53359 — A 16-year-old bug in the Linux kernel lets a rented VM break out and attack the host it runs on. Intel and AMD alike. Januscape is a use-after-free vulnerability in the KVM code that has been sitting there since 2010. | Kitploit
Tools/GitHubGitHub/ndouglas-cloudsmith/cve-2026-53359
Vulnerability AnalysisExploitationCloud SecurityContainer Escape
GitHubndouglas-cloudsmith/cve-2026-53359

CVE-2026-53359

A 16-year-old bug in the Linux kernel lets a rented VM break out and attack the host it runs on. Intel and AMD alike. Januscape is a use-after-free vulnerability in the KVM code that has been sitting there since 2010.

View Repository
444 months agoNot yet reviewed
Share

CVE-2026-53359

A 16-year-old bug in the Linux kernel lets a rented VM break out and attack the host it runs on.
Januscape is a use-after-free vulnerability in the KVM code that has been sitting there since 2010.
Using the exploit-check.sh script, we can get more vuln info about the Linux Kernel vulnerability - CVE-2026-53359.

wget https://raw.githubusercontent.com/ndouglas-cloudsmith/exploit-check/refs/heads/main/exploit-check.sh
chmod +x exploit-check.sh
./exploit-check.sh update
./exploit-check.sh query CVE-2026-53359 --full
./exploit-check.sh query CVE-2026-46113 --full
./exploit-check.sh query CVE-2016-5195 --full --package-info

At the time of writing, there was No CVSS Score or any Known Exploited Vulnerabilities for this flaw.
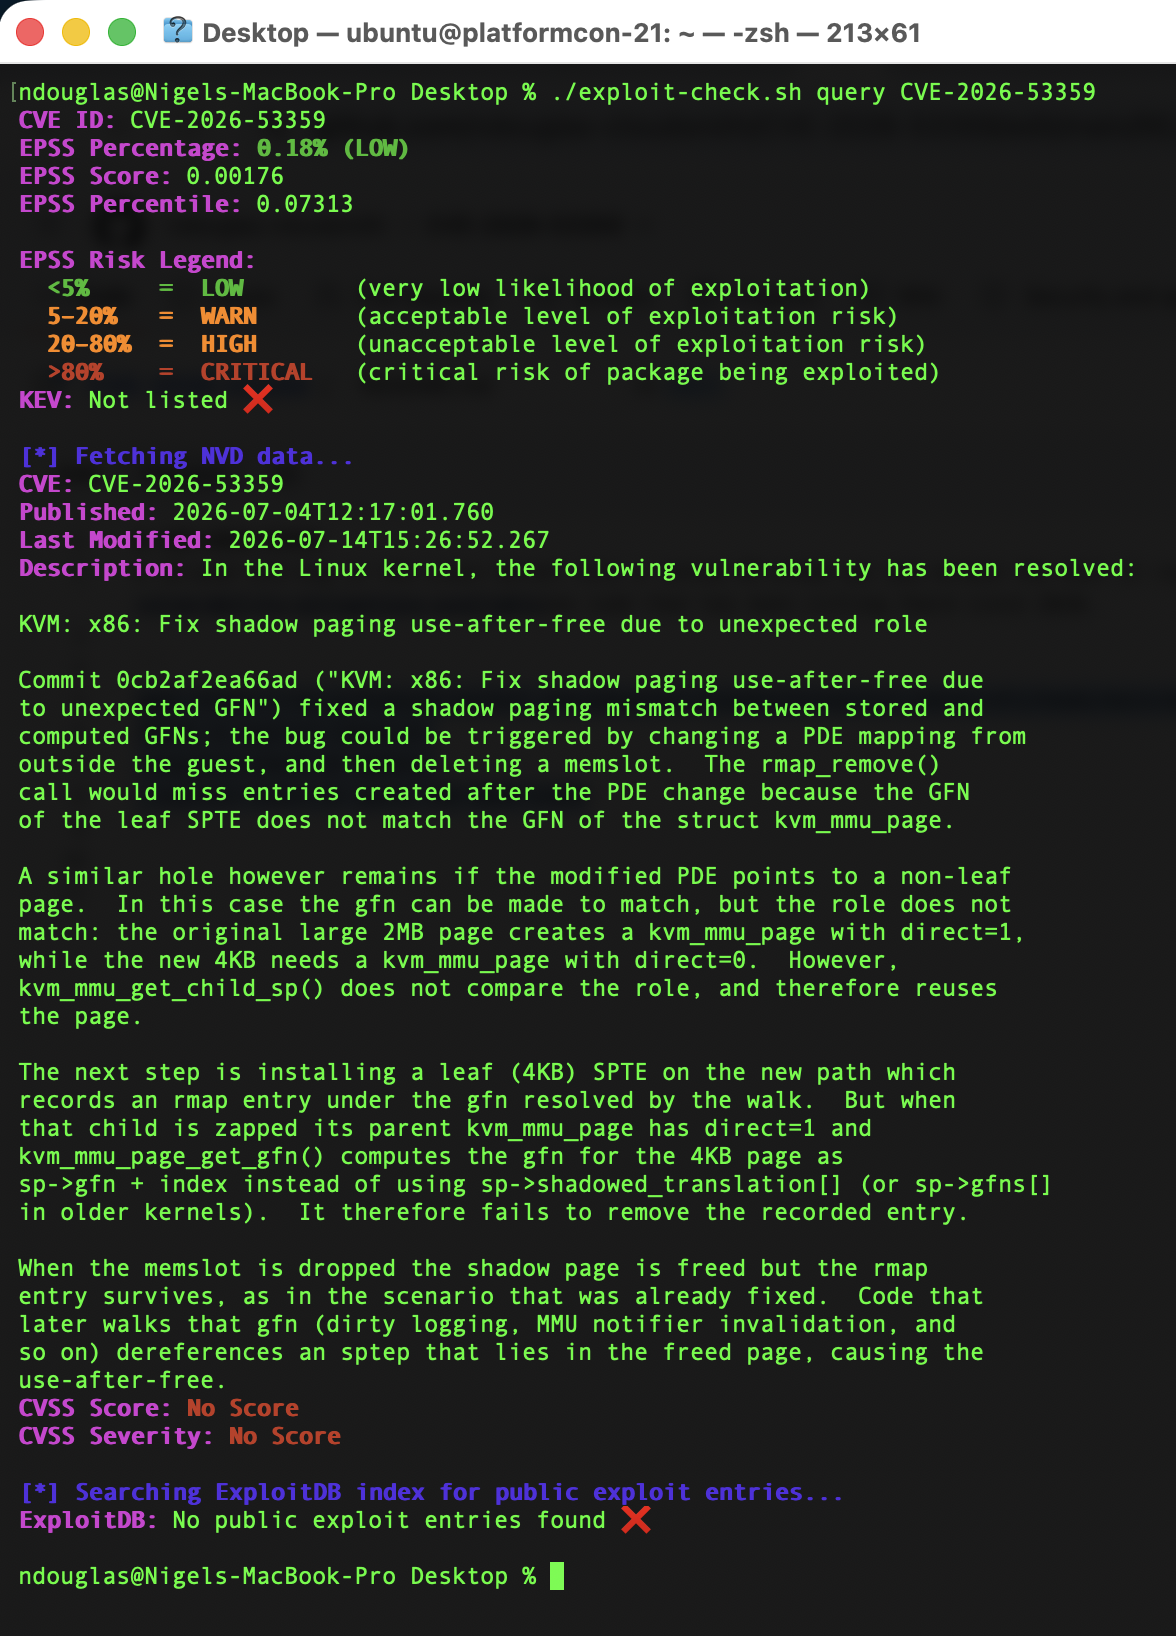
Screenshot 2026-07-15 at 11 57 14

Can the vulnerability be exploited?

Neither NVD (referenced above) nor Kernel.org have published their own CVSS scores for this issue.
Canonical calculated it as an 8.4 CVSS and we have seen others publish scores of 7.8, 8.8, and even 9.3

wget https://raw.githubusercontent.com/ndouglas-cloudsmith/ExploitPwned/refs/heads/main/exploitPwned.sh
chmod +x exploitPwned.sh
./exploitPwned.sh update
./exploitPwned.sh CVE-2026-53359
./exploitPwned.sh CVE-2026-46113
./exploitPwned.sh CVE-2016-5195 --details
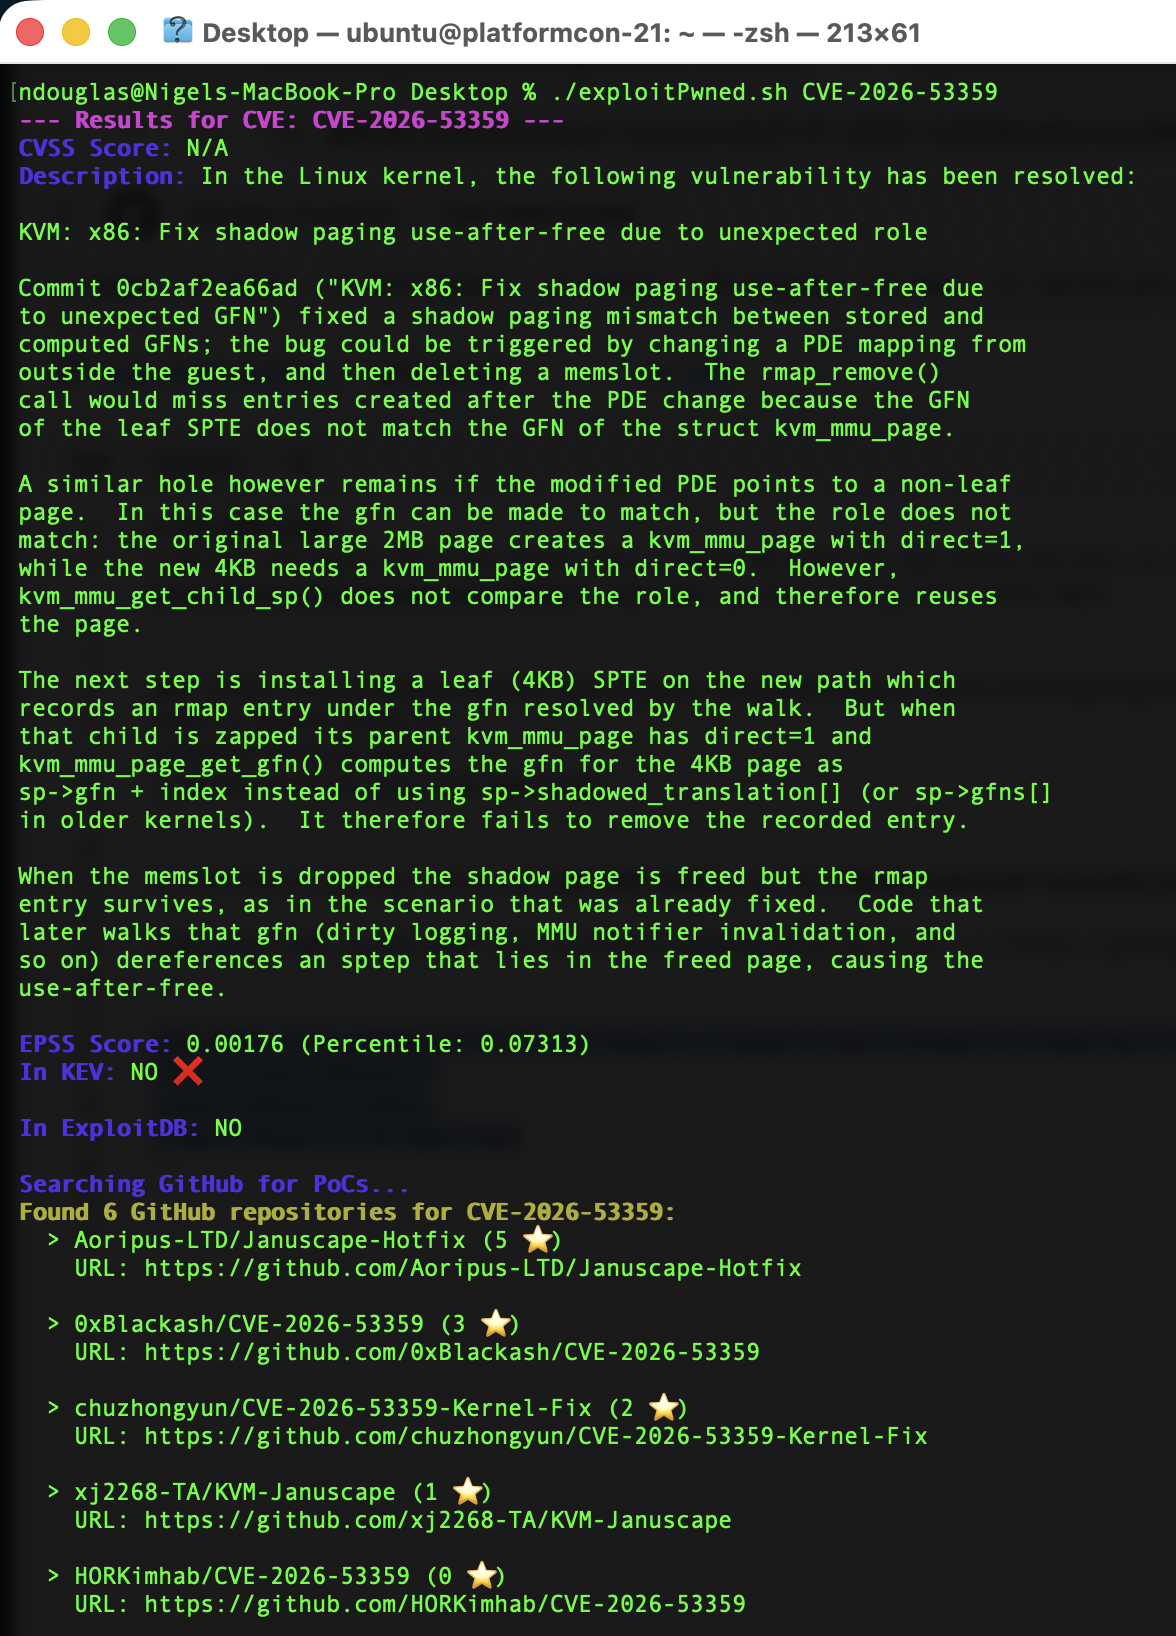
Screenshot 2026-07-15 at 12 05 05

Proof we cannot blindly trust KEV and ExploitDB

Using the exploitPwned.sh script, we can see that certain users have already exploited the vulnerability. In one scenario, instead of modifying the kernel source code or replacing functions, a Chinese threat research used a text_poke binary hotpatch (NOP Patch) method that directly modifies the vulnerable instructions inside active kernel memory.

RepositoryURL
Aoripus-LTD/Januscape-Hotfixhttps://github.com/Aoripus-LTD/Januscape-Hotfix
0xBlackash/CVE-2026-53359https://github.com/0xBlackash/CVE-2026-53359
chuzhongyun/CVE-2026-53359-Kernel-Fixhttps://github.com/chuzhongyun/CVE-2026-53359-Kernel-Fix
xj2268-TA/KVM-Januscapehttps://github.com/xj2268-TA/KVM-Januscape
HORKimhab/CVE-2026-53359https://github.com/HORKimhab/CVE-2026-53359
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    867
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    544
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    385
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    360
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    302
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    279

Explore all tools

Browse our collection of tools

View all tools →






