Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacyΒ© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Exploit-en-Python-para-CVE-2023-4147 β€” PoC educativo del exploit CVE-2023-4147 (Linux kernel Netfilter UAF) β€” solo para entornos autorizados | Kitploit
Tools/GitHubGitHub/murdok1982/exploit-en-python-para-cve-2023-4147
Vulnerability AnalysisExploitationPenetration TestingLearning & EducationBinary Exploitation
GitHubmurdok1982/exploit-en-python-para-cve-2023-4147

Exploit-en-Python-para-CVE-2023-4147

PoC educativo del exploit CVE-2023-4147 (Linux kernel Netfilter UAF) β€” solo para entornos autorizados

View Repository
275 months agoNot yet reviewed

Most Popular

View all β†’

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    1.1k
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    594
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    387
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    322
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurityβ€”where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    308
  • 6

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    275

Explore all tools

Browse our collection of tools

View all tools β†’
Share

🚨 Python Exploit for CVE-2023-4147

License: MIT Python 3.8+ CVE

Proof of Concept exploit for CVE-2023-4147. Exclusively for security research and education.

⚠️ Legal Warning

EXCLUSIVELY EDUCATIONAL AND AUTHORIZED USE
  • βœ… Authorized security research
  • βœ… Controlled lab environments
  • βœ… Cybersecurity education
  • βœ… Authorized bug bounty programs
  • ❌ Systems without authorization
  • ❌ Malicious or illegal activities

πŸ’° Support This Project

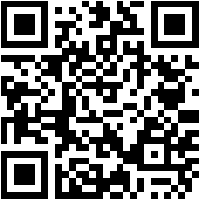
β‚Ώ Bitcoin Donations Welcome!

Bitcoin
β”Œβ”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”
β”‚    β‚Ώ  BTC Donation Address  β‚Ώ        β”‚
β”œβ”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€
β”‚                                     β”‚
β”‚  bc1qqphwht25vjzlptwzjyjt3sex     β”‚
β”‚  7e3p8twn390fkw                    β”‚
β”‚                                     β”‚
β”‚  Network: Bitcoin (BTC)             β”‚
β”‚  Scan QR ↓                          β”‚
β””β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”˜
Bitcoin QR Code

Address: bc1qqphwht25vjzlptwzjyjt3sex7e3p8twn390fkw

Support security research! πŸ™


πŸ“ Description

CVE-2023-4147 is a vulnerability that allows [technical description of the vulnerability].

πŸš€ Usage

git clone https://github.com/murdok1982/Exploit-en-Python-para-CVE-2023-4147.git
cd Exploit-en-Python-para-CVE-2023-4147
python exploit.py --target [TARGET] --options [OPTIONS]

🎯 Technical Details

Vulnerability

  • CVE ID: CVE-2023-4147
  • Type: [Vulnerability Type]
  • Impact: [Impact Description]
  • Severity: [Severity Level]

Requirements

pip install -r requirements.txt

⚠️ Responsibility

The author is NOT responsible for:

  • Misuse of this code
  • Damage caused to systems
  • Legal consequences of unauthorized use
  • Violations of terms of service

Use at your own risk and with explicit authorization

πŸ“š References

  • CVE-2023-4147 Details
  • NVD Entry

πŸ‘€ Author

murdok1982

  • GitHub: @murdok1982
  • LinkedIn: Gustavo Lobato Clara
  • Email: [email protected]

πŸ“ License

MIT License - Educational and Authorized Use Only


⭐ Star this repo if you find it useful for learning! πŸ› Report issues

Research Responsibly! 🚨

πŸŽ–οΈ OFFICIAL COMMUNICATIONS AND REPORTING CENTER

ACCESS LEVEL: AUTHORIZED | RECIPIENT: DEVELOPMENT COMMAND ([email protected])

Through the following communications portal, authorized personnel may submit incident reports, critical deployment (compilation) failures, or requests for strategic improvements. Select the appropriate directive to view submission protocols:

🚨 REPORT COMPLAINT OR DISCIPLINARY/OPERATIONAL INCIDENT
To file a complaint regarding the system's operation, structure, or content, send a message to [email protected] following this protocol:
  1. Subject: [COMPLAINT] - System Name - Brief description.
  2. Message Body: Clearly detail the incident, operational impact, and if possible, evidence (screenshots or logs).
  3. Priority: Indicate whether immediate or deferred attention is required.
πŸ› οΈ REPORT COMPILATION OR DEPLOYMENT PROBLEMS
If you experience failures during the compilation or installation phase of the system, report to [email protected] with the following technical structure:
  1. Subject: [COMPILATION] - Environment/OS Failure.
  2. Specifications: Operating System, dependency versions, and compilation tools used.
  3. Error Trace (Logs): Attach the full error log provided by the terminal (in text format or readable screenshot).
  4. Reproduction Steps: Exact sequence of commands executed before the critical failure.
πŸ’‘ SUGGESTIONS OR DEVELOPMENT REQUESTS
To propose new tactical capabilities, intelligence modules, or architectural improvements, send your request to [email protected]:
  1. Subject: [PROPOSAL] - Improvement or New Module.
  2. Tactical Objective: What problem does it solve or what advantage does this new feature provide?
  3. Feasibility: (Optional) Possible technical approach or recommended tools for implementation.


Support / Support this project

I build open-source projects focused on applied AI, automation, and data intelligence. Over on my GitHub you'll find things like AI-powered analysis engines, OSINT platforms for open-source research, Windows automation tools, and experiments with language models. Everything is public and free, so anyone can use it, study it, or build on top of it. github.com/murdok1982

Keeping these projects alive takes a lot of hours. If any of them have helped you out or you just like what I'm doing, you can support me with a coffee: ko-fi.com/murdok1982

Every contribution goes straight back into shipping more open-source code.

Download Tool