 mrphrazer/obfuscation_detection
Binary Ninja plugin to identify obfuscated code and other interesting code constructs

Author: Tim Blazytko
Automatically detect obfuscated code and other interesting code constructs
Obfuscation Detection is a Binary Ninja plugin to detect obfuscated code and interesting code constructs (e.g., state machines) in binaries. Given a binary, the plugin eases analysis by identifying code locations which might be worth a closer look during reverse engineering.
Based on various heuristics, the plugin pinpoints functions that contain complex or uncommon code constructs. Such code constructs may implement
The following blog posts provide more information about the underlying heuristics and demonstrate their use cases:
Some example use cases can be found in examples. Furthermore, the REcon talk "Unveiling Secrets in Binaries using Code Detection Strategies" demonstrates some use cases. The slides can be found here; the recording can be found here.
The tool can be installed using Binary Ninja's plugin manager.
For the headless version, follow these steps:
git clone https://github.com/mrphrazer/obfuscation_detection.git
cd obfuscation_detection

# install obfuscation_detection
pip install .
The plugin can be used in the user interface and in headless mode.
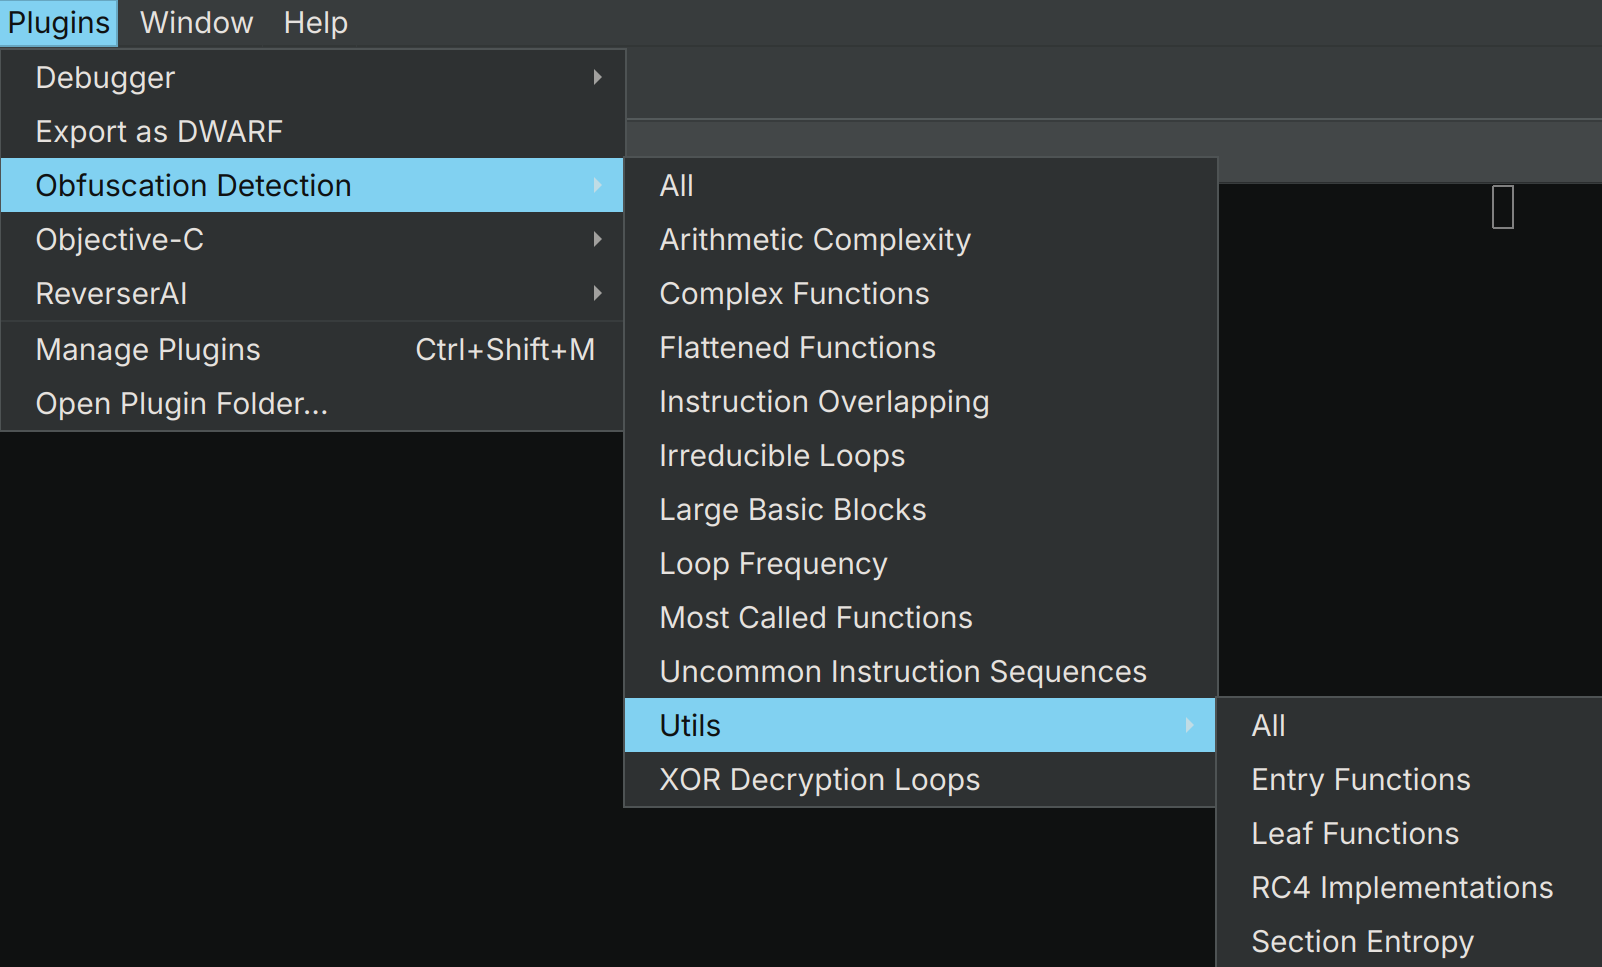
Choose Plugins -> Obfuscation Detection to run individual heuristics, or Plugins -> Obfuscation Detection -> Utils to run individual utility detections. The Plugins -> Obfuscation Detection -> All command runs all heuristics and all utilities together.
The results are displayed in the Log window:
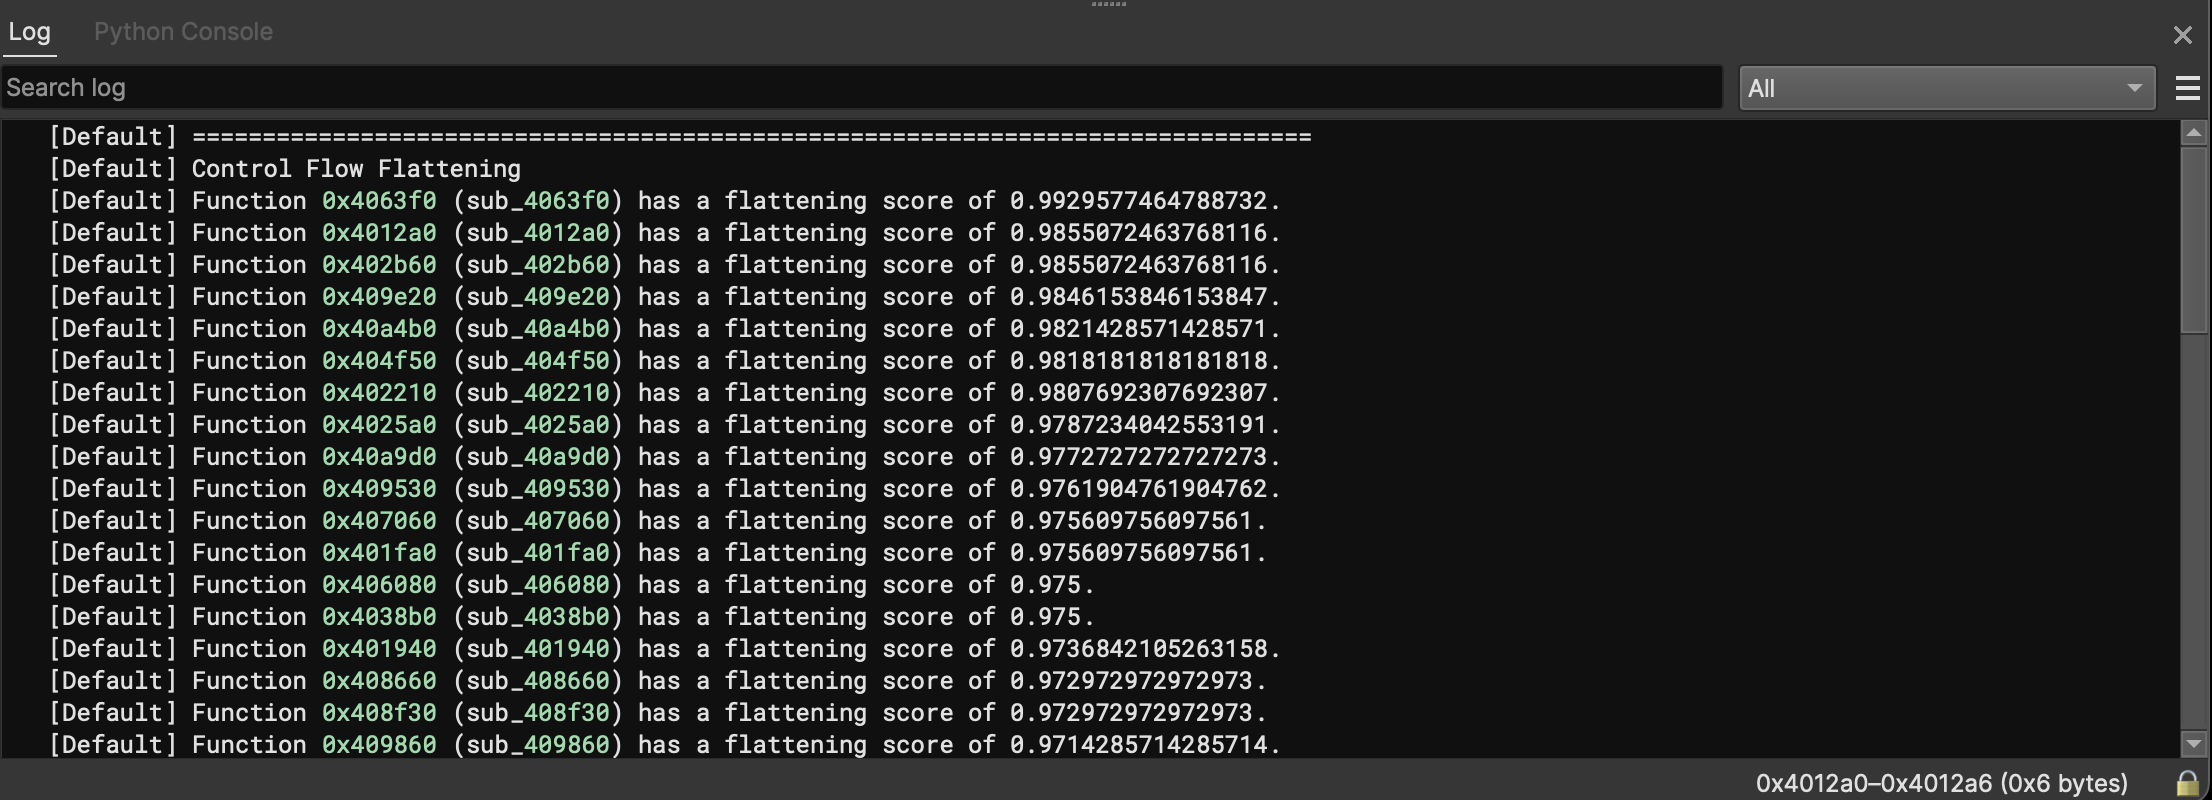
By clicking on the identified function addresses, Binary Ninja navigates to the selected function.
To use the plugin in headless mode, run scripts/detect_obfuscation.py:
$ python3 scripts/detect_obfuscation.py <binary>
This runs all heuristics and all utilities. For machine-readable output, pass --json:
$ python3 scripts/detect_obfuscation.py --json <binary>
The JSON payload contains all results under the detections key. Each detection has a stable id for automation and a human-readable name. Each tagged function finding includes the tag type and description used by the Binary Ninja plugin.
To run only the state machine heuristic in headless mode, use scripts/detect_state_machine.py:
$ python3 scripts/detect_state_machine.py [--json] <binary>
The plugin implements various detection heuristics to detect different code constructs. In the following, we briefly describe the individual heuristics and explain their usage.
The large basic block heuristic identifies the top 10% of functions with the largest average number of instructions per basic block. It allows to detect
The complex function heuristic identifies the top 10% of functions with the most complex control-flow graphs (based on cyclomatic complexity). It allows to identify
The state machine heuristic uses graph-theoretic properties to identify functions implementing state machines. Usually, such state machines can be represented as switch statements that are dispatched in a loop. The heuristic allows to identify
The uncommon instruction sequence heuristic performs a statistical analysis to identify the top 10% of functions whose code patterns deviate from a pre-computed ground truth. This way, the heuristic allows to identify
The overlapping instruction heuristic identifies functions with disaligned instructions (instruction bytes are shared by two different instructions). The heuristic identifies
If the heuristic is used in Binary Ninja's user interface, overlapping instructions are also highlighted in the graph view.
The most called function heuristic identifies the top 10% of functions with the largest number of calls from different functions. This way, the heuristic can identify
The heuristic identifies functions with a high number of loops. These kind of functions might implement
The heuristic also helps pinpointing potential performance bottlenecks.
The heuristic identifies functions with rare and complex loop structures that typically suggest
The heuristic identifies functions which perform an XOR operation with a constant inside of a loop. This way, the heuristic can identify
The heuristic identifies functions in which the expressions have more than one arithmetic operation and one boolean operation simultaneously. This way, the heuristic can identify
The heuristic uses an iterative context-hashing approach to detect repeated multi-block structures within each function’s control-flow graph. By comparing each block’s opcode signature along with the signatures of its successors, the heuristic identifies subgraphs that are duplicated or near-duplicated in a single function. This helps pinpoint:
