#1
Firmware extraction, unpacking, emulation, vulnerability discovery, and binary analysis tools.
Kitploit recommended

 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 openwrt/openwrt
Linux operating system for embedded devices with writable filesystem, package management, and build framework. Enables custom firmware creation for…
 werwolv/imhex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 zhaoxuya520/reverse-skill
AI-powered skill router pack for reverse engineering, penetration testing, and security research. Routes AI agents to correct methodologies and…
 djsime1/awesome-flipperzero
🐬 A collection of awesome resources for the Flipper Zero device.
 qemu/qemu
Official QEMU mirror. Please see https://www.qemu.org/contribute/ for how to submit changes to QEMU. Pull Requests are disabled. Please only use…
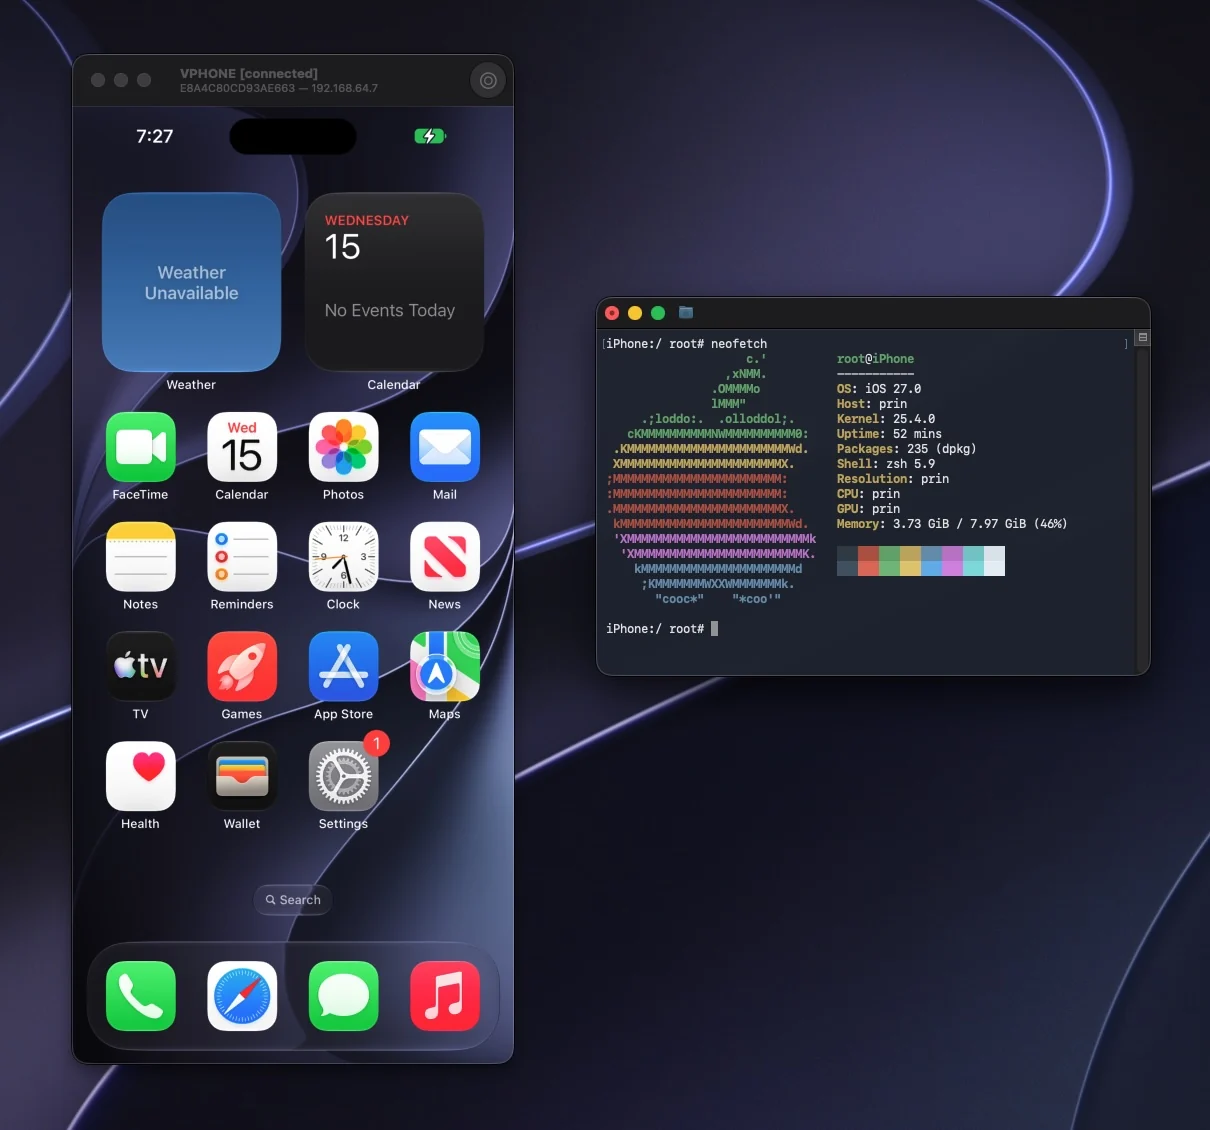 lakr233/vphone-cli
Boot and manage virtual iPhones on Apple Silicon with firmware patching, jailbreak variants, and security research features for iOS testing and…
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
 mrexodia/ida-pro-mcp
AI-powered reverse engineering assistant that bridges IDA Pro with language models through MCP.
refirmlabs/binwalkFirmware Analysis Tool
 angr/angr
A powerful and user-friendly binary analysis platform!
 mister-devel/main_mister
FPGA-based hardware emulation platform main binary and documentation for retro system development, firmware compilation, and hardware security…
 qilingframework/qiling
A True Instrumentable Binary Emulation Framework
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
 mandiant/flare-vm
A collection of software installations scripts for Windows systems that allows you to easily setup and maintain a reverse engineering environment on…