
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Syborg — Recursive DNS Subdomain Enumerator with dead-end avoidance system (BETA) | Kitploit

Tools/GitHubGitHub/milindpurswani/syborg
ReconnaissanceDNS & Subdomain EnumerationInformation GatheringDNS Analysis
GitHubmilindpurswani/syborg

Syborg

Recursive DNS Subdomain Enumerator with dead-end avoidance system (BETA)

View Repository
14619485 years agoReviewed by Kitploit
Share

Syborg

Syborg is a Recursive DNS Domain Enumerator which is neither active nor completely passive. This tool simply constructs a domain name and queries it with a specified DNS Server.

Syborg has a Dead-end Avoidance system inspired from @Tomnomnom's ettu.

When you run subdomain enumeration with some of the tools, most of them passively query public records like virustotal, crtsh or censys. This enumeration technique is really fast and helps to find out a lot of domains in much less time.

However, there are some domains that may not be mentioned in these public records. In order to find those domains, Syborg interacts with the nameservers and recursively brute-forces subdomain from the DNS until it's queue is empty.
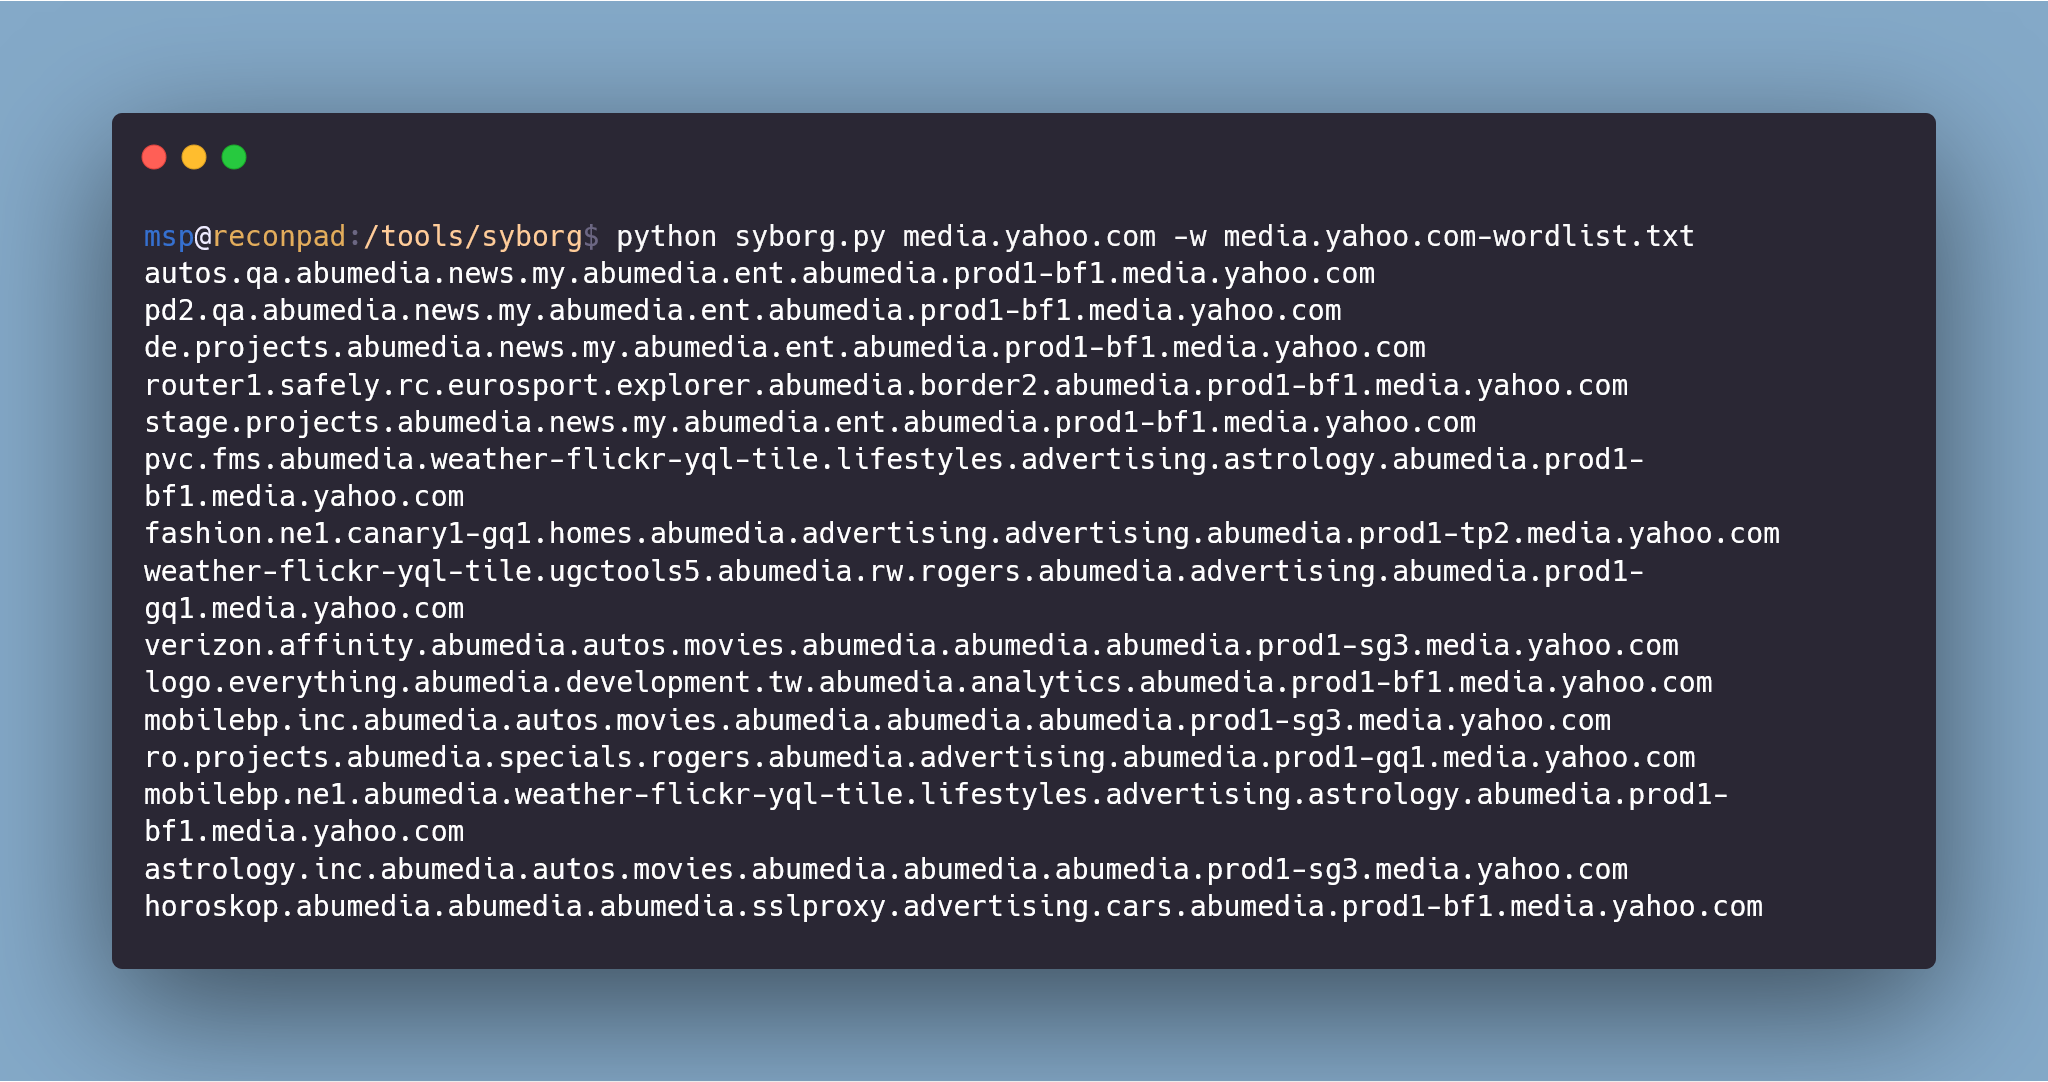
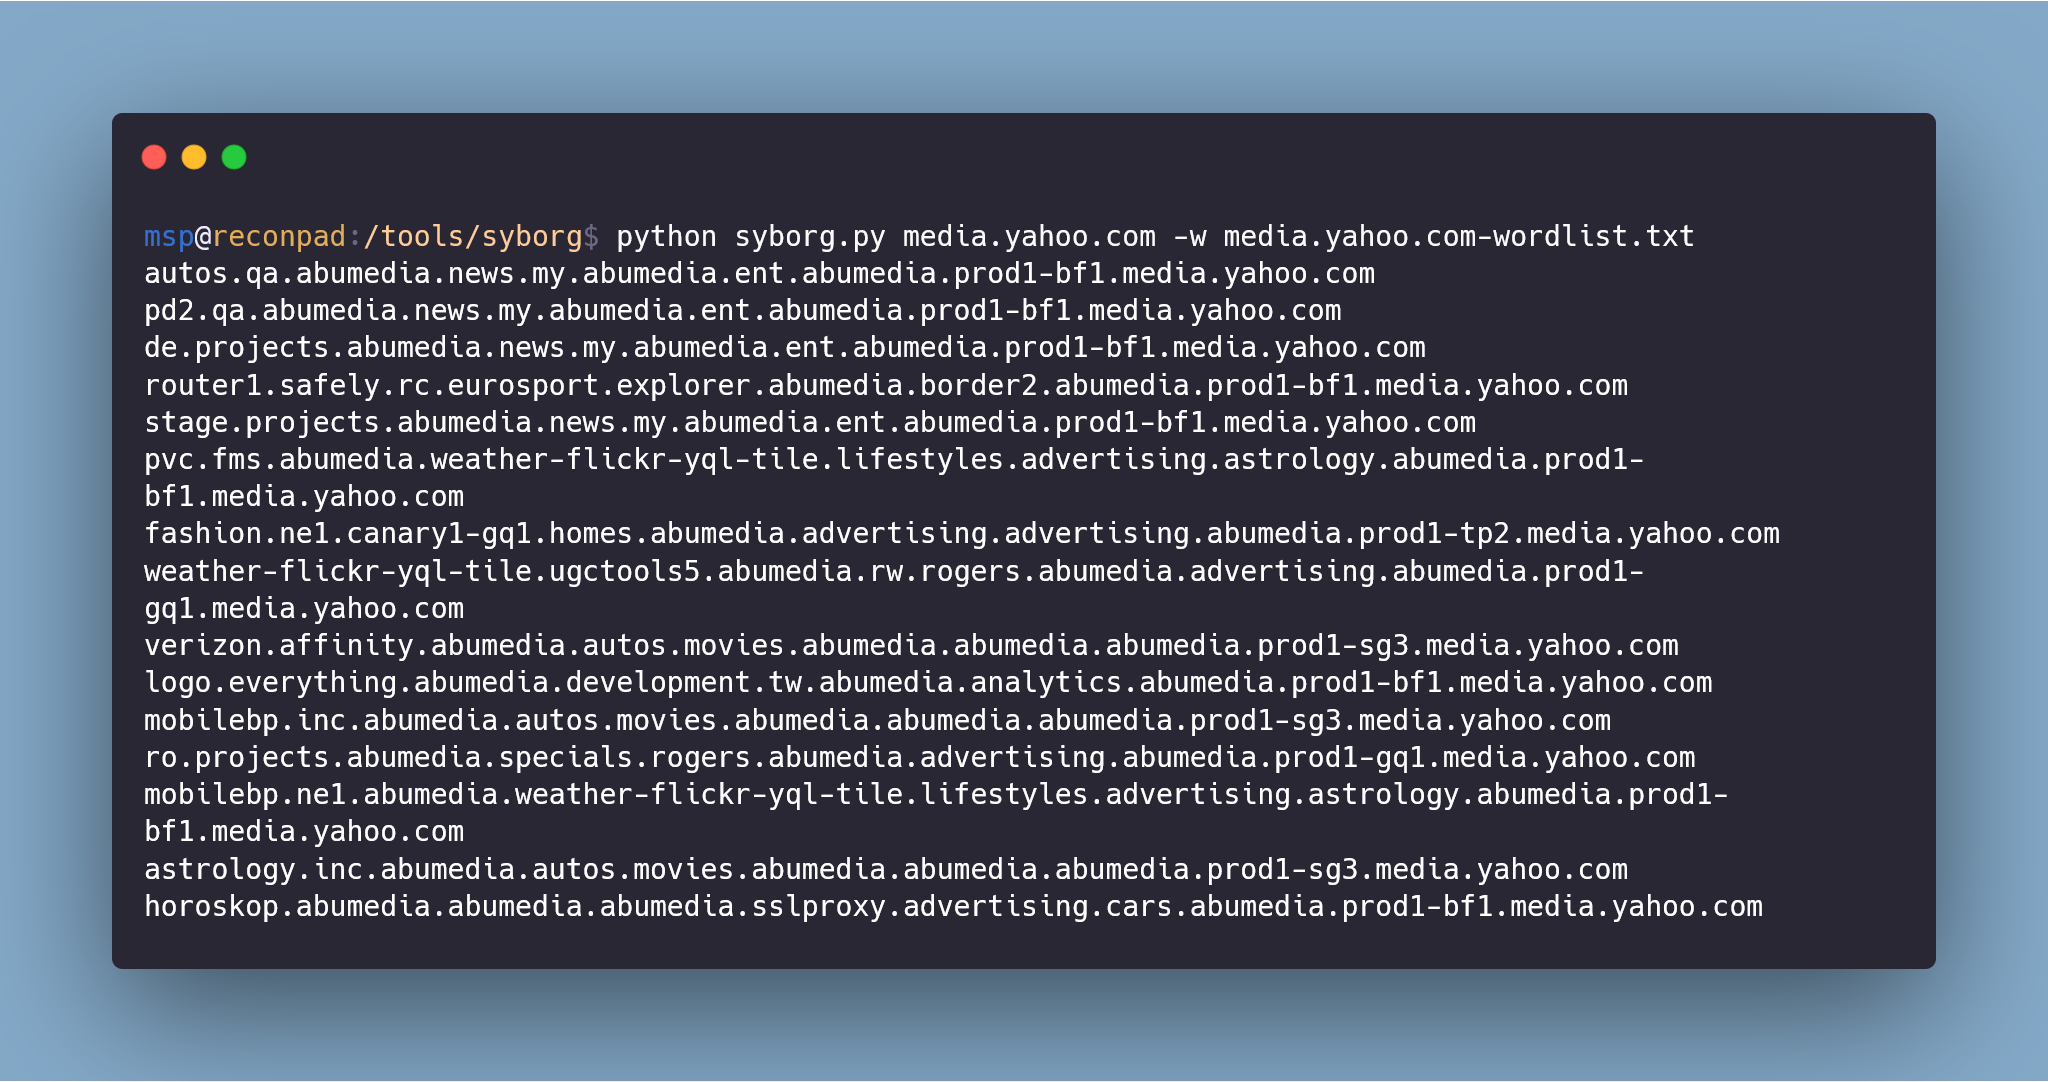
carbon.png Image Credits: Carbon

As mentioned on ettu's page, I quote:

Ordinarily if there are no records to return for a DNS name you might expect an NXDOMAIN error:

▶ host four.tomnomnom.uk
Host four.tomnomnom.uk not found: 3(NXDOMAIN)

You may have noticed that sometimes you get an empty response instead though:

▶ host three.tomnomnom.uk

The difference in the latter case is often that another name - one that has your queried name as a suffix - exists and has records to return

▶ host one.two.three.tomnomnom.uk
one.two.three.tomnomnom.uk has address 46.101.59.42

This difference in response can be used to help avoid dead-ends in recursive DNS brute-forcing by not recursing in the former situation:

▶ echo -e "www\none\ntwo\nthree" | ettu tomnomnom.uk
one.two.three.tomnomnom.uk

Syborg incorporates all of these functionalities with simple concurrency and recursion.

Requirements:

Python 3.x (Recommended)

Python 2.x (Not tested)

Installation:

Clone the repo using the git clone command as follows:

git clone https://github.com/MilindPurswani/Syborg.git

Resolve the Dependencies:

pip3 install -r requirements.txt

Usage:

python3 syborg.py yahoo.com 

More information regarding usage can be found in Syborg's Creative Usage Guidelines. Do check it out!

At times, it is also possible that Syborg will hit High CPU Usage and that can cost you a lot if you are trying to use this tool on your VPS. Therefore to limit that use another utility called Cpulimit

cpulimit -l 50 -p $(pgrep python3)

This tool can be downloaded as follows:

sudo apt install cpulimit

Special Thanks <3:

  1. @nahamsec for his invaluable contribution towards the community by live streams. Check out his twitch channel https://twitch.tv/nahamsec
  2. @tomnomnom for making such awesome tools and sharing with everyone. Be sure to check out his twitch https://www.twitch.tv/tomnomnomuk
  3. @GP89 for the FileQueue lib that resolved high memory consumption problem with Syborg.
  4. Patrik Hudak for his awesome teachings and tools like dnsgen.
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    927
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    555
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    360
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    357
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    324
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    289

Explore all tools

Browse our collection of tools

View all tools →






