Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/maximilianljungblut/hipcam-rtsp-format-validation-vulnerability
IoT SecurityVulnerability AnalysisExploitationFuzzingPenetration Testing
GitHubmaximilianljungblut/hipcam-rtsp-format-validation-vulnerability

Hipcam-RTSP-Format-Validation-Vulnerability

View Repository

About

This POC exploits a format validation vulnerability in the RTSP service of the Hipcam RealServer/V1.0, inducing a crash for approximately 45 seconds by injecting random data into the 'client_port' parameter during the RTSP SETUP request. Hipcam RealServer/V1.0 is used in many Hipcam Cameras. | CVE-2023-50685

Website
186432 years agoReviewed by Kitploit
Share

Hipcam RealServer/V1.0 RTSP Format Validation Vulnerability Proof-of-Concept | CVE-2023-50685

Proof-of-Concept for RTSP Service Format Validation Vulnerability in Hipcam RealServer/V1.0.

Description

This POC exploits a format validation vulnerability in the Real Time Streaming Protocol (RTSP) service of the Hipcam RealServer/V1.0, stemming from inadequate input validation and handling of the 'client_port' parameter in the RTSP SETUP request.

Vulnerability Details

The 'client_port' parameter in the RTSP SETUP request is manipulated, inducing a vulnerability in the RTSP server's format validation. Unlike conventional exploits with a specific overflow value, this vulnerability is triggered by improper formatting, particularly when the 'client_port' is not in the expected format (e.g., client_port=[custom_port]-[custom_port+1]). Format validation vulnerabilities occur when an application fails to properly validate or handle input, potentially leading to unexpected behavior. In this case, the goal is to disrupt the service.

cam_address = "rtsp://120.75.111.XX:554/11" #The RTSP port is normaly 554 with the path /11 which is also normaly used in Hipcam Cameras
random_data_value = 8712429 #It can be anything except the correct format of [custom_port]-[custom_port+1]
rtsp_request = f"SETUP {cam_address}/trackID=1 RTSP/1.0\r\nCSeq: 3\r\nTransport: RTP/AVP;unicast;client_port={random_data_value}\r\n\r\n"

Exploitation

Steps

  1. Formulate an RTSP URL for the target camera.
  2. Craft an RTSP SETUP request with a manipulated 'client_port' parameter (ensure it is not in the expected format).
  3. Establish a connection to the RTSP service on the target camera.
  4. Send the crafted RTSP request to the camera, attempting to trigger the format validation vulnerability.

Script Usage

python3 poc.py 120.75.111.XX 554
python3 poc.py -h

Impact

Upon successful exploitation, the RTSP stream is offline for approximately 45 seconds. This disruption could be leveraged in physical attack scenarios where temporary unavailability of surveillance footage may provide an opportunity for unauthorized access or other malicious activities.

Shodan Trends

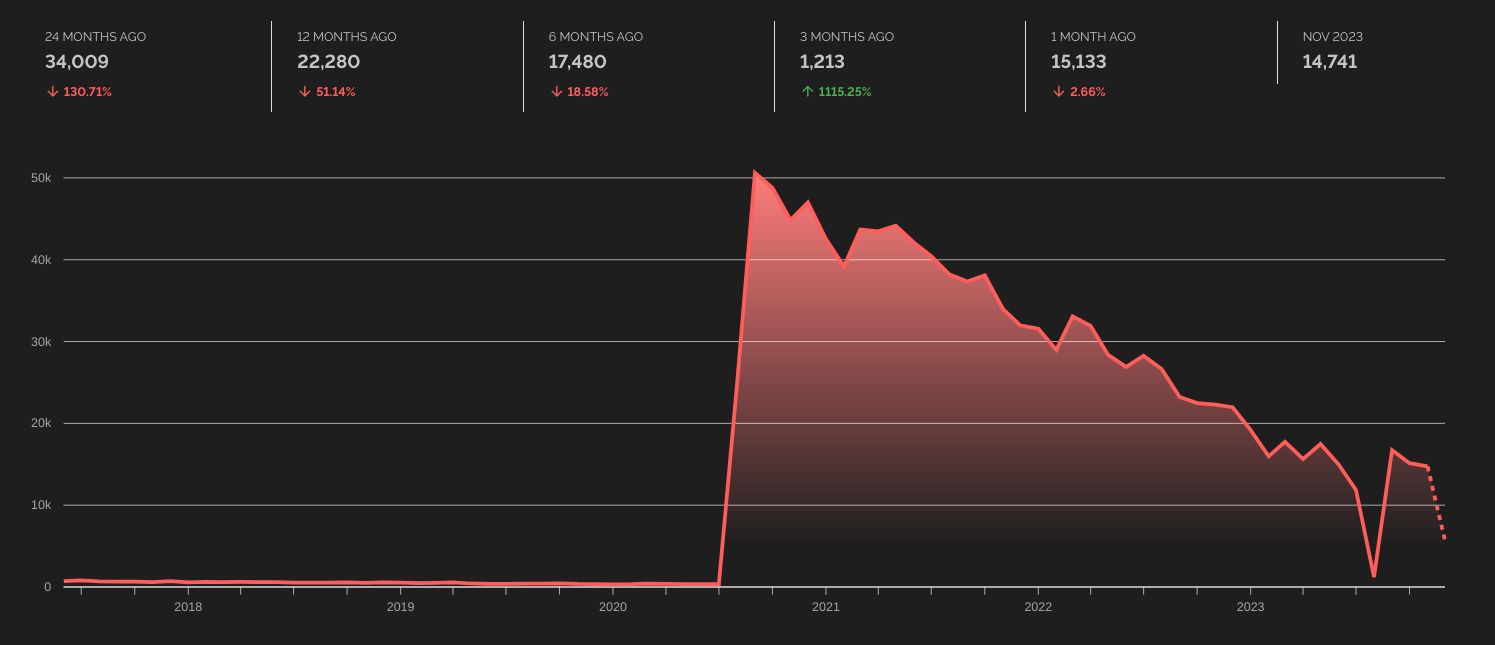
Timeline Shodan Trend of Hipcam RealServer/V1.0 Devices

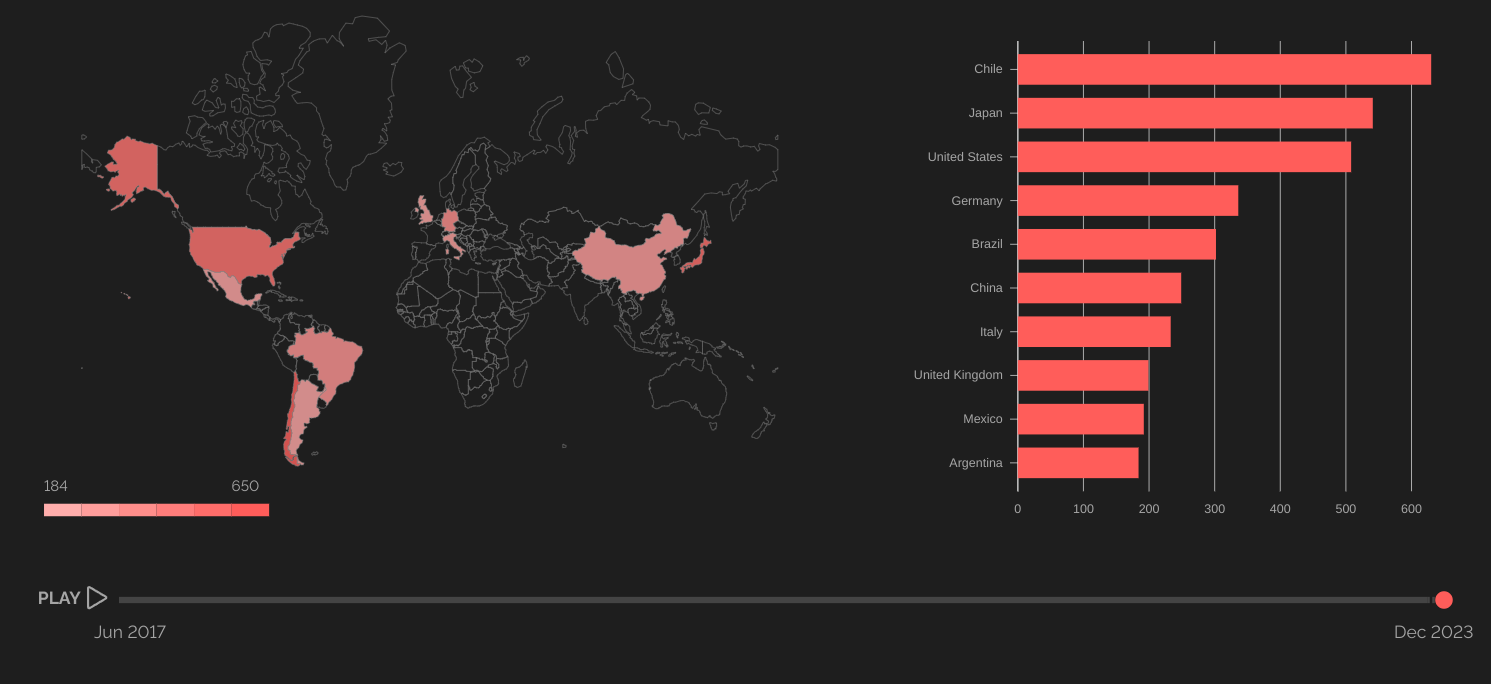
Countries Top Ranked Countries with Hipcam RealServer/V1.0 Devices

For more information on the Shodan trend of Hipcam RealServer, check Shodan Trends.

Search query used: has_screenshot:true port:554 "Hipcam RealServer/V1.0".

Disclaimer

This script is intended for educational and responsible disclosure purposes only. Unauthorized use of this script on systems without proper authorization is illegal and unethical. The user is responsible for ensuring compliance with legal and ethical standards.


Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    851
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    538
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    420
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    357
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    297
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    280

Explore all tools

Browse our collection of tools

View all tools →