
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2019-0708-scan — Batch scanner for CVE-2019-0708 (BlueKeep) RDP vulnerability with Windows and Linux support, using rdpscan and custom Cscan for mass IP range detection. | Kitploit
Tools/GitHubGitHub/lisinan988/cve-2019-0708-scan
ReconnaissanceVulnerability ScannersExploitationInformation GatheringNetwork SecurityPenetration Testing
GitHublisinan988/cve-2019-0708-scan

CVE-2019-0708-scan

Batch scanner for CVE-2019-0708 (BlueKeep) RDP vulnerability with Windows and Linux support, using rdpscan and custom Cscan for mass IP range detection.

Share
View Repository
264 years agoNot yet reviewed

Microsoft 3389 Remote Vulnerability CVE-2019-0708 Mass Detection Tool

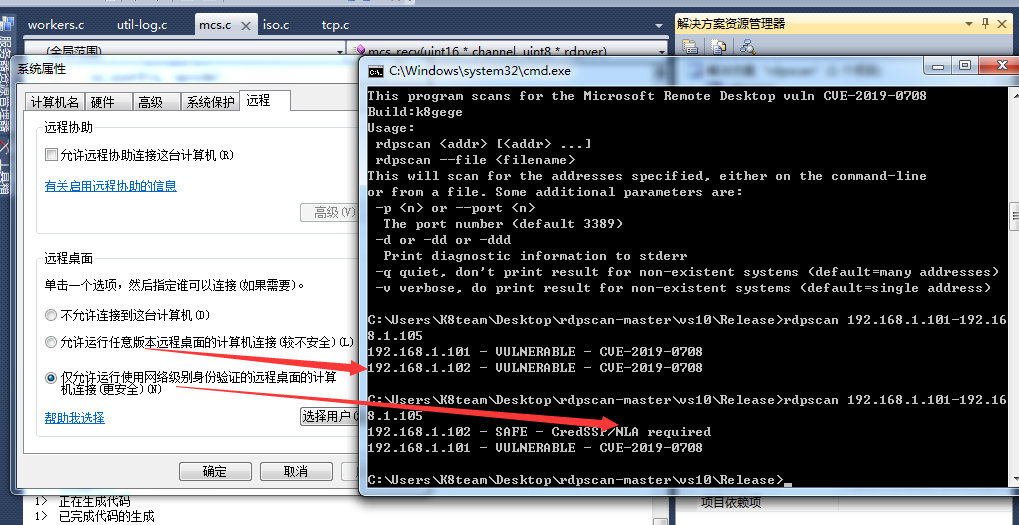
0x001 Detection on Windows

https://github.com/robertdavidgraham/rdpscan

C:\Users\K8team\Desktop\rdpscan-master\vs10\Release 的目录

2019/06/02 02:11 <DIR> . 2019/06/02 02:11 <DIR> .. 2019/06/02 01:55 2,582,016 libcrypto-1_1.dll 2019/06/02 01:57 619,520 libssl-1_1.dll 2019/06/02 02:04 172,032 rdpscan.exe 3 个文件 3,373,568 字节 2 个目录 2,462,433,280 可用字节

C:\Users\K8team\Desktop\rdpscan-master\vs10\Release>rdpscan 192.168.1.101-192.168.1.105 192.168.1.101 - VULNERABLE - CVE-2019-0708 192.168.1.102 - VULNERABLE - CVE-2019-0708

C:\Users\K8team\Desktop\rdpscan-master\vs10\Release>rdpscan 192.168.1.101-192.168.1.105 192.168.1.102 - SAFE - CredSSP/NLA required 192.168.1.101 - VULNERABLE - CVE-2019-0708

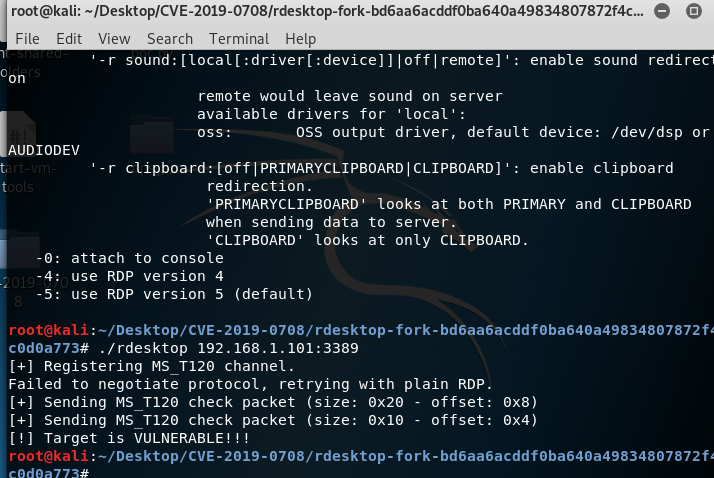
0x002 Detection on Linux

https://github.com/SugiB3o/Check-vuln-CVE-2019-0708

root@kali:~/Desktop# ./rdesktop 192.168.1.101:3389 ERROR: Failed to open keymap en-us [+] Registering MS_T120 channel. Failed to negotiate protocol, retrying with plain RDP. [+] Sending MS_T120 check packet (size: 0x20 - offset: 0x8) [+] Sending MS_T120 check packet (size: 0x10 - offset: 0x4) [!] Target is VULNERABLE!!!
 

0x003 Cscan Batch Detection

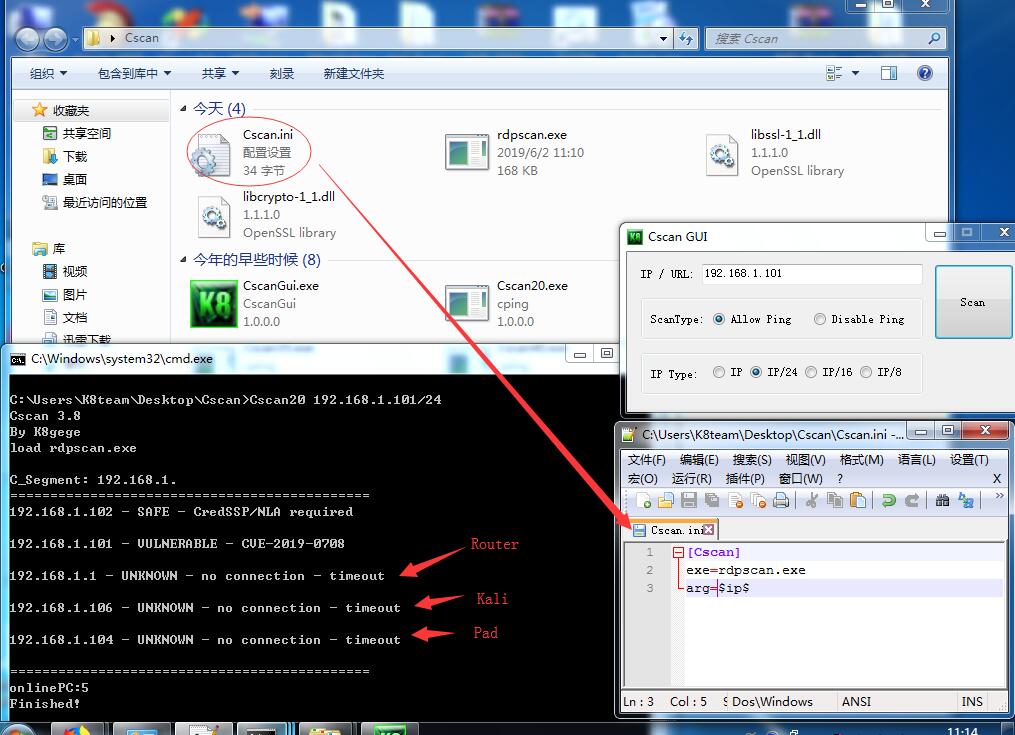
Copy rdpscan.exe and the dll files to the Cscan directory, create a new Cscan.ini file with the following content

[Cscan]
exe=rdpscan.exe
arg=$ip$

 Batch scan

Cscan.exe 192.168.1.101/24  (Scan a single C class subnet; for multiple C class subnets or B class subnets, please refer to Cscan documentation)

A GUI can be used locally (only .NET 2.0; please select the Cscan version according to your own or the target computer's .NET version)
0x004 Bin Download

Compilation on Windows may be troublesome; here we provide pre-compiled binaries.

They are the exe for Win7 x86, but it can also be used under 64-bit systems.

The executable for Kali 2019 x64; other versions compile on your own.

POC:  https://github.com/k8gege/CVE-2019-0708

Cscan: https://www.cnblogs.com/k8gege/p/10519321.html

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    911
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    548
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    366
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    362
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    311
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    287

Explore all tools

Browse our collection of tools

View all tools →





