 legus-yeung/cve-2025-55182-exploit
Proof-of-concept exploit for CVE-2025-55182, a critical unauthenticated RCE in React Server Components. Includes a Python script demonstrating malicious HTTP request crafting against vulnerable Next.js/React versions.

This repository contains a simple exploit for CVE-2025-55182, a critical remote code execution vulnerability in React Server Components.
CVE-2025-55182 is an unauthenticated remote code execution vulnerability in React Server Components (CVSS 10.0). The vulnerability affects how React decodes payloads sent to React Server Function endpoints, allowing an attacker to craft malicious HTTP requests that achieve remote code execution on the server.
react-server-dom-webpack: 19.0, 19.1.0, 19.1.1, 19.2.0react-server-dom-parcel: 19.0, 19.1.0, 19.1.1, 19.2.0react-server-dom-turbopack: 19.0, 19.1.0, 19.1.1, 19.2.0react-server-dom-webpack: 19.0.1, 19.1.2, 19.2.1react-server-dom-parcel: 19.0.1, 19.1.2, 19.2.1react-server-dom-turbopack: 19.0.1, 19.1.2, 19.2.1The exploit.py script demonstrates how an attacker could exploit this vulnerability by crafting a malicious HTTP request to a React Server Function endpoint.
Note: This exploit only works against vulnerable versions of Next.js and React. After updating to the patched versions, the exploit will no longer function.
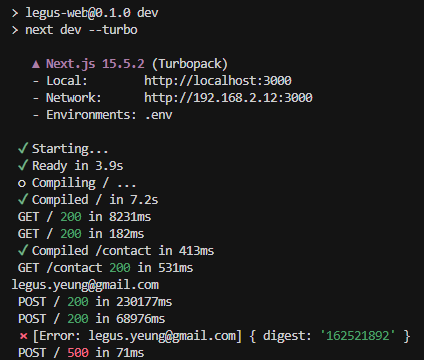
The exploit script targeting a vulnerable Next.js application:
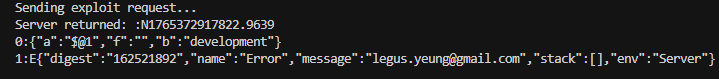
The same exploit script after updating Next.js and React - the exploit no longer works:

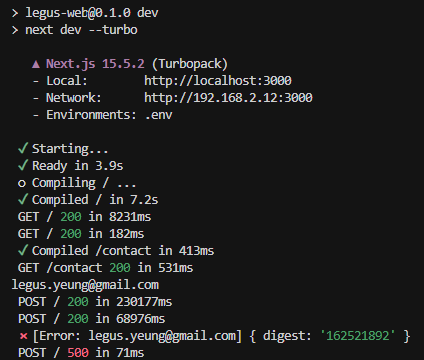
Example output showing the exploit in action:
This vulnerability allows unauthenticated remote code execution on servers running vulnerable versions of React Server Components. Even if your application doesn't explicitly implement React Server Function endpoints, it may still be vulnerable if it supports React Server Components.
Immediate action required: Upgrade to the latest patched versions:
npm install next@latest
npm install react@latest react-dom@latest react-server-dom-webpack@latest
This exploit is provided for educational and security research purposes only. Do not use this code against systems you do not own or have explicit permission to test. Unauthorized access to computer systems is illegal.
