Skip to content
KitploitKITPLOIT
ToolsBlog
Log in
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Get-log4j-Windows-local — Identifying all log4j components across on local windows servers. CVE-2021-44228 | Kitploit

Tools/GitHubGitHub/keysau/get-log4j-windows-local
ReconnaissanceVulnerability ScannersPort ScanningVulnerability AnalysisExploitationInformation Gathering
GitHubkeysau/get-log4j-windows-local

Get-log4j-Windows-local

Identifying all log4j components across on local windows servers. CVE-2021-44228

View Repository
51384 years agoNot yet reviewed
Share

Get-log4j-Windows-local.ps1

Identify all log4j components on a single local windows servers. CVE-2021-44228. A single use copy - see https://github.com/KeysAU/Get-log4j-Windows.ps1 for multi computer.

Apache log4j

CVE-2021-44228

Script Running:

image

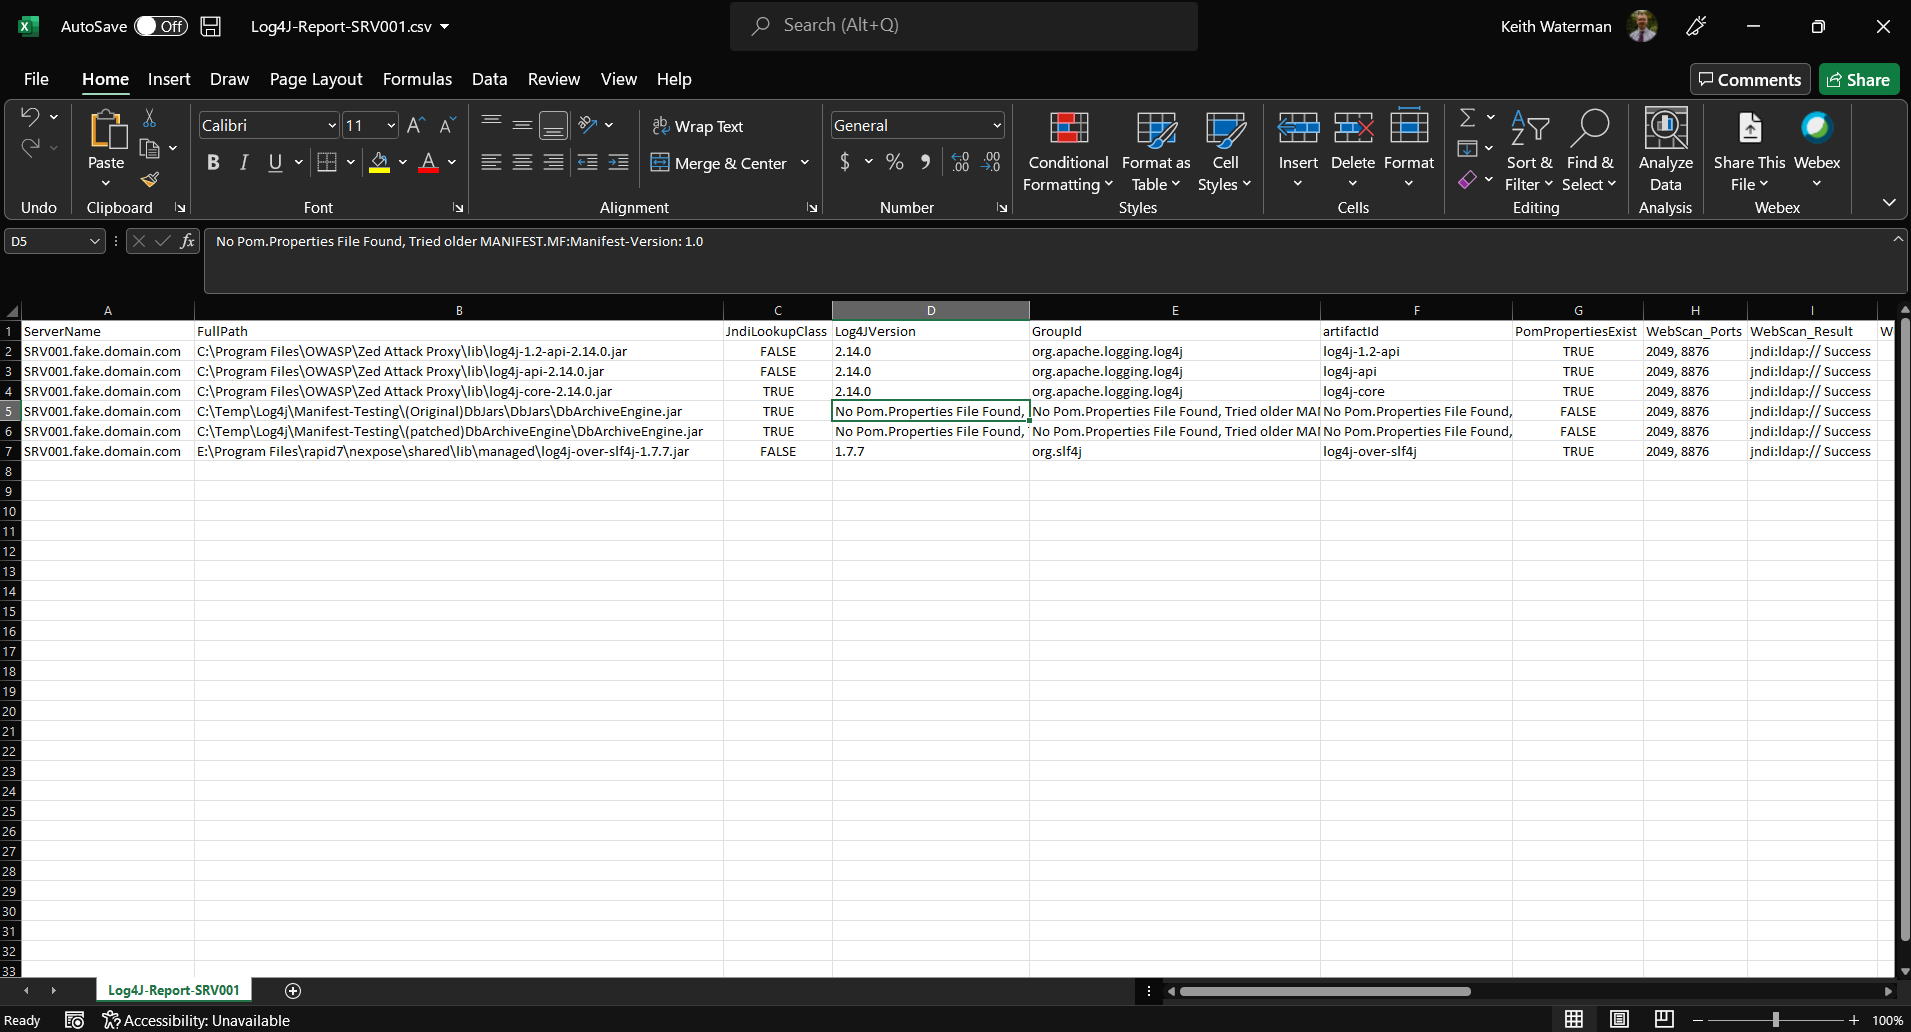
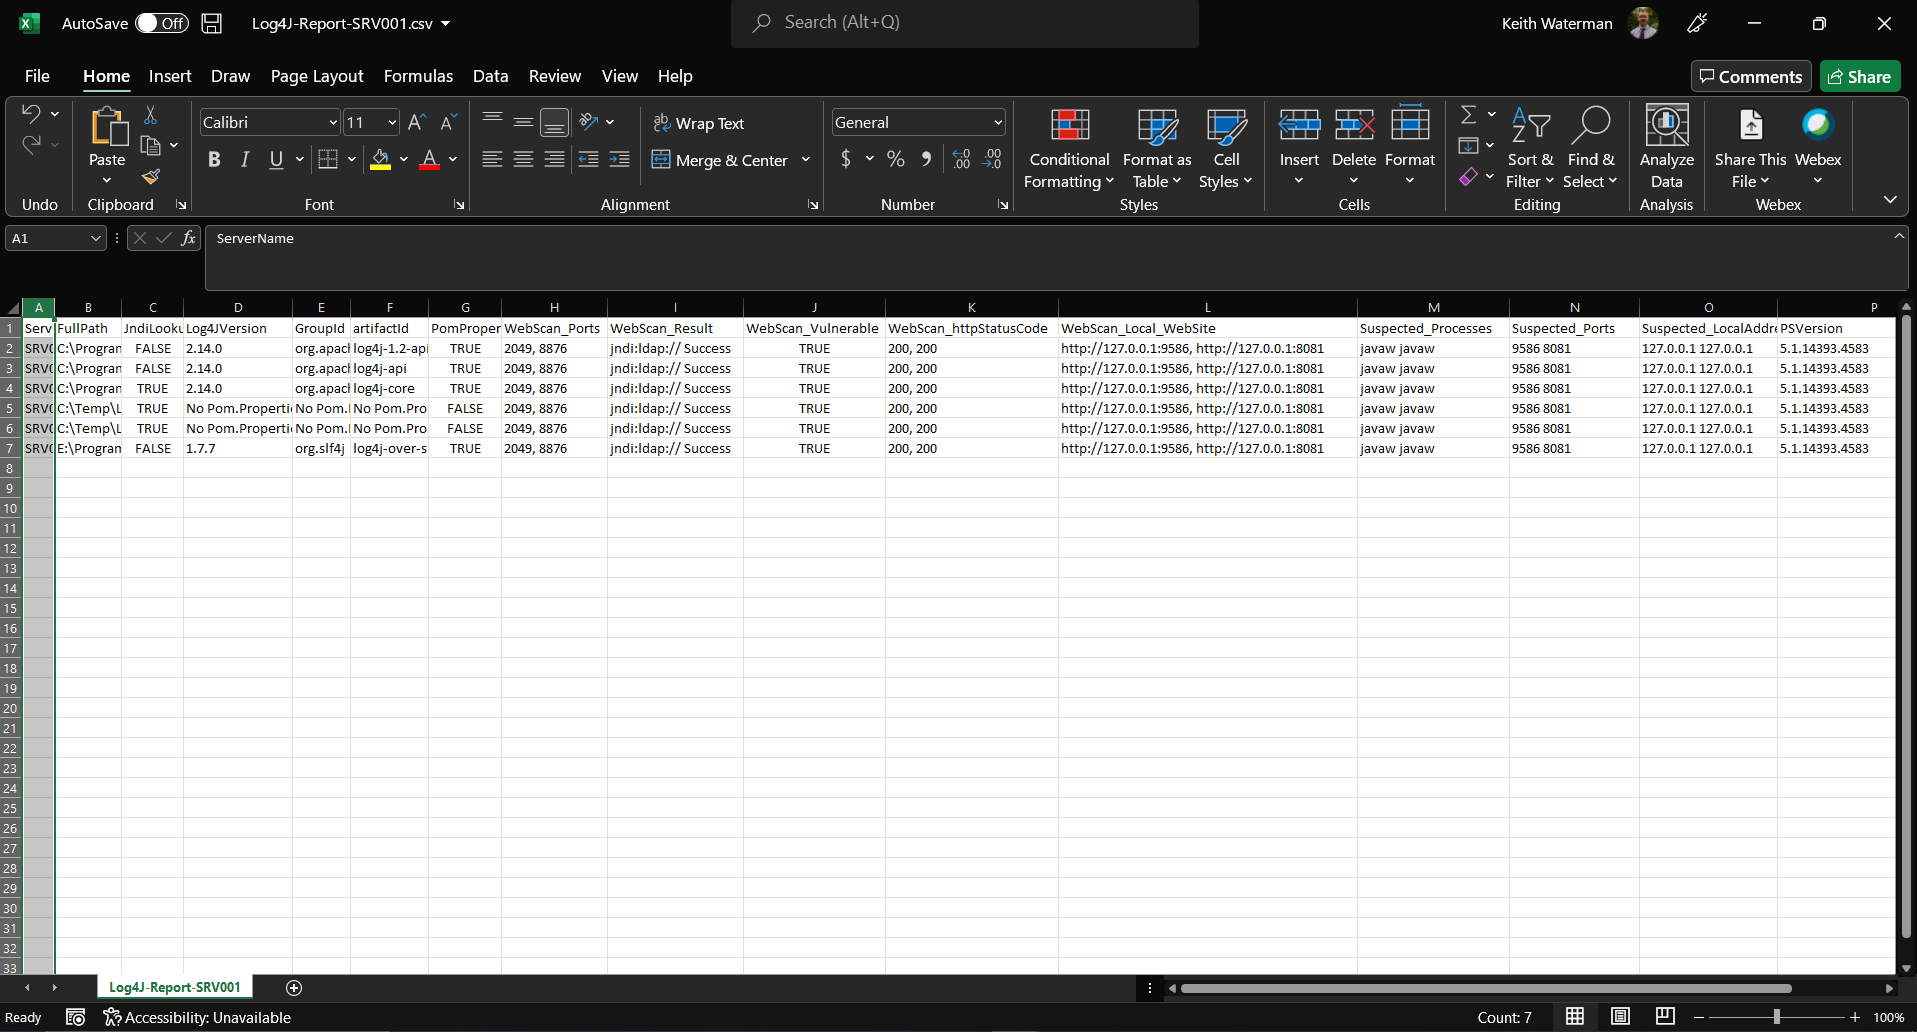
Export:

Columns A - I: image

Continued: image

Description:

          Local run version for a single server.            
          Sets up working directory C:\Temp\log4j on local server.
          Recursevly scans all drives for .jar containers.
          Extracts all .jar with 7-zip.exe to C:\temp\log4j\Extracted           
          Gets version number of log4j version.
          Checks if log4j jindiLookup.class file exists of log4j version.
          Scans all local listening IP ports and attempts to exploit with http header.
          Captures failed ps jobs, and closes stuck jobs.
          Dynamically creates csv of where embedded log4j module was located, 
              if web exploitation was possible and if contains jindilookup.class file.
			

Created for:

          Identifying all log4j components on local windows server. CVE-2021-44228

Dependencies:

          You must install 7-zip.exe in C:\support\tools\7-zip on the local server (x32 bit suggested)
          PowerShell 5.0+
          Must run as a local admin or equivalent permissions to scan all drives

Change Log:

    15-Dec-2021  -Change Notes: Initial local copy version.
    19-Dec-2021  -Change Notes: Added scanning for jindiLookup.class
    19-Dec-2021  -Change Notes: Added local listening port scan and exploitation attempt

Notes:

    No modification, will out out of the box. Note you still need 7zip.

Licence:

Open-sourced software licensed under the MIT license.

Author:

     Keith Waterman

Date :

    19-Dec-2021
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    851
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    538
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    420
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    357
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    297
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    280

Explore all tools

Browse our collection of tools

View all tools →