
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Horn3t — Powerful Visual Subdomain Enumeration at the Click of a Mouse | Kitploit

Tools/GitHubGitHub/janniskirschner/horn3t
ReconnaissanceInformation GatheringWeb SecurityPenetration TestingSubdomain Enumeration
GitHubjanniskirschner/horn3t

Horn3t

Powerful Visual Subdomain Enumeration at the Click of a Mouse

View Repository
13826367 years agoReviewed by Kitploit
Share

Horn3t 🐝 - Better Subdomain Reconnaissance

logo
  • Recon your targets at blazing speed
  • Enhance your productivity by focusing on interesting looking sites
  • Enumerate critical sites immediately
  • Sting your target

Horn3t is your Nr #1 tool for exploring subdomains visually.
Building on the great Sublist3r framework (or extensible with your favorite one) it searches for subdomains and generates awesome picture previews. Get a fast overview of your target with http status codes, add custom found subdomains and directly access found urls with one click.
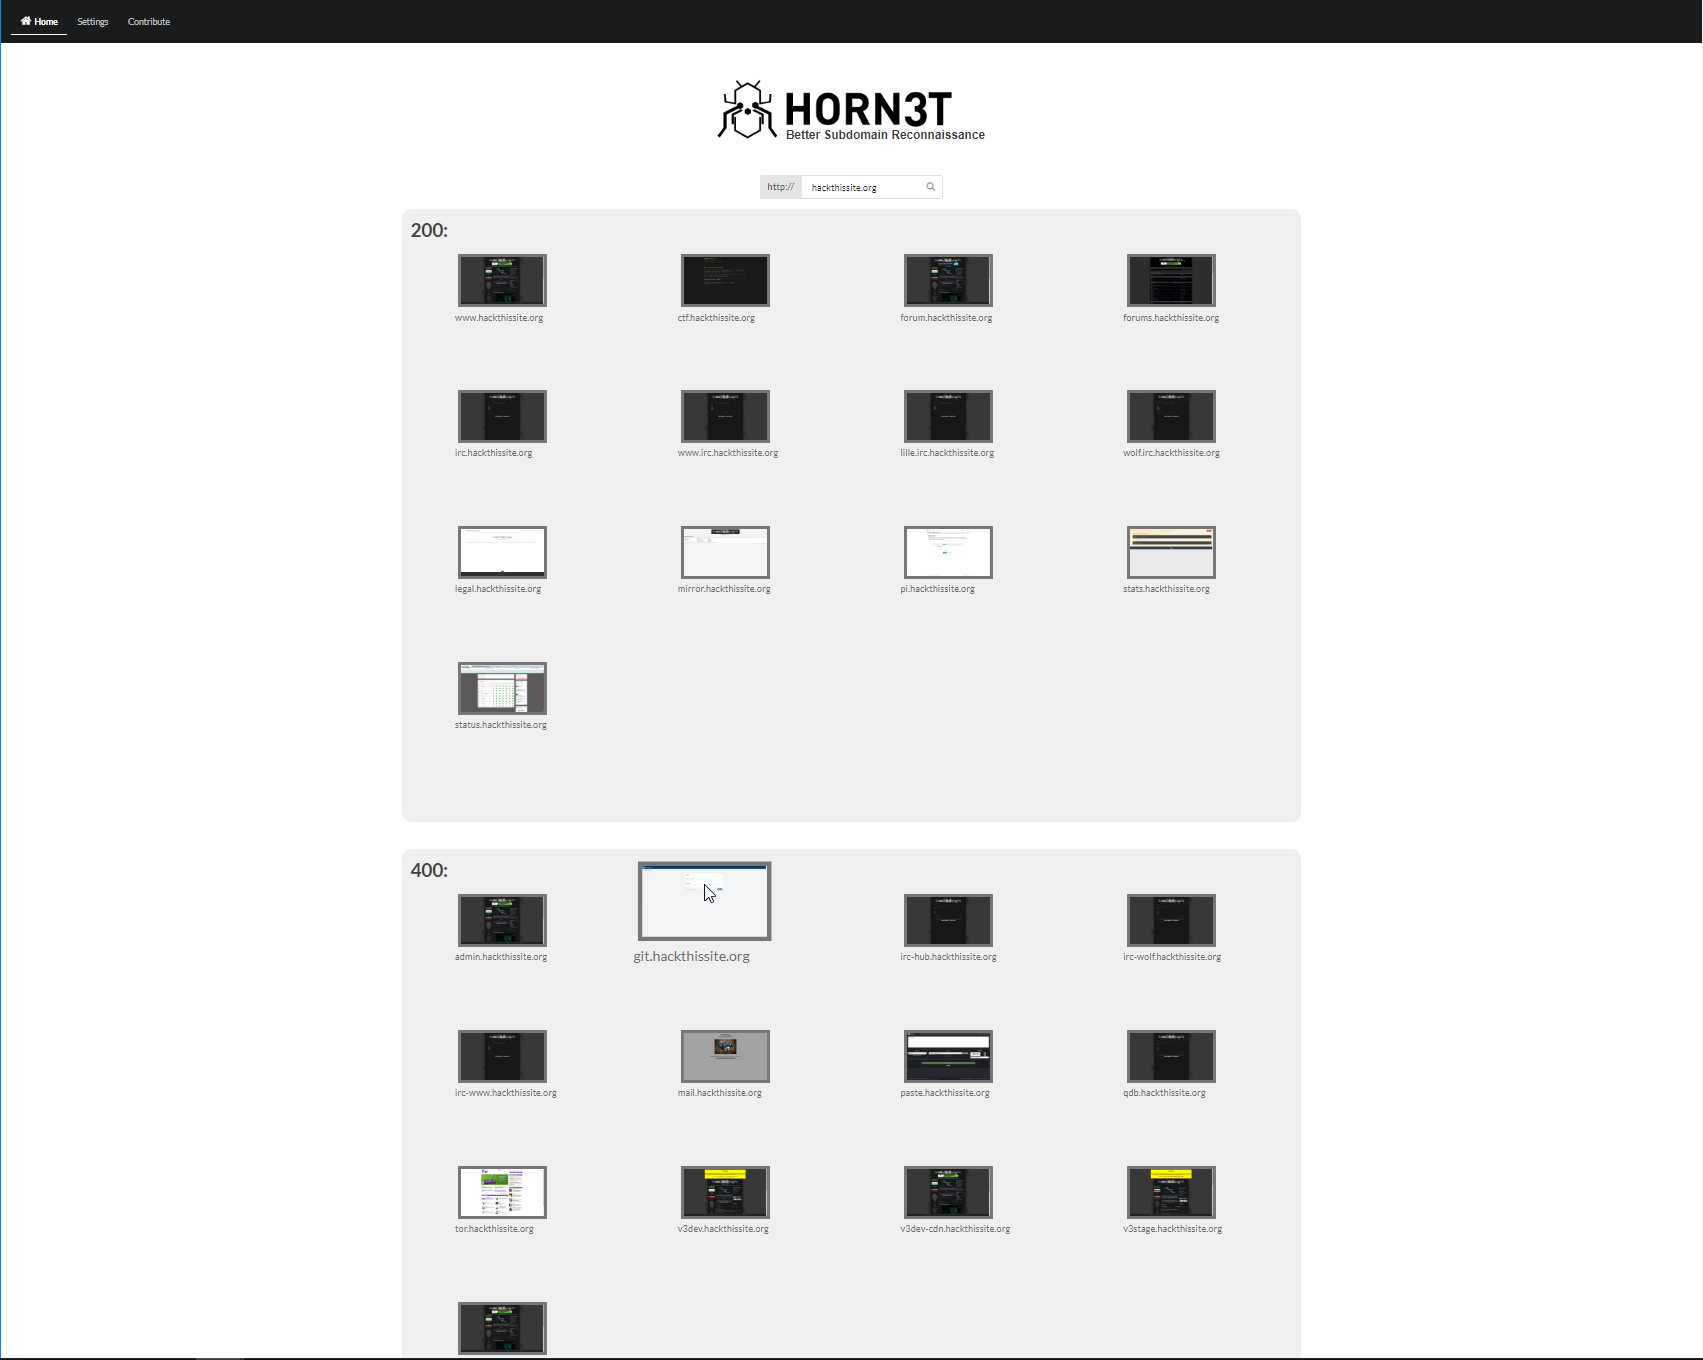
demo preview

Installation

  • Install Google Chrome
  • Install requirements.txt with pip3
  • Install requirements.txt of sublist3r with pip3
  • Put the directory within the web server of your choice
  • Make sure to have the right permissions
  • Run horn3t.py

Or alternatively use the install.sh file with docker.
Afterwards you can access the web portal under http://localhost:1337

Todo

  • Better Scaling on Firefox
  • Add Windows Dockerfile
  • Direkt Nmap Support per click on a subdomain
  • Direkt Dirb Support per click on a subdomain
  • Generate PDF Reports of found subdomains
  • Assist with subdomain takeover

License

Horn3t is licensed under the GNU GPL license. take a look at the LICENSE for more information.

Respect legal restrictions and only conduct testing against infrastructure that you have permission to target.

Credits

  • aboul3la - The creator of Sublist3r; turbolist3r adds some features but is otherwise a near clone of sublist3r.
  • TheRook - The bruteforce module was based on his script subbrute.
  • bitquark - The Subbrute's wordlist was based on his research dnspop.

Tested on Windows 10 and Debian with Google Chrome/Chromium 73

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    831
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    534
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    429
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    355
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    284
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    275

Explore all tools

Browse our collection of tools

View all tools →





