Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
unicorn_pe — Emulates Windows PE execution using Unicorn engine for malware analysis, unpacking packed binaries, and decrypting VMProtect strings and imports. | Kitploit
Tools/GitHubGitHub/hzqst/unicorn_pe
Dynamic Analysis (Sandboxing)ExploitationReverse EngineeringFuzzingMalware AnalysisBinary AnalysisArchived
GitHubhzqst/unicorn_pe

unicorn_pe

Emulates Windows PE execution using Unicorn engine for malware analysis, unpacking packed binaries, and decrypting VMProtect strings and imports.

View Repository
9272064710 months agoNot yet reviewed
Share

Unicorn PE

Unicorn PE is an unicorn based instrumentation project/framework designed to emulate code execution for windows PE files, especially packed ones.

  • This project is archived and no longer maintained. sogen is recommended as a successor.

Feature

Dump PE image from emu-memory into file, fix import table, decrypt VMProtect strings, decrypt VMProtect imports.

Partial support for exception. (only #DB and #BP)

Show disasm for all instructions that is being executed.

Update BlackBone to latest ver (2020.4.5).

TODO

Feature: x86 (low priority) -- 0%

Build

Visual Studio 2017 or 2019

Open unicorn_pe.sln with Visual Studio

Build project "unicorn_pe" as x64/Release or x64/Debug. (No x86 support for now)

Usage

unicorn_pe (filename or filepath) [-k for kernel mode driver emulation] [-disasm for displaying disasm] [-dump for binary dump] [-packed for packed binary] [-boundcheck for memory access bound check, may slower the execution]

Programming

...to be documented

Snapshots

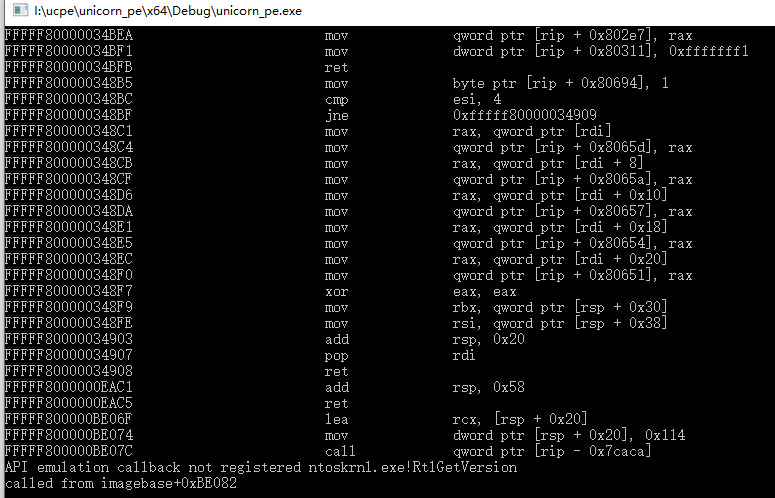
original driver

1

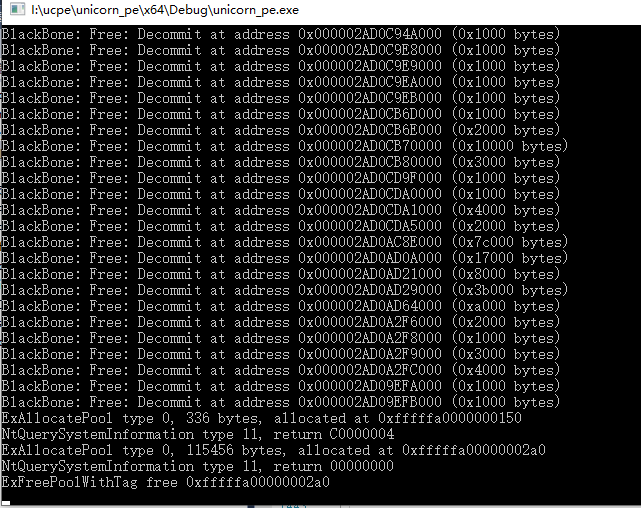
vmprotect packed driver

2

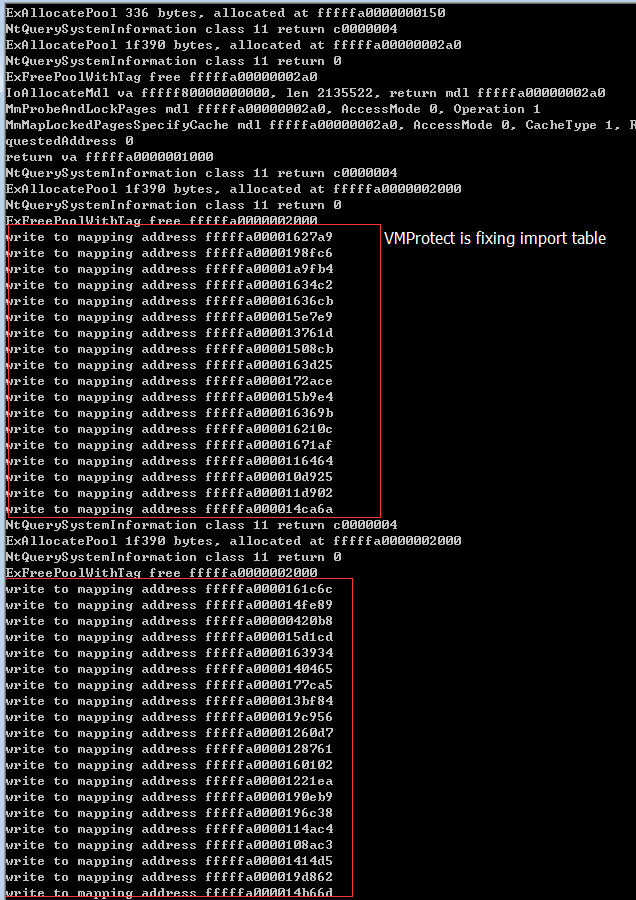
vmprotect is fixing encrypted IAT

3

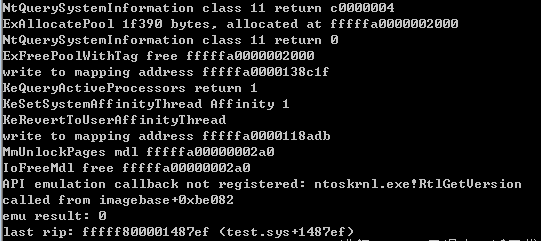
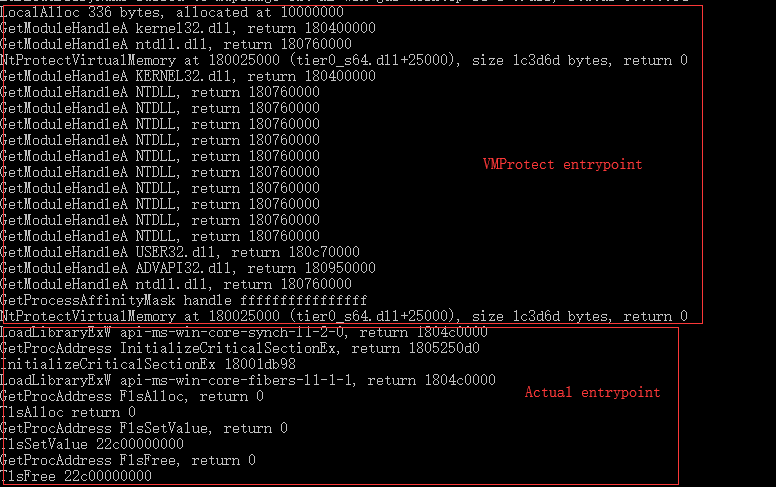
vmprotect goes back to original entry point

4

vmprotect packed DLL, full user-mode emulation.

4

License

This software is released under the MIT License, see LICENSE.

Dependencies

A modification of https://github.com/DarthTon/Blackbone is done for PE manual-mapping.

https://github.com/unicorn-engine/unicorn for emulation.

https://github.com/aquynh/capstone for disasm.

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    938
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    556
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    352
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    343
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    336
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    291

Explore all tools

Browse our collection of tools

View all tools →