Backported Debian and Enterprise Linux NGINX packages with reviewed patches for the nginx2root CVEs, plus reproducible build scripts, checksums, and installer upgrade tests.

Backported Debian and Enterprise Linux packages for the November 2026 NGINX security fixes, built by Hosted Power. The repository contains the exact patches, pinned source inputs, reproducible build scripts, and package-upgrade tests.
These packages contain the complete fixes for every nginx2root vulnerability that applies to each release. They are not a mitigation and need no follow-up.
The packages preserve the distribution build configuration and package layout. Their versions are deliberately ordered below the next distribution update, so if your distribution ships its own update later, it takes over automatically through normal package upgrades.
Current status (19 November 2026): v1.7.0 contains native RHEL 10, Rocky
Linux 10, and Oracle Linux 10 package families. v1.6.1 contains native RHEL 8
and Rocky Linux 8 AppStream 1.24 package families. v1.4.0 contains 13 native EL9 vendor/stream package
families, alongside the existing Debian and CentOS 7/8 releases. The signed Hosted Power APT
repository also carries the complete Debian 12 and 13 hp3 package sets. Debian
12 currently selects hp3. Debian 13 now selects Debian's newer
1.26.3-3+deb13u11 automatically; inspection of that source package confirms
that it contains all nine applicable NGINX 1.30.7 security patches listed here.
Disabling HTTP/2 does not fix nginx2root. It only blocks CVE-2026-123007 and CVE-2026-123633. The other three stay open: the resolver (CVE-2026-123634), the mail proxy (CVE-2026-113425) and HTTP/3 (CVE-2026-121810). It also costs performance for every client. These packages fix all applicable issues, so HTTP/2 can stay enabled.
If you disabled HTTP/2 as a stopgap: install the packages (the upgrade restarts
NGINX), re-enable HTTP/2 (listen 443 ssl http2; on Debian 9–12 and CentOS 7/8,
http2 on; on Debian 13), then run nginx -t and reload.
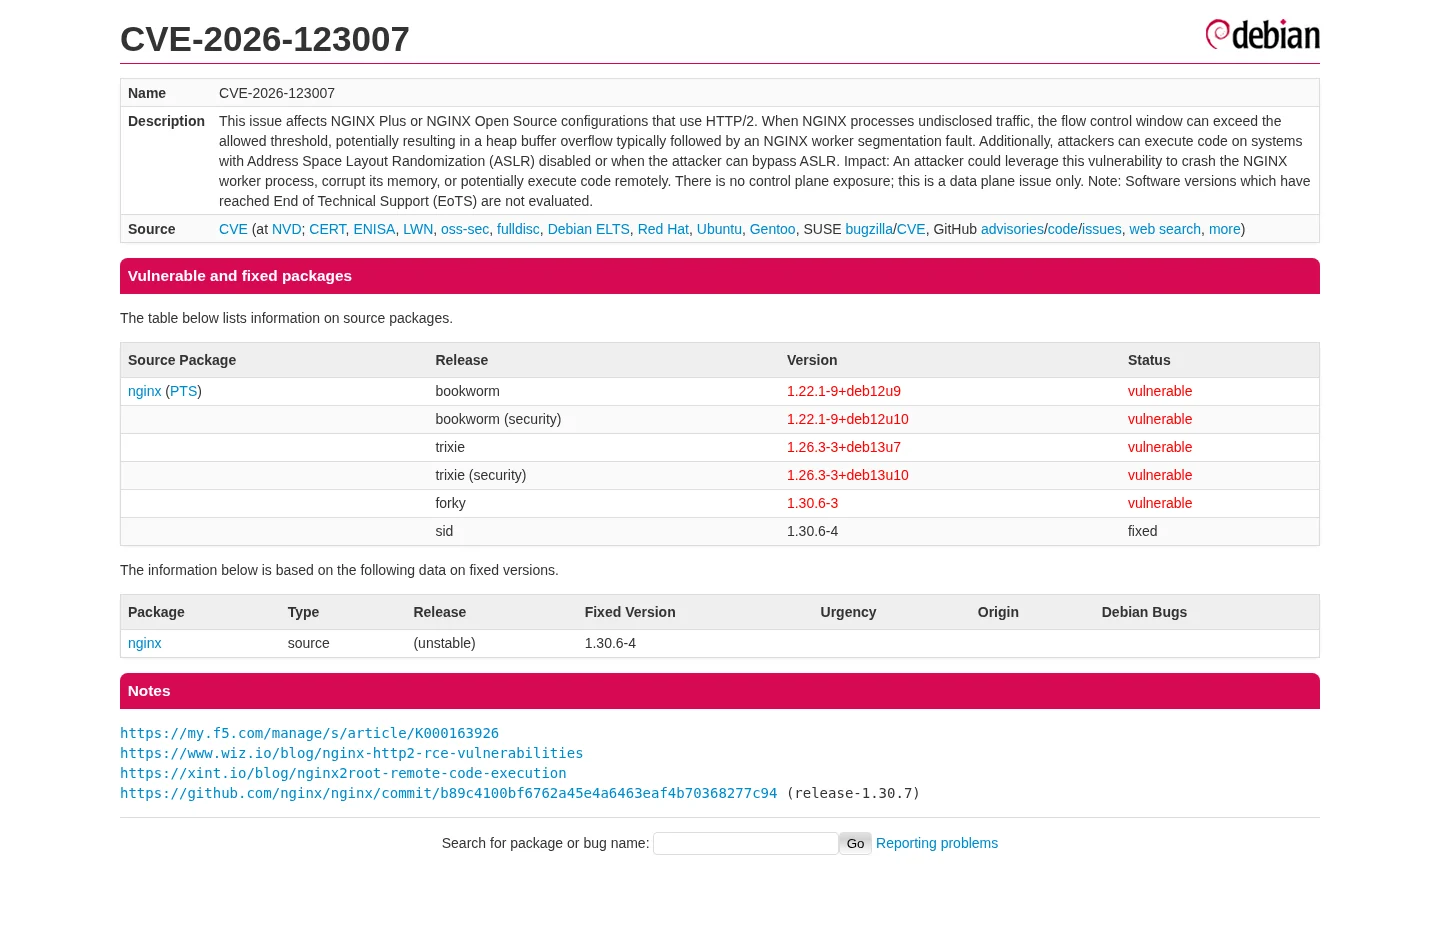
Debian Security Tracker on 19 November 2026. Click the screenshot for the live status.
The v1.3.2 release contains complete x86-64 package sets. Its hp3 package
revision upgrades the earlier builds while remaining below the next distribution
update. Every package changelog names each included CVE explicitly, so standard
installed-package changelog checks, rpm -q --changelog, and CVE audit tools
recognize the fixes. On Debian, inspect the installed evidence directly with
zgrep CVE-2026 /usr/share/doc/nginx/changelog.Debian.gz; apt changelog
consults repository metadata and is not reliable for third-party packages:
| Debian | Base package | Hotfix package | Included fixes |
|---|---|---|---|
| 8 Jessie | 1.6.2-5+deb8u10 | 1.6.2-5+deb8u10.1~hp3 | CVE-2026-113425, CVE-2026-123634, CVE-2026-125283 |
| 9 Stretch | 1.10.3-1+deb9u10 | 1.10.3-1+deb9u10.1~hp3 | CVE-2026-113425, CVE-2026-123007, CVE-2026-123633, CVE-2026-123634, CVE-2026-125283 |
| 10 Buster | 1.14.2-2+deb10u9 | 1.14.2-2+deb10u9.1~hp3 | the Stretch fixes plus CVE-2026-118899 and CVE-2026-123640 |
| 11 Bullseye | 1.18.0-6.1+deb11u9 | 1.18.0-6.1+deb11u9.1~hp3 | the same seven fixes as Buster |
| 12 Bookworm | 1.22.1-9+deb12u10 | 1.22.1-9+deb12u10.1~hp3 | the same seven, plus CVE-2026-15176, CVE-2026-93479, CVE-2026-97205 and additional CVE-2023-44487 hardening |
| 13 Trixie | 1.26.3-3+deb13u10 | 1.26.3-3+deb13u10.1~hp3 | all nine applicable NGINX 1.30.7 fixes, including CVE-2026-120967 and CVE-2026-121810 |
Debian's official Trixie 1.26.3-3+deb13u11 package now supersedes the Trixie
hotfix through normal version ordering. Its source has the same nine relevant
patches, including the HTTP/2, resolver, mail, QUIC, request-body, stream SNI,
ssl_preread, and try_files fixes. The Debian security tracker may lag the
package archive briefly while its fixed-version data is updated.
Debian 8 NGINX predates HTTP/2, so CVE-2026-123007 and CVE-2026-123633 do not apply. Its package contains all three fixes applicable to that old source tree. Debian 8 through 11 use source packages from Freexian Extended LTS. Their older NGINX trees require small context adaptations and, for Debian 9 and 10, the upstream SMTP duplicate-resolution prerequisite from 2019. Every adapted source tree is checked for the security-sensitive conditions before it is built.
| Distribution | Base package | Hotfix package | Included fixes |
|---|---|---|---|
| CentOS 7 archived EPEL | 1:1.20.1-10.el7 | 1:1.20.1-10.el7.0.1.hp3 | seven applicable fixes: CVE-2026-113425, CVE-2026-118899, CVE-2026-123007, CVE-2026-123633, CVE-2026-123634, CVE-2026-123640, CVE-2026-125283 |
| CentOS 8 AppStream 1.14 (original/default) | 1:1.14.1-9.module_el8.0.0+184+e34fea82 | 1:1.14.1-9.module_el8.0.0+184+e34fea82.0.1.hp3 | the same seven applicable fixes |
| CentOS 8 AppStream 1.16 | 1:1.16.1-2.module_el8.4.0+820+127618ce.1 | 1:1.16.1-2.module_el8.4.0+820+127618ce.1.0.1.hp3 | the same seven applicable fixes |
| CentOS 8 AppStream 1.18 | 1:1.18.0-3.module_el8.4.0+818+5ada96a6.1 | 1:1.18.0-3.module_el8.4.0+818+5ada96a6.1.0.1.hp3 | the same seven applicable fixes |
| CentOS 8 AppStream 1.20 | 1:1.20.0-2.module_el8.5.0+899+43b718f6 | 1:1.20.0-2.module_el8.5.0+899+43b718f6.0.1.hp3 | the same seven applicable fixes |
The CentOS 7 package set targets only NGINX installed from the archived EPEL 7 package family. The installer rejects nginx.org, control-panel, and other package families rather than attempting an unsafe cross-vendor replacement.
CentOS Linux 8 shipped NGINX through AppStream from its first 1.14 default stream onward. Separate bundles preserve the exact package version, module stream identity, modularity label, package layout, and ABI for each of the four final official CentOS Linux 8 streams. The installer upgrades only an exact matching package family and rejects cross-stream or cross-vendor replacement.
AlmaLinux now has complete official fixes for the five headline NGINX2Root CVEs
on every supported stream. The follow-up packages matter: on AlmaLinux 9 these
are the default 1.20 .alma.4, 1.24 .alma.4, and 1.26 .alma.2 builds; on
AlmaLinux 10 it is the 1.26 .alma.3 build. Earlier .alma.2/.alma.3 packages
from the initial advisories fixed only the two HTTP/2 issues. Update from the
normal AlmaLinux repositories rather than installing a CentOS bundle:
sudo dnf update nginx 'nginx-*'
sudo nginx -t
The CentOS Linux 8 bundles must not be installed on AlmaLinux. Retired
AlmaLinux 8 streams 1.14, 1.16, 1.18, 1.20, and 1.22 should be migrated to the
supported 1.24 stream. AlmaLinux 9's retired 1.22 stream has not received these
fixes. The v1.4.0 release includes an exact native package for that retired
stream where an immediate stream migration is not practical.
RHEL 8 and Rocky Linux 8 still ship vulnerable NGINX 1.24 AppStream families.
The v1.6.1 release provides separate native hotfixes with all seven applicable
fixes. Each preserves that vendor's exact package split, configuration, ABI,
release lineage, and module identity:








