 giki-shergill/cve-2026-123014---iterm2-terminal
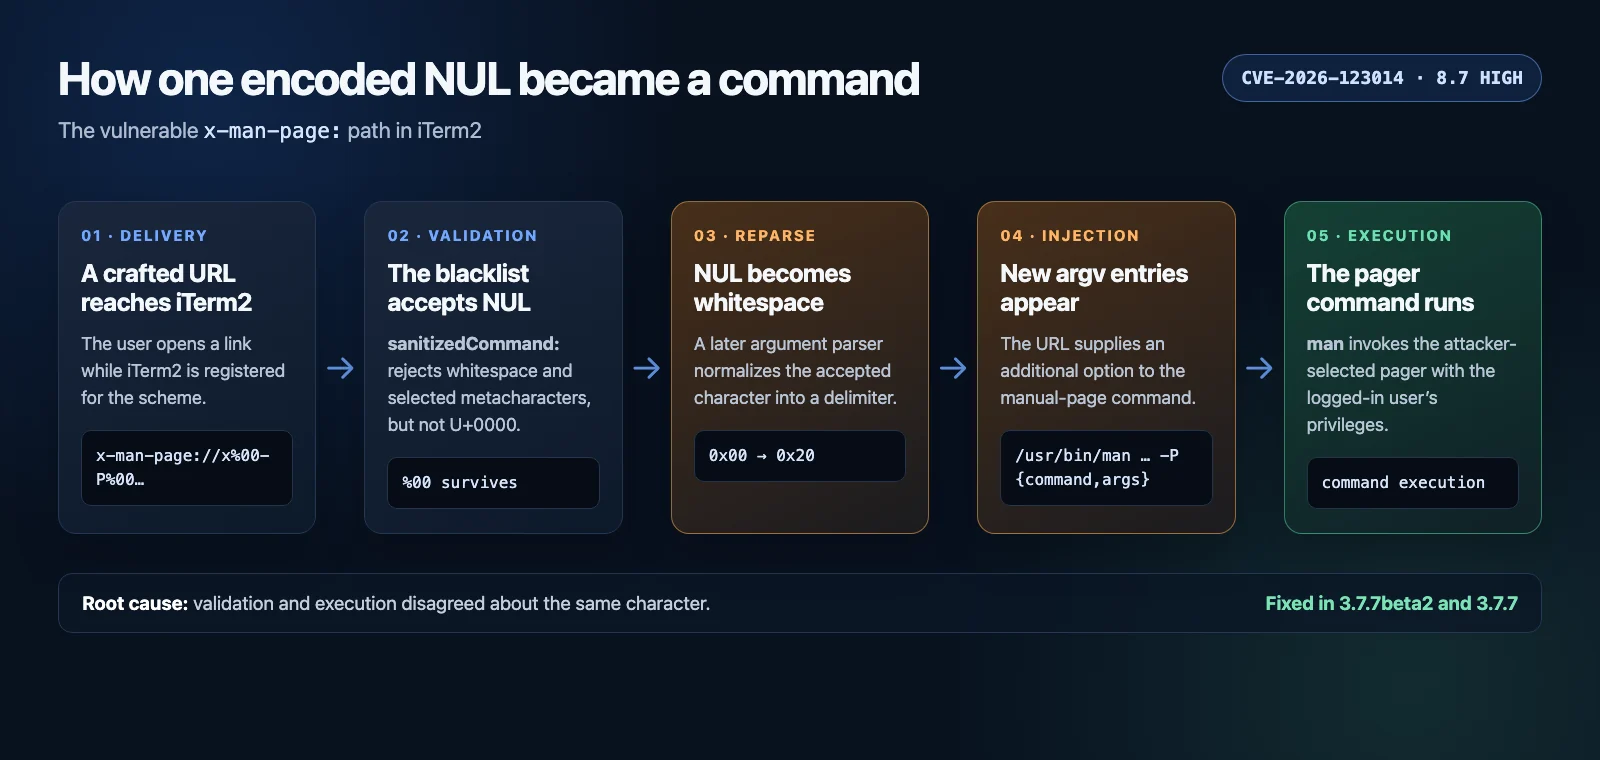
PoC and research for CVE-2026-123014: iTerm2 x-man-page NUL-byte argument injection.

Harmless proof-of-concept material for the iTerm2 x-man-page: NUL-byte argument-injection vulnerability. A percent-decoded NUL survived sanitizedCommand: and was later converted to a space during command-line parsing, allowing an additional /usr/bin/man -P option and command execution as the logged-in user.
Run only on a Mac and iTerm2 installation you own or are explicitly authorized to test:
zsh poc.zsh
On a vulnerable build, the script prints:
VULNERABLE: command execution confirmed
The payload only creates a temporary empty canary file. The script removes the file when it exits. A fixed build should reject the URL and should not create the canary.
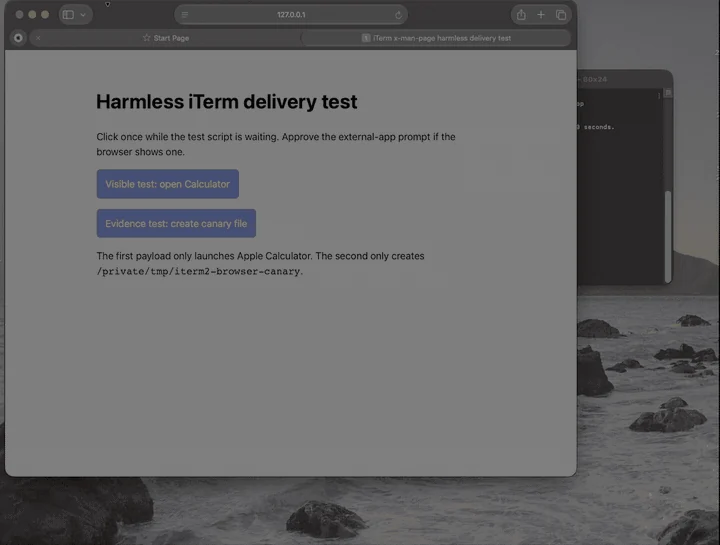
The browser harness temporarily selects iTerm2 as the handler for x-man-page:, serves the included page on 127.0.0.1, opens it in Safari, and restores the original handler on exit:
zsh browser_delivery_test.zsh
Safari or macOS may show an external-application confirmation. That user interaction is part of the documented attack model.
Reported by Gurpreet Shergill (@giki-shergill).






