
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/gagaltotal/cve-2026-60004-poc-gitea
ReconnaissanceVulnerability AnalysisExploitationWeb Application ExploitationWeb SecurityPenetration Testing
GitHubgagaltotal/cve-2026-60004-poc-gitea

CVE-2026-60004-poc-gitea

CVE-2026-60004 — Gitea Pre-Auth RCE via diffpatch hook injection

View Repository
1513 months agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    930
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    554
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    354
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    349
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    326
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    289

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2026-60004 Proof-of-Concept (PoC)

Overview

This repository contains a proof-of-concept tool for CVE-2026-60004, an authenticated or pre-auth remote code execution (RCE) vector affecting certain Gitea versions via the diffpatch hook injection technique. The primary implementation is a single Go program that performs detection and exploitation flows.

Repository contents

  • https://github.com/gagaltotal/CVE-2026-60004-poc-gitea — Main Go source file implementing detection, exploit delivery, and optional output retrieval.
  • backup.txt — miscellaneous notes/backups.
  • images/ — supporting images used for documentation.

Important notice and legal / ethical use

This PoC demonstrates exploitation techniques that can compromise remote systems. It is provided for research, testing, and defensive purposes only. Do not run this tool against systems you do not own or do not have explicit permission to test. The author and contributors are not responsible for misuse.

Requirements

  • Go toolchain (Go 1.18+ recommended)
  • Network access to the target Gitea instance
  • Optional: an HTTP proxy for debugging (e.g. Burp)

Build

From the repository root run:

go build -o cve-2026-60004-poc cve-2026-60004-poc.go

Usage

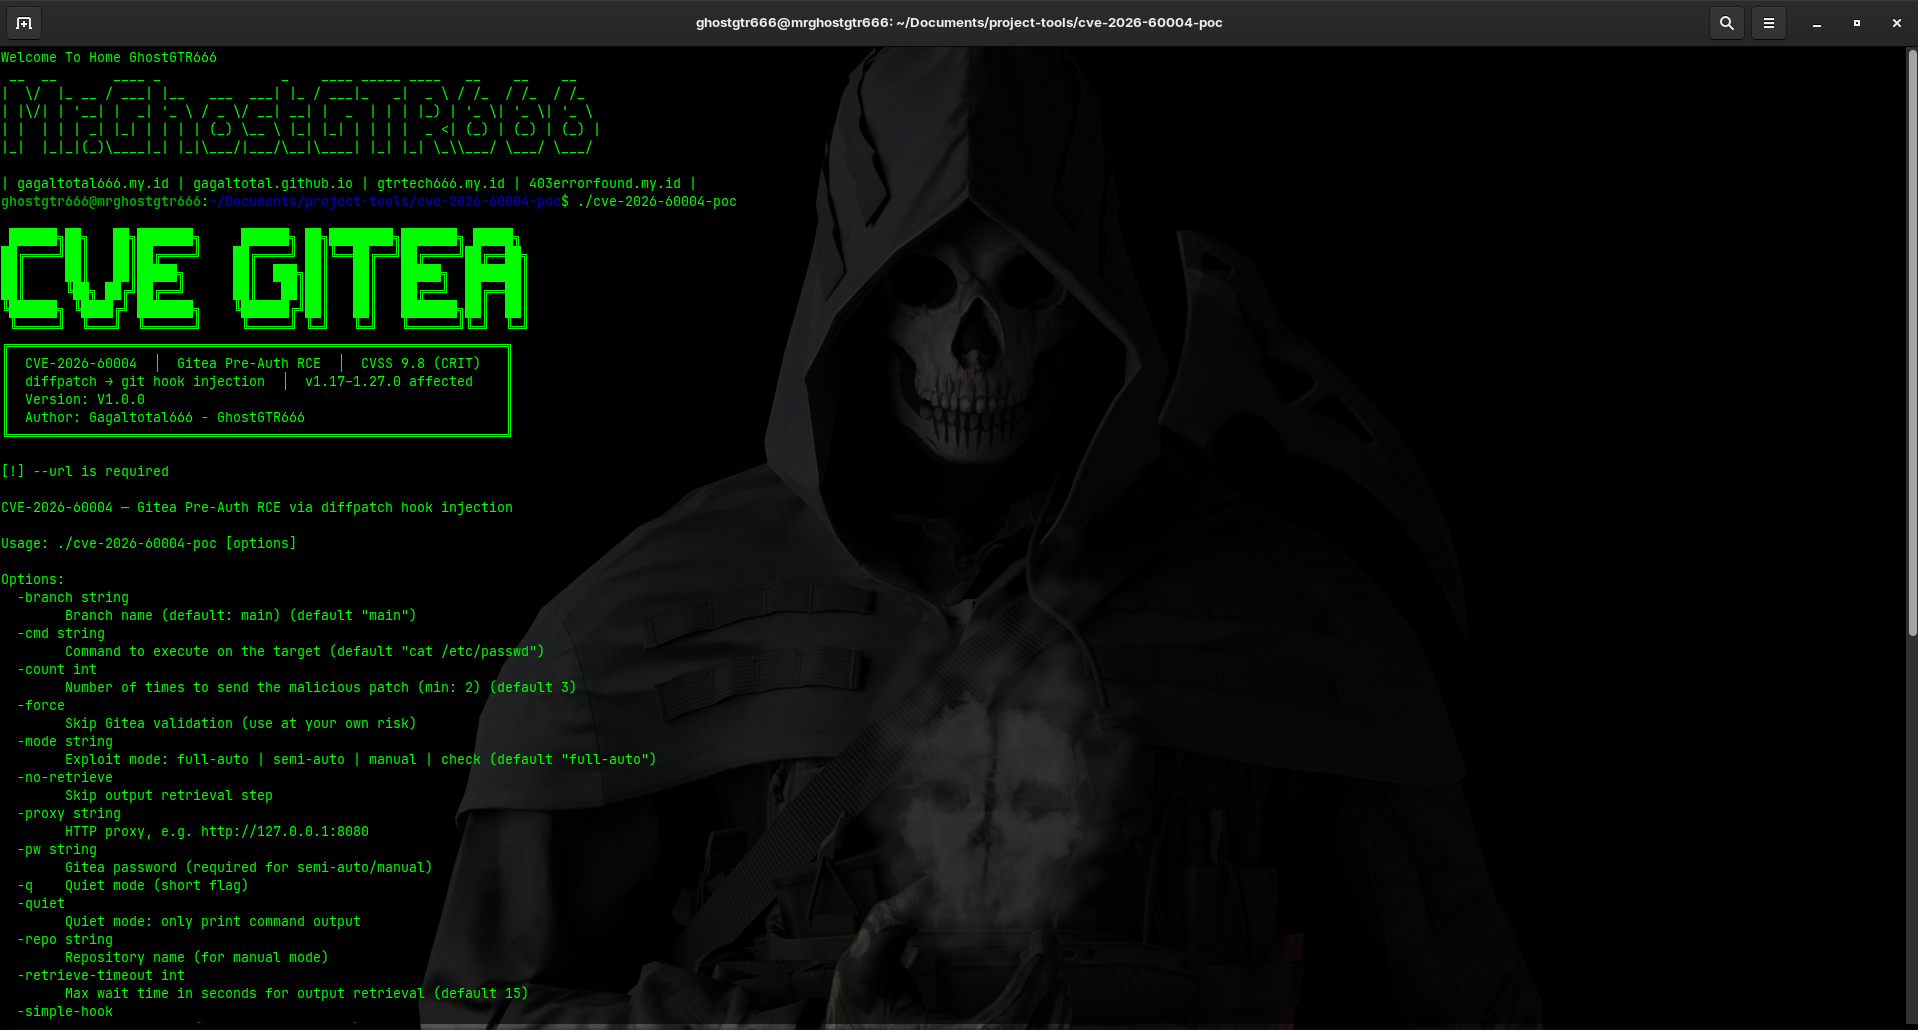
The compiled binary supports multiple modes: full-auto, semi-auto, manual, and check.

Examples

Screen Capture

Non-intrusive detection

Screen Capture

./cve-2026-60004-poc --url http://target:3000 --mode check

Full-auto (registers a user, creates repo, attempts exploit)

./cve-2026-60004-poc --url http://target:3000 --mode full-auto

Semi-auto (use existing credentials)

./cve-2026-60004-poc --url http://target:3000 --mode semi-auto --user attacker --pw 'P@ssw0rd'

Manual (existing user+repo, exploit only)

./cve-2026-60004-poc --url http://target:3000 --mode manual --user attacker --pw 'P@ssw0rd' --repo myrepo

Use a custom command and retrieve output

./cve-2026-60004-poc --url http://target:3000 --mode manual --user attacker --pw 'P@ssw0rd' --repo myrepo --cmd "whoami; id"

Options (high-level)

  • --url (required) : Target Gitea base URL (e.g. http://10.0.0.1:3000)
  • --mode : full-auto | semi-auto | manual | check (default: full-auto)
  • --user, --pw : Credentials for semi-auto/manual modes
  • --repo : Repository name (for manual mode)
  • --branch : Branch name (default: main)
  • --cmd : Command to execute on target (default: cat /etc/passwd)
  • --count : Number of diffpatch requests to send (min 2)
  • --simple-hook : Use a simple hook (skips advanced payload)
  • --no-retrieve : Skip output retrieval
  • --proxy : HTTP proxy (e.g. http://127.0.0.1:8080)
  • --verbose, -v : Verbose output
  • --quiet, -q : Quiet mode; only print command output
  • --force : Skip Gitea validation checks

Detection vs Exploitation

  • check mode runs non-intrusive checks to detect Gitea and probe the presence of the diffpatch endpoint.
  • full-auto tries to register a new user (requires open registration), create a repository, deliver the malicious diffpatch payload, and retrieve output from the injected hook.
  • semi-auto uses supplied credentials to create a repository and proceed with exploitation steps.
  • manual requires an existing user and repository; it only attempts exploit delivery and (optionally) output retrieval.

Security recommendations

  • Do not expose Gitea API endpoints unnecessarily. Limit public access.
  • Keep Gitea updated; versions >= 1.28.0 address this specific vulnerability.
  • Monitor repository creation, API calls and unusual commits or refs.

Development notes

  • The PoC is implemented as a single-file Go program. It intentionally sets InsecureSkipVerify to true for TLS connections to maximize compatibility during testing; do not use this behavior in production code.
  • The primary endpoints used are /api/v1/version, /user/sign_up, /api/v1/user, /api/v1/user/repos, and /api/v1/repos/:owner/:repo/diffpatch.

Contributing

Contributions should be limited to defensive improvements, documentation, and non-exploit-related fixes. Do not submit modifications that make the tool more destructive.

License

This repository is provided for research and defensive purposes. No license is explicitly included; if you require a license, add one and ensure it is compatible with your intended use.

Author / Contact

Author: Gagaltotal666 - GhostGTR666

Acknowledgements

This PoC was prepared to demonstrate the vulnerability and to assist defenders in detecting and mitigating it.


References

  • See the source implementation in https://github.com/gagaltotal/CVE-2026-60004-poc-gitea
Download Tool




