
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/gagaltotal/cve-2021-41773-apache
Payload GenerationVulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingLearning & Education
GitHubgagaltotal/cve-2021-41773-apache

CVE-2021-41773-apache

CVE-2021-41773 Apache

View Repository
1273 months agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    871
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    548
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    383
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    361
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    305
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    280

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2021-41773 Apache HTTP Server Exploit

This repository contains a Python-based proof-of-concept exploit for the Apache HTTP Server path traversal vulnerability identified as CVE-2021-41773. The script is designed for security research, defensive testing, and authorized evaluations of vulnerable systems.

Overview

CVE-2021-41773 is a path traversal vulnerability affecting Apache HTTP Server versions 2.4.49 and related configurations where the server improperly handles encoded traversal sequences in certain CGI request paths. This project provides a basic PoC implementation that can be used to verify exposure and interact with a vulnerable target.

Project Purpose

This repository is intended for:

  • Security research and vulnerability assessment
  • Educational demonstrations of path traversal behavior
  • Authorized penetration testing in controlled environments
  • Defensive validation and patch verification

Features

  • Verifies whether a target appears vulnerable
  • Sends crafted requests to test for command execution behavior
  • Supports one-shot command execution
  • Provides an interactive shell-style interface
  • Uses a simple Python implementation with minimal dependencies

Repository Structure

  • exploit.py: main Python exploit script
  • requirements.txt: Python dependencies
  • images/: screenshots or supporting materials
  • README.md: project documentation

Requirements

This project requires Python 3 and the following dependency:

  • requests

Install dependencies with:

python -m venv .venv
source .venv/bin/activate
pip install -r requirements.txt

Usage

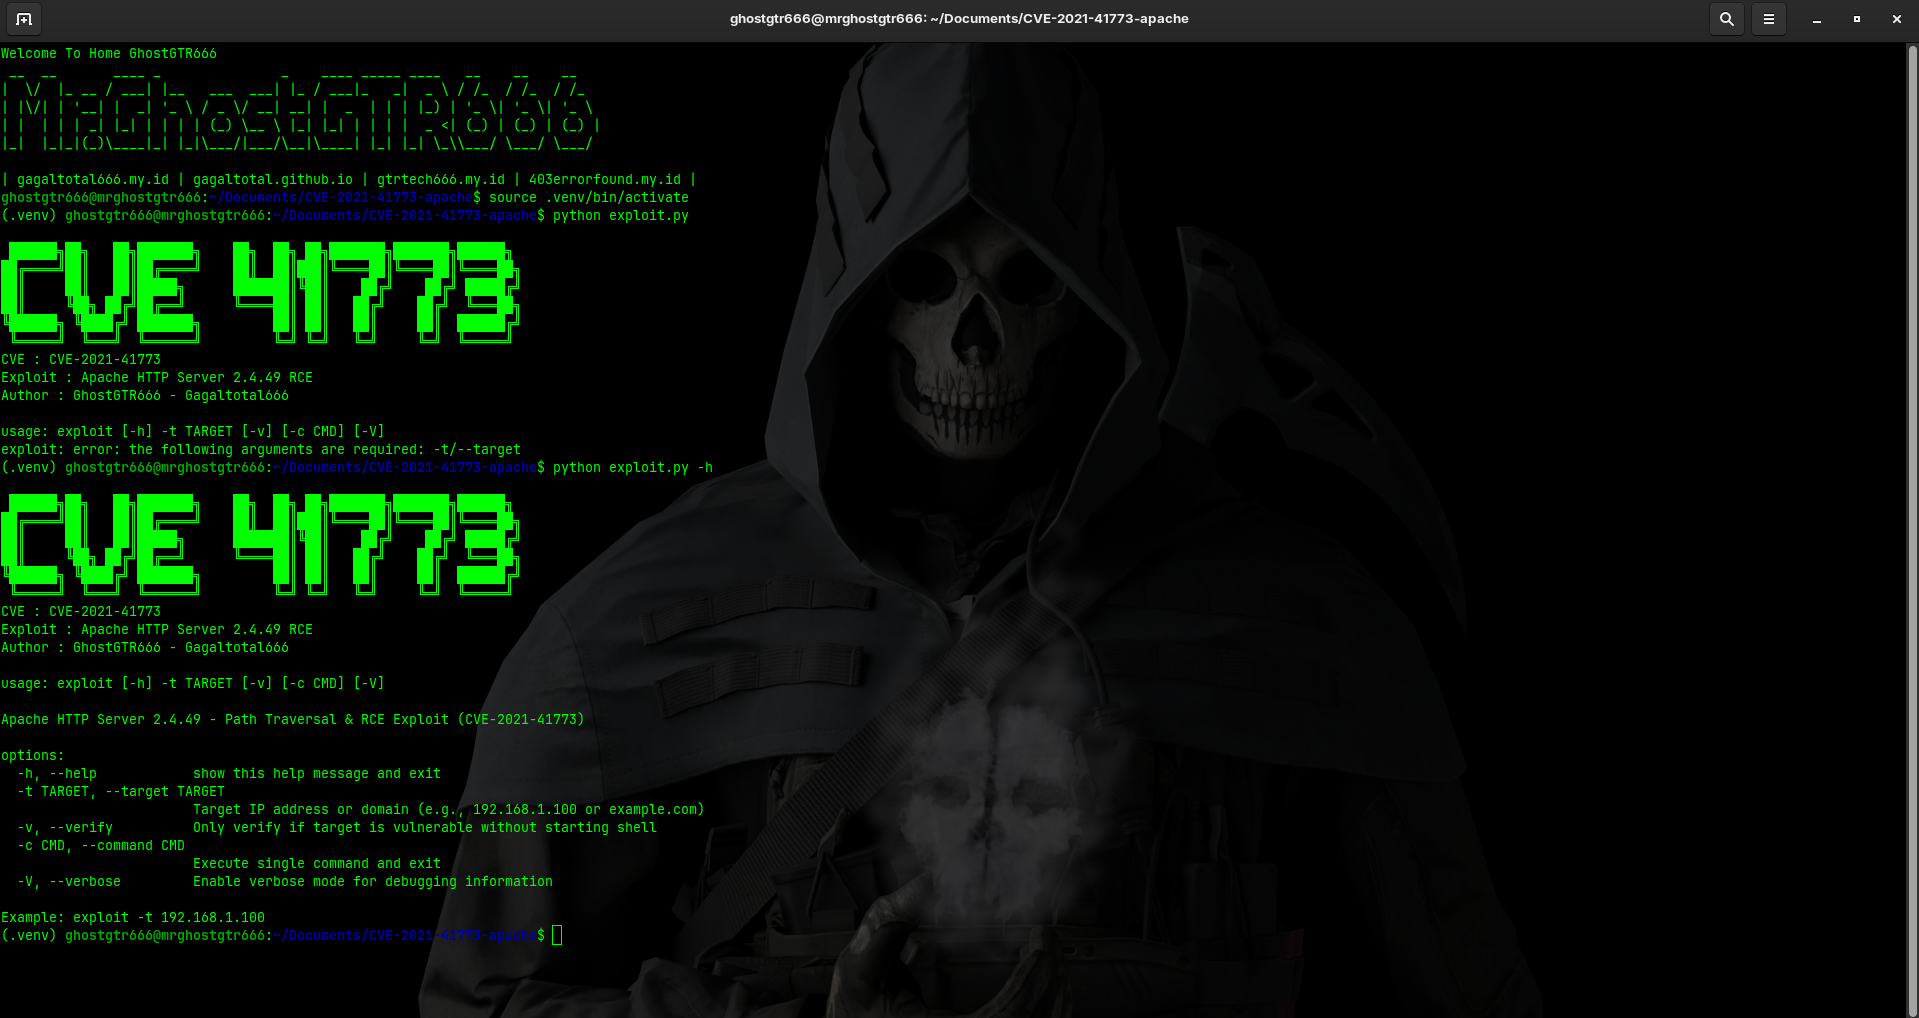
Screen Capture

Run the script with a target host or IP address.

Verify vulnerability

python3 exploit.py -t 192.168.1.100 -v

Execute a single command

python3 exploit.py -t 192.168.1.100 -c "whoami"

Start an interactive shell

python3 exploit.py -t 192.168.1.100

Example Commands

The script supports the following modes:

  • -t, --target: specify the target host or IP address
  • -v, --verify: verify vulnerability only
  • -c, --command: execute a single command and exit
  • -V, --verbose: display detailed request and response information

Notes

  • This tool is intended only for authorized environments.
  • A target must be explicitly tested with permission from the owner.
  • Results may vary depending on server configuration, web server version, and environmental restrictions.
  • The script uses insecure request handling by design for compatibility with the vulnerability scenario.

Security and Legal Disclaimer

This project is provided for educational and authorized security research purposes only. The author is not responsible for any misuse, unauthorized access, or illegal activity conducted with this software. You are solely responsible for ensuring that your use complies with all applicable laws, regulations, and policies.

Screenshots

Screenshots and supporting evidence can be placed in the images directory as needed.

Credits

Developed for research and demonstration purposes related to CVE-2021-41773.

Download Tool





