Open-source CTF guidebook covering Pwn, reverse engineering, and web security, with structured chapters, worked examples, and tooling setup for hands-on practice.
This book "The Definitive Guide to CTF Competitions (Pwn Edition)" (written by Yang Chao, reviewed by Wu Shi of the eee team) is now available!!! Buy on JD.com Buy on Dangdang
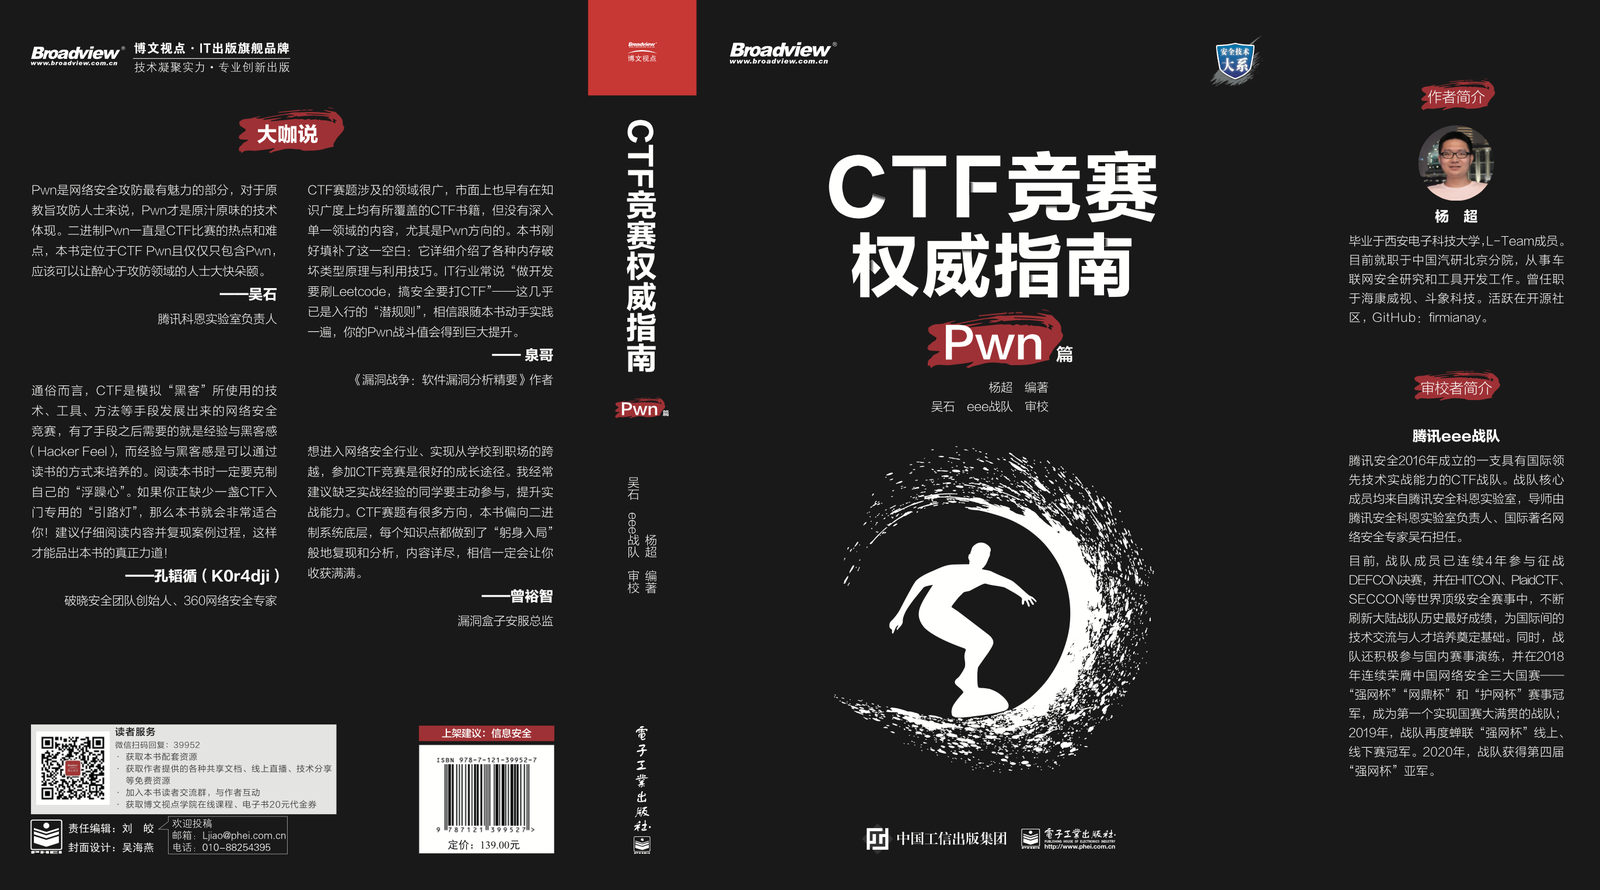
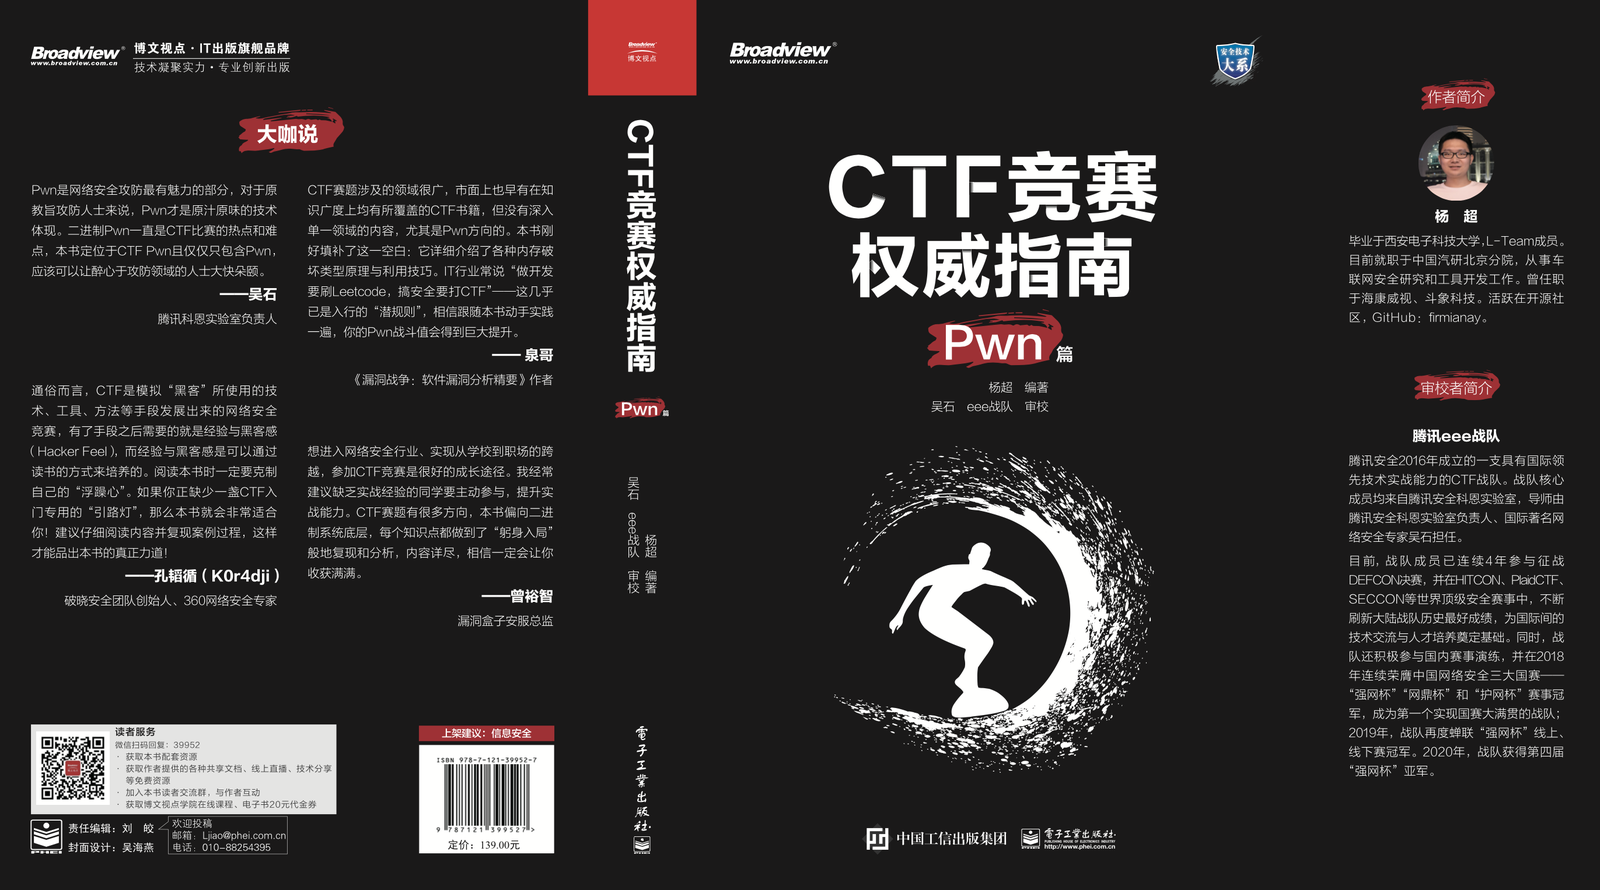
This book is primarily aimed at CTF Pwn beginners and focuses on Linux binary security. The book contains 12 chapters, starting from the low-level fundamentals of binaries, and combines source code to analyze common binary security vulnerabilities, mitigation mechanisms, and exploitation methods in detail, supplemented by explanations of analysis tools and environment setup, progressing step by step so that readers can engage in systematic learning. The book's selection of content and materials is relatively continuous and complete, with each knowledge point paired with classic examples, and a great deal of space devoted to explanation, aiming to reproduce the analysis approach and problem-solving process to the greatest extent and achieve the effect of drawing inferences from one instance.
Pwn is the most fascinating part of cybersecurity offense and defense; for fundamentalist offense-and-defense practitioners, pwn is the authentic embodiment of the technology. Binary pwn has always been a hot topic and a difficult point in CTF competitions. This book is positioned on CTF pwn content and contains only pwn, which should allow those devoted to the offense-and-defense field to feast to their heart's content. — Wu Shi, Head of Tencent Keen Lab
CTF challenges cover a very broad range of fields, and there have long been CTF books on the market that cover a breadth of knowledge, but none with in-depth content on a single field, especially the Pwn direction. This book precisely fills that gap: it provides a detailed introduction to the principles and exploitation techniques of various types of memory corruption. The IT industry often says, "For development, grind LeetCode; for security, play CTF"—this is almost an unspoken rule for entering the field. I believe that if you follow this book and practice hands-on, your Pwn combat power will be greatly enhanced. — Quan Ge, author of Vulnerability War: Essentials of Software Vulnerability Analysis. More on CTF Books
If you want to enter the cybersecurity industry and make the transition from school to the workplace, CTF is an excellent growth path. I often advise students on campus who lack practical experience to actively participate in CTF competitions to improve their practical skills. This book leans toward the low-level fundamentals of binary systems, and for each knowledge point it truly "steps into the fray" to reproduce and analyze the process. The content of this book is detailed, and I believe it will surely leave you richly rewarded. — Zeng Yuzhi, Security Services Director of Vulbox
From an accessible perspective, CTF is a cybersecurity competition developed from the techniques, tools, methods, and other means used by simulated "hackers." Once you have the means, what you need is experience and Hacker Feel, and experience and Hacker Feel can be cultivated through reading books. When reading this book, you must restrain your "impetuous mind." If you are lacking a dedicated "guiding light" for getting started with CTF, this book will be very suitable for you. I recommend carefully reading the content and reproducing the processes within to truly savor the real flavor of this book. — Kong Taoxun (K0r4dji), Founder of the Dawn Security Team, 360 Cybersecurity Expert
About This Book | Table of Contents | Sample Chapter | Related Resources (source code, errata, etc.)
Reader communication QQ groups: 808542982, 217863340
For the WeChat group, please add me on WeChat and note "join group." Welcome to follow the official account:
Writing a book takes time and effort and embodies a great deal of the author's dedication. Fight piracy and support genuine copies!
Writing in progress...
About This Book | Table of Contents | Sample Chapter | Related Resources (source code, errata, etc.)
Writing in progress...
About This Book | Table of Contents | Sample Chapter | Related Resources (source code, errata, etc.)
—"Rather than believing rumors, keep learning."
GitHub address: https://github.com/firmianay/CTF-All-In-One
GitBook address: https://firmianay.gitbook.io/ctf-all-in-one/
Please see SUMMARY.md
Please see CONTRIBUTING.md
Please see CHANGELOG
CC-BY-SA-4.0