Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
thm-blue-writeup — Writeup da sala Blue do TryHackMe — exploração do EternalBlue (MS17-010/CVE-2017-0143). | Kitploit
Tools/GitHubGitHub/fernandotdalcin/thm-blue-writeup
ReconnaissanceVulnerability AnalysisExploitationNetwork SecurityCTFPenetration TestingLearning & EducationLabs & Practice
Share
GitHub
fernandotdalcin/thm-blue-writeup

thm-blue-writeup

Writeup da sala Blue do TryHackMe — exploração do EternalBlue (MS17-010/CVE-2017-0143).

View Repository
346 months agoNot yet reviewed

TryHackMe — Blue | Phase 1: Reconnaissance with Nmap

Course: Cyber Security 101 | Room: Blue | Tool: Nmap


Context

The Blue room's main objective is the use of Metasploit. However, the first exercise focuses on reconnaissance — identifying open ports and vulnerabilities on the target before any exploitation.


Command used

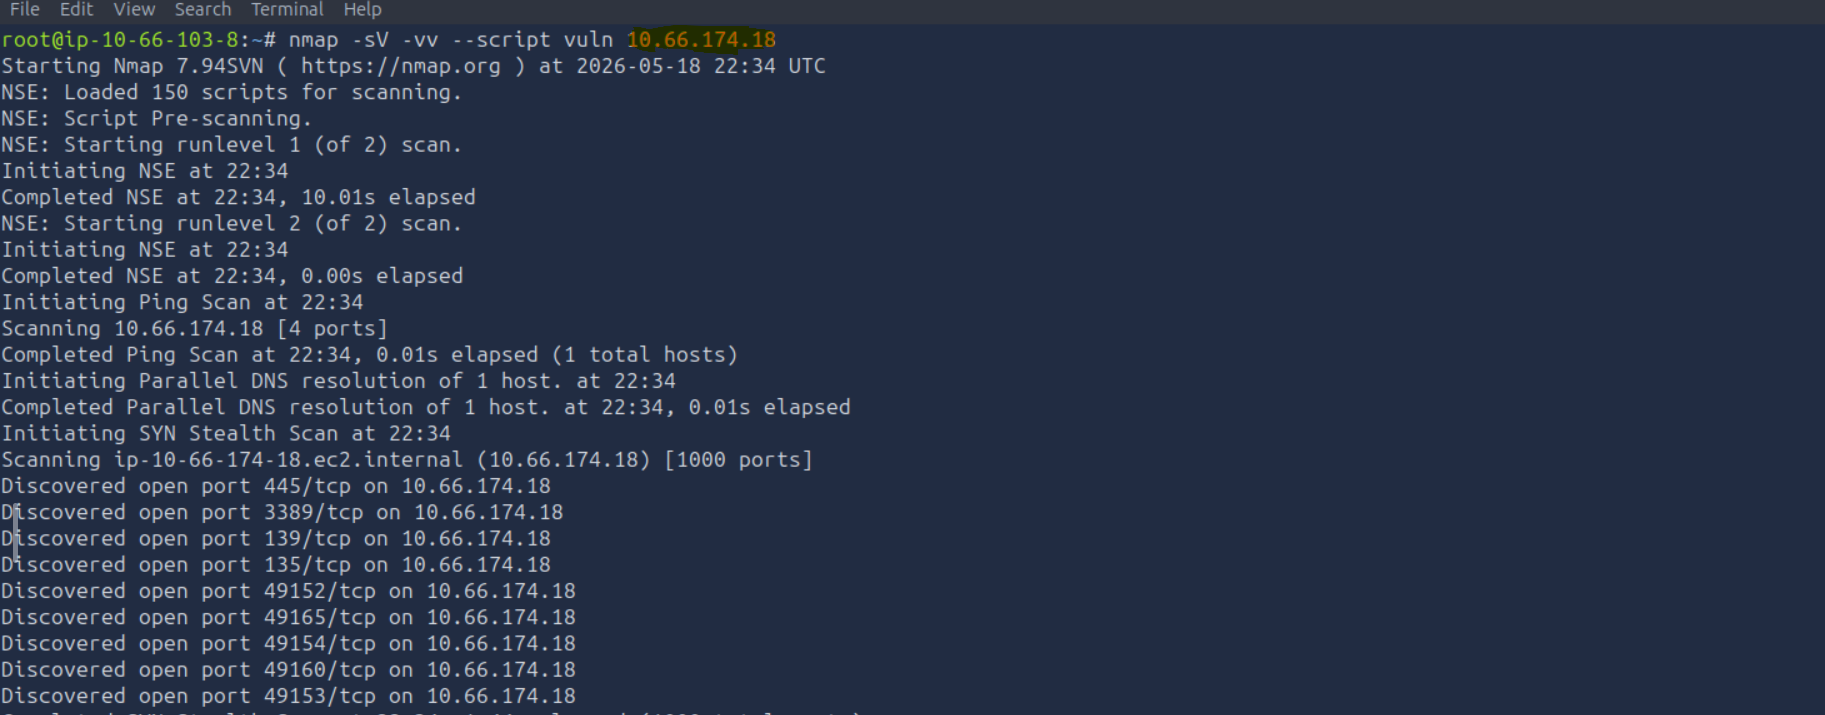
nmap -sV -vv --script vuln <IP>
FlagFunction
-sVDetects service version on ports
-vvVerbose output
--script vulnRuns NSE vulnerability detection scripts

Discovered ports

Nmap scan — open ports

PortProtocolService
135TCPRPC
139TCPNetBIOS
445TCPSMB
3389TCPRDP
49152–49165TCPWindows dynamic ports

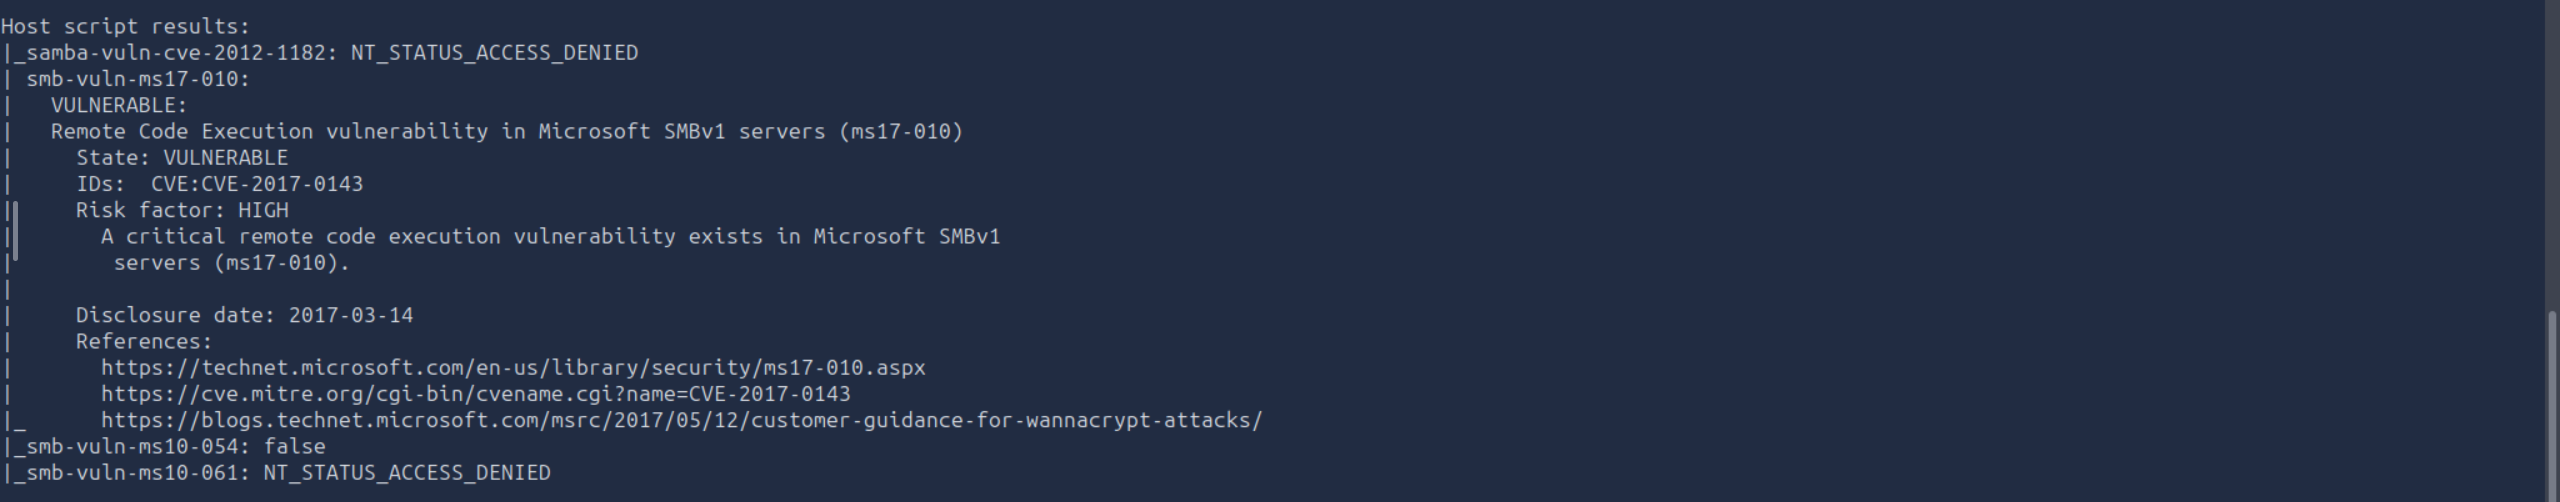
Identified vulnerability

MS17-010 result — EternalBlue

smb-vuln-ms17-010: VULNERABLE
CVE: CVE-2017-0143
Risk factor: HIGH
Disclosure date: 2017-03-14

The NSE script smb-vuln-ms17-010 confirmed that SMBv1 is active and vulnerable to EternalBlue — the same flaw used by the WannaCry ransomware in 2017.


Blue Team Perspective

This reconnaissance step is also a valuable exercise for those working in defense. What Nmap reveals about the target is exactly what a Blue Team analyst should proactively identify on their own network.

What this scan indicates for the defensive team:

ObservationRecommended defensive action
SMBv1 active (port 445)Disable SMBv1 — legacy unsupported protocol
MS17-010 unpatchedApply security update available since March 2017
RDP exposed (port 3389)Restrict access via firewall or VPN
Scan not detectedImplement alerts for port scanning on the network

Central question: if an attacker can obtain this information in seconds with Nmap, does the defense team already have visibility over this attack surface?

Reconnaissance is not just an offensive step — it is a mirror of what the Blue Team should be seeing first.


Room completed in May 2026 — TryHackMe Cyber Security 101

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    795
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    520
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    439
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    346
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    267
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    264

Explore all tools

Browse our collection of tools

View all tools →